

On this page
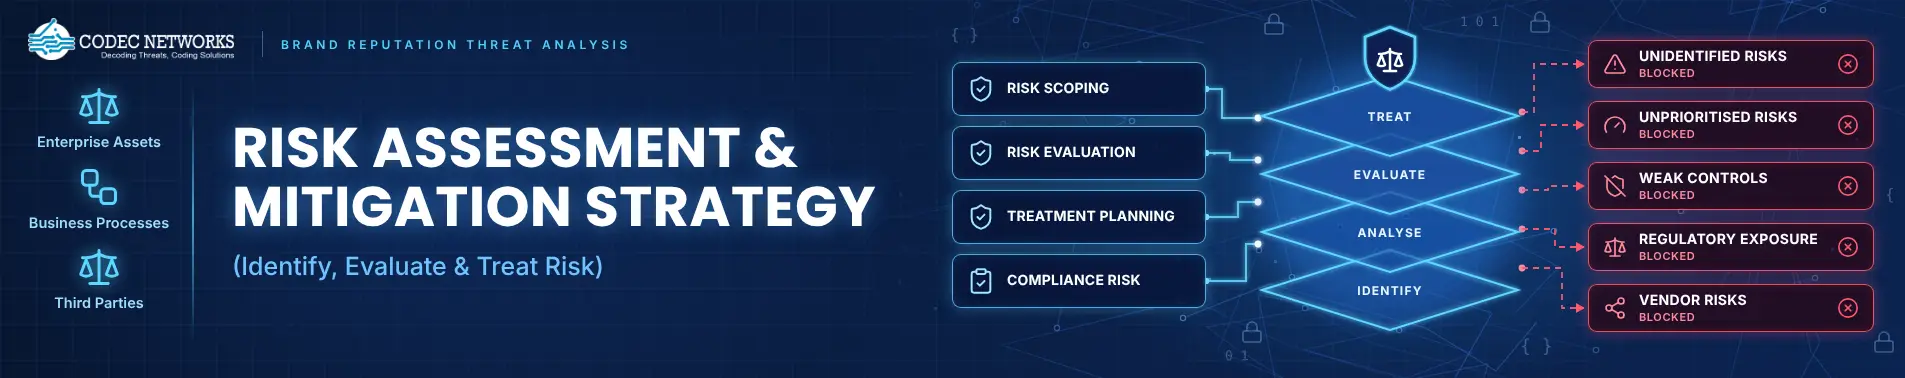

Risk Assessment & Mitigation Strategy
Every organisation - regardless of sector, size, or maturity — operates within a risk landscape that is continuously evolving. Regulatory obligations multiply, technology estates grow more complex, supply chains extend further, and the threat environment shifts faster than most internal security programmes can track. Organisations that lack a structured, repeatable approach to identifying, evaluating, and treating risk do not eliminate uncertainty — they simply operate within it without the visibility needed to manage it purposefully.
Codec Networks' Risk Assessment & Mitigation Strategy service is a structured, evidence-based programme that gives organisations a precise, current, and actionable picture of the risks they face — across information security, operational resilience, regulatory compliance, and third-party dependencies. The service is built on internationally recognised risk management frameworks including ISO 31000, ISO/IEC 27005, NIST RMF, and COSO ERM, applied with the rigour that governance stakeholders, regulators, and certification bodies require.
The assessment process spans risk identification across business functions and technology layers, likelihood and impact analysis calibrated to the client's specific context, control effectiveness evaluation, residual risk determination, and the development of prioritised, owner-assigned treatment plans that translate risk findings into concrete remediation activity. The programme addresses not only what the risks are, but who owns them, how they should be treated, and how progress will be measured and reported.
Findings are validated, risk-rated against agreed criteria, and mapped to applicable regulatory and compliance frameworks. Deliverables are designed to serve multiple audiences simultaneously — providing board-level risk visibility, operational guidance for risk owners, and compliance evidence for regulators and auditors — through a single, integrated engagement that respects the constraints of real organisations managing real risk programmes.
Industry Significance
Structured risk assessment is no longer optional but a core operational foundation. Organisations that actively manage risk make informed decisions, while others react too late. Sustained long-term performance depends on the ability to identify, assess, and manage inherent risks effectively.
Read More
Service Relevance
Codec Networks' Risk Assessment & Mitigation Strategy service addresses gap between understanding and execution, helping organisations apply rigorous, consistent, and comprehensive risk governance. It delivers structure and expertise needed to strengthen internal programmes and ensure effective, disciplined risk management practices.
Read More
Benefits to Customers
Risk Assessment & Mitigation Strategy delivers the precise, current, and credible risk intelligence that organisations need to govern effectively and make strategic decisions. The benefits extend from board governance to operational execution — and from current compliance to long-term resilience.
Read More
Risk Assessment & Mitigation Strategy
SERVICE FEATURES AND DELIVERY FRAMEWORK
Codec Networks delivers risk assessment and mitigation strategy through structured methodology, expert analysis, comprehensive framework
coverage, calibrated delivery metrics, and governance-grade documentation that serves boards, regulators, and certification auditors alike.
Codec Networks' Risk Assessment & Mitigation Strategy service addresses gap between understanding and execution, helping organisations apply rigorous, consistent, and comprehensive risk governance. It delivers structure and expertise needed to strengthen internal programmes and ensure effective, disciplined risk management practices.
Codec Networks' service features are designed to address these structural weaknesses systematically — producing risk outputs that are technically rigorous, practically actionable, and credible to the governance, compliance, and operational stakeholders who depend on them.
Codec Networks offers these services across the following segments:
- Enterprise Risk Identification and Scoping
- Structured Risk Universe Definition: Establishes a comprehensive risk taxonomy covering information security, operational, regulatory, third-party, strategic, and resilience risk categories relevant to the client's specific operating context.
- Stakeholder Workshops and Interviews: Structured elicitation sessions with business unit leaders, technology owners, compliance functions, and operational management to surface risks with genuine organisational intelligence rather than generic templates.
- Asset and Process Dependency Mapping: Documents the critical assets, processes, systems, and third-party relationships that underpin business objectives — establishing the foundation for risk identification that reflects operational reality.
- Regulatory Obligation Inventory: Systematically identifies applicable regulatory, statutory, and contractual risk management requirements across the client's operational jurisdictions and sector obligations.
- Threat Intelligence Integration: Current threat intelligence relevant to the client's sector, technology profile, and geographic footprint is incorporated into risk identification to ensure emerging threats are captured alongside established risk categories.
- Risk Identification Report: Comprehensive documentation of identified risks with initial categorisation, source, and potential consequence — providing the complete risk universe for subsequent assessment phases.
2. Risk Analysis and Evaluation
- Agreed Likelihood and Impact Criteria: Risk rating scales calibrated to the client's organisational context, risk appetite, and tolerance thresholds — ensuring ratings carry consistent meaning across business units, assessors, and assessment cycles.
- Inherent Risk Assessment: Each identified risk is rated for inherent likelihood and impact before control consideration, establishing the baseline exposure the organisation would face without existing controls.
- Control Inventory and Mapping: Existing controls — technical, procedural, and contractual — are inventoried and mapped to the risks they are intended to address, documenting the designed control environment.
- Control Effectiveness Testing: Independent assessment of whether mapped controls are operating as designed and actually reducing the risks they are intended to manage — distinguishing policy compliance from operational effectiveness.
- Residual Risk Determination: Residual risk ratings derived from inherent assessment adjusted for validated control effectiveness — producing a risk register that reflects genuine remaining exposure rather than assumed reduction.
- Risk Evaluation Against Appetite: Residual risks compared against the organisation's documented risk appetite and tolerance boundaries, identifying where accepted risk exceeds stated thresholds and where escalation or treatment is required.
3. Risk Treatment Planning and Mitigation Strategy
- Treatment Option Analysis: For each material risk, treatment options are identified and evaluated across the full range: avoidance, reduction, sharing/transfer, and acceptance — with rationale for recommended approach.
- Prioritised Mitigation Recommendations: Treatment actions sequenced by the risk reduction they deliver relative to implementation effort and cost, ensuring resource-constrained organisations can make rational prioritisation decisions.
- Owner and Accountability Assignment: Every mitigation action is assigned to a named owner with defined accountability for implementation, progress reporting, and closure confirmation.
- Implementation Roadmap: Phased treatment timeline with milestones, dependencies, resource requirements, and interim risk reduction measures for exposures where full treatment will take time to complete.
- Residual Risk Acceptance Framework: Where risks are to be accepted rather than treated, a structured acceptance process with documented rationale, accountable sign-off, and review schedule is established.
- Risk Treatment Plan Documentation: Comprehensive, governance-grade treatment plan documentation suitable for board approval, regulatory submission, and ISO 27001 certification audit purposes.
4. Regulatory and Compliance Risk Assessment
- Multi-Framework Obligation Mapping: Regulatory and compliance obligations across ISO 27001, ISO 31000, GDPR, In-country regulatory norms and guidelines, and sector-specific requirements are systematically identified and mapped to risk findings.
- Compliance Gap Analysis: Current compliance posture assessed against each applicable framework, identifying specific gaps and the risk exposure they represent.
- DPIA and Privacy Risk Assessment Integration: Data Protection Impact Assessment requirements identified and integrated where personal data processing in scope triggers GDPR and In-country regulatory norms and guidelines obligations.
- Audit-Ready Evidence Generation: Risk assessment documentation structured to serve as direct compliance evidence for regulatory examinations, certification audits, and contractual due diligence processes.
- Regulatory Change Horizon Monitoring: Emerging regulatory developments relevant to the client's sector are identified and their risk implications flagged for inclusion in near-term assessment cycles.
- Compliance Risk Register: Dedicated compliance risk section within the enterprise risk register, tracking regulatory obligations, associated risks, control status, and treatment plans.
5. Third-Party and Supply Chain Risk Assessment
- Material Third-Party Identification: Systematic identification of all material third-party relationships — technology vendors, cloud providers, outsourced processors, logistics partners, and professional service providers — that carry operational or regulatory risk.
- Criticality and Concentration Assessment: Each material third party assessed for criticality to business operations, concentration risk (multiple critical dependencies on single provider), and substitutability.
- Third-Party Security and Resilience Evaluation: Assessment of third-party security controls, resilience arrangements, sub-contractor dependencies, and compliance obligations relevant to the services they provide.
- Contractual Risk Allocation Review: Existing contractual security and risk obligations reviewed for completeness, enforceability, and alignment with actual risk exposure in the relationship.
- Third-Party Risk Register: Documented register of material third-party risks with owner assignment, current control status, and prioritised treatment actions for identified gaps.
- Ongoing Monitoring Framework: Structured approach to continuous third-party risk monitoring, including assessment triggers, review frequency, and escalation criteria for material third-party risk changes.
6. Risk Reporting and Governance Framework
- Board and Senior Management Risk Reporting: Executive risk reports presenting the organisation's risk profile in governance language — heat maps, trending analysis, risk appetite comparison, and key risk indicators — designed for board and audit committee audiences.
- Operational Risk Dashboards: Management-level reporting providing operational teams with clear visibility of their risk responsibilities, treatment progress, and control performance indicators.
- Key Risk Indicator Development: Design of forward-looking metrics that provide early warning of emerging risk materialisation — enabling proactive management rather than reactive response.
- Risk Governance Structure Advisory: Recommendations for risk ownership, escalation pathways, committee structures, and three-lines-of-defence arrangements appropriate to the client's size and complexity.
- Risk Appetite Statement Development: Facilitation of risk appetite articulation with board and senior management — translating governance intent into specific, measurable tolerance thresholds that can be operationalised.
- Risk Management Policy and Procedure Framework: Documentation of risk management policies, assessment procedures, and governance standards that provide the structural framework for a sustainable ongoing programme.
Codec Networks' Risk Assessment & Mitigation Strategy follows a structured, consultative engagement model that progresses from programme design through comprehensive assessment, validated findings, and governance-grade deliverables to implementation support. Each phase builds on the last, and each produces outputs that serve immediate value while contributing to the cumulative programme outcome.
The methodology integrates ISO 31000, ISO/IEC 27005, NIST RMF, COSO ERM, and FAIR quantitative analysis within a delivery framework calibrated to the client's sector, regulatory environment, organisational complexity, and risk maturity — ensuring that every engagement produces results proportionate to the organisation's specific governance context.
Codec Network's overall Service Delivery methodology comprises of:
1. Project Initiation & Scoping
- Engagement Design Workshop: Codec Networks works with key stakeholders — board sponsors, senior management, risk and compliance leads, and IT and operational owners — to establish the precise scope, objectives, and success criteria for the engagement.
- Scope and Boundary Definition: Business units, technology systems, regulatory frameworks, and third-party relationships included within the assessment scope are formally documented alongside explicit exclusions and their rationale.
- Risk-Based Prioritisation: Business-critical processes, high-regulatory-exposure areas, and organisational concentrations are identified for deeper assessment focus based on initial scoping intelligence.
- Engagement Charter and SoW: A signed Statement of Work documents scope, methodology, deliverables, timelines, stakeholder responsibilities, communication protocols, and governance arrangements for the engagement.
2. Pre-Engagement Preparation
- Documentation and Evidence Request: Existing risk management documentation — current risk registers, control frameworks, audit reports, incident records, and regulatory correspondence — is collected and reviewed before assessment activity begins.
- Stakeholder Interview Schedule: A structured interview programme is designed covering all material business areas, ensuring that the assessment captures risk knowledge from across the organisation rather than from a limited central perspective.
- Assessment Criteria Calibration: Likelihood and impact rating scales are agreed with the client, calibrated to their specific risk appetite, regulatory obligations, and organisational scale — ensuring that risk ratings carry operationally meaningful significance throughout the engagement.
3. Information Gathering & Reconnaissance
- Document Review and Analysis: Existing policies, procedures, risk registers, audit findings, incident reports, contractual obligations, and regulatory correspondence are reviewed to establish the current risk management baseline and identify known risks.
- Stakeholder Interviews: Structured interviews with business unit leaders, technology owners, compliance and legal teams, operations management, and board-level risk owners surface risks with genuine organisational context and intelligence.
- Technology and Process Inventory: Critical technology assets, operational processes, data flows, and third-party dependencies are mapped to provide the asset and process foundation that risk identification requires.
4. Vulnerability Assessment
- Technical Risk Assessment: Technology infrastructure, application environments, cloud deployments, and operational technology are assessed for technical vulnerabilities that translate into information security and operational risk findings.
- Process and Control Gap Review: Operational processes, governance procedures, and control frameworks are assessed against applicable standards and best practice to identify process-level risk exposures.
- Regulatory Compliance Baseline: Current compliance status against applicable regulatory frameworks is assessed, providing the compliance risk component of the overall risk picture.
5. Manual Risk Assessment & Deep Analysis
- Risk Identification Workshops: Facilitated workshops across business units and technology functions apply structured risk identification techniques — scenario analysis, bow-tie analysis, and process-level assessment — to surface risks beyond those captured in documentation review.
- Third-Party Risk Deep-Dive: Material third-party relationships are assessed in depth — covering security posture, resilience arrangements, regulatory compliance, contractual adequacy, and concentration risk.
- Control Effectiveness Testing: Key controls are independently tested for operational effectiveness — validating that residual risk calculations are based on controls that work in practice, not just controls that exist in policy.
- Risk Interdependency Analysis: Relationships and cascade effects between identified risks are mapped — identifying where the materialisation of one risk would trigger or amplify others, and where risk concentrations create compounded exposure.
- Quantitative Risk Analysis (Where Applicable): FAIR methodology applied to high-priority risks where financial quantification would materially improve governance decision quality.
- Emerging Risk Identification: Horizon-scanning analysis integrates current threat intelligence, regulatory developments, and strategic change factors to identify emerging risks not yet reflected in current risk registers.
6. Post-Assessment Risk Validation
- Findings Validation: All identified risks are validated with relevant business and technical stakeholders before finalisation — ensuring risk descriptions accurately reflect organisational context and that ratings are appropriate to the client's specific circumstances.
- Risk Rating Calibration: Final risk ratings are calibrated across the full risk register to ensure consistency of scoring across business units, risk categories, and assessors.
- False Comfort Elimination: Risks where assumed control effectiveness has been generating false assurance are explicitly identified — ensuring residual risk ratings reflect the tested control environment rather than the designed one.
7. Reporting & Documentation
- Board and Executive Risk Report: High-level risk summary presenting the organisation's overall risk profile, critical risk findings, risk appetite comparison, strategic implications, and governance recommendations — structured for board and audit committee consumption.
- Comprehensive Risk Register: Detailed risk documentation covering risk description, category, inherent rating, control inventory, control effectiveness assessment, residual rating, risk appetite comparison, and treatment recommendations for every identified risk.
- Risk Treatment Plan: Prioritised, owner-assigned action plan with implementation timelines, resource requirements, dependencies, and success criteria for every material risk requiring treatment.
- Regulatory Compliance Matrix: Structured mapping of risk findings and control gaps to applicable regulatory and compliance framework requirements, formatted for direct submission in regulatory examinations and certification audits.
8. Remediation Support & Workshops
- Risk Register Walkthrough: Structured session with risk owners, management, and governance stakeholders presenting all findings, treatment recommendations, and governance implications — providing the shared understanding that effective risk management requires.
- Risk Owner Capability Workshops: Targeted sessions with risk owners covering risk assessment methodology, treatment planning, progress tracking, and escalation procedures — building internal capability for ongoing programme management.
- Treatment Implementation Advisory: Consultative support for treatment plan development and initial implementation — helping organisations translate assessment outputs into operational programmes without losing momentum after delivery.
- Control Design Guidance: Advisory on the design, implementation, and testing of mitigating controls for prioritised risk findings — ensuring treatment activity closes the identified risk rather than addressing its symptoms.
9. Continuous Risk Management & Monitoring Integration (Optional – Advanced Clients)
- Ongoing Risk Monitoring Framework: Key risk indicators, trigger-based reassessment processes, and reporting mechanisms designed and implemented to maintain current risk visibility between formal assessment cycles.
- Recurring Assessment Programmes: Scheduled reassessment cycles — quarterly for critical risks, annual for full enterprise scope — providing regulators, board, and management with continuously current risk assurance.
- Integrated Threat Intelligence: Assessment programme augmented with ongoing threat intelligence relevant to the client's sector and risk profile, ensuring that the risk picture evolves with the threat landscape.
- Red Team and Scenario Testing (Optional): Adversarial scenario exercises designed around the most material identified risks — testing whether controls and response capability are effective against the specific scenarios that matter most to the organisation.
10. Closure & Governance
- Programme Closure Review: Formal completion meeting with all stakeholders covering findings acceptance, treatment plan launch, open items, and governance recommendations — establishing the ongoing risk management programme on a clear foundation.
- Risk Governance Dashboard: Optional delivery of an operational risk tracking dashboard providing management and board visibility into risk register status, treatment progress, and key risk indicators.
- Long-Term Advisory Relationship: Continuation options including ongoing risk advisory, recurring assessment cycles, board risk reporting support, and access to Codec Networks' risk management expertise as the organisation's risk environment evolves.
|
Standard / Framework |
Scope & Applicability |
How It Is Applied in Service Delivery |
Client Value Delivered |
|
ISO 31000:2018 |
International standard providing principles, framework, and process guidance for risk management applicable to any organisation, sector, or context. |
Risk assessment methodology, process design, and governance framework structured around ISO 31000 principles and process requirements. |
Anchors the risk management programme within a globally recognised, auditor-accepted framework — providing credibility for regulatory, certification, and investor audiences. |
|
ISO/IEC 27005:2022 |
International standard for information security risk management, providing detailed guidance on risk identification, analysis, evaluation, and treatment in information and technology contexts. |
Information security risk identification and assessment methodology aligned to ISO 27005 process requirements and risk treatment guidance. |
Ensures information and technology risk assessments meet the rigour expected by ISO 27001 certification auditors and information security regulators. |
|
NIST Risk Management Framework (RMF) |
U.S. federal framework providing a structured, repeatable process for managing information system risk across prepare, categorise, select, implement, assess, authorise, and monitor stages. |
RMF process stages used to structure risk treatment planning and control selection for technology and information system risk findings. |
Supports compliance with U.S. federal requirements and aligns with internationally recognised risk management practice for technology environments. |
|
NIST Cybersecurity Framework (CSF) 2.0 |
Risk-based framework organising cybersecurity activities around Govern, Identify, Protect, Detect, Respond, and Recover functions. |
Risk findings categorised and reported against CSF functions, providing a structured view of organisational cybersecurity risk posture and maturity. |
Enables risk communication using the common language that boards, regulators, and enterprise partners increasingly use to discuss and govern cybersecurity risk. |
|
ISO/IEC 27001:2022 |
International standard for information security management systems, with risk assessment as a core requirement under Clause 6.1. |
Information security risk assessment outputs structured to meet ISO 27001 Clause 6 requirements for documented risk assessment and treatment planning. |
Provides the risk assessment evidence required for ISO 27001 certification and supports ongoing surveillance audit compliance. |
|
COSO ERM Framework (2017) |
Enterprise Risk Management framework published by the Committee of Sponsoring Organizations linking risk management to strategy and performance. |
Enterprise risk assessment findings presented in alignment with COSO ERM components — governance, strategy, performance, review, and information. |
Connects the risk management programme to strategic and operational performance objectives, giving board and senior management the enterprise risk context they need. |
|
FAIR (Factor Analysis of Information Risk) |
Quantitative risk analysis methodology providing a structured approach to measuring information risk in financial terms. |
FAIR methodology applied where quantitative risk analysis is appropriate, converting qualitative risk findings into financial exposure estimates. |
Enables risk-based investment decisions by expressing risk in financial terms that business stakeholders understand and can act on without requiring security expertise. |
|
IEC 62443 |
Industrial cybersecurity standard addressing risk management for operational technology and industrial control system environments. |
OT and ICS risk assessment components structured around IEC 62443 risk management requirements where operational technology is in scope. |
Ensures risk assessment addresses the distinct risk profile of operational technology environments, including safety consequence and availability requirements. |
|
GDPR / Data Protection Legislation |
European and national data protection regulations imposing specific obligations for privacy risk assessment including Data Protection Impact Assessments. |
Privacy risk identification and DPIA requirements integrated into risk assessment scope where personal data processing is in scope. |
Demonstrates compliance with data protection risk assessment obligations and provides documented evidence for supervisory authority enquiries. |
|
In country- norms and guidelines and Sector-Specific Regulatory Guidelines |
Cybersecurity guidance and mandatory risk management requirements issued by In country- norms and guidelines and sector regulators applicable to Indian organisations. |
Risk assessment scope and outputs aligned to applicable In country- norms and guidelines and sectoral risk management requirements. |
Ensures risk management activity addresses the full range of regulatory obligations applicable to the client's sector and jurisdiction. |
Please Note:
- Risk management principles are applied to structure the assessment process, not simply to label its outputs — ensuring that every stage of the engagement contributes to better-informed governance decisions.
- Information security risk assessment follows ISO/IEC 27005 process rigour while remaining accessible to business stakeholders who own risks without having information security expertise.
- Regulatory framework mapping is applied with attention to the specific obligations of the client's sector and jurisdiction — avoiding the generic compliance templating that produces compliant paperwork without compliance substance.
- Quantitative risk analysis is applied selectively, where financial expression of risk genuinely improves governance decision quality — not as a universal methodology that imposes false precision on inherently qualitative risk categories.
- Governance and accountability structures established during the engagement are designed for sustainability — enabling the client to maintain and develop their risk management programme without ongoing external dependency.
- Total liability for all services is strictly limited to the international standards as far as possible as agreed in contracted engagement value. Codec Networks expressly excludes any indirect, financial, operational, incidental, punitive, or consequential damages, which may arise due to any coincidental events, or changes in international standards guidelines time to time
Codec Networks' Risk Assessment & Mitigation Strategy service addresses gap between understanding and execution, helping organisations apply rigorous, consistent, and comprehensive risk governance. It delivers structure and expertise needed to strengthen internal programmes and ensure effective, disciplined risk management practices.
Codec Networks' service features are designed to address these structural weaknesses systematically — producing risk outputs that are technically rigorous, practically actionable, and credible to the governance, compliance, and operational stakeholders who depend on them.
Codec Networks offers these services across the following segments:
- Enterprise Risk Identification and Scoping
- Structured Risk Universe Definition: Establishes a comprehensive risk taxonomy covering information security, operational, regulatory, third-party, strategic, and resilience risk categories relevant to the client's specific operating context.
- Stakeholder Workshops and Interviews: Structured elicitation sessions with business unit leaders, technology owners, compliance functions, and operational management to surface risks with genuine organisational intelligence rather than generic templates.
- Asset and Process Dependency Mapping: Documents the critical assets, processes, systems, and third-party relationships that underpin business objectives — establishing the foundation for risk identification that reflects operational reality.
- Regulatory Obligation Inventory: Systematically identifies applicable regulatory, statutory, and contractual risk management requirements across the client's operational jurisdictions and sector obligations.
- Threat Intelligence Integration: Current threat intelligence relevant to the client's sector, technology profile, and geographic footprint is incorporated into risk identification to ensure emerging threats are captured alongside established risk categories.
- Risk Identification Report: Comprehensive documentation of identified risks with initial categorisation, source, and potential consequence — providing the complete risk universe for subsequent assessment phases.
2. Risk Analysis and Evaluation
- Agreed Likelihood and Impact Criteria: Risk rating scales calibrated to the client's organisational context, risk appetite, and tolerance thresholds — ensuring ratings carry consistent meaning across business units, assessors, and assessment cycles.
- Inherent Risk Assessment: Each identified risk is rated for inherent likelihood and impact before control consideration, establishing the baseline exposure the organisation would face without existing controls.
- Control Inventory and Mapping: Existing controls — technical, procedural, and contractual — are inventoried and mapped to the risks they are intended to address, documenting the designed control environment.
- Control Effectiveness Testing: Independent assessment of whether mapped controls are operating as designed and actually reducing the risks they are intended to manage — distinguishing policy compliance from operational effectiveness.
- Residual Risk Determination: Residual risk ratings derived from inherent assessment adjusted for validated control effectiveness — producing a risk register that reflects genuine remaining exposure rather than assumed reduction.
- Risk Evaluation Against Appetite: Residual risks compared against the organisation's documented risk appetite and tolerance boundaries, identifying where accepted risk exceeds stated thresholds and where escalation or treatment is required.
3. Risk Treatment Planning and Mitigation Strategy
- Treatment Option Analysis: For each material risk, treatment options are identified and evaluated across the full range: avoidance, reduction, sharing/transfer, and acceptance — with rationale for recommended approach.
- Prioritised Mitigation Recommendations: Treatment actions sequenced by the risk reduction they deliver relative to implementation effort and cost, ensuring resource-constrained organisations can make rational prioritisation decisions.
- Owner and Accountability Assignment: Every mitigation action is assigned to a named owner with defined accountability for implementation, progress reporting, and closure confirmation.
- Implementation Roadmap: Phased treatment timeline with milestones, dependencies, resource requirements, and interim risk reduction measures for exposures where full treatment will take time to complete.
- Residual Risk Acceptance Framework: Where risks are to be accepted rather than treated, a structured acceptance process with documented rationale, accountable sign-off, and review schedule is established.
- Risk Treatment Plan Documentation: Comprehensive, governance-grade treatment plan documentation suitable for board approval, regulatory submission, and ISO 27001 certification audit purposes.
4. Regulatory and Compliance Risk Assessment
- Multi-Framework Obligation Mapping: Regulatory and compliance obligations across ISO 27001, ISO 31000, GDPR, In-country regulatory norms and guidelines, and sector-specific requirements are systematically identified and mapped to risk findings.
- Compliance Gap Analysis: Current compliance posture assessed against each applicable framework, identifying specific gaps and the risk exposure they represent.
- DPIA and Privacy Risk Assessment Integration: Data Protection Impact Assessment requirements identified and integrated where personal data processing in scope triggers GDPR and In-country regulatory norms and guidelines obligations.
- Audit-Ready Evidence Generation: Risk assessment documentation structured to serve as direct compliance evidence for regulatory examinations, certification audits, and contractual due diligence processes.
- Regulatory Change Horizon Monitoring: Emerging regulatory developments relevant to the client's sector are identified and their risk implications flagged for inclusion in near-term assessment cycles.
- Compliance Risk Register: Dedicated compliance risk section within the enterprise risk register, tracking regulatory obligations, associated risks, control status, and treatment plans.
5. Third-Party and Supply Chain Risk Assessment
- Material Third-Party Identification: Systematic identification of all material third-party relationships — technology vendors, cloud providers, outsourced processors, logistics partners, and professional service providers — that carry operational or regulatory risk.
- Criticality and Concentration Assessment: Each material third party assessed for criticality to business operations, concentration risk (multiple critical dependencies on single provider), and substitutability.
- Third-Party Security and Resilience Evaluation: Assessment of third-party security controls, resilience arrangements, sub-contractor dependencies, and compliance obligations relevant to the services they provide.
- Contractual Risk Allocation Review: Existing contractual security and risk obligations reviewed for completeness, enforceability, and alignment with actual risk exposure in the relationship.
- Third-Party Risk Register: Documented register of material third-party risks with owner assignment, current control status, and prioritised treatment actions for identified gaps.
- Ongoing Monitoring Framework: Structured approach to continuous third-party risk monitoring, including assessment triggers, review frequency, and escalation criteria for material third-party risk changes.
6. Risk Reporting and Governance Framework
- Board and Senior Management Risk Reporting: Executive risk reports presenting the organisation's risk profile in governance language — heat maps, trending analysis, risk appetite comparison, and key risk indicators — designed for board and audit committee audiences.
- Operational Risk Dashboards: Management-level reporting providing operational teams with clear visibility of their risk responsibilities, treatment progress, and control performance indicators.
- Key Risk Indicator Development: Design of forward-looking metrics that provide early warning of emerging risk materialisation — enabling proactive management rather than reactive response.
- Risk Governance Structure Advisory: Recommendations for risk ownership, escalation pathways, committee structures, and three-lines-of-defence arrangements appropriate to the client's size and complexity.
- Risk Appetite Statement Development: Facilitation of risk appetite articulation with board and senior management — translating governance intent into specific, measurable tolerance thresholds that can be operationalised.
- Risk Management Policy and Procedure Framework: Documentation of risk management policies, assessment procedures, and governance standards that provide the structural framework for a sustainable ongoing programme.
RISK ASSESSMENT & MITIGATION STRATEGY - CODEC NETWORK'S INDUSTRY OFFERINGS
Codec Networks' Risk Assessment & Mitigation Strategy packages are structured to match organisational risk maturity — from establishing a
credible risk baseline to delivering enterprise-grade continuous risk governance across complex, multi-regulatory environments
Basic Packages (Foundation Tier)
Target Clients:
Small and medium-sized organisations, early-stage companies, and businesses establishing their first structured risk management programme — typically those who recognise the need for documented risk governance but have not yet built internal risk management infrastructure.
Sub-Services in Scope :
- Foundational Risk Identification Assessment
- Risk Register Development and Population
- Critical Risk Prioritisation and Treatment Plan
- Basic Regulatory Compliance Gap Assessment
- ISO 31000 and ISO 27001 Risk Assessment Alignment Review
Objective:
Establish a credible, documented risk baseline that identifies the most material exposures, assigns clear ownership, and provides a prioritised treatment roadmap — giving the organisation a structured starting point for risk management rather than an ad hoc approach.
Value Delivered:
A risk register the organisation can stand behind, a treatment plan that leadership can commit to, and compliance documentation that satisfies foundational regulatory and customer due diligence requirements — delivered efficiently for organisations at the beginning of their risk governance journey.
Medium Packages (Enhanced Protection Tier)
Target Clients:
Growing organisations, regulated-sector companies, and businesses that have some risk management activity in place but need to improve its rigour, coverage, and governance credibility — particularly those facing regulatory examinations, certification audits, or enterprise customer security requirements.
Sub-Services in Scope
- Comprehensive Enterprise Risk Assessment
- Control Effectiveness Testing and Residual Risk Validation
- Third-Party and Supply Chain Risk Assessment
- Multi-Framework Regulatory Compliance Mapping
- Risk Appetite Assessment and Alignment Analysis
- Governance Framework, Reporting Structure, and Remediation Workshop
Objective:
Deliver a comprehensive, methodology-compliant risk assessment with validated control effectiveness, complete regulatory compliance mapping, and a governance-grade treatment plan that satisfies the requirements of regulators, certification bodies, and enterprise customers simultaneously.
Value Delivered:
A materially improved risk management programme with validated findings, credible residual risk ratings, multi-framework compliance evidence, and the governance infrastructure needed to sustain risk management between formal assessment cycles.
Advanced Packages (Enterprise Resilience Tier)
Target Clients:
Large enterprises, financial institutions, regulated entities, government bodies, and complex organisations that require enterprise-grade risk governance, quantitative risk analysis, continuous monitoring, and strategic board-level risk programme advisory.
Sub-Services in Scope
- Full Enterprise Risk Assessment with Quantitative Analysis
- Adversarial Risk Scenario Testing and Red Team Exercise
- Continuous Risk Monitoring and Intelligence Integration Programme
- Enterprise Risk Architecture and Governance Design
- Integrated Privacy, Operational, and Strategic Risk Programme
- Board Risk Governance Advisory, Metrics Programme, and Executive Reporting
Objective:
Deliver a world-class enterprise risk assessment and mitigation programme that satisfies the most demanding governance, regulatory, and strategic requirements — integrating quantitative analysis, continuous monitoring, adversarial scenario testing, and ongoing advisory into a comprehensive risk management ecosystem.
Value Delivered:
Complete risk governance visibility across the enterprise, continuous assurance infrastructure, quantitative risk intelligence for strategic decision-making, and the expert partnership needed to build and sustain a risk management programme that meets the expectations of the most demanding regulatory and governance environments.
Basic Packages (Foundation Tier)
Target Clients:
Small and medium-sized organisations, early-stage companies, and businesses establishing their first structured risk management programme — typically those who recognise the need for documented risk governance but have not yet built internal risk management infrastructure.
Sub-Services in Scope :
- Foundational Risk Identification Assessment
- Risk Register Development and Population
- Critical Risk Prioritisation and Treatment Plan
- Basic Regulatory Compliance Gap Assessment
- ISO 31000 and ISO 27001 Risk Assessment Alignment Review
Objective:
Establish a credible, documented risk baseline that identifies the most material exposures, assigns clear ownership, and provides a prioritised treatment roadmap — giving the organisation a structured starting point for risk management rather than an ad hoc approach.
Value Delivered:
A risk register the organisation can stand behind, a treatment plan that leadership can commit to, and compliance documentation that satisfies foundational regulatory and customer due diligence requirements — delivered efficiently for organisations at the beginning of their risk governance journey.
Medium Packages (Enhanced Protection Tier)
Target Clients:
Growing organisations, regulated-sector companies, and businesses that have some risk management activity in place but need to improve its rigour, coverage, and governance credibility — particularly those facing regulatory examinations, certification audits, or enterprise customer security requirements.
Sub-Services in Scope
- Comprehensive Enterprise Risk Assessment
- Control Effectiveness Testing and Residual Risk Validation
- Third-Party and Supply Chain Risk Assessment
- Multi-Framework Regulatory Compliance Mapping
- Risk Appetite Assessment and Alignment Analysis
- Governance Framework, Reporting Structure, and Remediation Workshop
Objective:
Deliver a comprehensive, methodology-compliant risk assessment with validated control effectiveness, complete regulatory compliance mapping, and a governance-grade treatment plan that satisfies the requirements of regulators, certification bodies, and enterprise customers simultaneously.
Value Delivered:
A materially improved risk management programme with validated findings, credible residual risk ratings, multi-framework compliance evidence, and the governance infrastructure needed to sustain risk management between formal assessment cycles.
Advanced Packages (Enterprise Resilience Tier)
Target Clients:
Large enterprises, financial institutions, regulated entities, government bodies, and complex organisations that require enterprise-grade risk governance, quantitative risk analysis, continuous monitoring, and strategic board-level risk programme advisory.
Sub-Services in Scope
- Full Enterprise Risk Assessment with Quantitative Analysis
- Adversarial Risk Scenario Testing and Red Team Exercise
- Continuous Risk Monitoring and Intelligence Integration Programme
- Enterprise Risk Architecture and Governance Design
- Integrated Privacy, Operational, and Strategic Risk Programme
- Board Risk Governance Advisory, Metrics Programme, and Executive Reporting
Objective:
Deliver a world-class enterprise risk assessment and mitigation programme that satisfies the most demanding governance, regulatory, and strategic requirements — integrating quantitative analysis, continuous monitoring, adversarial scenario testing, and ongoing advisory into a comprehensive risk management ecosystem.
Value Delivered:
Complete risk governance visibility across the enterprise, continuous assurance infrastructure, quantitative risk intelligence for strategic decision-making, and the expert partnership needed to build and sustain a risk management programme that meets the expectations of the most demanding regulatory and governance environments.
WHAT OUR CUSTOMERS SAY
Codec Networks transforms our cybersecurity posture with practical insights, enabling
faster risk mitigation and stronger regulatory compliance across operations
-
“Vijay Pratap is a passionate Software Developer specializing in building scalable web applications and APIs. He enjoys solving complex problems with clean,”
Vijay Pratap
Developer -
“Deepak is a passionate Software Developer specializing in building scalable web applications and APIs. He enjoys solving complex problems with clean,”
Deepak
Developer -
“KumKum is a passionate Software Developer specializing in building scalable web applications and APIs. He enjoys solving complex problems with clean,”
KumKum
Developer
“Vijay Pratap is a passionate Software Developer specializing in building scalable web applications and APIs. He enjoys solving complex problems with clean,”
Vijay Pratap
Developer
“Deepak is a passionate Software Developer specializing in building scalable web applications and APIs. He enjoys solving complex problems with clean,”
Deepak
Developer
“KumKum is a passionate Software Developer specializing in building scalable web applications and APIs. He enjoys solving complex problems with clean,”
KumKum
DeveloperINDUSTRY & SECURITY THREAT LANDSCAPE
Mapping the industry and threat landscape through a risk management lens enables organisations to build risk programmes that address genuine
exposure rather than generic categories — directing resources where they produce the greatest reduction in actual organisational risk.
Business & Cyber Challenges
- Financial institutions operate under the most concentrated regulatory risk assessment obligation of any sector — with In country –norms and guidelines, each imposing specific risk management requirements that many organisations are meeting in form rather than substance.
- Digital transformation has extended the BFSI risk landscape substantially — cloud adoption, API banking, mobile platforms, and digital lending have each introduced risk categories that legacy risk frameworks were not designed to address.
- Third-party and outsourcing concentration risk is systemic in BFSI — core banking, payment processing, and analytics functions are routinely dependent on a small number of critical providers whose failure would cascade across multiple institutions simultaneously.
- Operational resilience requirements are tightening, with regulators demanding demonstrated ability to recover from severe but plausible disruption scenarios — a standard that requires risk assessment with operational consequence analysis rather than probability estimation alone.
- Fraud risk, increasingly technology-mediated, requires risk assessment methodologies that can address rapidly evolving threat patterns rather than historical frequency data.
How Risk Assessment & Mitigation Strategy Helps
- Produces a regulatory-compliant risk assessment framework that satisfies and In country- norms and guidelines requirements simultaneously — reducing the compliance evidence burden while improving the quality of governance outcomes.
- Addresses digital transformation risk through systematic assessment of cloud, API, and mobile risk categories with the specialist methodology these environments require.
- Third-party concentration risk assessment identifies systemic dependencies and provides the governance evidence that regulators increasingly require from financial institutions regarding supply chain risk management.
- Operational resilience risk analysis provides the scenario-based assessment that regulators expect — mapping risk findings to recovery capability and identifying gaps that would prevent meeting recovery time and point objectives.
- Provides a complete risk management evidence package that supports regulatory examination, internal audit, and board risk oversight simultaneously.
INDUSTRY & SECURITY THREAT LANDSCAPE
Mapping the industry and threat landscape through a risk management lens enables organisations to build risk programmes that address genuine
exposure rather than generic categories — directing resources where they produce the greatest reduction in actual organisational risk.
Industry Landscape
Business & Cyber Challenges
- Financial institutions operate under the most concentrated regulatory risk assessment obligation of any sector — with In country –norms and guidelines, each imposing specific risk management requirements that many organisations are meeting in form rather than substance.
- Digital transformation has extended the BFSI risk landscape substantially — cloud adoption, API banking, mobile platforms, and digital lending have each introduced risk categories that legacy risk frameworks were not designed to address.
- Third-party and outsourcing concentration risk is systemic in BFSI — core banking, payment processing, and analytics functions are routinely dependent on a small number of critical providers whose failure would cascade across multiple institutions simultaneously.
- Operational resilience requirements are tightening, with regulators demanding demonstrated ability to recover from severe but plausible disruption scenarios — a standard that requires risk assessment with operational consequence analysis rather than probability estimation alone.
- Fraud risk, increasingly technology-mediated, requires risk assessment methodologies that can address rapidly evolving threat patterns rather than historical frequency data.
How Risk Assessment & Mitigation Strategy Helps
- Produces a regulatory-compliant risk assessment framework that satisfies and In country- norms and guidelines requirements simultaneously — reducing the compliance evidence burden while improving the quality of governance outcomes.
- Addresses digital transformation risk through systematic assessment of cloud, API, and mobile risk categories with the specialist methodology these environments require.
- Third-party concentration risk assessment identifies systemic dependencies and provides the governance evidence that regulators increasingly require from financial institutions regarding supply chain risk management.
- Operational resilience risk analysis provides the scenario-based assessment that regulators expect — mapping risk findings to recovery capability and identifying gaps that would prevent meeting recovery time and point objectives.
- Provides a complete risk management evidence package that supports regulatory examination, internal audit, and board risk oversight simultaneously.
Business & Cyber Challenges
- FinTech organisations operate in a risk environment characterised by extreme speed — risk landscapes shift through product iteration, partnership evolution, and regulatory change faster than most risk programmes are designed to track.
- Regulatory obligations accumulate rapidly as FinTech organisations scale — PCI DSS, GDPR, In-country regulatory norms and guidelines digital lending guidelines, and payment system operator requirements impose risk management obligations that must be addressed simultaneously.
- Third-party API dependencies create systemic risk concentration — a FinTech whose core product depends on a small number of partner APIs carries concentration risk that generic risk frameworks do not adequately characterise.
- Investor and enterprise customer due diligence requirements for risk management documentation are intensifying — FinTechs without structured, credible risk programmes are increasingly disadvantaged in funding and enterprise sales processes.
How Risk Assessment & Mitigation Strategy Helps
- Provides a risk assessment framework designed for the pace of FinTech operations — structured enough to satisfy regulatory requirements, agile enough to reflect the risk environment as the organisation evolves.
- Multi-regulatory compliance mapping produces risk assessment outputs that satisfy PCI DSS, GDPR, In-country regulatory norms and guidelines, and sector-specific requirements from a single engagement — reducing the duplicated assessment effort that growing FinTechs otherwise face.
- Third-party API risk assessment addresses concentration risk with the analytical depth that standard vendor management processes do not provide.
- Produces the risk management documentation that investors and enterprise customers require for due diligence — converting risk management from a governance obligation into a commercial enabler.
Business & Cyber Challenges
- Healthcare organisations carry the dual burden of patient safety risk and information security risk — a combination that requires risk assessment methodology capable of addressing consequence in clinical, operational, and data protection dimensions simultaneously.
- Regulatory obligations across HIPAA, GDPR, ISO 27018, and In-country regulatory norms and guidelines impose specific risk assessment requirements for personal health data that many healthcare organisations address through compliance activity rather than genuine risk management.
- Clinical system availability risk carries a consequence profile unlike any other sector — the failure of clinical information systems directly affects patient safety outcomes, creating a risk category that requires specialised assessment methodology.
- Digital health transformation — EHR adoption, telemedicine, connected devices, AI diagnostics — has expanded the healthcare risk landscape substantially, introducing technology risk categories that clinical governance frameworks were not designed to address.
How Risk Assessment & Mitigation Strategy Helps
- Delivers risk assessment that addresses patient safety, operational continuity, and information security risk within a unified framework — reflecting the interconnected nature of these risk categories in healthcare rather than treating them as separate domains.
- Produces DPIA-integrated risk documentation that satisfies GDPR, HIPAA, and In-country regulatory norms and guidelines obligations for health data processing — with the structured evidence that privacy regulators require.
- Clinical system availability risk is assessed with consequence analysis that reflects patient safety implications — providing the governance evidence that healthcare regulators and accreditation bodies increasingly require.
- Digital health risk assessment provides the methodology and coverage needed to govern the expanded risk landscape that technology adoption has created — protecting patient safety while enabling the clinical benefits that digital health delivers.
Business & Cyber Challenges
- Retail organisations face a risk landscape shaped by extreme concentration in seasonal revenue periods — a risk profile where operational failure during a narrow time window can cause financial damage disproportionate to the duration of the disruption.
- Customer data risk is structurally significant in retail — PII, payment card data, and behavioural data carried across multiple platforms and third-party integrations create a privacy risk footprint that is rarely fully mapped.
- Supply chain and logistics risk has been elevated by recent experience of supply chain disruption — retail organisations need risk assessments that address physical and digital supply chain dependencies with equal rigour.
- PCI DSS compliance obligations impose specific risk assessment requirements on retail organisations processing payment card data — requirements that must be addressed with documented evidence rather than management assertion.
How Risk Assessment & Mitigation Strategy Helps
- Seasonal concentration risk is assessed with the operational consequence analysis that its disproportionate financial impact warrants — identifying exposures that standard annual risk assessments, conducted outside peak periods, systematically understate.
- Customer data risk mapping provides the comprehensive PII and payment data risk assessment that GDPR, In-country regulatory norms and guidelines, and PCI DSS obligations require — with documentation structured for regulatory and certification purposes.
- Supply chain risk assessment addresses both physical logistics and digital integration dependencies — providing a complete picture of the supply chain risk that increasingly drives retail operational disruption.
- PCI DSS compliance risk documentation provides the evidence base that payment brands and acquiring banks require — demonstrating genuine risk management rather than compliance attestation.
Business & Cyber Challenges
- Telecom operators carry national critical infrastructure status in most jurisdictions, imposing risk management obligations that extend beyond standard corporate governance to national security considerations.
- Network architecture transformation — 5G, virtualised network functions, cloud-native infrastructure — has fundamentally changed the risk landscape for telecom, introducing technology risk categories that legacy risk frameworks do not adequately address.
- Customer data risk is structurally significant for telecom operators who process location data, communication metadata, and financial information for millions of subscribers simultaneously.
- Regulatory risk is multi-layered in telecom — TRAI, In country- norms and guidelines, data protection legislation, and cybersecurity obligations from critical infrastructure frameworks must all be addressed within the risk management programme.
How Risk Assessment & Mitigation Strategy Helps
- Delivers risk assessment calibrated for critical infrastructure obligations — addressing national security risk dimensions alongside standard information security and operational risk categories.
- 5G and network transformation risk is assessed with the technical depth that virtual network function architecture, network slicing, and cloud-native deployment require — beyond what generic risk frameworks can address.
- Multi-regulatory compliance mapping produces risk documentation that satisfies TRAI, In country- norms and guidelines, and data protection obligations simultaneously — reducing duplicated assessment effort across the complex regulatory landscape.
- Subscriber data risk assessment addresses the scale, sensitivity, and regulatory significance of the personal data that telecom operators process — with documentation appropriate for regulatory examination and data protection authority enquiries.
Business & Cyber Challenges
- IT service providers and SaaS organisations carry risk management obligations that are multiplied by their customer relationships — the risk management standards they must meet are increasingly defined by the most demanding customers and regulatory environments they serve.
- ISO 27001 certification has become a baseline requirement in enterprise IT procurement — but certification without genuine risk management substance is increasingly insufficient as customer security assessments become more sophisticated.
- Multi-tenant risk is structurally complex in SaaS — risk events in one tenant environment can have consequences for others, creating risk interdependencies that require specialist assessment methodology.
- Rapid product development creates a risk accumulation dynamic where new features, integrations, and platform changes introduce risk faster than governance processes typically identify and address it.
How Risk Assessment & Mitigation Strategy Helps
- ISO 27001 risk assessment alignment provides the documented methodology and risk register that certification auditors require — structured for certification success rather than generic compliance adequacy.
- Customer-facing risk documentation provides the evidence that enterprise customers and procurement processes require — converting risk management into a commercial differentiator.
- Multi-tenant risk assessment addresses the interdependency and isolation risks that SaaS architectures create — providing governance evidence of responsible multi-tenant risk management.
- Rapid-development risk governance framework integrates risk assessment into development and release processes — ensuring risk accumulation is identified and managed continuously rather than discovered during periodic assessments.
Business & Cyber Challenges
- Public sector risk management carries an accountability dimension that commercial governance does not — the consequences of inadequate risk management affect citizens rather than shareholders, creating a governance obligation that is qualitatively different from corporate risk management.
- eGov and digital identity platforms carry risk profiles shaped by extreme data sensitivity, national security implications, and availability requirements — a combination that requires risk assessment methodology capable of addressing all three simultaneously.
- Smart city infrastructure introduces physical consequence risk — failure of traffic management, utilities monitoring, or emergency response systems has safety implications that require risk assessment beyond information security considerations.
- Procurement and governance processes in government are structured around compliance demonstration rather than risk management substance, creating environments where risk management documentation meets formal requirements without delivering genuine governance value.
How Risk Assessment & Mitigation Strategy Helps
- Public sector risk assessment is structured to meet formal compliance requirements while delivering genuine governance substance — producing outputs that satisfy formal oversight requirements and actual board-level risk management needs simultaneously.
- Digital identity and eGov risk assessment addresses the data sensitivity, availability, and national security dimensions of public digital infrastructure with the specialist methodology these risk categories require.
- Smart city risk assessment integrates physical consequence analysis with information security and operational risk — providing a complete risk picture for infrastructure whose failure has public safety implications.
- Risk documentation is structured for public sector governance requirements — audit committee reporting, parliamentary accountability, and public interest transparency — reflecting the distinctive governance context of public organisations.
Business & Cyber Challenges
- Energy and utility organisations carry the most severe consequence risk profile of any sector — operational failure affects public safety, national security, and economic function in ways that make conventional risk management approaches insufficient.
- OT and ICS risk requires specialist assessment methodology that addresses the safety, availability, and integrity consequences of risk events in operational technology environments — a distinct risk domain from information technology risk.
- National and international regulatory obligations — NERC CIP, ISO 27019, sector-specific national frameworks — impose specific risk management requirements with technical evidence standards that many utility organisations struggle to meet.
- Supply chain and vendor risk is particularly consequential in energy — a single compromised component or vendor access pathway can affect operational technology with national-scale consequence.
How Risk Assessment & Mitigation Strategy Helps
- Delivers risk assessment that addresses operational consequence — including safety, availability, and integrity impacts — alongside standard information security risk categories, providing the complete risk picture that critical infrastructure governance requires.
- OT and ICS risk assessment is conducted with specialist methodology aligned to IEC 62443 — not as an extension of IT risk assessment, but as a distinct assessment addressing the specific risk characteristics of operational technology environments.
- Regulatory compliance documentation provides the technical evidence that NERC CIP, ISO 27019, and national critical infrastructure frameworks require — structured for regulatory examination and audit purposes.
- Supply chain risk assessment addresses vendor access, component integrity, and third-party concentration risk with the rigour that operational technology supply chain risk warrants.
Business & Cyber Challenges
- Transport sector risk management must address the intersection of physical safety, operational continuity, customer data protection, and cybersecurity — a multi-dimensional risk profile that few generic risk frameworks adequately address.
- Regulatory risk is multi-layered in aviation and rail — ICAO, IATA, and national aviation authorities impose safety and security requirements that intersect with cybersecurity and data protection obligations in complex ways.
- Operational dependency concentration is characteristic of transport — single points of failure in reservation systems, navigation infrastructure, and logistics management create risk exposures with potentially severe service disruption consequences.
- Third-party and partner risk is systemic in transport — airlines, airports, ground handlers, logistics providers, and maintenance organisations are interconnected in ways that create risk cascades across the sector.
How Risk Assessment & Mitigation Strategy Helps
- Multi-dimensional risk assessment addresses safety, operational, cyber, and regulatory risk within a unified framework — reflecting the interconnected nature of these categories in transport rather than addressing them through separate risk silos.
- Regulatory compliance mapping covers aviation, rail, and logistics regulatory requirements alongside cybersecurity and data protection obligations — producing compliance evidence across the full regulatory landscape.
- Operational dependency analysis identifies single points of failure and concentration risks — providing the assessment foundation for continuity planning that meets regulatory operational resilience requirements.
- Third-party and partner risk assessment maps the risk interdependencies across the transport ecosystem — enabling organisations to understand and manage risks that originate outside their direct control.
Business & Cyber Challenges
- Educational institutions carry data protection obligations for minor students that impose particularly stringent risk management requirements — obligations that are frequently under-appreciated in organisations whose governance focus is naturally on educational outcomes.
- EdTech platforms operate at the intersection of rapid technology development and sensitive user data — a combination that creates risk accumulation dynamics that governance processes often fail to track.
- Regulatory obligations across GDPR, In-country regulatory norms and guidelines, and FERPA apply simultaneously to many educational organisations — particularly those with international student populations or global platform reach.
- Reputational risk is disproportionately significant for educational institutions — a data breach or governance failure affecting student data carries institutional consequence that extends far beyond immediate financial impact.
How Risk Assessment & Mitigation Strategy Helps
- Student data risk assessment addresses the heightened protection obligations for minor data subjects — providing governance evidence of the due care that educational data protection requires.
- Multi-regulatory compliance mapping satisfies GDPR, In-country regulatory norms and guidelines, and FERPA obligations from a single assessment — reducing the compliance burden for internationally oriented educational organisations.
- Reputational risk analysis quantifies the institutional consequence of data governance failures — providing the impact assessment needed to justify appropriate investment in risk treatment.
- EdTech product risk governance framework integrates risk assessment into development and deployment processes — ensuring that student data protection obligations are addressed as platforms evolve rather than assessed retrospectively.
Threat Landscape
Threat/Challenge:
The most consequential risk management failure is not rating risks inaccurately — it is failing to identify them in the first place. Risks that are never identified are never treated, and organisations that believe their risk register is complete when it is not are operating with false assurance. Systematic blind spots are particularly common in technology risk, third-party concentration risk, and regulatory obligation completeness — areas where the knowledge required to identify risks is not uniformly distributed across the organisation.
Internal risk assessments are structurally prone to reflecting the knowledge of the people conducting them rather than the full risk universe. Emerging risk categories — new technology adoption, novel regulatory obligations, evolving threat patterns — are consistently underrepresented in assessments conducted exclusively from internal perspective. The result is a risk programme that manages what is already known while remaining systematically exposed to what is not.
How Risk Assessment & Mitigation Strategy Helps
- Applies a structured risk identification methodology that covers known, emerging, and sector-specific risk categories — not just those familiar to internal teams.
- Cross-sector risk experience surfaces risk categories that internally conducted assessments consistently miss — particularly in technology, third-party, and regulatory obligation domains.
- Threat intelligence integration ensures that the risk identification process captures current and emerging threats rather than exclusively historical risk patterns.
- Independent facilitation of risk identification workshops removes the organisational dynamics that prevent honest disclosure of risks that management is aware of but reluctant to formalise.
Threat/Challenge:
Risk registers populated without agreed, calibrated rating criteria produce outputs where risk scores reflect assessor judgement variation more than genuine differences in risk level. When 'High' likelihood means different things to different assessors, and 'Critical' impact is calibrated to different consequence scales across business units, the resulting risk register cannot support consistent prioritisation, meaningful board reporting, or credible comparison between assessment cycles.
This is not a marginal deficiency — it is a fundamental governance failure that renders risk registers unsuitable for the purposes they are supposed to serve. Boards making risk oversight decisions based on inconsistently rated registers are not exercising informed governance; they are ratifying an appearance of governance that does not reflect organisational reality.
How Risk Assessment & Mitigation Strategy Helps
- Establishes agreed likelihood and impact criteria before assessment begins — calibrated to organisational context, risk appetite, and regulatory obligations.
- Applies calibration exercises to ensure rating consistency across assessors, business units, and risk categories throughout the engagement.
- Produces a risk register where ratings carry defined meaning — enabling consistent prioritisation, comparative analysis across cycles, and credible board reporting.
- Provides rating criteria documentation that enables internal teams to apply consistent standards in ongoing risk management between formal assessment cycles.
Threat/Challenge:
Assigning residual risk ratings based on the assumed effectiveness of controls that have never been independently tested is one of the most pervasive and consequential errors in risk management practice. The gap between designed control effectiveness and operational control performance is consistently wider than organisations expect — controls exist in policy that are not implemented in practice, controls are implemented that are not operating effectively, and controls operate effectively in normal conditions but fail precisely when most needed.
False assurance from assumed control effectiveness produces residual risk registers that systematically understate actual exposure. Organisations believe they are managing risks that are, in practice, unmitigated or under-mitigated. This belief influences governance decisions, resource allocation, and regulatory representations in ways that can have severe consequences when the gap between assumed and actual control performance is eventually revealed — typically during an adverse event rather than during a review.
How Risk Assessment & Mitigation Strategy Helps
- Independent control effectiveness testing is built into the assessment methodology as a standard component, not an optional enhancement.
- Controls are tested operationally — not just documented in policy — with evidence of actual performance required before effectiveness credit is granted in residual risk calculations.
- Testing failures that reveal the gap between designed and operational control effectiveness are explicitly reported, enabling management to address false assurance rather than continue relying on it.
- Residual risk ratings in Codec Networks' assessments reflect tested control environments — providing a risk picture that governance stakeholders can rely on.
Threat/Challenge:
Third-party risk is the fastest-growing source of organisational loss across all sectors — driven by increasing operational dependence on external providers, the complexity of modern supply chains, and the frequency of adverse events originating in third-party relationships that the affected organisation did not adequately govern. Regulators across financial services, healthcare, and critical infrastructure have responded by imposing increasingly specific third-party risk management obligations — obligations that many organisations are meeting superficially rather than substantively.
Concentration risk — the dependence of multiple critical processes on a single third party or a small number of providers — is the most consequential form of supply chain risk that organisations consistently underassess. When a critical provider fails, the organisation's ability to respond depends entirely on whether it understood and prepared for the concentration risk that dependence created. Organisations that discover this concentration only when failure occurs consistently sustain more severe and more prolonged disruption than those that identified and managed it in advance.
How Risk Assessment & Mitigation Strategy Helps
- Systematic identification of all material third-party relationships provides the complete supply chain risk picture that selective vendor management produces only partially.
- Concentration risk analysis identifies dependencies where a single provider failure would cascade across multiple critical functions — surfacing the risk that causes the most severe impact when it materialises.
- Third-party security and resilience assessment provides a genuine evaluation of provider risk posture — not just contractual due diligence that reflects what providers represent rather than what they demonstrably maintain.
- Contractual risk allocation review identifies gaps between assumed and actual contractual protection — ensuring organisations understand what contractual remedies are available in adverse scenarios.
Threat/Challenge:
Risk assessment processes that produce treatment plans without accountability structures, tracking mechanisms, or implementation support consistently fail to translate identified risks into actual remediation activity. Risk registers identify risks, treatment plans document intended responses, and nothing changes. This is not a failure of intent — it is a failure of governance infrastructure. Risk treatment without named ownership, defined milestones, progress tracking, and escalation mechanisms does not produce risk reduction; it produces evidence of governance process completion.
How Risk Assessment & Mitigation Strategy Helps
- Every treatment plan produced by Codec Networks includes named accountable owners with defined roles and responsibilities for implementation.
- Implementation timelines with specific milestones and dependencies are established for every material treatment action — providing the structure needed for genuine progress tracking.
- Escalation criteria and governance reporting mechanisms are defined — ensuring that treatment delays or implementation obstacles reach appropriate governance attention rather than persisting unnoticed.
- Post-engagement implementation advisory supports organisations through the treatment plan execution phase — maintaining the momentum that the assessment generated.
Threat/Challenge:
Organisations consistently underestimate regulatory compliance risk — not because they are unaware that regulations exist, but because the scope, specificity, and enforcement seriousness of applicable obligations is frequently not fully mapped. The intersection of multiple regulatory frameworks — ISO 27001, GDPR, In-country regulatory norms and guidelines, sector-specific requirements, and In country- norms and guidelines obligations — creates compliance obligations whose aggregate scope is greater than any single internal function typically tracks. Gaps in mapping produce gaps in compliance, which produce regulatory risk that management does not know it is carrying.
How Risk Assessment & Mitigation Strategy Helps
- Systematic identification of all applicable regulatory obligations across the client's sector, jurisdiction, and operational context — closing the mapping gaps that produce unidentified compliance risk.
- Multi-framework compliance gap analysis produces a complete picture of regulatory exposure — enabling treatment prioritisation based on actual regulatory risk rather than management impression.
- Audit-ready compliance evidence documentation provides the structured proof of compliance management that regulatory examinations require.
- Regulatory horizon monitoring identifies emerging obligations that will affect the organisation's compliance risk profile — enabling proactive preparation rather than reactive compliance.
Threat/Challenge:
Most organisations have a stated risk appetite. Few have systematically verified that their actual risk posture is consistent with it. When residual risks across the enterprise are compared against formally stated risk appetite boundaries, it is common to find that accepted risks in multiple areas significantly exceed stated tolerance — not through deliberate governance decision, but through the accumulation of operational decisions made without explicit risk appetite reference. This 'silent risk acceptance' is a governance failure that boards are typically unaware of until it is revealed through an adverse event or external assessment.
How Risk Assessment & Mitigation Strategy Helps
- Risk appetite comparison analysis systematically compares residual risk ratings against stated tolerance boundaries across every risk category in the enterprise register.
- Silent risk acceptance is explicitly identified and reported — enabling boards and senior management to make conscious decisions about whether stated appetite boundaries should be revised or whether risks that exceed them should be treated.
- Risk appetite statement development facilitates the articulation of genuine, operationally meaningful appetite boundaries — rather than aspirational statements that do not translate into governance decisions.
- Periodic reassessment confirms whether risk posture remains within appetite over time — maintaining the alignment between stated and actual risk governance.
Threat/Challenge:
Risk management programmes that produce technically competent assessments but communicate poorly to governance audiences fail to deliver their governance purpose. Boards cannot exercise meaningful risk oversight based on reports they cannot interpret. Management cannot make informed resource allocation decisions based on risk registers without business consequence translation. The quality of risk governance is ultimately determined not by the technical rigour of the assessment but by whether the risk intelligence it produces reaches the right decision-makers in a form they can act on.
How Risk Assessment & Mitigation Strategy Helps
- Executive reporting is designed specifically for board and senior management audiences — translating technical risk findings into strategic consequence, financial exposure, and governance implication language.
- Risk heat maps, trending analysis, and risk appetite dashboards provide visual risk communication that enables pattern recognition without requiring detailed reading of technical assessment outputs.
- Key risk indicator development provides the forward-looking metrics that early-warning risk governance requires — complementing the retrospective picture that conventional risk registers provide.
- Multi-audience reporting design ensures that each stakeholder group receives risk information at the appropriate level of detail and in the language appropriate to their governance role.
Threat/Challenge:
Risk assessments conducted annually — or less frequently — describe the risk environment as it existed at the time of assessment. They do not describe the risk environment at the time governance decisions are being made. In organisations where technology, operations, regulatory obligations, and threat landscape are changing continuously, the gap between assessment and decision can represent a material difference in actual risk exposure. Organisations making governance decisions based on twelve-month-old risk assessments in dynamic risk environments are not practising risk governance — they are practising historical documentation review.
How Risk Assessment & Mitigation Strategy Helps
- Key risk indicators and monitoring mechanisms established during the engagement provide continuous risk visibility between formal assessment cycles.
- Trigger-based reassessment processes ensure that significant changes — technology deployments, regulatory developments, organisational restructuring, and adverse events — prompt reassessment of affected risk areas rather than waiting for the scheduled annual cycle.
- Recurring assessment programmes provide regular formal reassessment for organisations in dynamic risk environments or under heightened regulatory scrutiny.
- Threat intelligence integration ensures that the risk picture is updated with current threat developments between formal cycles.
Threat/Challenge:
Insider threat and advanced persistent threat risks present distinctive assessment challenges — they operate through legitimate access mechanisms, they are designed to avoid detection, and their impact is often not apparent until significant damage has already occurred. Standard risk assessment methodologies that focus on probability-impact matrices struggle to adequately represent these threat categories because their probability is difficult to estimate with precision and their impact can be catastrophic rather than proportional. The consequence is that these risks are frequently underrepresented in risk registers relative to their actual threat significance.
How Risk Assessment & Mitigation Strategy Helps
- Scenario-based risk assessment methodology is applied to insider and APT risks — focusing on consequence and control effectiveness rather than probability estimation alone.
- Access and privilege risk analysis identifies the pathways that both insider misuse and external adversarial actors would exploit — enabling preventive control improvement rather than detection-only response.
- Control effectiveness testing specifically addresses the detection and containment controls relevant to insider and persistent threat scenarios — validating that response capability matches the threat profile.
- Residual risk for these categories is assessed with the honest acknowledgement of inherent uncertainty — providing governance stakeholders with a realistic rather than artificially precise risk picture.
BLOGS & ARTICLES
Codec Networks’ blogs and industry articles provide actionable insights, helping enterprises navigate
risk management challenges, regulatory shifts, and emerging risk governance trends.
Blog 1: BFSI and FinTech
FinTech Scaling Risk: The Risk Management Debt That Accumulates Between Funding Rounds and How to Address It Before Regulators Find It
Read FurtherBlog2 : IT / ITES / SaaS / Telecom
SaaS Multi-Tenant Risk: How to Assess and Document the Risk That One Tenant's Data Will Affect Another — and Why Enterprise Customers Are Starting to Ask
Read FurtherBlog3 : Power, Aviation, Railways, and Transport
Supply Chain Concentration Risk in Logistics: Why the Sector's Operational Dependence Creates Risk Register Gaps That Standard Third-Party Assessment Does Not Catch
Read FurtherBlog 4: Industry Infrastructure & Production / E-Commerce
PCI DSS v4.0 Risk Assessment Requirements: What Has Changed and What E-Commerce Organisations Need to Update in Their Risk Management Programmes
Read FurtherFREQUENTLY ASKED QUESTION
Asking the right questions is the first step toward security; our FAQs
deliver clear, concise, and practical guidance for clients
CODEC NETWORKS OTHER RELATED SERVICES
Codec Networks doesn't just find your risks - we build the roadmap that resolves every single one.
-
Brand monitoring and threat detection track online reputation and identify cyber threats to protect corporate image.
-
Cyber reputation risk management monitors and mitigates online threats to safeguard brand trust and stakeholder confidence.
-
Crisis management and incident response coordinate actions to contain cyber incidents and minimize organizational impact effectively.
-
Data leak and PII protection prevent unauthorized exposure of personal information to ensure privacy and regulatory compliance.
-
Competitive intelligence gathers and analyzes market data to inform strategic decisions and gain business advantages.
Brand monitoring and threat detection track online reputation and identify cyber threats to protect corporate image.
Cyber reputation risk management monitors and mitigates online threats to safeguard brand trust and stakeholder confidence.
Crisis management and incident response coordinate actions to contain cyber incidents and minimize organizational impact effectively.
Data leak and PII protection prevent unauthorized exposure of personal information to ensure privacy and regulatory compliance.
Competitive intelligence gathers and analyzes market data to inform strategic decisions and gain business advantages.