

On this page
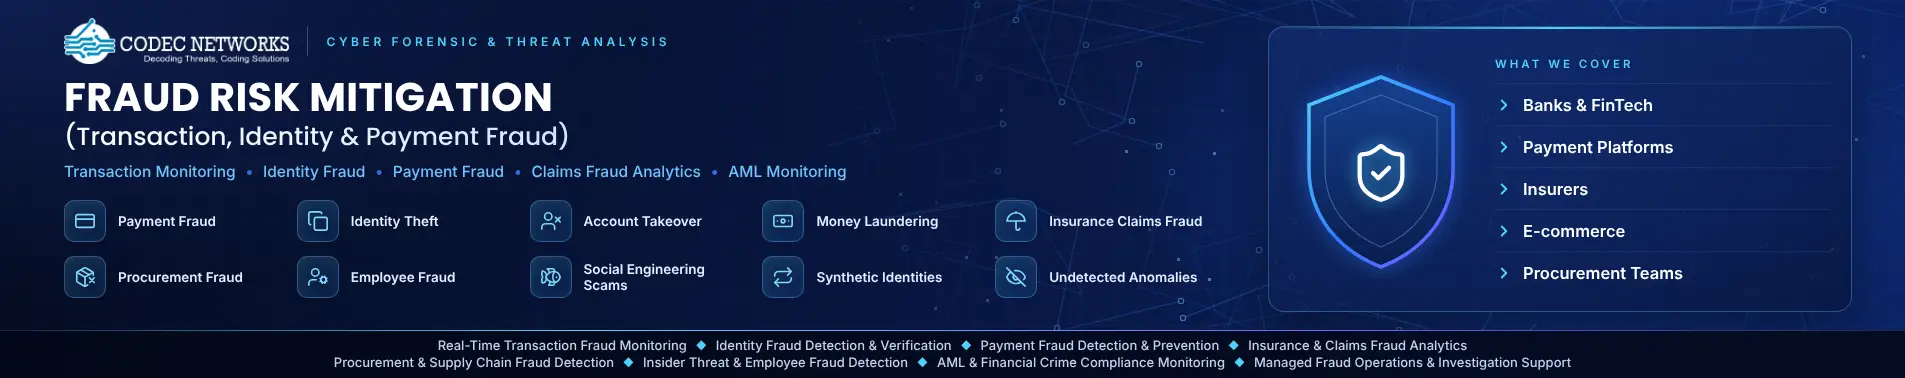
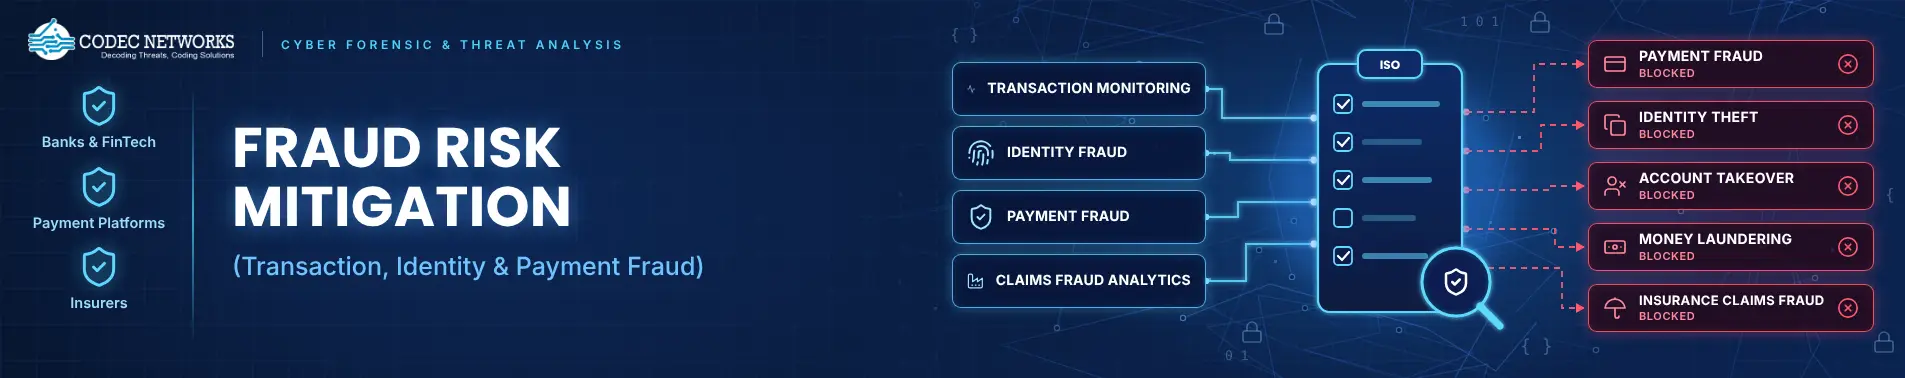

Fraud Risk Mitigation
Fraud Risk Mitigation at Codec Networks refers to a comprehensive suite of cybersecurity and financial intelligence services that enables organizations to proactively identify, detect, prevent, and respond to fraud threats targeting their financial operations, digital channels, customer relationships, and business processes. This service leverages advanced AI-driven analytics, behavioral intelligence, real-time transaction monitoring, and deep threat intelligence capabilities to detect fraudulent activity across payment ecosystems, identity verification workflows, procurement processes, insurance claims, and digital banking channels—before fraud causes measurable financial or reputational damage.
The service is designed to provide end-to-end fraud visibility across complex organizational ecosystems by identifying transaction anomalies, identity manipulation, synthetic fraud patterns, insider threats, and coordinated fraud campaigns targeting financial operations. It combines automated detection with expert-driven forensic analysis, enabling faster fraud intervention and significantly reducing the time required to identify and neutralize fraud attempts. By delivering real-time risk scoring, AI-powered investigation tools, and structured incident response capabilities, these services minimize the dwell time of fraud activity within organizational systems.
By integrating proactive fraud intelligence, continuous monitoring, and coordinated response capabilities, Codec Networks' Fraud Risk Mitigation services help organizations protect financial integrity, maintain regulatory compliance, and safeguard customer trust in an increasingly complex and fraud-prone digital environment. These services are designed to evolve continuously alongside the fraud threat landscape—ensuring that organizational defenses remain effective against both established and emerging fraud typologies across BFSI, insurance, healthcare, retail, manufacturing, and technology sectors.
Industry Significance
In today’s digital economy, fraud is a rapidly growing threat to financial integrity and customer trust. Proactive fraud risk mitigation is now strategic necessity for protecting businesses, reducing financial losses, ensuring operational resilience, and maintaining long-term organizational credibility across industries.
Read More
Service Relevance
Fraud Risk Mitigation services are essential for organizations navigating today's complex digital financial environment. They enable proactive detection of fraudulent activity, financial crime, and identity exploitation, ensuring organizations protect customer assets, maintain regulatory compliance, and preserve financial integrity.
Read More
Benefits to Customers
Fraud Risk Mitigation Services offered by Codec Networks deliver significant value by protecting organizational financial integrity, enabling real-time fraud detection, improving operational efficiency, and ensuring continuous compliance with evolving financial crime and regulatory requirements across complex digital environments.
Read More
Fraud Risk Mitigation
SERVICE FEATURES AND DELIVERY FRAMEWORK
Codec Networks' delivers real-time fraud risk mitigation with structured methodologies, standardized
controls, measurable KPIs, and globally aligned financial crime prevention service excellence
Fraud Risk Mitigation services are essential for organizations navigating today's complex digital financial environment. They enable proactive detection of fraudulent activity, financial crime, and identity exploitation, ensuring organizations protect customer assets, maintain regulatory compliance, and preserve financial integrity.
Fraud Risk Mitigation services are essential in modern digital financial ecosystems, enabling real-time fraud detection, centralized intelligence, and rapid intervention. They help organizations protect financial integrity, secure customer assets, and defend against evolving fraud typologies and financial crime threats.
Sub-Services offered includes:
1. Real-Time Transaction Fraud Monitoring
- Continuous 24/7 monitoring of financial transactions across payment channels, digital banking, and e-commerce platforms.
- Real-time fraud scoring using AI models analyzing transaction context, behavioral signals, and risk indicators.
- Prioritization of fraud alerts using severity and financial impact levels to focus on high-risk events.
- Integration with transaction authorization systems for seamless real-time fraud decision embedding.
- Automated notification workflows for rapid escalation and coordinated fraud response actions.
2. Identity Fraud Detection & Verification
- Multi-factor identity verification integrating biometric authentication, document validation, and database intelligence.
- Detection of synthetic identity fraud through cross-referencing identity attributes across multiple intelligence sources.
- Monitoring of identity anomalies including unusual account access patterns and profile modification activity.
- Dark web surveillance for compromised identity credentials and personal financial data exposure.
- Real-time alerting on identity exploitation attempts and account takeover indicators.
3. Payment Fraud Detection & Prevention
- AI-driven detection of card-not-present fraud, account takeover, and unauthorized payment initiation.
- Behavioral biometrics analyzing device interaction patterns to authenticate users during payment transactions.
- Real-time network analysis identifying organized fraud rings exploiting multiple payment accounts.
- Velocity monitoring detecting unusual transaction frequency, amount patterns, and geographic anomalies.
- Integration with payment processing systems for seamless fraud risk assessment at transaction authorization.
4. Insurance & Claims Fraud Analytics
- Machine learning models analyzing claim characteristics, provider patterns, and claimant behavior for fraud signals.
- Network analysis identifying organized fraud rings connecting claimants, providers, and intermediaries.
- Natural language processing analyzing claims documentation for fabrication indicators and misrepresentation.
- Predictive fraud scoring at claims submission enabling early high-risk case identification before settlement.
- Post-settlement fraud investigation support including forensic analysis and evidence documentation.
5. Procurement & Supply Chain Fraud Detection
- AI-driven invoice analysis detecting anomalies in amounts, vendor details, and approval workflow patterns.
- Vendor verification and ongoing monitoring for identity fraud, account compromise, and impersonation.
- Document intelligence detecting fabricated invoices, contracts, and procurement authorization documents.
- Real-time procure-to-pay monitoring identifying approval bypass, threshold manipulation, and segregation violations.
- Network analytics identifying kickback arrangements and undisclosed vendor-employee conflict relationships.
6. Insider Threat & Employee Fraud Detection
- Behavioral analytics monitoring employee access patterns, system activity, and transaction authorization behavior.
- Anomaly detection identifying unusual data access, financial system manipulation, and policy violations.
- User and Entity Behavior Analytics (UEBA) establishing behavioral baselines for fraud deviation detection.
- Integration with HR systems and access management platforms for contextual fraud risk assessment.
- Confidential fraud reporting mechanisms supporting whistleblower-based fraud intelligence collection.
7. AML & Financial Crime Compliance Monitoring
- Automated suspicious activity monitoring aligned with AML regulatory reporting obligations.
- Transaction pattern analysis detecting money laundering indicators including structuring, layering, and integration.
- Customer risk profiling and ongoing monitoring for elevated financial crime risk indicators.
- Regulatory reporting workflow management supporting SAR filing and AML compliance documentation.
- Integration with sanctions screening and PEP (politically exposed persons) watchlist databases.
8. Managed Fraud Operations & Investigation Support
- End-to-end management of fraud monitoring platforms, analytics tools, and investigation case management.
- Continuous optimization of fraud detection models to improve accuracy and reduce false positive rates.
- Expert fraud analyst support providing specialized investigation and case resolution capabilities.
- Integration with legal, compliance, and financial operations teams for coordinated fraud response.
- Scalability management supporting growing transaction volumes and evolving fraud risk environments.
Project / Service Delivery Methodology for Fraud Risk Mitigation Services delivered by Codec Networks is a structured, lifecycle-driven approach aligned with global best practices such as ITIL, ISO 27001, and NIST Cybersecurity Framework. The methodology ensures consistent, scalable, and measurable fraud mitigation service delivery across all sub-services.
Codec Networks' overall Service Delivery methodology comprises of:
1. Assessment & Requirement Analysis Phase
This initial phase establishes a strong foundation by understanding the client's fraud risk landscape and mitigation requirements.
- Stakeholder discussions to identify fraud risk appetite, financial operations, and priority fraud typologies
- Assessment of existing fraud controls, detection capabilities, and operational vulnerability gaps
- Gap analysis against industry fraud prevention best practices and regulatory compliance requirements
- Identification of critical fraud risk exposure areas, high-value attack vectors, and control weaknesses
Outcome: A detailed fraud risk assessment report, defined mitigation scope, and tailored fraud detection strategy.
2. Solution Design & Architecture
In this phase, a customized fraud risk mitigation architecture is designed for the client environment.
- Selection and configuration planning of fraud detection platforms and AI analytics tools
- Definition of data sources, integration points, and fraud signal flow architecture
- Fraud use-case development including detection scenarios, model logic, and alert threshold design
- Design of dashboards, reporting structures, and escalation and response workflows
Outcome: A scalable, intelligence-driven fraud mitigation architecture aligned with business and regulatory requirements.
3. Implementation & Integration
This phase focuses on deploying the fraud mitigation solution and integrating it into the client's operational environment.
- Deployment and configuration of fraud detection platforms and AI analytics models
- Integration with payment systems, identity platforms, procurement tools, and claims processing environments
- Data source onboarding, model training, and fraud alert workflow configuration
- Configuration of investigation case management and regulatory reporting workflows
Outcome: A fully operational fraud mitigation environment with comprehensive financial fraud visibility and detection.
4. Model Development & Fine-Tuning
Once implementation is complete, fraud detection models are optimized for accuracy and operational effectiveness.
- Development of industry-specific fraud detection use cases and behavioral analytics models
- Model tuning to reduce false positives and improve fraud signal accuracy
- Baseline behavioral analysis establishing normal transaction and identity patterns for anomaly detection
- Validation through historical fraud data testing and simulated fraud scenario exercises
Outcome: Highly optimized fraud detection capabilities with improved accuracy and reduced false positive rates.
5. 24/7 Monitoring & Managed Fraud Operations
This is the core operational phase executing continuous fraud monitoring and response.
- Round-the-clock monitoring by fraud analysts and data science professionals
- Real-time fraud alert triaging, prioritization, and escalation to investigation teams
- Fraud case investigation and response aligned with defined response playbooks
- Integration with financial operations, legal, and compliance teams for coordinated intervention
Outcome: Proactive fraud detection, rapid intervention, and minimized financial fraud losses.
6. Incident Response & Investigation Support
This phase ensures effective investigation and resolution of detected fraud incidents.
- Fraud incident classification and severity-based response prioritization
- Forensic analysis and evidence collection for legal enforcement and regulatory reporting
- Coordination with internal teams and law enforcement for organized fraud network investigation
- Post-incident review and fraud pattern documentation for continuous detection improvement
Outcome: Reduced financial impact of fraud incidents and strengthened fraud mitigation capabilities.
7. Compliance Management & Reporting
Ensures alignment with regulatory requirements and governance transparency in fraud operations.
- Continuous compliance monitoring aligned with AML regulations, PCI-DSS, and consumer protection standards
- Automated generation of fraud risk and compliance reports (daily, weekly, monthly)
- Audit support and fraud evidence documentation for regulatory inspections
- KPI and SLA tracking including MTTD, MTTR, detection accuracy, and false positive rates
Outcome: Audit-ready environment with clear visibility into fraud mitigation performance and compliance posture.
8. Continuous Improvement & Optimization
A feedback-driven phase enhancing fraud mitigation quality and adapting to evolving fraud threats.
- Regular review of fraud incidents, emerging typologies, and detection performance metrics
- Updating fraud detection models based on new intelligence and confirmed fraud patterns
- Platform tuning and analytics optimization for sustained detection accuracy
- Periodic fraud risk assessments and mitigation maturity evaluations
Outcome: An adaptive, continuously improving fraud mitigation framework aligned with the evolving fraud landscape.
9. Governance & Service Management
Ensures structured service delivery aligned with agreed fraud mitigation service levels.
- SLA management and service performance reviews with defined governance mechanisms
- Stakeholder reporting on fraud mitigation outcomes and financial loss prevention
- Change and configuration management for fraud detection scope and coverage
- Documentation and knowledge management for fraud mitigation processes and investigations
Outcome: Transparent, accountable, and high-quality fraud risk mitigation service delivery aligned with business expectations.
|
Standard / Framework |
Description |
Key Controls / Practices Applied |
Relevance to Fraud Risk Mitigation |
|
ISO/IEC 27001 |
Global Information Security Management System standard. |
Risk assessment, access control, incident management, asset protection. |
Ensures structured security governance supporting fraud risk management practices. |
|
ISO/IEC 27002 |
Guidance on implementing security controls. |
Monitoring, logging, operational security, fraud-related controls. |
Strengthens fraud detection configuration and operational control implementation. |
|
NIST Cybersecurity Framework |
Framework for managing and reducing cybersecurity risks. |
Identify, Protect, Detect, Respond, Recover functions. |
Aligns fraud mitigation with proactive threat detection and response lifecycle. |
|
PCI DSS |
Security standard for payment card data handling. |
Fraud monitoring, access control, vulnerability management, audit trails. |
Enables compliant fraud monitoring for payment transaction environments. |
|
GDPR |
Regulation for personal data protection and privacy. |
Data protection, breach notification, data minimization, auditability. |
Ensures fraud monitoring supports privacy compliance and data breach detection. |
|
ISO/IEC 20000 |
International standard for IT Service Management. |
Service delivery, incident handling, SLA management, change management. |
Ensures structured, SLA-driven fraud mitigation service delivery. |
|
SOC 2 |
Framework for managing customer data security principles. |
Security, availability, processing integrity, confidentiality, privacy. |
Validates reliability and integrity of fraud monitoring and reporting services. |
|
COBIT |
Framework for enterprise IT governance and control. |
Governance processes, risk management, performance measurement. |
Supports alignment of fraud mitigation with governance requirements. |
|
CIS Controls |
Prioritized cybersecurity best practices. |
Continuous monitoring, log management, incident response. |
Enhances fraud detection capabilities and operational security monitoring. |
Please Note –
- Services are delivered in alignment with recognized international security standards ensuring consistent methodology and technical rigor.
- Standard alignment guides service depth and structure but does not imply certification, accreditation, or regulatory approval.
- Coverage is limited to controls, practices, and systems mapped to the agreed service scope and selected standards.
- The service evaluates fraud risk posture at the time of assessment and does not guarantee future risk elimination.
- Liability is limited to professional services performed under the agreed engagement terms.
- Responsibility for remediation, operational decisions, and ongoing compliance remains with the client organization.
- Total liability for all services is strictly limited to the international standards as far as possible as agreed in contracted engagement value. Codec Networks expressly excludes any indirect, financial, operational, incidental, punitive, or consequential damages, which may arise due to any coincidental events, or changes in international standards guidelines time to time.
Fraud Risk Mitigation services are essential for organizations navigating today's complex digital financial environment. They enable proactive detection of fraudulent activity, financial crime, and identity exploitation, ensuring organizations protect customer assets, maintain regulatory compliance, and preserve financial integrity.
Fraud Risk Mitigation services are essential in modern digital financial ecosystems, enabling real-time fraud detection, centralized intelligence, and rapid intervention. They help organizations protect financial integrity, secure customer assets, and defend against evolving fraud typologies and financial crime threats.
Sub-Services offered includes:
1. Real-Time Transaction Fraud Monitoring
- Continuous 24/7 monitoring of financial transactions across payment channels, digital banking, and e-commerce platforms.
- Real-time fraud scoring using AI models analyzing transaction context, behavioral signals, and risk indicators.
- Prioritization of fraud alerts using severity and financial impact levels to focus on high-risk events.
- Integration with transaction authorization systems for seamless real-time fraud decision embedding.
- Automated notification workflows for rapid escalation and coordinated fraud response actions.
2. Identity Fraud Detection & Verification
- Multi-factor identity verification integrating biometric authentication, document validation, and database intelligence.
- Detection of synthetic identity fraud through cross-referencing identity attributes across multiple intelligence sources.
- Monitoring of identity anomalies including unusual account access patterns and profile modification activity.
- Dark web surveillance for compromised identity credentials and personal financial data exposure.
- Real-time alerting on identity exploitation attempts and account takeover indicators.
3. Payment Fraud Detection & Prevention
- AI-driven detection of card-not-present fraud, account takeover, and unauthorized payment initiation.
- Behavioral biometrics analyzing device interaction patterns to authenticate users during payment transactions.
- Real-time network analysis identifying organized fraud rings exploiting multiple payment accounts.
- Velocity monitoring detecting unusual transaction frequency, amount patterns, and geographic anomalies.
- Integration with payment processing systems for seamless fraud risk assessment at transaction authorization.
4. Insurance & Claims Fraud Analytics
- Machine learning models analyzing claim characteristics, provider patterns, and claimant behavior for fraud signals.
- Network analysis identifying organized fraud rings connecting claimants, providers, and intermediaries.
- Natural language processing analyzing claims documentation for fabrication indicators and misrepresentation.
- Predictive fraud scoring at claims submission enabling early high-risk case identification before settlement.
- Post-settlement fraud investigation support including forensic analysis and evidence documentation.
5. Procurement & Supply Chain Fraud Detection
- AI-driven invoice analysis detecting anomalies in amounts, vendor details, and approval workflow patterns.
- Vendor verification and ongoing monitoring for identity fraud, account compromise, and impersonation.
- Document intelligence detecting fabricated invoices, contracts, and procurement authorization documents.
- Real-time procure-to-pay monitoring identifying approval bypass, threshold manipulation, and segregation violations.
- Network analytics identifying kickback arrangements and undisclosed vendor-employee conflict relationships.
6. Insider Threat & Employee Fraud Detection
- Behavioral analytics monitoring employee access patterns, system activity, and transaction authorization behavior.
- Anomaly detection identifying unusual data access, financial system manipulation, and policy violations.
- User and Entity Behavior Analytics (UEBA) establishing behavioral baselines for fraud deviation detection.
- Integration with HR systems and access management platforms for contextual fraud risk assessment.
- Confidential fraud reporting mechanisms supporting whistleblower-based fraud intelligence collection.
7. AML & Financial Crime Compliance Monitoring
- Automated suspicious activity monitoring aligned with AML regulatory reporting obligations.
- Transaction pattern analysis detecting money laundering indicators including structuring, layering, and integration.
- Customer risk profiling and ongoing monitoring for elevated financial crime risk indicators.
- Regulatory reporting workflow management supporting SAR filing and AML compliance documentation.
- Integration with sanctions screening and PEP (politically exposed persons) watchlist databases.
8. Managed Fraud Operations & Investigation Support
- End-to-end management of fraud monitoring platforms, analytics tools, and investigation case management.
- Continuous optimization of fraud detection models to improve accuracy and reduce false positive rates.
- Expert fraud analyst support providing specialized investigation and case resolution capabilities.
- Integration with legal, compliance, and financial operations teams for coordinated fraud response.
- Scalability management supporting growing transaction volumes and evolving fraud risk environments.
FRAUD RISK MITIGATION - CODEC NETWORK'S INDUSTRY OFFERINGS
Codec Networks' delivers industry-aligned bundled fraud mitigation packages combining analytics,
compliance monitoring, and intelligence for scalable, cost-effective financial crime prevention
Foundational Fraud Monitoring
Target Clients:
Small businesses and startups requiring cost-effective foundational fraud monitoring to gain transaction visibility and protect financial operations with minimal operational complexity.
Services Included
- Transaction Monitoring & Alert Management
- Basic Identity Verification
- Fraud Incident Reporting
Purpose:
Establish baseline fraud monitoring capabilities enabling organizations to detect fundamental transaction fraud, identity exploitation, and initial financial crime exposure.
Value Delivered:
Improved financial visibility, early fraud detection, and reduced exploitation risk through affordable, standardized, and easy-to-implement fraud mitigation services.
Enhanced Fraud Detection & Response
Target Clients:
Mid-sized enterprises requiring enhanced fraud detection, faster incident response, and compliance alignment across growing digital financial and operational environments.
Services Included
- Advanced AI Fraud Analytics & Use Case Development
- Behavioral Analytics & Identity Intelligence
- Compliance Monitoring & Regulatory Reporting
Purpose:
Strengthen fraud detection accuracy, improve incident response capabilities, and integrate intelligence for proactive and resilient fraud risk management operations.
Value Delivered:
Reduced fraud losses, improved detection precision, and enhanced operational efficiency through integrated, scalable, and intelligence-driven fraud mitigation services.
Comprehensive Fraud Operations & Predictive Prevention
Target Clients:
Large enterprises, regulated financial institutions, and global organizations requiring comprehensive, scalable, and compliance-driven advanced fraud mitigation and financial crime prevention operations.
Services Included
- AI-Driven Predictive Fraud Analytics
- Full Managed Fraud Operations
- Advanced Compliance Automation & Reporting
Purpose:
Deliver proactive, intelligence-led fraud prevention with predictive analytics ensuring resilience against evolving fraud typologies and strict regulatory compliance obligations.
Value Delivered:
High-maturity fraud mitigation posture, minimized fraud losses, and continuous compliance through advanced analytics, automation, and fully managed fraud operations capabilities.
Foundational Fraud Monitoring
Target Clients:
Small businesses and startups requiring cost-effective foundational fraud monitoring to gain transaction visibility and protect financial operations with minimal operational complexity.
Services Included
- Transaction Monitoring & Alert Management
- Basic Identity Verification
- Fraud Incident Reporting
Purpose:
Establish baseline fraud monitoring capabilities enabling organizations to detect fundamental transaction fraud, identity exploitation, and initial financial crime exposure.
Value Delivered:
Improved financial visibility, early fraud detection, and reduced exploitation risk through affordable, standardized, and easy-to-implement fraud mitigation services.
Enhanced Fraud Detection & Response
Target Clients:
Mid-sized enterprises requiring enhanced fraud detection, faster incident response, and compliance alignment across growing digital financial and operational environments.
Services Included
- Advanced AI Fraud Analytics & Use Case Development
- Behavioral Analytics & Identity Intelligence
- Compliance Monitoring & Regulatory Reporting
Purpose:
Strengthen fraud detection accuracy, improve incident response capabilities, and integrate intelligence for proactive and resilient fraud risk management operations.
Value Delivered:
Reduced fraud losses, improved detection precision, and enhanced operational efficiency through integrated, scalable, and intelligence-driven fraud mitigation services.
Comprehensive Fraud Operations & Predictive Prevention
Target Clients:
Large enterprises, regulated financial institutions, and global organizations requiring comprehensive, scalable, and compliance-driven advanced fraud mitigation and financial crime prevention operations.
Services Included
- AI-Driven Predictive Fraud Analytics
- Full Managed Fraud Operations
- Advanced Compliance Automation & Reporting
Purpose:
Deliver proactive, intelligence-led fraud prevention with predictive analytics ensuring resilience against evolving fraud typologies and strict regulatory compliance obligations.
Value Delivered:
High-maturity fraud mitigation posture, minimized fraud losses, and continuous compliance through advanced analytics, automation, and fully managed fraud operations capabilities.
CODEC NETWORKS VALUE PROPOSITION
Codec Networks' delivers proactive, intelligence-driven fraud risk mitigation enabling real-time detection,
apid intervention, and resilient financial crime prevention for evolving digital environments
Codec Networks: Trusted Partner for Fraud Risk Mitigation Services
When delivering Fraud Risk Mitigation Services, Codec Networks brings differentiated industry value through mature delivery practices, deep technical competency, and hands-on financial crime intelligence expertise—ensuring measurable fraud loss reduction and operational financial resilience.
1. Strategic Delivery Approach & Operational Excellence
- Adopts a structured lifecycle-driven delivery model aligned with global frameworks including ITIL and NIST Cybersecurity Framework.
- Ensures standardized onboarding, model implementation, monitoring, and continuous improvement processes.
- Enables 24/7 Fraud Operations with defined SLAs, escalation matrices, and governance mechanisms.
- Incorporates automation and AI-driven orchestration to streamline fraud detection and response workflows.
- Focuses on measurable outcomes through KPIs including MTTD, MTTR, detection rates, and loss prevention.
2. Advanced Technical Competency & Fraud Analytics Expertise
- Deep expertise in AI fraud detection platforms, behavioral analytics, network analysis, and real-time scoring.
- Strong capabilities in integrating diverse data sources including transaction systems, identity platforms, and intelligence feeds.
- Proficiency in implementing advanced fraud models, UEBA, and anomaly detection for diverse fraud typologies.
- Experience in managing complex multi-channel fraud architectures across payment, insurance, and procurement ecosystems.
- Continuous model tuning and optimization to maintain high detection accuracy against evolving fraud techniques.
3. Skilled Financial Crime & Fraud Investigation Professionals
- Team of certified professionals with expertise in financial crime investigation, AI fraud analytics, and compliance.
- Strong knowledge of fraud typologies, attack patterns, and organized fraud network structures across industries.
- Capability to perform fraud case investigation, forensic analysis, and evidence documentation effectively.
- Continuous training programs ensuring expertise remains current with emerging fraud techniques and regulatory changes.
- Ability to provide strategic fraud advisory alongside operational fraud investigation support.
4. Proactive Fraud Intelligence & Risk Management
- Integration of global fraud intelligence feeds identifying emerging typologies and indicators of fraud compromise.
- Proactive monitoring detecting coordinated fraud campaigns, synthetic identity schemes, and insider fraud activity.
- Risk-based prioritization focusing mitigation resources on highest-value fraud threats affecting business operations.
- Continuous vulnerability and fraud risk assessment aligned with evolving financial crime landscapes.
- Enhanced situational awareness through contextual enrichment of fraud intelligence signals.
5. Compliance Alignment & Governance
- Strong alignment with international regulatory standards including AML regulations, PCI-DSS, and GDPR.
- Automated compliance monitoring, audit trails, and regulatory reporting to meet financial crime obligations.
- Policy-driven fraud monitoring ensuring adherence to internal governance and risk management frameworks.
- Facilitates regulatory audit readiness with structured evidence management and fraud documentation.
- Supports industry-specific compliance needs across BFSI, insurance, healthcare, and technology sectors.
6. Scalability, Flexibility & Global Delivery Capability
- Scalable service models supporting small, mid-sized, and large enterprises across diverse geographies.
- Flexible deployment supporting cloud-based, on-premise, and hybrid fraud mitigation architectures.
- Ability to expand fraud detection coverage and use cases as business environments and risks evolve.
- Global delivery capability ensuring consistent fraud mitigation quality across multiple regions and time zones.
- Modular service offerings enabling customized fraud solutions aligned with specific client risk profiles.
7. Business Value & Outcome-Driven Fraud Prevention
- Reduces direct financial and reputational risks from fraud through early detection and rapid intervention.
- Enhances organizational resilience ensuring financial continuity through uninterrupted fraud monitoring.
- Improves decision-making with actionable fraud risk insights, dashboards, and executive reporting.
- Optimizes fraud mitigation investments by delivering measurable ROI and reducing internal resource dependency.
- Builds customer confidence and organizational credibility through strong, proactive fraud risk management.
Founded in 2008 with 17+ Years of Industry Experience in Information and Cyber Security domain
Codec Networks Full-Spectrum Cybersecurity Expertise across all Industry Domains:
- Security Vulnerability Assessment & Penetration Testing (VAPT): Covering Web, Mobile, API, IoT, Blockchain, Cloud-Native, and smart infrastructure environments, with a focus on OWASP, MITRE ATT&CK, and real-world exploit simulation.
- Offensive Security & Deep Level Security Assessments: Advanced Red Team, Blue Team and Purple Team Exercises, Threat Simulations, Social Engineering Campaigns, and Secure Code Review.
- IT Security Audit & Compliance Services: Implementation and audit support for ISO/IEC 27001, ISO 27701, NIST CSF, RBI-CSF, SEBI, IRDAI, PCI DSS, HIPAA, SOC 2, GDPR, and India’s DPDPA 2023.
- Data Privacy & Strategic Risk Advisory: ISO 27701, GDPR, DPDPA, Cross-border compliance, DPIA, DPO-as-a-service, supply chain risk management, and digital transformation risk consulting.
- Emerging Technology Security (Web3.0 | AI | Blockchain): Specialized testing for smart contracts, DeFi platforms, Metaverse applications, AI/ML models, quantum readiness, and blockchain nodes.
- Managed SOC & Threat Monitoring Services: End-to-end SOC operations, SIEM/EDR/XDR/SOAR integration, threat intelligence, cloud security monitoring, and 24/7 incident response.
- Cyber Forensics & Threat Analysis: Investigation services including Device forensics, Malware Analysis, Cloud and Mobile forensics, insider threat detection, and Forensic support.
- Board-Level Cybersecurity Advisory Services to build governance, quantify risks, and align with enterprise-wide digital priorities : Codec Networks enables this transformation by offering Integrated Cyber Risk Management, GRC Program Advisory, Reputation Management, Crisis Communication Readiness, and CISO Support, tailored for CXOs and board members seeking to integrate cybersecurity into strategic decision-making.
- Cyber Security Education & Global Certifications - Through the Codec Centre for Professional Excellence, we deliver Post Graduate Certification in Advanced Cybersecurity (PGCAC), Graduate Certification in Advanced Cybersecurity (GCAC), Accredited Trainings & Certifications from EC Council, PECB, TUV, Quality Austria, ISACA and ISC2 - building the next generation of cybersecurity leaders.
- CERT-IN empaneled Information Security Auditing Organization
- NICSI empaneled for providing Application Audit and Compliance Services under Start-Up Category


- An ISO/IEC 27001:2022 certified company, has established Information Security Management System (ISMS), demonstrating a structured approach to manage and protect sensitive information from cyber threats.
- An ISO 9001 certified company, has established and maintains a certified Quality Management System (QMS) that meets international standards for quality and consistency
At Codec Networks, our foundation is built on deep technical mastery, certified expertise, and an unrelenting pursuit of cyber excellence. With a team of globally accredited professionals, advanced methodologies, and next-generation tools, we deliver measurable security outcomes across assessment, compliance, monitoring, and forensic domains. Our competency-driven approach ensures every engagement is governed by precision, accountability, and alignment with international standards — empowering enterprises to stay secure, compliant, and resilient.
Governance, Risk & Compliance (GRC) Competency
Codec Networks’ dedicated Governance, Risk & Compliance (GRC) group specializes in security assessments, risk management, regulatory compliance, and audit readiness. The team partners with organizations to strengthen governance frameworks and ensure end-to-end compliance in a complex regulatory landscape.
Key Attributes:
- Team of certified auditors and consultants with credentials including ISO 27001 LA/LI, ISO 31000 Risk Specialist, ISO 27701 PIMS, GDPR, SOC 2, HIPAA, CCPA, DPO, CISA, CISM, CRISC, CISSP and other advanced industry certifications.
- Expertise in enterprise risk quantification, privacy impact assessment (PIA/DPIA), audit automation, and supply chain risk mapping.
- Proven track record in implementing ISO-based ISMS/PIMS frameworks, RBI/SEBI/IRDAI audits, and cross-border data compliance projects.
Vulnerability Assessment & Penetration Testing (VAPT) Expertise
Our VAPT teams bring extensive technical depth across Web, Mobile, API, Cloud, Network, Database, Infrastructure, IoT, and People & Process domains. Every engagement is mapped to OWASP, NIST, MITRE ATT&CK, ISO 27001, PCI DSS, HIPAA, RBI, and GDPR frameworks — ensuring real-world relevance and compliance alignment.
Core Strengths:
- Certified professionals with CEH, C-PENT, LPT, OSCP, OSWE, OSEE, and CREST credentials, averaging 7–10 years of offensive security experience.
- Proven expertise in Red/Blue/Purple Teaming, DevSecOps, secure SDLC, and threat emulation.
- Continuous skill enhancement through CTFs, hackathons, and product certifications (on case to case basis) such as CCNA, CCNP etc.
Managed SOC & Threat Intelligence Operations
Codec Networks operates a 24/7 Managed Security Operations Center (SOC) delivering continuous visibility, detection, and response across hybrid environments. Our SOC integrates SIEM, SOAR, EDR/XDR, and Cloud-Native Analytics to ensure rapid threat detection, incident containment, and business continuity.
Key Capabilities:
- Certified SOC analysts with credentials such as CHFI, CEH, CompTIA CySA+, GCIA, GCFA, and Splunk Certified Architect.
- Integration with platforms like Splunk, QRadar, SentinelOne, CrowdStrike, Elastic, Microsoft Sentinel, and Cortex XSOAR.
- Advanced use cases include cloud posture management, insider threat analytics, MITRE ATT&CK–aligned detections, and threat hunting automation.
- Comprehensive SOC Maturity Assessments and Threat Intelligence Fusion through integration with global feeds and dark web monitoring.
Cyber Forensics & Threat Analysis Expertise
Our Cyber Forensic Division delivers end-to-end investigation, evidence preservation, and digital analysis services — designed to support law enforcement, corporate forensics, and internal response teams. We combine forensic science with cyber intelligence to identify root causes, trace adversaries, and restore operational integrity.
Core Expertise Areas:
- Device, Network, Cloud, and Mobile Forensics – leveraging latest forensic tools (wherever applicable) such as Autopsy, Cyber Triage, Kape, EnCase, FTK, Magnet AXIOM, and Cellebrite.
- Malware Reverse Engineering and Memory Forensics for incident containment and threat attribution.
- Blockchain & Crypto Forensics – tracing DeFi fraud, NFT manipulation, and crypto laundering activities using Chainalysis, TRM Labs, and Elliptic (wherever applicable).
- Incident Response Support – forensic readiness, eDiscovery, evidence preservation, aligned with ISO/IEC 27037 & 27043.
- Certified experts including CHFI, eCIR, eCDFP, GCFE, GCFA, EnCE, CFCE and ECIH, ensuring investigations meet both technical and legal standards.
Advanced Tools, Frameworks & Continuous Innovation
Codec Networks leverages industry-leading tools and platforms such as Burp Suite Pro, Nessus, Prisma Cloud, Splunk, QRadar, CrowdStrike, SentinelOne, Autopsy, Chainalysis, MythX, and Prowler (wherever applicable) ensuring accuracy, scalability, and efficiency.
Our methodologies align with globally recognized frameworks including:
- MITRE ATT&CK & D3FEND
- OWASP Top 10 / MASVS / ASVS
- NIST Cybersecurity Framework & SP 800-115
- ISO/IEC 27001, 27701, 31000, 22301
Through ongoing research, Codec Networks continually evolves to address modern threats — from Generative AI prompt attacks and smart contract exploits to IoT zero-days, metaverse impersonation, and quantum-era vulnerabilities.
Compliance-Driven Deliverables
All technical engagements and reports are mapped to major global and Indian compliance frameworks — including ISO 27001, PCI DSS, HIPAA, GDPR, RBI-CSF, SEBI, IRDAI, and DPDPA 2023. Our structured technical and executive reports support board-level visibility, audit evidence, and certification readiness, ensuring that every engagement drives both technical assurance and regulatory confidence.
Codec Networks – Certified Competence. Proven Expertise. Real-World Cyber Resilience. Empowering enterprises through advanced security engineering, continuous monitoring, and forensic intelligence.
At Codec Networks, we believe that cybersecurity excellence is not achieved through tools alone — it is built through methodical delivery, risk-based insight, and measurable outcomes. Our Agile and Modular 8-Stage Delivery Methodology ensures that every engagement — from rapid risk assessments to full-scale ISMS implementations — is structured, standards-aligned, and business-focused.
Agile & Modular Methodology
Our delivery framework integrates global best practices with localized regulatory insight, ensuring each engagement is executed with clarity, accountability, and precision. Clients benefit from seamless onboarding, milestone-driven execution, and transparent reporting throughout the lifecycle.
- Discovery & Scoping: Collaborative workshops to understand business context, IT landscape, compliance obligations, and risk appetite, forming the foundation of a well-defined project scope.
- Risk Profiling & Gap Assessment: Comprehensive evaluation of people, process, and technology controls aligned with ISO 27001, NIST CSF, GDPR, HIPAA, DPDPA 2023, RBI, and PCI DSS.
- Regulatory Mapping & Framework Alignment: Mapping organizational obligations against applicable standards and laws — from ISO & NIST to RBI, SEBI, IRDAI, UIDAI, and DPDPA — including new-age frameworks like ISO 42001 (AI) and FATF for emerging technologies.
- Security Architecture & Control Design: Designing or refining network, cloud, and data security architectures with controls tailored for cloud, AI, OT/ICS, and Web3.0 environments.
- Documentation & Policy Development: Creation and refinement of Policies, SOPs, Risk Registers, DPIAs, Incident Response Plans, and Governance Documents, ensuring audit readiness and legal compliance.
- Implementation & Risk Treatment: Execution of remediation roadmaps, vendor risk management, privacy engineering, and workforce training to mitigate gaps and operationalize security controls.
- Validation, Testing & Audit Readiness: Conducting mock audits, VAPT, forensic readiness, and compliance testing to validate effectiveness and prepare for certifications.
- Governance Reporting & Continual Improvement: Delivering executive dashboards, compliance scorecards, and board-level insights with ongoing advisory through vCISO and DPO-as-a-Service models.
Risk-Based & Business-Oriented Audit Approach
Our methodology goes beyond testing systems — it focuses on how vulnerabilities translate into business, reputational, and compliance risks.
- Deliver Deep Insight: Actionable intelligence into vulnerabilities, attack paths, business impact, and remediation priorities.
- Extend Beyond Tools: Manual and contextual assessments combining automation with human expertise across government, financial, and commercial sectors.
- Actionable Reporting: Executive-friendly reports that translate complex findings into strategic, risk-aware recommendations.
- Efficient Execution: Critical assets prioritized for testing to deliver maximum value within tight engagement windows.
Outcome-Driven Engagements for Security Maturity
Each stage is modular yet interconnected, adaptable to enterprises of any scale or industry. Whether it’s a cloud-native fintech pursuing SOC 2, a healthcare provider ensuring HIPAA alignment, or a bank meeting RBI-CSF requirements, Codec Networks ensures consistency, compliance, and measurable improvement.
Beyond certification checklists, our Post-Audit Support and Continuous Risk Monitoring provide remediation guidance, breach response playbooks, staff training, and ongoing compliance tracking — building sustainable security posture and resilient business continuity.
Codec Networks – Turning Compliance into a Competitive Advantage. Structured. Measurable. Secure. Always Aligned with Your Business Goals.
At Codec Networks, our clients are not just audit subjects — they are long-term partners in a shared cybersecurity journey. Every engagement is designed around the client’s business priorities, security maturity, and risk appetite, ensuring solutions that are relevant, practical, and results-driven.
With a legacy of 650+ successful engagements across industries such as Banking, Fintech, Healthcare, Telecom, Energy, Aviation, Manufacturing, E-commerce, and Government, Codec Networks has attempted to become a trusted advisor for organizations seeking to transform compliance into resilience.
Our engagement philosophy extends beyond conventional audits. We integrate strategic advisory, technical assurance, remediation support, and continuous compliance monitoring, creating a full lifecycle relationship rather than a one-time service. Clients benefit from:
- Personalized advisory frameworks tailored to their business model and operational scale.
- Collaborative engagement models featuring joint workshops, stakeholder training, and compliance awareness sessions.
- Board-level guidance and reporting that translates complex technical findings into actionable business intelligence.
- Transparent communication channels with dedicated project managers, secure digital workspaces, and real-time status dashboards.
By combining the objectivity of an auditor with the empathy of an advisor, Codec Networks builds trust, accountability, and measurable security growth. Our commitment is simple — to deliver cybersecurity as a continuous partnership, not a periodic project.
Codec Networks – Where Advisory Meets Assurance. Empowering Clients Through Partnership, Transparency, and Trust.
At Codec Networks, integrity, professionalism, and ethical responsibility form the cornerstone of every engagement. As a trusted strategic partner in cybersecurity, we operate within the highest standards of ethical conduct, legal compliance, and regulatory governance, ensuring our services strengthen both our clients’ defenses and their reputations.
We adhere to a strict ethical code of conduct, driven by transparency, independence, and accountability. Every consultant, auditor, and engineer within Codec Networks upholds the core security triad of Confidentiality, Integrity, and Availability (CIA) — ensuring data protection, operational reliability, and business continuity at all times.
Our professional ethos blends technical excellence with moral responsibility, following structured processes, defined service standards, and adherence to international and national regulatory frameworks.
Our Ethical & Professional Commitments
- Zero-Compromise Consulting: We maintain independence, neutrality, and confidentiality across all audits and advisory engagements.
- Legal & Regulatory Conformance: We assist clients to conform strictly within the boundaries of applicable cyber laws, privacy regulations, and data protection statutes.
- Client-First Philosophy: Every recommendation is designed to safeguard stakeholder interests, minimize legal exposure, and build sustainable resilience.
- Outcome-Driven Security Maturity: Our modular yet integrated delivery approach supports organizations of all sizes in achieving measurable improvements in security posture.
- Global Delivery, Local Integrity: Our Global Network Delivery Model integrates international best practices with local regulatory expertise — ensuring value-driven, compliant outcomes.
Industry-Specific Security Advisory
Recognizing that every sector faces distinct threats and compliance challenges, Codec Networks provides customized, industry-aligned security advisory across BFSI, Fintech, Telecom, Healthcare, Energy, Aviation, E-commerce, Government, and Critical Infrastructure domains.
Our sector-specific consulting translates regulatory complexity into practical, business-aware strategies, ensuring risk mitigation plans are compliant, auditable, and operationally feasible.
Our Commitment
With a zero-tolerance approach to ethical compromise, Codec Networks stands for trust, transparency, and truth in cybersecurity. We are more than consultants — we are custodians of digital integrity, committed to helping organizations navigate risk, maintain compliance, and enable secure business growth.
Codec Networks – Where Integrity Meets Innovation. Trusted. Ethical. Future-Ready.
At Codec Networks, we combine the strength of a global delivery ecosystem with the precision of local regulatory insight to deliver cybersecurity solutions that are both internationally benchmarked and regionally compliant.
Our Global Delivery Capability enables clients across continents to access specialized cybersecurity expertise, advanced technologies, and globally aligned methodologies. Through a distributed network of certified professionals, partner alliances, and intelligence centers, Codec Networks ensures consistent service quality and rapid response across time zones and geographies.
What truly differentiates us is our Local Expertise — a deep understanding of national regulations, industry frameworks, and operational nuances that shape cybersecurity implementation in each region.
Our hybrid delivery model blends remote and on-site collaboration, combining the agility of digital operations with the contextual understanding of local consultants. This ensures culturally aligned communication, faster problem resolution, and seamless coordination with client teams.
With a presence across India, Codec Networks empowers global enterprises to manage cybersecurity uniformly while adapting to local risks, regulations, and realities.
Codec Networks – Global Vision. Local Precision. Consistent Cyber Resilience.
“With Codec Networks, you’re not just buying a service — you’re investing in a cybersecurity ally who understands your business, defends your reputation, and strengthens your future.”
At Codec Networks, we believe cybersecurity is not a project — it’s a partnership. Our approach is built on trust, transparency, and transformation, helping clients evolve from compliance readiness to cyber resilience.
Your Strategic Security Partner
Codec Networks acts as a strategic security partner, providing continuous roadmap development, architecture reviews, and improvement programs that evolve with your business and the threat landscape.
“We don’t just secure businesses — we empower them to lead with confidence in a digital-first world.”
Our strength lies in the fusion of technical depth, regulatory insight, industry specialization, and future readiness — providing unmatched cybersecurity value to enterprises across India and beyond.
Codec Networks – Certified Competence. Proven Expertise. Real-World Cyber Resilience. Empowering enterprises through advanced security engineering, continuous monitoring, and forensic intelligence.
Every engagement reflects our belief that advisory must meet assurance — a promise we deliver through partnership, integrity, and measurable impact.
Codec Networks – Where Advisory Meets Assurance. Empowering Clients Through Partnership, Transparency, and Trust.
And above all —
“Decoding Threats. Coding Solutions.” That’s the Codec Networks Advantage.
Codec Networks: Trusted Partner for Fraud Risk Mitigation Services
When delivering Fraud Risk Mitigation Services, Codec Networks brings differentiated industry value through mature delivery practices, deep technical competency, and hands-on financial crime intelligence expertise—ensuring measurable fraud loss reduction and operational financial resilience.
1. Strategic Delivery Approach & Operational Excellence
- Adopts a structured lifecycle-driven delivery model aligned with global frameworks including ITIL and NIST Cybersecurity Framework.
- Ensures standardized onboarding, model implementation, monitoring, and continuous improvement processes.
- Enables 24/7 Fraud Operations with defined SLAs, escalation matrices, and governance mechanisms.
- Incorporates automation and AI-driven orchestration to streamline fraud detection and response workflows.
- Focuses on measurable outcomes through KPIs including MTTD, MTTR, detection rates, and loss prevention.
2. Advanced Technical Competency & Fraud Analytics Expertise
- Deep expertise in AI fraud detection platforms, behavioral analytics, network analysis, and real-time scoring.
- Strong capabilities in integrating diverse data sources including transaction systems, identity platforms, and intelligence feeds.
- Proficiency in implementing advanced fraud models, UEBA, and anomaly detection for diverse fraud typologies.
- Experience in managing complex multi-channel fraud architectures across payment, insurance, and procurement ecosystems.
- Continuous model tuning and optimization to maintain high detection accuracy against evolving fraud techniques.
3. Skilled Financial Crime & Fraud Investigation Professionals
- Team of certified professionals with expertise in financial crime investigation, AI fraud analytics, and compliance.
- Strong knowledge of fraud typologies, attack patterns, and organized fraud network structures across industries.
- Capability to perform fraud case investigation, forensic analysis, and evidence documentation effectively.
- Continuous training programs ensuring expertise remains current with emerging fraud techniques and regulatory changes.
- Ability to provide strategic fraud advisory alongside operational fraud investigation support.
4. Proactive Fraud Intelligence & Risk Management
- Integration of global fraud intelligence feeds identifying emerging typologies and indicators of fraud compromise.
- Proactive monitoring detecting coordinated fraud campaigns, synthetic identity schemes, and insider fraud activity.
- Risk-based prioritization focusing mitigation resources on highest-value fraud threats affecting business operations.
- Continuous vulnerability and fraud risk assessment aligned with evolving financial crime landscapes.
- Enhanced situational awareness through contextual enrichment of fraud intelligence signals.
5. Compliance Alignment & Governance
- Strong alignment with international regulatory standards including AML regulations, PCI-DSS, and GDPR.
- Automated compliance monitoring, audit trails, and regulatory reporting to meet financial crime obligations.
- Policy-driven fraud monitoring ensuring adherence to internal governance and risk management frameworks.
- Facilitates regulatory audit readiness with structured evidence management and fraud documentation.
- Supports industry-specific compliance needs across BFSI, insurance, healthcare, and technology sectors.
6. Scalability, Flexibility & Global Delivery Capability
- Scalable service models supporting small, mid-sized, and large enterprises across diverse geographies.
- Flexible deployment supporting cloud-based, on-premise, and hybrid fraud mitigation architectures.
- Ability to expand fraud detection coverage and use cases as business environments and risks evolve.
- Global delivery capability ensuring consistent fraud mitigation quality across multiple regions and time zones.
- Modular service offerings enabling customized fraud solutions aligned with specific client risk profiles.
7. Business Value & Outcome-Driven Fraud Prevention
- Reduces direct financial and reputational risks from fraud through early detection and rapid intervention.
- Enhances organizational resilience ensuring financial continuity through uninterrupted fraud monitoring.
- Improves decision-making with actionable fraud risk insights, dashboards, and executive reporting.
- Optimizes fraud mitigation investments by delivering measurable ROI and reducing internal resource dependency.
- Builds customer confidence and organizational credibility through strong, proactive fraud risk management.
Founded in 2008 with 17+ Years of Industry Experience in Information and Cyber Security domain
Codec Networks Full-Spectrum Cybersecurity Expertise across all Industry Domains:
- Security Vulnerability Assessment & Penetration Testing (VAPT): Covering Web, Mobile, API, IoT, Blockchain, Cloud-Native, and smart infrastructure environments, with a focus on OWASP, MITRE ATT&CK, and real-world exploit simulation.
- Offensive Security & Deep Level Security Assessments: Advanced Red Team, Blue Team and Purple Team Exercises, Threat Simulations, Social Engineering Campaigns, and Secure Code Review.
- IT Security Audit & Compliance Services: Implementation and audit support for ISO/IEC 27001, ISO 27701, NIST CSF, RBI-CSF, SEBI, IRDAI, PCI DSS, HIPAA, SOC 2, GDPR, and India’s DPDPA 2023.
- Data Privacy & Strategic Risk Advisory: ISO 27701, GDPR, DPDPA, Cross-border compliance, DPIA, DPO-as-a-service, supply chain risk management, and digital transformation risk consulting.
- Emerging Technology Security (Web3.0 | AI | Blockchain): Specialized testing for smart contracts, DeFi platforms, Metaverse applications, AI/ML models, quantum readiness, and blockchain nodes.
- Managed SOC & Threat Monitoring Services: End-to-end SOC operations, SIEM/EDR/XDR/SOAR integration, threat intelligence, cloud security monitoring, and 24/7 incident response.
- Cyber Forensics & Threat Analysis: Investigation services including Device forensics, Malware Analysis, Cloud and Mobile forensics, insider threat detection, and Forensic support.
- Board-Level Cybersecurity Advisory Services to build governance, quantify risks, and align with enterprise-wide digital priorities : Codec Networks enables this transformation by offering Integrated Cyber Risk Management, GRC Program Advisory, Reputation Management, Crisis Communication Readiness, and CISO Support, tailored for CXOs and board members seeking to integrate cybersecurity into strategic decision-making.
- Cyber Security Education & Global Certifications - Through the Codec Centre for Professional Excellence, we deliver Post Graduate Certification in Advanced Cybersecurity (PGCAC), Graduate Certification in Advanced Cybersecurity (GCAC), Accredited Trainings & Certifications from EC Council, PECB, TUV, Quality Austria, ISACA and ISC2 - building the next generation of cybersecurity leaders.
- CERT-IN empaneled Information Security Auditing Organization
- NICSI empaneled for providing Application Audit and Compliance Services under Start-Up Category
- An ISO/IEC 27001:2022 certified company, has established Information Security Management System (ISMS), demonstrating a structured approach to manage and protect sensitive information from cyber threats.
- An ISO 9001 certified company, has established and maintains a certified Quality Management System (QMS) that meets international standards for quality and consistency
At Codec Networks, our foundation is built on deep technical mastery, certified expertise, and an unrelenting pursuit of cyber excellence. With a team of globally accredited professionals, advanced methodologies, and next-generation tools, we deliver measurable security outcomes across assessment, compliance, monitoring, and forensic domains. Our competency-driven approach ensures every engagement is governed by precision, accountability, and alignment with international standards — empowering enterprises to stay secure, compliant, and resilient.
Governance, Risk & Compliance (GRC) Competency
Codec Networks’ dedicated Governance, Risk & Compliance (GRC) group specializes in security assessments, risk management, regulatory compliance, and audit readiness. The team partners with organizations to strengthen governance frameworks and ensure end-to-end compliance in a complex regulatory landscape.
Key Attributes:
- Team of certified auditors and consultants with credentials including ISO 27001 LA/LI, ISO 31000 Risk Specialist, ISO 27701 PIMS, GDPR, SOC 2, HIPAA, CCPA, DPO, CISA, CISM, CRISC, CISSP and other advanced industry certifications.
- Expertise in enterprise risk quantification, privacy impact assessment (PIA/DPIA), audit automation, and supply chain risk mapping.
- Proven track record in implementing ISO-based ISMS/PIMS frameworks, RBI/SEBI/IRDAI audits, and cross-border data compliance projects.
Vulnerability Assessment & Penetration Testing (VAPT) Expertise
Our VAPT teams bring extensive technical depth across Web, Mobile, API, Cloud, Network, Database, Infrastructure, IoT, and People & Process domains. Every engagement is mapped to OWASP, NIST, MITRE ATT&CK, ISO 27001, PCI DSS, HIPAA, RBI, and GDPR frameworks — ensuring real-world relevance and compliance alignment.
Core Strengths:
- Certified professionals with CEH, C-PENT, LPT, OSCP, OSWE, OSEE, and CREST credentials, averaging 7–10 years of offensive security experience.
- Proven expertise in Red/Blue/Purple Teaming, DevSecOps, secure SDLC, and threat emulation.
- Continuous skill enhancement through CTFs, hackathons, and product certifications (on case to case basis) such as CCNA, CCNP etc.
Managed SOC & Threat Intelligence Operations
Codec Networks operates a 24/7 Managed Security Operations Center (SOC) delivering continuous visibility, detection, and response across hybrid environments. Our SOC integrates SIEM, SOAR, EDR/XDR, and Cloud-Native Analytics to ensure rapid threat detection, incident containment, and business continuity.
Key Capabilities:
- Certified SOC analysts with credentials such as CHFI, CEH, CompTIA CySA+, GCIA, GCFA, and Splunk Certified Architect.
- Integration with platforms like Splunk, QRadar, SentinelOne, CrowdStrike, Elastic, Microsoft Sentinel, and Cortex XSOAR.
- Advanced use cases include cloud posture management, insider threat analytics, MITRE ATT&CK–aligned detections, and threat hunting automation.
- Comprehensive SOC Maturity Assessments and Threat Intelligence Fusion through integration with global feeds and dark web monitoring.
Cyber Forensics & Threat Analysis Expertise
Our Cyber Forensic Division delivers end-to-end investigation, evidence preservation, and digital analysis services — designed to support law enforcement, corporate forensics, and internal response teams. We combine forensic science with cyber intelligence to identify root causes, trace adversaries, and restore operational integrity.
Core Expertise Areas:
- Device, Network, Cloud, and Mobile Forensics – leveraging latest forensic tools (wherever applicable) such as Autopsy, Cyber Triage, Kape, EnCase, FTK, Magnet AXIOM, and Cellebrite.
- Malware Reverse Engineering and Memory Forensics for incident containment and threat attribution.
- Blockchain & Crypto Forensics – tracing DeFi fraud, NFT manipulation, and crypto laundering activities using Chainalysis, TRM Labs, and Elliptic (wherever applicable).
- Incident Response Support – forensic readiness, eDiscovery, evidence preservation, aligned with ISO/IEC 27037 & 27043.
- Certified experts including CHFI, eCIR, eCDFP, GCFE, GCFA, EnCE, CFCE and ECIH, ensuring investigations meet both technical and legal standards.
Advanced Tools, Frameworks & Continuous Innovation
Codec Networks leverages industry-leading tools and platforms such as Burp Suite Pro, Nessus, Prisma Cloud, Splunk, QRadar, CrowdStrike, SentinelOne, Autopsy, Chainalysis, MythX, and Prowler (wherever applicable) ensuring accuracy, scalability, and efficiency.
Our methodologies align with globally recognized frameworks including:
- MITRE ATT&CK & D3FEND
- OWASP Top 10 / MASVS / ASVS
- NIST Cybersecurity Framework & SP 800-115
- ISO/IEC 27001, 27701, 31000, 22301
Through ongoing research, Codec Networks continually evolves to address modern threats — from Generative AI prompt attacks and smart contract exploits to IoT zero-days, metaverse impersonation, and quantum-era vulnerabilities.
Compliance-Driven Deliverables
All technical engagements and reports are mapped to major global and Indian compliance frameworks — including ISO 27001, PCI DSS, HIPAA, GDPR, RBI-CSF, SEBI, IRDAI, and DPDPA 2023. Our structured technical and executive reports support board-level visibility, audit evidence, and certification readiness, ensuring that every engagement drives both technical assurance and regulatory confidence.
Codec Networks – Certified Competence. Proven Expertise. Real-World Cyber Resilience. Empowering enterprises through advanced security engineering, continuous monitoring, and forensic intelligence.
At Codec Networks, we believe that cybersecurity excellence is not achieved through tools alone — it is built through methodical delivery, risk-based insight, and measurable outcomes. Our Agile and Modular 8-Stage Delivery Methodology ensures that every engagement — from rapid risk assessments to full-scale ISMS implementations — is structured, standards-aligned, and business-focused.
Agile & Modular Methodology
Our delivery framework integrates global best practices with localized regulatory insight, ensuring each engagement is executed with clarity, accountability, and precision. Clients benefit from seamless onboarding, milestone-driven execution, and transparent reporting throughout the lifecycle.
- Discovery & Scoping: Collaborative workshops to understand business context, IT landscape, compliance obligations, and risk appetite, forming the foundation of a well-defined project scope.
- Risk Profiling & Gap Assessment: Comprehensive evaluation of people, process, and technology controls aligned with ISO 27001, NIST CSF, GDPR, HIPAA, DPDPA 2023, RBI, and PCI DSS.
- Regulatory Mapping & Framework Alignment: Mapping organizational obligations against applicable standards and laws — from ISO & NIST to RBI, SEBI, IRDAI, UIDAI, and DPDPA — including new-age frameworks like ISO 42001 (AI) and FATF for emerging technologies.
- Security Architecture & Control Design: Designing or refining network, cloud, and data security architectures with controls tailored for cloud, AI, OT/ICS, and Web3.0 environments.
- Documentation & Policy Development: Creation and refinement of Policies, SOPs, Risk Registers, DPIAs, Incident Response Plans, and Governance Documents, ensuring audit readiness and legal compliance.
- Implementation & Risk Treatment: Execution of remediation roadmaps, vendor risk management, privacy engineering, and workforce training to mitigate gaps and operationalize security controls.
- Validation, Testing & Audit Readiness: Conducting mock audits, VAPT, forensic readiness, and compliance testing to validate effectiveness and prepare for certifications.
- Governance Reporting & Continual Improvement: Delivering executive dashboards, compliance scorecards, and board-level insights with ongoing advisory through vCISO and DPO-as-a-Service models.
Risk-Based & Business-Oriented Audit Approach
Our methodology goes beyond testing systems — it focuses on how vulnerabilities translate into business, reputational, and compliance risks.
- Deliver Deep Insight: Actionable intelligence into vulnerabilities, attack paths, business impact, and remediation priorities.
- Extend Beyond Tools: Manual and contextual assessments combining automation with human expertise across government, financial, and commercial sectors.
- Actionable Reporting: Executive-friendly reports that translate complex findings into strategic, risk-aware recommendations.
- Efficient Execution: Critical assets prioritized for testing to deliver maximum value within tight engagement windows.
Outcome-Driven Engagements for Security Maturity
Each stage is modular yet interconnected, adaptable to enterprises of any scale or industry. Whether it’s a cloud-native fintech pursuing SOC 2, a healthcare provider ensuring HIPAA alignment, or a bank meeting RBI-CSF requirements, Codec Networks ensures consistency, compliance, and measurable improvement.
Beyond certification checklists, our Post-Audit Support and Continuous Risk Monitoring provide remediation guidance, breach response playbooks, staff training, and ongoing compliance tracking — building sustainable security posture and resilient business continuity.
Codec Networks – Turning Compliance into a Competitive Advantage. Structured. Measurable. Secure. Always Aligned with Your Business Goals.
At Codec Networks, our clients are not just audit subjects — they are long-term partners in a shared cybersecurity journey. Every engagement is designed around the client’s business priorities, security maturity, and risk appetite, ensuring solutions that are relevant, practical, and results-driven.
With a legacy of 650+ successful engagements across industries such as Banking, Fintech, Healthcare, Telecom, Energy, Aviation, Manufacturing, E-commerce, and Government, Codec Networks has attempted to become a trusted advisor for organizations seeking to transform compliance into resilience.
Our engagement philosophy extends beyond conventional audits. We integrate strategic advisory, technical assurance, remediation support, and continuous compliance monitoring, creating a full lifecycle relationship rather than a one-time service. Clients benefit from:
- Personalized advisory frameworks tailored to their business model and operational scale.
- Collaborative engagement models featuring joint workshops, stakeholder training, and compliance awareness sessions.
- Board-level guidance and reporting that translates complex technical findings into actionable business intelligence.
- Transparent communication channels with dedicated project managers, secure digital workspaces, and real-time status dashboards.
By combining the objectivity of an auditor with the empathy of an advisor, Codec Networks builds trust, accountability, and measurable security growth. Our commitment is simple — to deliver cybersecurity as a continuous partnership, not a periodic project.
Codec Networks – Where Advisory Meets Assurance. Empowering Clients Through Partnership, Transparency, and Trust.
At Codec Networks, integrity, professionalism, and ethical responsibility form the cornerstone of every engagement. As a trusted strategic partner in cybersecurity, we operate within the highest standards of ethical conduct, legal compliance, and regulatory governance, ensuring our services strengthen both our clients’ defenses and their reputations.
We adhere to a strict ethical code of conduct, driven by transparency, independence, and accountability. Every consultant, auditor, and engineer within Codec Networks upholds the core security triad of Confidentiality, Integrity, and Availability (CIA) — ensuring data protection, operational reliability, and business continuity at all times.
Our professional ethos blends technical excellence with moral responsibility, following structured processes, defined service standards, and adherence to international and national regulatory frameworks.
Our Ethical & Professional Commitments
- Zero-Compromise Consulting: We maintain independence, neutrality, and confidentiality across all audits and advisory engagements.
- Legal & Regulatory Conformance: We assist clients to conform strictly within the boundaries of applicable cyber laws, privacy regulations, and data protection statutes.
- Client-First Philosophy: Every recommendation is designed to safeguard stakeholder interests, minimize legal exposure, and build sustainable resilience.
- Outcome-Driven Security Maturity: Our modular yet integrated delivery approach supports organizations of all sizes in achieving measurable improvements in security posture.
- Global Delivery, Local Integrity: Our Global Network Delivery Model integrates international best practices with local regulatory expertise — ensuring value-driven, compliant outcomes.
Industry-Specific Security Advisory
Recognizing that every sector faces distinct threats and compliance challenges, Codec Networks provides customized, industry-aligned security advisory across BFSI, Fintech, Telecom, Healthcare, Energy, Aviation, E-commerce, Government, and Critical Infrastructure domains.
Our sector-specific consulting translates regulatory complexity into practical, business-aware strategies, ensuring risk mitigation plans are compliant, auditable, and operationally feasible.
Our Commitment
With a zero-tolerance approach to ethical compromise, Codec Networks stands for trust, transparency, and truth in cybersecurity. We are more than consultants — we are custodians of digital integrity, committed to helping organizations navigate risk, maintain compliance, and enable secure business growth.
Codec Networks – Where Integrity Meets Innovation. Trusted. Ethical. Future-Ready.
At Codec Networks, we combine the strength of a global delivery ecosystem with the precision of local regulatory insight to deliver cybersecurity solutions that are both internationally benchmarked and regionally compliant.
Our Global Delivery Capability enables clients across continents to access specialized cybersecurity expertise, advanced technologies, and globally aligned methodologies. Through a distributed network of certified professionals, partner alliances, and intelligence centers, Codec Networks ensures consistent service quality and rapid response across time zones and geographies.
What truly differentiates us is our Local Expertise — a deep understanding of national regulations, industry frameworks, and operational nuances that shape cybersecurity implementation in each region.
Our hybrid delivery model blends remote and on-site collaboration, combining the agility of digital operations with the contextual understanding of local consultants. This ensures culturally aligned communication, faster problem resolution, and seamless coordination with client teams.
With a presence across India, Codec Networks empowers global enterprises to manage cybersecurity uniformly while adapting to local risks, regulations, and realities.
Codec Networks – Global Vision. Local Precision. Consistent Cyber Resilience.
“With Codec Networks, you’re not just buying a service — you’re investing in a cybersecurity ally who understands your business, defends your reputation, and strengthens your future.”
At Codec Networks, we believe cybersecurity is not a project — it’s a partnership. Our approach is built on trust, transparency, and transformation, helping clients evolve from compliance readiness to cyber resilience.
Your Strategic Security Partner
Codec Networks acts as a strategic security partner, providing continuous roadmap development, architecture reviews, and improvement programs that evolve with your business and the threat landscape.
“We don’t just secure businesses — we empower them to lead with confidence in a digital-first world.”
Our strength lies in the fusion of technical depth, regulatory insight, industry specialization, and future readiness — providing unmatched cybersecurity value to enterprises across India and beyond.
Codec Networks – Certified Competence. Proven Expertise. Real-World Cyber Resilience. Empowering enterprises through advanced security engineering, continuous monitoring, and forensic intelligence.
Every engagement reflects our belief that advisory must meet assurance — a promise we deliver through partnership, integrity, and measurable impact.
Codec Networks – Where Advisory Meets Assurance. Empowering Clients Through Partnership, Transparency, and Trust.
And above all —
“Decoding Threats. Coding Solutions.” That’s the Codec Networks Advantage.
WHAT OUR CUSTOMERS SAY
Codec Networks' significantly improves fraud detection capabilities with proactive monitoring,
delivering faster intervention times and stronger overall financial crime prevention posture.
-
“Vijay Pratap is a passionate Software Developer specializing in building scalable web applications and APIs. He enjoys solving complex problems with clean”
Vijay Pratap
Developer -
“Deepak Baghel is a passionate Frontend Developer specializing in building responsive, accessible interfaces. He enjoys solving complex problems with clean”
Deepak Baghel
Frontend Developer -
“Saurav is a passionate DevOps engineer specializing in building resilient, automated delivery pipelines. He enjoys solving complex problems with clean”
Saurav
DevOps
“Vijay Pratap is a passionate Software Developer specializing in building scalable web applications and APIs. He enjoys solving complex problems with clean”
Vijay Pratap
Developer
“Deepak Baghel is a passionate Frontend Developer specializing in building responsive, accessible interfaces. He enjoys solving complex problems with clean”
Deepak Baghel
Frontend Developer
“Saurav is a passionate DevOps engineer specializing in building resilient, automated delivery pipelines. He enjoys solving complex problems with clean”
Saurav
DevOpsINDUSTRY & SECURITY THREAT LANDSCAPE
Codec Networks' evolving fraud threats demand continuous monitoring, advanced analytics, and
proactive intelligence to safeguard financial ecosystems and ensure operational resilience.
Key Business / Industry Dynamics, Trends, Challenges, Threats
- High-value digital payment fraud risk Rapid digital banking growth increases exposure to payment fraud, account takeover, and organized financial crime targeting customers.
- Strict AML and regulatory compliance obligations Institutions must maintain comprehensive fraud monitoring, suspicious activity reporting, and regulatory audit trail capabilities.
- Open banking & API ecosystem expansion Third-party API integrations increase fraud attack surface across digital banking and payment ecosystems.
- Customer trust & reputational risk Even isolated fraud incidents can generate substantial financial and reputational losses affecting customer retention.
- Legacy system fraud vulnerabilities Older core banking systems create fraud detection gaps during digital transformation and modernization initiatives.
Cyber Threats & Challenges
- Payment fraud, account takeover, and card-not-present exploitation
- Synthetic identity fraud targeting loan origination and account opening
- Business email compromise targeting corporate payment authorization
- Insider fraud and unauthorized access to financial systems
How Codec Networks Fraud Risk Mitigation Services Helps
- Provides real-time transaction fraud scoring across payment channels and digital banking platforms.
- Enables synthetic identity detection through cross-channel identity intelligence and behavioral analytics.
- Ensures AML compliance monitoring and audit readiness through centralized fraud incident management.
- Detects insider fraud using behavioral analytics and UEBA across financial system access.
- Reduces fraud response time through automated alerts and coordinated intervention workflows.
INDUSTRY & SECURITY THREAT LANDSCAPE
Codec Networks' evolving fraud threats demand continuous monitoring, advanced analytics, and
proactive intelligence to safeguard financial ecosystems and ensure operational resilience.
Industry Landscape
Key Business / Industry Dynamics, Trends, Challenges, Threats
- High-value digital payment fraud risk Rapid digital banking growth increases exposure to payment fraud, account takeover, and organized financial crime targeting customers.
- Strict AML and regulatory compliance obligations Institutions must maintain comprehensive fraud monitoring, suspicious activity reporting, and regulatory audit trail capabilities.
- Open banking & API ecosystem expansion Third-party API integrations increase fraud attack surface across digital banking and payment ecosystems.
- Customer trust & reputational risk Even isolated fraud incidents can generate substantial financial and reputational losses affecting customer retention.
- Legacy system fraud vulnerabilities Older core banking systems create fraud detection gaps during digital transformation and modernization initiatives.
Cyber Threats & Challenges
- Payment fraud, account takeover, and card-not-present exploitation
- Synthetic identity fraud targeting loan origination and account opening
- Business email compromise targeting corporate payment authorization
- Insider fraud and unauthorized access to financial systems
How Codec Networks Fraud Risk Mitigation Services Helps
- Provides real-time transaction fraud scoring across payment channels and digital banking platforms.
- Enables synthetic identity detection through cross-channel identity intelligence and behavioral analytics.
- Ensures AML compliance monitoring and audit readiness through centralized fraud incident management.
- Detects insider fraud using behavioral analytics and UEBA across financial system access.
- Reduces fraud response time through automated alerts and coordinated intervention workflows.
Key Dynamics & Challenges
- Insurance billing fraud & claims manipulation Healthcare fraud schemes generate enormous losses through phantom billing, upcoding, and organized provider fraud.
- Digital health platform expansion Telemedicine and digital health channels create new fraud vectors for identity exploitation and service fraud.
- Prescription fraud and controlled substance abuse Fraudulent prescription schemes generate financial losses and patient safety risks requiring active monitoring.
- Regulatory compliance obligations Healthcare organizations must report fraud and maintain audit trails under HIPAA and insurance regulatory frameworks.
- Patient identity theft and medical fraud Stolen patient identities enable fraudulent medical service claims and insurance exploitation.
Cyber Threats & Challenges
- Insurance billing fraud through phantom claims and upcoding
- Identity-based fraudulent medical service claims
- Prescription fraud and controlled substance diversion
- Provider kickback and patient recruitment schemes
How Codec Networks Fraud Risk Mitigation Services Helps
- Enables AI-driven claims fraud detection identifying suspicious billing patterns and provider network anomalies.
- Detects identity-based medical fraud through cross-referencing patient identity signals.
- Maintains compliance logs and fraud documentation for healthcare regulatory reporting obligations.
- Supports fraud investigation through network analysis of organized provider fraud schemes.
- Provides centralized visibility across claims processing and healthcare payment channels.
Key Dynamics & Challenges
- Subscription fraud and service exploitation Telecom organizations face fraudulent service registration, subscription abuse, and revenue leakage from fraud.
- Account takeover targeting digital service accounts Compromised customer accounts enable fraudulent service usage and data theft in digital service environments.
- International revenue sharing fraud (IRSF) Sophisticated telecom fraud schemes generate enormous losses through fraudulent international call routing.
- SIM swap and number porting fraud SIM swap fraud enables account takeover across financial and digital services linked to mobile numbers.
- Complex multi-service fraud environments Diverse digital service portfolios create complex fraud monitoring requirements across multiple channels.
Cyber Threats & Challenges
- SIM swap fraud enabling financial account takeover
- International revenue sharing fraud exploiting telecoms infrastructure
- Account takeover targeting digital service platforms
- Subscription fraud and fraudulent service registration
How Codec Networks Fraud Risk Mitigation Services Helps
- Provides real-time fraud monitoring across digital service channels and subscription platforms.
- Detects SIM swap fraud through behavioral and identity anomaly correlation.
- Reduces telecom fraud revenue leakage through intelligent traffic pattern analysis.
- Enables faster fraud detection and service protection across distributed digital environments.
- Supports scalability for high-volume fraud monitoring across large customer bases.
Key Dynamics & Challenges
- High-volume payment fraud exposure Digital retail platforms process enormous transaction volumes creating significant fraud risk across payment channels.
- Account takeover and credential stuffing attacks Automated attacks compromise customer accounts for fraudulent purchases and payment data theft.
- Refund and return fraud exploitation Organized refund fraud schemes generate significant losses through systematic exploitation of return policies.
- Promotion and loyalty program fraud Fraudulent coupon redemption, loyalty point manipulation, and promotional exploitation generate revenue losses.
- Seasonal fraud peaks during high-traffic events Major sales events attract concentrated fraud activity requiring scalable real-time detection capabilities.
Cyber Threats & Challenges
- Card-not-present payment fraud targeting online transactions
- Account takeover enabling fraudulent purchases and data theft
- Organized return and refund fraud schemes
- Promotion abuse and loyalty program exploitation
How Codec Networks Fraud Risk Mitigation Services Helps
- Monitors payment channels detecting fraudulent transactions and unauthorized payment patterns.
- Detects account takeover through behavioral biometrics and access anomaly monitoring.
- Supports PCI-DSS compliance through comprehensive payment fraud monitoring and documentation.
- Identifies organized refund fraud through behavioral pattern analysis across return workflows.
- Enables rapid fraud intervention during peak traffic periods and major promotional events.
Key Dynamics & Challenges
- Procurement fraud and invoice manipulation Complex procurement processes create exploitation opportunities for invoice fraud, kickbacks, and vendor manipulation.
- Supply chain counterfeit component infiltration Fraudulent components entering supply chains under legitimate brand identities pose safety and quality risks.
- Vendor impersonation and payment redirection Business email compromise targeting accounts payable redirects legitimate vendor payments to fraud accounts.
- Insider fraud and unauthorized procurement Employee collusion with vendors and unauthorized procurement commitments generate significant losses.
- Digital procurement platform vulnerabilities E-procurement system adoption creates new fraud vectors requiring specialized monitoring capabilities.
Cyber Threats & Challenges
- Invoice fraud and payment redirection via vendor impersonation
- Procurement kickbacks and supplier collusion schemes
- Counterfeit component infiltration through fraudulent supply chains
- Insider fraud through unauthorized procurement authorization
How Codec Networks Fraud Risk Mitigation Services Helps
- Provides AI-driven invoice fraud detection identifying anomalous billing patterns and vendor activity.
- Detects vendor impersonation through payment destination monitoring and account intelligence.
- Reduces procurement fraud through real-time approval workflow monitoring and segregation controls.
- Secures supply chain integrity through vendor verification and ongoing risk monitoring.
- Enables forensic investigation of procurement fraud for legal enforcement and recovery actions.
Key Dynamics & Challenges
- Rapid digital financial product fraud exposure FinTech growth creates concentrated fraud risk as adversaries exploit new product launches and brand recognition.
- API vulnerability and third-party fraud vectors Open API ecosystems create fraud exploitation opportunities across third-party FinTech integrations.
- Regulatory compliance in evolving frameworks FinTech organizations must navigate complex and evolving financial crime compliance obligations.
Cyber Threats & Challenges
- Synthetic identity fraud at account opening and loan origination
- Payment fraud targeting digital wallet and payment platform customers
- Account takeover exploiting FinTech authentication vulnerabilities
- Regulatory compliance fraud through falsified financial reporting
How Codec Networks Fraud Risk Mitigation Services Helps
- Enables real-time detection of fraudulent account opening using identity intelligence and behavioral analytics.
- Monitors payment channels for unauthorized transactions and digital wallet fraud indicators.
- Supports regulatory compliance monitoring and suspicious activity reporting obligations.
- Detects synthetic identity schemes through cross-referencing identity attributes across data sources.
- Enables faster fraud intervention through automated risk scoring and coordinated response workflows.
Key Dynamics & Challenges
- Billing fraud and meter manipulation Energy organizations face billing fraud through meter manipulation, false usage reporting, and energy theft.
- Procurement fraud in capital project environments Large capital expenditure projects create significant procurement fraud risk through contractor manipulation.
- Vendor fraud in maintenance and service contracts Complex maintenance contracting environments create opportunities for vendor fraud and overbilling.
- Digital metering and IoT fraud vulnerabilities Smart meter and IoT device adoption creates new fraud vectors requiring specialized detection capabilities.
- Regulatory compliance in utility operations Energy regulators require fraud monitoring and reporting capabilities as part of market conduct obligations.
Cyber Threats & Challenges
- Energy theft through meter manipulation and fraudulent billing
- Procurement fraud in major capital project expenditure
- Vendor overbilling and contract fraud in maintenance operations
- Digital meter fraud exploiting smart grid vulnerabilities
How Codec Networks Fraud Risk Mitigation Services Helps
- Provides real-time monitoring of billing data for anomalies indicating energy theft and meter fraud.
- Detects procurement fraud through invoice intelligence and vendor behavior monitoring.
- Reduces contractor fraud through approval workflow monitoring and document intelligence.
- Supports regulatory compliance through fraud monitoring and incident documentation capabilities.
- Enhances visibility into fraud patterns across operational and commercial energy environments.
Key Dynamics & Challenges
- Claims fraud across personal and commercial lines Insurance fraud in claims generates enormous losses across motor, property, health, and liability insurance lines.
- Application fraud and premium manipulation Fraudulent misrepresentation at application reduces premiums fraudulently and creates coverage liability exposure.
- Organized fraud rings targeting insurance systems Coordinated fraud networks submit systematically fraudulent claims across multiple claimants and providers.
- Digital insurance platform fraud vulnerabilities Digital distribution and claims channels create new fraud exploitation vectors requiring specialized detection.
- Regulatory compliance and fraud reporting obligations Insurers must demonstrate active fraud detection and maintain regulatory reporting capabilities.
Cyber Threats & Challenges
- Organized claims fraud rings coordinating multiple fraudulent submissions
- Application fraud through deliberate misrepresentation of risk
- Healthcare insurance billing fraud through phantom services and upcoding
- Identity fraud enabling fraudulent policy purchases and claims
How Codec Networks Fraud Risk Mitigation Services Helps
- Enables AI-powered claims fraud detection identifying suspicious patterns across individual and network levels.
- Detects application fraud through identity intelligence and behavioral anomaly analysis.
- Maintains fraud compliance documentation and regulatory reporting capabilities.
- Supports investigation of organized fraud rings through network analytics and relationship mapping.
- Provides centralized visibility across claims processing, underwriting, and payment channels.
Key Dynamics & Challenges
- High-frequency payment fraud transactions Digital marketplace scale generates enormous fraud transaction volumes requiring automated real-time detection.
- Seller fraud and marketplace manipulation Fraudulent sellers exploit marketplace platforms through review manipulation, counterfeit listings, and payment fraud.
- Customer account compromise at scale Credential stuffing enables mass account takeover affecting large customer populations simultaneously.
- Chargeback fraud and friendly fraud exploitation Fraudulent chargeback claims generate losses while legitimate fraud chargebacks indicate payment control gaps.
- Cross-border fraud complexity International e-commerce creates complex fraud monitoring requirements across diverse jurisdictions and payment systems.
Cyber Threats & Challenges
- Payment fraud and unauthorized transaction exploitation
- Seller fraud and marketplace manipulation through fraudulent listings
- Mass account takeover enabling fraudulent purchase activity
- Chargeback fraud and systematic return abuse
How Codec Networks Fraud Risk Mitigation Services Helps
- Provides real-time payment fraud scoring across marketplace and direct retail transaction channels.
- Detects seller fraud through behavioral monitoring and listing intelligence across marketplace platforms.
- Enables account takeover detection through behavioral biometrics and access anomaly monitoring.
- Supports chargeback fraud investigation through transaction correlation and evidence documentation.
- Scales detection capacity for high-volume transaction environments during peak retail periods.
Key Dynamics & Challenges
- Digital health platform fraud exposure Telemedicine and digital health platforms create new fraud vectors for prescription fraud and service manipulation.
- Patient data fraud and identity exploitation Stolen patient identities enable fraudulent medical service claims across digital health channels.
- Prescription fraud in digital dispensing environments Digital prescription management creates opportunities for fraudulent prescription generation and exploitation.
- Insurance billing fraud through digital platforms Digital health billing platforms create opportunities for systematic billing manipulation and claims fraud.
- Regulatory compliance in digital health fraud monitoring Healthcare regulators require active fraud detection capabilities across digital health service environments.
Cyber Threats & Challenges
- Telemedicine fraud through fraudulent consultations and prescriptions
- Patient identity theft enabling fraudulent digital health service claims
- Digital prescription fraud and controlled substance exploitation
- Insurance billing manipulation through digital health platforms
How Codec Networks Fraud Risk Mitigation Services Helps
- Provides specialized fraud monitoring for digital health platform transactions and service claims.
- Detects identity-based fraud through cross-referencing patient identity signals across data sources.
- Maintains compliance documentation and fraud reporting capabilities for healthcare regulatory obligations.
- Supports investigation of organized digital health fraud through behavioral and network analytics.
- Enhances visibility into fraud patterns across digital health service and payment channels.
Threat Landscape
Threat / Challenge:
Payment fraud targeting digital transactions has grown dramatically alongside e-commerce and digital banking adoption. Card-not-present fraud enables criminals to use stolen card credentials for online purchases without physical possession of the payment instrument. Automated credential testing tools allow fraudsters to validate stolen card data at enormous scale across multiple merchants simultaneously. Organizations face direct financial losses, chargeback costs, and reputational damage from inadequate payment fraud controls.
How Fraud Risk Mitigation Services Help:
- Real-time payment fraud scoring analyzes transaction context, behavioral signals, and risk indicators at authorization.
- Velocity monitoring detects unusual transaction frequency and amount patterns consistent with organized payment fraud.
- Network analytics identifies fraud rings exploiting multiple compromised payment accounts simultaneously.
- Automated fraud intervention prevents fraudulent transactions before financial losses are completed.
Threat / Challenge:
Synthetic identity fraud combines real and fabricated personal information to create plausible but fraudulent identities that evade traditional verification controls. These synthetic identities are cultivated over extended periods—building credit history and account tenure—before being exploited for high-value fraudulent transactions or credit applications. Detection is particularly challenging because synthetic identities exhibit many characteristics of legitimate customers. Organizations face losses from both the fraudulent transactions and the investigation costs of identifying synthetic fraud retrospectively.
How Fraud Risk Mitigation Services Help:
- Identity intelligence cross-referencing detects inconsistencies across identity attributes indicating synthetic construction.
- Behavioral analytics identifies anomalous patterns inconsistent with genuine customer identity history.
- Network analysis surfaces relationships between synthetic identities, common device fingerprints, and address clusters.
- Continuous identity monitoring detects synthetic identity maturation patterns before exploitation occurs.
Threat / Challenge:
Account takeover involves unauthorized access to legitimate customer accounts through credential theft, phishing, SIM swap attacks, or exploitation of authentication vulnerabilities. Compromised accounts provide fraudsters with authenticated access to financial services, payment instruments, and personal data—enabling high-value fraudulent transactions that appear legitimate to payment systems. Credential stuffing attacks use automated tools to test stolen credentials across multiple platforms simultaneously at enormous scale. Organizations face both direct financial losses from fraudulent transactions and customer relationship damage from account compromise incidents.
How Fraud Risk Mitigation Services Help:
- Behavioral biometrics detect anomalous user interaction patterns inconsistent with account holder behavior.
- Device intelligence identifies access from unrecognized or suspicious devices and network characteristics.
- Velocity monitoring detects unusual login patterns and authentication attempts indicating credential attacks.
- Real-time session monitoring identifies suspicious account activity after authentication for immediate intervention.
Threat / Challenge:
Insurance claims fraud encompasses opportunistic individual fraud and sophisticated organized fraud ring activity targeting insurance claims processes. Organized fraud networks coordinate multiple claimants, medical providers, legal representatives, and vehicle repair facilities to submit systematically fraudulent claims across insurance portfolios. Healthcare billing fraud generates enormous losses through phantom service billing, upcoding, and kickback arrangements. The scale and sophistication of organized insurance fraud requires AI-driven detection capabilities that can identify fraud patterns across large claims populations.
How Fraud Risk Mitigation Services Help:
- Machine learning models analyze claim characteristics identifying statistical anomalies and suspicious patterns.
- Network analytics surfaces organized fraud rings connecting claimants, providers, and intermediaries.
- Natural language processing detects fabricated or manipulated claims documentation and misrepresentation.
- Predictive fraud scoring at claims submission enables early intervention before fraudulent settlements occur.
Threat / Challenge:
Procurement and invoice fraud exploits organizational purchasing processes through fraudulent invoice submission, vendor impersonation, and payment redirection schemes. Business email compromise targeting accounts payable teams uses convincing executive or vendor impersonation to redirect legitimate payments to fraudster-controlled accounts. Phantom vendor fraud creates fictitious supplier entities within procurement systems to generate fraudulent payments. Insider involvement in procurement fraud—through kickback arrangements and unauthorized purchasing—represents a particularly challenging detection problem requiring behavioral monitoring.
How Fraud Risk Mitigation Services Help:
- AI-driven invoice analytics detects anomalies in amounts, vendor details, and approval workflow patterns.
- Payment destination monitoring evaluates beneficiary account risk at the moment of payment initiation.
- Vendor behavior analytics detects suspicious account activity including bank detail changes and communication anomalies.
- Approval workflow monitoring identifies threshold manipulation and segregation-of-duties violations.
Threat / Challenge:
Insider fraud involves employees exploiting legitimate system access to commit financial crimes including unauthorized payment authorization, data theft, account manipulation, and procurement corruption. Insider fraudsters exploit their knowledge of organizational processes, approval workflows, and control gaps to conduct fraud that evades external-facing detection systems. The challenge of detecting insider fraud is compounded by the trust inherent in employment relationships and the legitimate access that insiders hold. Organizations face both direct financial losses and the operational disruption of investigating and addressing insider fraud incidents.
How Fraud Risk Mitigation Services Help:
- User and Entity Behavior Analytics (UEBA) establishes behavioral baselines detecting anomalous employee activity.
- Access pattern monitoring identifies unusual financial system access, data queries, and transaction authorization.
- Transaction monitoring correlates employee-initiated approvals with known fraud risk indicators.
- Whistleblower reporting mechanisms capture insider fraud intelligence beyond automated monitoring capabilities.
Threat / Challenge:
Money laundering through fraud schemes involves using fraudulent financial transactions to conceal the origins of criminal proceeds. Fraudsters structure transactions to evade detection thresholds, use multiple accounts and jurisdictions to layer funds, and exploit complex financial products to integrate fraudulent proceeds into legitimate financial flows. The intersection of fraud and money laundering creates complex detection challenges requiring coordination between fraud and AML monitoring functions. Regulatory requirements for suspicious activity reporting create significant compliance obligations for organizations identifying potential fraud-facilitated money laundering.
How Fraud Risk Mitigation Services Help:
- Automated suspicious activity monitoring detects transaction patterns consistent with money laundering typologies.
- Structuring detection identifies transaction sequences designed to evade regulatory reporting thresholds.
- Customer risk profiling identifies accounts demonstrating elevated financial crime risk indicators.
- Integrated fraud and AML monitoring provides comprehensive financial crime visibility across organizational systems.
Threat / Challenge:
Social engineering fraud exploits human trust and cognitive biases to manipulate individuals into initiating fraudulent transactions or disclosing sensitive information. Authorized push payment scams convince legitimate account holders to transfer funds to fraudster accounts—circumventing technical fraud controls because the transaction is authenticated. Phishing campaigns targeting digital banking and payment customers steal credentials enabling account takeover and fraudulent payment initiation. Vishing and smishing attacks exploit telephone and SMS channels to impersonate financial institutions and extract authentication information.
How Fraud Risk Mitigation Services Help:
- Behavioral analytics identifies transaction patterns inconsistent with account holder normal behavior.
- Real-time friction insertion challenges suspicious authorized payment transactions with additional verification.
- Device and communication channel intelligence identifies suspicious access patterns preceding social engineering fraud.
- Customer communication monitoring detects phishing campaign indicators targeting organizational customers.
Threat / Challenge:
Real-time payment systems—enabling instant fund transfers with immediate finality—create unique fraud risks because fraudulent transactions complete before traditional fraud detection systems can intervene. The instant settlement characteristic eliminates the opportunity for post-authorization fraud review that exists in traditional payment systems. Fraudsters specifically exploit real-time payment systems for high-value fraud schemes because recovery of fraudulent payments is extremely difficult once settled. Organizations operating real-time payment services must implement fraud detection capabilities specifically designed for the speed and finality constraints of instant payment environments.
How Fraud Risk Mitigation Services Help:
- Ultra-low latency fraud scoring evaluates real-time payment risk within the authorization window.
- Behavioral and contextual signals provide real-time payment risk assessment without introducing settlement delays.
- Dynamic friction rules challenge high-risk real-time payments with step-up authentication before settlement.
- Post-settlement monitoring identifies fraud patterns requiring investigation and recovery action.
Threat / Challenge:
Organizations face significant regulatory obligations related to fraud monitoring, detection, and reporting across financial crime compliance frameworks. Failure to maintain adequate fraud detection capabilities, suspicious activity reporting processes, and fraud investigation documentation can result in regulatory sanctions, civil liability, and institutional reputational damage. Regulatory frameworks are evolving rapidly in response to the growing scale of digital fraud—creating compliance obligations that require organizations to continuously update their fraud detection and reporting capabilities. Demonstrating proactive fraud mitigation to regulators has become a critical component of financial institution governance.
How Fraud Risk Mitigation Services Help:
- Automated fraud compliance monitoring generates audit-ready evidence of monitoring program effectiveness.
- Suspicious activity reporting workflows ensure timely regulatory notification of identified fraud incidents.
- Detailed fraud investigation documentation supports regulatory examinations and enforcement proceedings.
- Compliance dashboard reporting provides clear visibility into fraud mitigation program performance metrics.
BLOGS & ARTICLES
Codec Networks' shares expert blogs delivering insights on evolving fraud typologies,
mitigation strategies, and proactive financial crime prevention best practices.
BFSI, Insurance, Retail & Healthcare
AI-Driven Fraud Risk Mitigation: Moving from Rule-Based Detection to Predictive Financial Crime Prevention
Read FurtherBFSI, FinTech, E-commerce & Telecommunications
Digital Payment Fraud in Real-Time Ecosystems: Protecting Transaction Integrity in Instant Payment Environments
Read FurtherBFSI, FinTech, IT/ITES, Retail & E-commerce
Account Takeover Prevention: Behavioral Biometrics and Real-Time Authentication Intelligence
Read FurtherRetail & E-commerce, BFSI, FinTech, IT/ITES
E-Commerce Fraud Protection: Defending Digital Retail Revenue During High-Volume Transaction Events
Read FurtherFREQUENTLY ASKED QUESTION
Codec Networks' answers key questions on fraud risk mitigation, financial crime prevention,
and detection services to help organizations make informed fraud management decisions.
These services provide comprehensive fraud detection, prevention, and response capabilities protecting financial operations, customer assets, and business processes from fraud threats.
They enable proactive fraud detection, protect financial integrity, ensure regulatory compliance, and minimize losses from increasingly sophisticated fraud attacks.
Fraud mitigation focuses specifically on financial crime patterns, transaction anomalies, and identity exploitation across operational processes rather than infrastructure security.
BFSI, FinTech, insurance, healthcare, retail, manufacturing, telecommunications, and energy organizations benefit significantly from comprehensive fraud mitigation.
Yes, scalable service models allow SMEs to adopt cost-effective fraud detection and improve their financial crime prevention posture affordably.
Core features include real-time transaction monitoring, AI fraud scoring, behavioral analytics, identity verification, network analysis, and regulatory reporting.
AI models continuously analyze transaction signals, behavioral patterns, and risk indicators generating fraud scores within milliseconds at the point of transaction initiation.
Fraud signal correlation links multiple fraud indicators across channels to identify coordinated attack campaigns invisible in single-channel transaction monitoring.
Yes, comprehensive fraud monitoring covers payment channels, digital banking, insurance claims, procurement systems, and identity verification workflows.
Automation reduces manual review burden by triggering predefined response workflows and streamlining fraud investigation and case management processes.
The team monitors, analyzes, and responds to fraud incidents using AI analytics tools and expert fraud investigation capabilities across all fraud channels.
Yes, continuous fraud monitoring ensures threats are detected and addressed at any time across all operational and digital channels.
Incidents are identified, prioritized, investigated, and resolved using predefined fraud response playbooks and coordinated intervention workflows.
Onboarding includes fraud risk assessment, data source integration, model training, alert threshold configuration, and validation before operational deployment.
Alerts are categorized based on financial severity, fraud type, customer impact potential, and regulatory reporting obligations for optimal response.
It provides continuous monitoring, audit trails, and regulatory reporting capabilities aligned with AML regulations, PCI-DSS, GDPR, and insurance fraud obligations.
Yes, integrated AML and fraud monitoring ensures suspicious activity detection, SAR filing, and financial crime compliance across regulated channels.
It maintains detailed fraud incident logs, investigation records, and enforcement documentation required for regulatory audits and legal proceedings.
It monitors financial operations against defined fraud policies and triggers automated alerts and intervention actions for detected violations.
Yes, it can be configured to align with diverse regulatory requirements including AML, PCI-DSS, consumer protection, and insurance fraud reporting standards.
They protect financial assets, reduce fraud losses, ensure regulatory compliance, preserve customer trust, and improve operational efficiency.
They minimize direct fraud losses, reduce manual review overhead, and prevent the significant financial consequences of undetected large-scale fraud.
ROI includes prevented financial losses, reduced customer attrition from fraud incidents, improved compliance efficiency, and protected revenue streams.
They provide actionable fraud risk intelligence and analytics for informed fraud strategy and business security decisions.
Yes, services scale with expanding transaction volumes, new product lines, and evolving fraud risk environments and regulatory requirements.
CODEC NETWORKS OTHER RELATED SERVICES
Codec Networks offers complementary cybersecurity and financial crime services integrating risk management,
compliance, and advanced protection to strengthen enterprise-wide fraud resilience.
-

Malware scanning detects and identifies malicious software to protect systems from threats and unauthorized access.
-
Malware analysis and device forensics use static and dynamic techniques to uncover threats and investigate compromised systems.
-
Cloud forensics investigates cloud environments to collect, preserve, and analyze digital evidence of cyber incidents securely.
-
Blockchain forensics traces transactions and analyzes blockchain data to detect fraud, money laundering, and cybercrime activities.
-
Cryptocurrency forensics investigates digital currency transactions to uncover fraud, theft, and illicit financial activities effectively.
-

IoT forensics collects and analyzes data from connected devices to investigate security incidents and device misuse.
Malware scanning detects and identifies malicious software to protect systems from threats and unauthorized access.
Malware analysis and device forensics use static and dynamic techniques to uncover threats and investigate compromised systems.
Cloud forensics investigates cloud environments to collect, preserve, and analyze digital evidence of cyber incidents securely.
Blockchain forensics traces transactions and analyzes blockchain data to detect fraud, money laundering, and cybercrime activities.
Cryptocurrency forensics investigates digital currency transactions to uncover fraud, theft, and illicit financial activities effectively.
IoT forensics collects and analyzes data from connected devices to investigate security incidents and device misuse.