

On this page
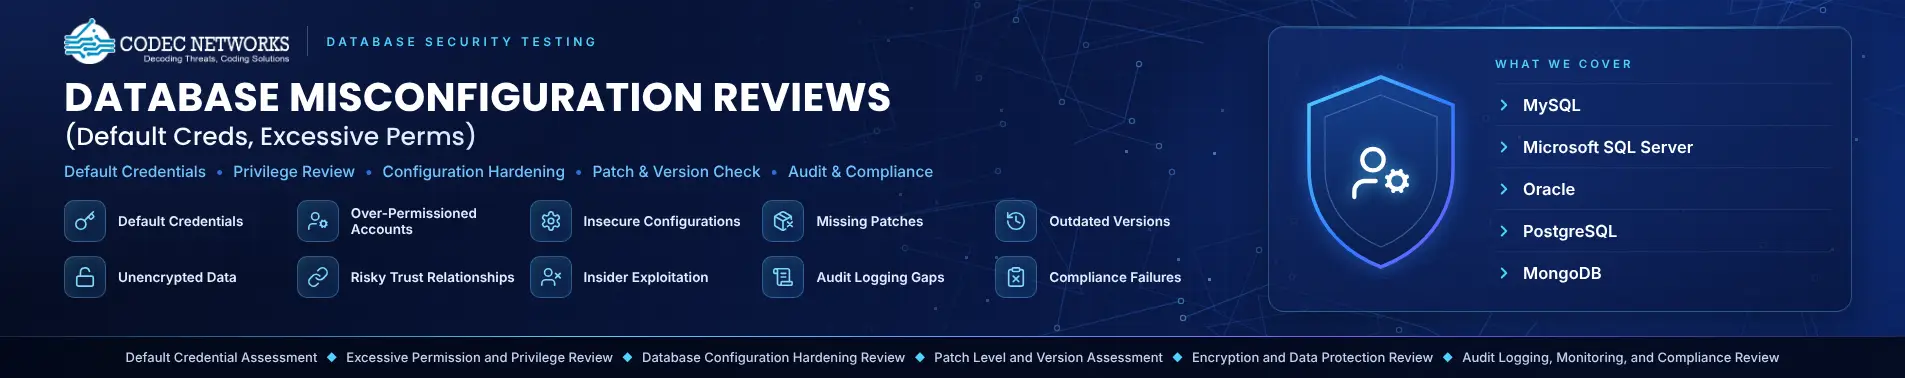
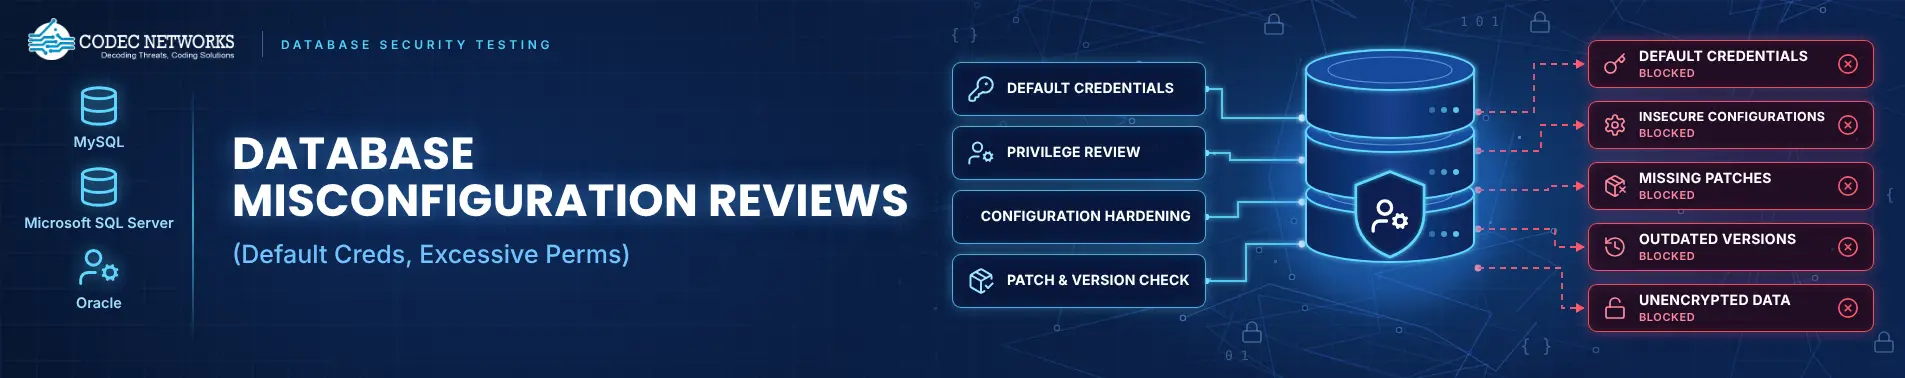

Database Misconfiguration Reviews (Default Creds, Excessive Perms)
Codec Networks' Database Misconfiguration Review is a structured, expert-led assessment that systematically identifies security weaknesses embedded within database environments. It focuses on uncovering unchanged default credentials left over from installation, over-permissioned accounts granting far more access than required, and insecure configuration settings that expose databases to unauthorized access, exploitation, and data theft.
The assessment covers major relational and non-relational database platforms including MySQL, Microsoft SQL Server, Oracle, PostgreSQL, and MongoDB. Reviewers evaluate authentication controls, account privileges, network exposure, encryption status, patch levels, and logging configurations. The service also examines database-to-application trust relationships and service account configurations that are frequently over-privileged.
Findings are risk-rated, validated, and mapped against industry standards including CIS Benchmarks, ISO 27001, PCI DSS, and NIST frameworks. The outcome delivers precise, actionable remediation guidance to harden database environments and significantly reduce the risk of unauthorized data access, insider exploitation, and compliance failures.
Industry Significance
Database Misconfiguration Review is not merely a technical audit — it is a foundational security imperative. It safeguards data integrity, regulatory compliance, business continuity, and stakeholder trust across every sector that relies on structured data storage
Read More
Service Relevance
Database Misconfiguration Reviews identify security weaknesses in database environments through structured configuration audits and expert-led access reviews. Aligned with CIS Benchmarks and global security standards, the service helps prevent unauthorized access, protect sensitive data, and ensure secure, well-governed database infrastructure
Read More
Benefits to Customers
Database Misconfiguration Reviews enable customers to strengthen access governance and protect sensitive data assets. The service improves compliance readiness, enforces least privilege, and supports confident data infrastructure management by identifying configuration weaknesses early and ensuring secure, well-hardened database environments
Read More
Database Misconfiguration Reviews (Default Creds, Excessive Perms)
SERVICE FEATURES AND DELIVERY FRAMEWORK
Codec Networks delivers database security through robust features, proven offerings, efficient delivery
methodology, precise service metrics, and compliance with international standards
Service Features
Database Misconfiguration Reviews identify security weaknesses in database environments through structured configuration audits and expert-led access reviews. Aligned with CIS Benchmarks and global security standards, the service helps prevent unauthorized access, protect sensitive data, and ensure secure, well-governed database infrastructure.
The service features are designed to help organizations eliminate default credentials, enforce least-privilege access, harden database configurations, and maintain compliance across their data infrastructure environments.
Codec Networks offers these services across the following segments:
1. Default Credential Assessment
- Credential Enumeration: Systematically identifies default, unchanged, and commonly known credentials across all database accounts and service users.
- Credential Testing: Validates whether default vendor-supplied credentials for MySQL, MSSQL, Oracle, PostgreSQL, and MongoDB remain in use.
- Service Account Review: Evaluates credentials and configurations of application service accounts connecting to databases.
- Password Policy Assessment: Reviews database-level password complexity, rotation, and enforcement policies.
- Remediation Guidance: Provides specific instructions for replacing default credentials and implementing strong authentication controls.
2. Excessive Permission and Privilege Review
- User Privilege Mapping: Comprehensively maps all database user accounts, roles, and granted permissions against operational requirements.
- Over-Privilege Identification: Identifies accounts possessing administrative rights, excessive schema access, or permissions beyond their functional need.
- Role and Group Analysis: Reviews database roles, group memberships, and inherited privilege chains for unnecessary access.
- Privilege Escalation Testing: Simulates escalation paths that low-privilege accounts could exploit to gain elevated database access.
- Least-Privilege Remediation: Provides structured recommendations to revoke excessive permissions and enforce minimum necessary access.
3. Database Configuration Hardening Review
- CIS Benchmark Assessment: Evaluates database configurations against relevant CIS Benchmark profiles for scoring and gap analysis.
- Unused Feature Identification: Detects enabled database features, stored procedures, and extensions not required for business operations.
- Network Exposure Review: Identifies databases accessible on untrusted network segments or exposed unnecessarily to external interfaces.
- Instance-Level Settings Review: Evaluates critical configuration parameters including remote access settings, logging options, and secure connection requirements.
- Hardening Recommendations: Delivers platform-specific configuration guidance to align with security baselines and reduce attack surface.
4. Patch Level and Version Assessment
- Version Enumeration: Identifies database engine versions across all instances and catalogs known CVEs applicable to each.
- Patch Gap Analysis: Compares installed versions against vendor-recommended current patch levels to identify outdated deployments.
- Third-Party Component Review: Evaluates plugins, extensions, and drivers associated with database environments for patch status.
- Risk Prioritization: Rates unpatched vulnerabilities using CVSS scoring to guide remediation priority.
- Patching Roadmap Guidance: Provides actionable patch management recommendations prioritized by exploitability and business impact.
5. Encryption and Data Protection Review
- Data at Rest Validation: Confirms that sensitive database columns, tablespaces, and files are encrypted using appropriate algorithms.
- Data in Transit Review: Validates that database connections enforce TLS/SSL and reject unencrypted communication.
- Key Management Assessment: Reviews how encryption keys are stored, rotated, and protected across database environments.
- Backup Encryption Check: Confirms that database backups are encrypted and access-controlled appropriately.
- Encryption Recommendations: Provides guidance for implementing database-level, column-level, and transport-layer encryption where missing.
6. Audit Logging, Monitoring, and Compliance Review
- Logging Configuration Assessment: Reviews whether database activity logging captures authentication attempts, privilege use, and data access events.
- Monitoring Coverage Evaluation: Assesses integration of database logs with SIEM platforms and alerting systems.
- Compliance Framework Mapping: Aligns findings with CIS Benchmarks, PCI DSS, ISO 27001, HIPAA, DPDPA, and relevant in-country norms.
- Audit Trail Validation: Confirms audit trails meet retention and tamper-evidence requirements for regulatory purposes.
- Continuous Compliance Support: Provides recurring review cycles to demonstrate ongoing database security governance.
Service Delivery Methodology
Codec Networks Project/Service Delivery Methodology shows the professional lifecycle of service delivery — from initiation through scoping, assessment, reporting, remediation, and continuous assurance. It balances technical rigor, compliance alignment, and business value, which resonates well with SMBs, enterprises, and regulators alike.
This methodology aligns with globally recognized database security standards — including CIS Benchmarks, ISO/IEC 27001, NIST SP 800-53, and PCI DSS — to ensure secure, compliant, and resilient database environments across on-premises, cloud, and hybrid architectures.
Codec Networks' overall Service Delivery methodology comprises of:
1. Project Initiation & Scoping
- Requirement Gathering: Engages with client stakeholders to understand database environments, technology stacks, regulatory obligations, and business objectives.
- Defining Scope: Finalizes database instances, schemas, platforms, and cloud environments in scope, with clear exclusions documented.
- Risk-Based Prioritization: Prioritizes business-critical databases (e.g., core banking, patient records, payment systems) to maximize risk reduction.
- Project Charter: A Statement of Work (SoW) is signed, detailing timelines, milestones, responsibilities, and communication protocols.
2. Pre-Engagement Preparation
- Legal & Compliance Setup: NDAs, data confidentiality agreements, and access authorizations are formalized prior to assessment commencement.
- Environment Alignment: Client provides read-access credentials and connectivity to database environments under controlled conditions.
- Rules of Engagement (RoE): Testing boundaries, working hours, emergency contacts, and stop-conditions are mutually agreed to ensure safe and ethical assessment.
3. Information Gathering & Environment Mapping
- Database Asset Discovery: Identifies all database instances, versions, schemas, and associated service accounts within the defined scope.
- Technology Fingerprinting: Documents database platforms (MySQL, MSSQL, Oracle, PostgreSQL, MongoDB), hosting models, and integration patterns.
- Attack Surface Mapping: Maps identified components to applicable CIS Benchmark controls and known database-specific threat vectors.
4. Vulnerability Assessment
- Automated Configuration Scanning: Tools are applied to scan database configurations against CIS Benchmark and hardening baselines.
- Credential Testing: Default and commonly known credentials are systematically tested against all identified accounts.
- Privilege Audit: Database user and role permissions are enumerated and analyzed for over-privilege and separation of duty violations.
5. Manual Review & Exploitation
- Deep Configuration Review: Expert-led manual review of database instance settings, enabled features, and network exposure configurations.
- Privilege Escalation Testing: Manual attempts to escalate privileges from low-privilege accounts using misconfigurations or trust relationships.
- Encryption Validation: Manual confirmation of encryption in transit and at rest, key management practices, and backup security.
- Logging and Monitoring Review: Manual evaluation of audit log coverage, SIEM integration, and alert configuration effectiveness.
- Controlled Exploitation: Proof-of-concept access demonstrations performed safely without disrupting production data or operations.
6. Post-Assessment Risk Validation
- Impact Analysis: Business, financial, and operational impacts of identified vulnerabilities are assessed and documented.
- Risk Rating: Vulnerabilities are categorized (Critical, High, Medium, Low) using CVSS scoring and CIS Benchmark severity classifications.
- False Positive Elimination: Manual re-testing confirms reported issues are valid, reproducible, and genuinely exploitable.
7. Reporting & Documentation
- Executive Summary: High-level findings, data exposure risks, and strategic recommendations for management decision-making.
- Technical Findings: Detailed configuration gaps, privilege violations, credential risks, and remediation steps with supporting evidence.
- Remediation Guidance: DBA-friendly configuration fixes, secure credential management procedures, and governance recommendations.
- Audit-Ready Evidence: Deliverables formatted to support client's internal and external compliance audits.
8. Remediation Support & Workshops
- Knowledge Transfer Sessions: Walkthrough of findings and remediation with client DBA and security teams.
- DBA Workshops: Secure database administration training including credential hygiene, privilege management, and configuration hardening.
- Security Configuration Guidance: Platform-specific hardening guidance for MySQL, MSSQL, Oracle, PostgreSQL, and MongoDB environments.
- Re-Testing & Validation: Post-remediation verification confirms effective resolution of identified vulnerabilities.
9. Continuous Security & Governance Integration (Optional – Advanced Clients)
- Recurring Assessment Cycles: Scheduled quarterly or bi-annual database reviews for compliance-driven industries.
- Configuration Monitoring Integration: Review outcomes used to configure ongoing database configuration drift monitoring.
- Threat Intelligence Alignment: Reviews enhanced with current threat intelligence on database-targeting attack campaigns.
- Red Teaming (Optional): Advanced adversary simulation targeting database access paths and privilege escalation scenarios.
10. Closure & Governance
- Final Review Meeting: Project completion session with stakeholders for feedback, findings summary, and recommended next steps.
- Client Governance Dashboard: Optional delivery of risk dashboard providing management visibility into database security posture.
- Long-Term Partnership: Offering ongoing database security reviews, managed monitoring, or follow-up assessments for sustained data protection.
|
Standard / Framework |
Scope & Applicability |
How It Is Applied in Service Delivery |
Client Value Delivered |
|
CIS Benchmarks (Database) |
Industry-standard configuration baselines for MySQL, MSSQL, Oracle, PostgreSQL, MongoDB. |
All database configurations assessed against relevant CIS benchmark controls and scoring criteria. |
Ensures configuration hardening aligns with globally recognized security baselines. |
|
ISO/IEC 27001:2022 |
Information Security Management System (ISMS) global standard. |
Service aligned with Annex A controls on access management, asset security, and vulnerability handling. |
Provides confidence in structured, process-driven database security delivery. |
|
NIST SP 800-53 |
U.S. federal security and privacy control framework. |
Findings mapped to AC (Access Control), AU (Audit), and CM (Configuration Management) control families. |
Supports alignment with federal and enterprise governance requirements. |
|
PCI DSS v4.0 |
Payment card industry standard for securing cardholder data environments. |
Database review mapped to PCI DSS Requirements 2, 7, 8, and 10 for configuration, access, and logging. |
Ensures payment-handling database environments remain audit-ready and compliant. |
|
HIPAA Security Rule |
U.S. healthcare standard for electronic PHI protection. |
Reviews validate access controls, encryption, and audit trail configurations protecting health databases. |
Enables compliance for healthcare and HealthTech clients handling sensitive patient data. |
|
GDPR / ISO 27701 |
EU and global data privacy regulations. |
Service delivery validates data minimization, encryption, and access boundary controls across databases. |
Provides privacy assurance for enterprises handling EU resident and PII data. |
|
OWASP Top 10 (A05 - Misconfiguration) |
Global standard highlighting security misconfiguration as a critical application and infrastructure risk. |
Database misconfigurations reviewed and mapped to OWASP A05 category findings. |
Ensures findings integrate with broader application security frameworks. |
|
DPDPA 2023 (India) |
India's Digital Personal Data Protection Act governing handling of personal data. |
Reviews confirm that databases storing Indian resident personal data implement adequate access and security controls. |
Supports legal compliance for organizations operating within India's data protection framework. |
|
CERT Guidelines |
National cyber security audit and assessment requirements. |
Database security reviews aligned to CERT audit expectations for organizations. |
Ensures audit-readiness and legal compliance with national cybersecurity directives. |
|
SOC 2 Type II |
Trust service criteria for SaaS and cloud service providers. |
Database security controls validated against availability, confidentiality, and security trust service criteria. |
Demonstrates database control effectiveness for SaaS and enterprise compliance audits. |
Please Note:
- Database security practices are aligned with widely recognized configuration security and access management methodologies.
- Information security management principles are incorporated to ensure structured, repeatable, and consistent assessment processes.
- Database instances, configurations, and supporting components are reviewed against broadly accepted security control baselines where appropriate.
- Threat modeling and review approaches leverage commonly adopted adversarial techniques and established assessment methodologies.
- Assessment activities follow industry-accepted secure database design, administration, and hardening practices.
- Governance, risk management, and service management principles guide the overall engagement framework, documentation quality, and delivery integrity.
- Total liability for all services is strictly limited to the international standards as far as possible as agreed in contracted engagement value. Codec Networks expressly excludes any indirect, financial, operational, incidental, punitive, or consequential damages, which may arise due to any coincidental events, or changes in international standards guidelines time to time
Service Features
Database Misconfiguration Reviews identify security weaknesses in database environments through structured configuration audits and expert-led access reviews. Aligned with CIS Benchmarks and global security standards, the service helps prevent unauthorized access, protect sensitive data, and ensure secure, well-governed database infrastructure.
The service features are designed to help organizations eliminate default credentials, enforce least-privilege access, harden database configurations, and maintain compliance across their data infrastructure environments.
Codec Networks offers these services across the following segments:
1. Default Credential Assessment
- Credential Enumeration: Systematically identifies default, unchanged, and commonly known credentials across all database accounts and service users.
- Credential Testing: Validates whether default vendor-supplied credentials for MySQL, MSSQL, Oracle, PostgreSQL, and MongoDB remain in use.
- Service Account Review: Evaluates credentials and configurations of application service accounts connecting to databases.
- Password Policy Assessment: Reviews database-level password complexity, rotation, and enforcement policies.
- Remediation Guidance: Provides specific instructions for replacing default credentials and implementing strong authentication controls.
2. Excessive Permission and Privilege Review
- User Privilege Mapping: Comprehensively maps all database user accounts, roles, and granted permissions against operational requirements.
- Over-Privilege Identification: Identifies accounts possessing administrative rights, excessive schema access, or permissions beyond their functional need.
- Role and Group Analysis: Reviews database roles, group memberships, and inherited privilege chains for unnecessary access.
- Privilege Escalation Testing: Simulates escalation paths that low-privilege accounts could exploit to gain elevated database access.
- Least-Privilege Remediation: Provides structured recommendations to revoke excessive permissions and enforce minimum necessary access.
3. Database Configuration Hardening Review
- CIS Benchmark Assessment: Evaluates database configurations against relevant CIS Benchmark profiles for scoring and gap analysis.
- Unused Feature Identification: Detects enabled database features, stored procedures, and extensions not required for business operations.
- Network Exposure Review: Identifies databases accessible on untrusted network segments or exposed unnecessarily to external interfaces.
- Instance-Level Settings Review: Evaluates critical configuration parameters including remote access settings, logging options, and secure connection requirements.
- Hardening Recommendations: Delivers platform-specific configuration guidance to align with security baselines and reduce attack surface.
4. Patch Level and Version Assessment
- Version Enumeration: Identifies database engine versions across all instances and catalogs known CVEs applicable to each.
- Patch Gap Analysis: Compares installed versions against vendor-recommended current patch levels to identify outdated deployments.
- Third-Party Component Review: Evaluates plugins, extensions, and drivers associated with database environments for patch status.
- Risk Prioritization: Rates unpatched vulnerabilities using CVSS scoring to guide remediation priority.
- Patching Roadmap Guidance: Provides actionable patch management recommendations prioritized by exploitability and business impact.
5. Encryption and Data Protection Review
- Data at Rest Validation: Confirms that sensitive database columns, tablespaces, and files are encrypted using appropriate algorithms.
- Data in Transit Review: Validates that database connections enforce TLS/SSL and reject unencrypted communication.
- Key Management Assessment: Reviews how encryption keys are stored, rotated, and protected across database environments.
- Backup Encryption Check: Confirms that database backups are encrypted and access-controlled appropriately.
- Encryption Recommendations: Provides guidance for implementing database-level, column-level, and transport-layer encryption where missing.
6. Audit Logging, Monitoring, and Compliance Review
- Logging Configuration Assessment: Reviews whether database activity logging captures authentication attempts, privilege use, and data access events.
- Monitoring Coverage Evaluation: Assesses integration of database logs with SIEM platforms and alerting systems.
- Compliance Framework Mapping: Aligns findings with CIS Benchmarks, PCI DSS, ISO 27001, HIPAA, DPDPA, and relevant in-country norms.
- Audit Trail Validation: Confirms audit trails meet retention and tamper-evidence requirements for regulatory purposes.
- Continuous Compliance Support: Provides recurring review cycles to demonstrate ongoing database security governance.
DATABASE MISCONFIGURATION REVIEWS - CODEC NETWORK'S INDUSTRY OFFERINGS
Codec Networks bundled offerings combine database misconfiguration reviews with compliance mapping,
industry benchmarks, and sector-focused data security strategies for enterprises worldwide
Foundation Tier
Target Clients:
Small businesses, early-stage organizations, and companies beginning structured database security programs with limited complexity in their database environments.
Sub-Services in Scope:
- Default Credential Identification & Reporting
- Basic Permission & Account Enumeration
- Essential Configuration Baseline Check
- Version & Patch Status Assessment
- Foundational CIS Benchmark Mapping & Reporting
- Basic Remediation Assistance & DBA Advisory
Objective:
Establish fundamental database security hygiene, identify critical credential and configuration risks, and provide essential protection across core database assets.
Value Delivered:
Offers an affordable security baseline, enabling visibility into database exposure, reduced credential risk, and improved governance for foundational data infrastructure.
Enhanced Protection Tier
Target Clients:
Growing mid-sized enterprises, regulated-sector organizations, and companies requiring deeper database security validation and structured access governance.
Sub-Services in Scope
- Comprehensive Privilege & Role Audit
- Advanced Configuration Hardening Review (CIS Benchmarks)
- Encryption & Secure Communication Validation
- Audit Logging & Monitoring Assessment
- Network Exposure & Access Boundary Review
- Enhanced Reporting, Governance & Remediation Support
Objective:
Enhance database security posture through structured privilege reviews, comprehensive configuration hardening, and stronger protection against exploitation and insider threats.
Value Delivered:
Reduces data breach risk, strengthens compliance alignment, and provides sustained protection across evolving database environments and cloud-hosted infrastructure.
Enterprise Resilience Tier
Target Clients:
Large enterprises, financial institutions, healthcare providers, and technology organizations with complex, multi-platform, and cloud-distributed database environments.
Sub-Services in Scope:
- Full-Scope Multi-Platform Database Review
- Adversarial Privilege Escalation Simulation
- Continuous Database Configuration Monitoring Integration
- Secure Database Architecture Review
- Advanced Insider Threat & Access Boundary Testing
- Executive Governance, Metrics & Database Security Program Advisory
Objective:
Deliver full-spectrum database security assurance through deep-dive configuration reviews, adversarial privilege testing, continuous monitoring integration, and comprehensive governance strengthening.
Value Delivered:
Provides enterprise-grade database security visibility, advanced configuration governance, and strategic assurance across mission-critical data environments and global infrastructure.
Foundation Tier
Target Clients:
Small businesses, early-stage organizations, and companies beginning structured database security programs with limited complexity in their database environments.
Sub-Services in Scope:
- Default Credential Identification & Reporting
- Basic Permission & Account Enumeration
- Essential Configuration Baseline Check
- Version & Patch Status Assessment
- Foundational CIS Benchmark Mapping & Reporting
- Basic Remediation Assistance & DBA Advisory
Objective:
Establish fundamental database security hygiene, identify critical credential and configuration risks, and provide essential protection across core database assets.
Value Delivered:
Offers an affordable security baseline, enabling visibility into database exposure, reduced credential risk, and improved governance for foundational data infrastructure.
Enhanced Protection Tier
Target Clients:
Growing mid-sized enterprises, regulated-sector organizations, and companies requiring deeper database security validation and structured access governance.
Sub-Services in Scope
- Comprehensive Privilege & Role Audit
- Advanced Configuration Hardening Review (CIS Benchmarks)
- Encryption & Secure Communication Validation
- Audit Logging & Monitoring Assessment
- Network Exposure & Access Boundary Review
- Enhanced Reporting, Governance & Remediation Support
Objective:
Enhance database security posture through structured privilege reviews, comprehensive configuration hardening, and stronger protection against exploitation and insider threats.
Value Delivered:
Reduces data breach risk, strengthens compliance alignment, and provides sustained protection across evolving database environments and cloud-hosted infrastructure.
Enterprise Resilience Tier
Target Clients:
Large enterprises, financial institutions, healthcare providers, and technology organizations with complex, multi-platform, and cloud-distributed database environments.
Sub-Services in Scope:
- Full-Scope Multi-Platform Database Review
- Adversarial Privilege Escalation Simulation
- Continuous Database Configuration Monitoring Integration
- Secure Database Architecture Review
- Advanced Insider Threat & Access Boundary Testing
- Executive Governance, Metrics & Database Security Program Advisory
Objective:
Deliver full-spectrum database security assurance through deep-dive configuration reviews, adversarial privilege testing, continuous monitoring integration, and comprehensive governance strengthening.
Value Delivered:
Provides enterprise-grade database security visibility, advanced configuration governance, and strategic assurance across mission-critical data environments and global infrastructure.
CODEC NETWORKS VALUE PROPOSITION
Codec Networks delivers advanced database security assurance, protecting your data infrastructure from
misconfigurations, credential risks, and excessive privilege exposure with precision and expertise.
Codec Networks deliver specialized cyber security services focused on identifying and mitigating database security weaknesses arising from misconfigurations, insecure default settings, weak access controls, and excessive user privileges. Through a combination of technical expertise, industry best practices, automated security validation, and risk-driven remediation strategies, the company helps organizations strengthen database security posture, improve regulatory compliance, and reduce the risk of unauthorized access and data breaches.
Key Industry Value Propositions
Proactive Identification of Database Security Weaknesses
- Comprehensive reviews of database environments help identify:
- Default usernames and passwords
- Excessive user privileges
- Weak authentication controls
- Misconfigured access permissions
- Insecure database parameters and settings
- Early detection minimizes the risk of:
- Unauthorized data access
- Insider threats
- Privilege escalation attacks
- Data leakage and ransomware exploitation
Delivery Approach of Codec Networks
Structured & Risk-Based Security Assessment Methodology
Codec Networks follows a systematic and industry-aligned delivery approach that includes:
Assessment Planning & Scoping
- Identification of critical databases, assets, and business applications
- Classification of sensitive and regulated data repositories
- Definition of security review objectives and compliance requirements
Configuration & Access Control Review
- Validation of database configurations against:
- CIS Benchmarks
- OWASP Guidelines
- Vendor security best practices
- Review of:
- Role-based access controls (RBAC)
- Administrative privileges
- Service accounts
- Shared credentials
- Dormant or orphan accounts
Vulnerability & Exposure Analysis
- Detection of:
- Default credentials
- Weak password policies
- Open database ports
- Insecure communication protocols
- Misconfigured audit logging
Remediation Guidance
- Prioritized remediation recommendations based on:
- Risk severity
- Business impact
- Exploitability
- Compliance implications
- Practical hardening guidance to reduce operational disruption
Validation & Reporting
- Detailed technical and executive-level reports
- Risk dashboards and remediation tracking
- Validation testing after remediation implementation
Technical Competency of Codec Networks
Expertise Across Multiple Database Technologies
Cyber security professionals at Codec Networks possess technical expertise in securing:
- Relational Databases:
- Oracle
- Microsoft SQL Server
- MySQL
- PostgreSQL
- IBM DB2
- NoSQL & Big Data Platforms:
- MongoDB
- Cassandra
- Elasticsearch
- Hadoop
- Redis
- Cloud Database Platforms:
- AWS RDS
- Azure SQL
- Google Cloud SQL
- Snowflake
Cyber Security Skills of Professionals
Highly Skilled Cyber Security Professionals
Codec Networks’ security experts demonstrate strong competencies in:
Database Security Hardening
- Secure configuration management
- Access control optimization
- Encryption implementation
- Database activity monitoring
Identity & Privilege Management
- Least privilege enforcement
- Privileged access reviews
- Segregation of duties validation
- Role-based access control implementation
Vulnerability Assessment & Penetration Testing
- Database vulnerability scanning
- Exploitation testing for privilege escalation
- Credential attack simulations
- Configuration weakness analysis
Compliance & Governance
Knowledge of industry regulations and standards including:
- ISO 27001
- PCI-DSS
- GDPR
- HIPAA
- NIST Cybersecurity Framework
- SOC 2
Business Benefits to Organizations
Enhanced Cyber Resilience
- Reduces attack surface created by insecure database configurations
- Prevents unauthorized access to critical business data
- Minimizes risks associated with insider threats and privilege misuse
Improved Regulatory Compliance
- Supports compliance audits through secure configuration validation
- Demonstrates implementation of strong access governance controls
- Reduces non-compliance penalties and audit findings
Reduced Risk of Data Breaches
- Eliminates exploitable default credentials
- Restricts unnecessary privileged access
- Strengthens protection against ransomware and credential-based attacks
Better Visibility & Governance
- Improves visibility into database security posture
- Enables continuous monitoring and governance of privileged accounts
- Facilitates security policy standardization across environments
Cost-Effective Risk Mitigation
- Identifies security gaps before exploitation occurs
- Reduces incident response and recovery costs
- Minimizes operational downtime caused by cyber incidents
Strategic Advantage of Codec Networks
Trusted Security Partner for Enterprise Database Protection
Codec Networks combines:
- Deep technical expertise
- Proven cyber security methodologies
- Skilled security professionals
- Industry best practices
- Risk-focused remediation strategies
to deliver comprehensive database misconfiguration review services that help organizations secure critical data assets, maintain compliance, and strengthen enterprise-wide cyber resilience.
Founded in 2008 with 17+ Years of Industry Experience in Information and Cyber Security domain
Codec Networks Full-Spectrum Cybersecurity Expertise across all Industry Domains:
- Security Vulnerability Assessment & Penetration Testing (VAPT): Covering Web, Mobile, API, IoT, Blockchain, Cloud-Native, and smart infrastructure environments, with a focus on OWASP, MITRE ATT&CK, and real-world exploit simulation.
- Offensive Security & Deep Level Security Assessments: Advanced Red Team, Blue Team and Purple Team Exercises, Threat Simulations, Social Engineering Campaigns, and Secure Code Review.
- IT Security Audit & Compliance Services: Implementation and audit support for ISO/IEC 27001, ISO 27701, NIST CSF, RBI-CSF, SEBI, IRDAI, PCI DSS, HIPAA, SOC 2, GDPR, and India’s DPDPA 2023.
- Data Privacy & Strategic Risk Advisory: ISO 27701, GDPR, DPDPA, Cross-border compliance, DPIA, DPO-as-a-service, supply chain risk management, and digital transformation risk consulting.
- Emerging Technology Security (Web3.0 | AI | Blockchain): Specialized testing for smart contracts, DeFi platforms, Metaverse applications, AI/ML models, quantum readiness, and blockchain nodes.
- Managed SOC & Threat Monitoring Services: End-to-end SOC operations, SIEM/EDR/XDR/SOAR integration, threat intelligence, cloud security monitoring, and 24/7 incident response.
- Cyber Forensics & Threat Analysis: Investigation services including Device forensics, Malware Analysis, Cloud and Mobile forensics, insider threat detection, and Forensic support.
- Board-Level Cybersecurity Advisory Services to build governance, quantify risks, and align with enterprise-wide digital priorities : Codec Networks enables this transformation by offering Integrated Cyber Risk Management, GRC Program Advisory, Reputation Management, Crisis Communication Readiness, and CISO Support, tailored for CXOs and board members seeking to integrate cybersecurity into strategic decision-making.
- Cyber Security Education & Global Certifications - Through the Codec Centre for Professional Excellence, we deliver Post Graduate Certification in Advanced Cybersecurity (PGCAC), Graduate Certification in Advanced Cybersecurity (GCAC), Accredited Trainings & Certifications from EC Council, PECB, TUV, Quality Austria, ISACA and ISC2 - building the next generation of cybersecurity leaders.
- CERT-IN empaneled Information Security Auditing Organization
- NICSI empaneled for providing Application Audit and Compliance Services under Start-Up Category


- An ISO/IEC 27001:2022 certified company, has established Information Security Management System (ISMS), demonstrating a structured approach to manage and protect sensitive information from cyber threats.
- An ISO 9001 certified company, has established and maintains a certified Quality Management System (QMS) that meets international standards for quality and consistency
At Codec Networks, our foundation is built on deep technical mastery, certified expertise, and an unrelenting pursuit of cyber excellence. With a team of globally accredited professionals, advanced methodologies, and next-generation tools, we deliver measurable security outcomes across assessment, compliance, monitoring, and forensic domains.
Our competency-driven approach ensures every engagement is governed by precision, accountability, and alignment with international standards — empowering enterprises to stay secure, compliant, and resilient.
Governance, Risk & Compliance (GRC) Competency
Codec Networks’ dedicated Governance, Risk & Compliance (GRC) group specializes in security assessments, risk management, regulatory compliance, and audit readiness. The team partners with organizations to strengthen governance frameworks and ensure end-to-end compliance in a complex regulatory landscape.
Key Attributes:
- Team of certified auditors and consultants with credentials including ISO 27001 LA/LI, ISO 31000 Risk Specialist, ISO 27701 PIMS, GDPR, SOC 2, HIPAA, CCPA, DPO, CISA, CISM, CRISC, CISSP and other advanced industry certifications.
- Expertise in enterprise risk quantification, privacy impact assessment (PIA/DPIA), audit automation, and supply chain risk mapping.
- Proven track record in implementing ISO-based ISMS/PIMS frameworks, RBI/SEBI/IRDAI audits, and cross-border data compliance projects.
Vulnerability Assessment & Penetration Testing (VAPT) Expertise
Our VAPT teams bring extensive technical depth across Web, Mobile, API, Cloud, Network, Database, Infrastructure, IoT, and People & Process domains.
Every engagement is mapped to OWASP, NIST, MITRE ATT&CK, ISO 27001, PCI DSS, HIPAA, RBI, and GDPR frameworks — ensuring real-world relevance and compliance alignment.
Core Strengths:
- Certified professionals with CEH, C-PENT, LPT, OSCP, OSWE, OSEE, and CREST credentials, averaging 7–10 years of offensive security experience.
- Proven expertise in Red/Blue/Purple Teaming, DevSecOps, secure SDLC, and threat emulation.
- Continuous skill enhancement through CTFs, hackathons, and product certifications (on case to case basis) such as CCNA, CCNP etc
Managed SOC & Threat Intelligence Operations
Codec Networks operates a 24/7 Managed Security Operations Center (SOC) delivering continuous visibility, detection, and response across hybrid environments.
Our SOC integrates SIEM, SOAR, EDR/XDR, and Cloud-Native Analytics to ensure rapid threat detection, incident containment, and business continuity.
Key Capabilities:
- Certified SOC analysts with credentials such as CHFI, CEH, CompTIA CySA+, GCIA, GCFA, and Splunk Certified Architect.
- Integration with platforms like Splunk, QRadar, SentinelOne, CrowdStrike, Elastic, Microsoft Sentinel, and Cortex XSOAR.
- Advanced use cases include cloud posture management, insider threat analytics, MITRE ATT&CK–aligned detections, and threat hunting automation.
- Comprehensive SOC Maturity Assessments and Threat Intelligence Fusion through integration with global feeds and dark web monitoring.
Cyber Forensics & Threat Analysis Expertise
Our Cyber Forensic Division delivers end-to-end investigation, evidence preservation, and digital analysis services — designed to support law enforcement, corporate forensics, and internal response teams.
We combine forensic science with cyber intelligence to identify root causes, trace adversaries, and restore operational integrity.
Core Expertise Areas:
- Device, Network, Cloud, and Mobile Forensics – leveraging latest forensic tools (wherever applicable) such as Autopsy, Cyber Triage, Kape, EnCase, FTK, Magnet AXIOM, and Cellebrite.
- Malware Reverse Engineering and Memory Forensics for incident containment and threat attribution.
- Blockchain & Crypto Forensics – tracing DeFi fraud, NFT manipulation, and crypto laundering activities using Chainalysis, TRM Labs, and Elliptic (wherever applicable).
- Incident Response Support – forensic readiness, eDiscovery, evidence preservation, aligned with ISO/IEC 27037 & 27043.
- Certified experts including CHFI, eCIR, eCDFP, GCFE, GCFA, EnCE, CFCE and ECIH, ensuring investigations meet both technical and legal standards.
Advanced Tools, Frameworks & Continuous Innovation
Codec Networks leverages industry-leading tools and platforms such as Burp Suite Pro, Nessus, Prisma Cloud, Splunk, QRadar, CrowdStrike, SentinelOne, Autopsy, Chainalysis, MythX, and Prowler, (wherever applicable) ensuring accuracy, scalability, and efficiency.
Our methodologies align with globally recognized frameworks including:
- MITRE ATT&CK & D3FEND
- OWASP Top 10 / MASVS / ASVS
- NIST Cybersecurity Framework & SP 800-115
- ISO/IEC 27001, 27701, 31000, 22301
Through ongoing research, Codec Networks continually evolves to address modern threats — from Generative AI prompt attacks and smart contract exploits to IoT zero-days, metaverse impersonation, and quantum-era vulnerabilities.
Compliance-Driven Deliverables
All technical engagements and reports are mapped to major global and Indian compliance frameworks — including ISO 27001, PCI DSS, HIPAA, GDPR, RBI-CSF, SEBI, IRDAI, and DPDPA 2023.
Our structured technical and executive reports support board-level visibility, audit evidence, and certification readiness, ensuring that every engagement drives both technical assurance and regulatory confidence.
Codec Networks – Certified Competence. Proven Expertise. Real-World Cyber Resilience.
Empowering enterprises through advanced security engineering, continuous monitoring, and forensic intelligence.
Agile & Modular Methodology
Our delivery framework integrates global best practices with localized regulatory insight, ensuring each engagement is executed with clarity, accountability, and precision. Clients benefit from seamless onboarding, milestone-driven execution, and transparent reporting throughout the lifecycle.
- Discovery & Scoping: Collaborative workshops to understand business context, IT landscape, compliance obligations, and risk appetite, forming the foundation of a well-defined project scope.
- Risk Profiling & Gap Assessment: Comprehensive evaluation of people, process, and technology controls aligned with ISO 27001, NIST CSF, GDPR, HIPAA, DPDPA 2023, RBI, and PCI DSS.
- Regulatory Mapping & Framework Alignment: Mapping organizational obligations against applicable standards and laws — from ISO & NIST to RBI, SEBI, IRDAI, UIDAI, and DPDPA — including new-age frameworks like ISO 42001 (AI) and FATF for emerging technologies.
- Security Architecture & Control Design: Designing or refining network, cloud, and data security architectures with controls tailored for cloud, AI, OT/ICS, and Web3.0 environments.
- Documentation & Policy Development: Creation and refinement of Policies, SOPs, Risk Registers, DPIAs, Incident Response Plans, and Governance Documents, ensuring audit readiness and legal compliance.
- Implementation & Risk Treatment: Execution of remediation roadmaps, vendor risk management, privacy engineering, and workforce training to mitigate gaps and operationalize security controls.
- Validation, Testing & Audit Readiness: Conducting mock audits, VAPT, forensic readiness, and compliance testing to validate effectiveness and prepare for certifications.
- Governance Reporting & Continual Improvement: Delivering executive dashboards, compliance scorecards, and board-level insights with ongoing advisory through vCISO and DPO-as-a-Service models.
Risk-Based & Business-Oriented Audit Approach
Our methodology goes beyond testing systems — it focuses on how vulnerabilities translate into business, reputational, and compliance risks.
- Deliver Deep Insight: Actionable intelligence into vulnerabilities, attack paths, business impact, and remediation priorities.
- Extend Beyond Tools: Manual and contextual assessments combining automation with human expertise across government, financial, and commercial sectors.
- Actionable Reporting: Executive-friendly reports that translate complex findings into strategic, risk-aware recommendations.
- Efficient Execution: Critical assets prioritized for testing to deliver maximum value within tight engagement windows.
Outcome-Driven Engagements for Security Maturity
Each stage is modular yet interconnected, adaptable to enterprises of any scale or industry. Whether it’s a cloud-native fintech pursuing SOC 2, a healthcare provider ensuring HIPAA alignment, or a bank meeting RBI-CSF requirements, Codec Networks ensures consistency, compliance, and measurable improvement.
Beyond certification checklists, our Post-Audit Support and Continuous Risk Monitoring provide remediation guidance, breach response playbooks, staff training, and ongoing compliance tracking — building sustainable security posture and resilient business continuity.
Codec Networks – Turning Compliance into a Competitive Advantage.
Structured. Measurable. Secure. Always Aligned with Your Business Goals.
At Codec Networks, our clients are not just audit subjects—they are long-term partners in a shared cybersecurity journey. Every engagement is designed around the client’s business priorities, security maturity, and risk appetite, ensuring solutions that are relevant, practical, and results-driven.
With a legacy of 650+ successful engagements across industries such as Banking, Fintech, Healthcare, Telecom, Energy, Aviation, Manufacturing, E-commerce, and Government, Codec Networks has attempted to become a trusted advisor for organizations seeking to transform compliance into resilience.
Our engagement philosophy extends beyond conventional audits. We integrate strategic advisory, technical assurance, remediation support, and continuous compliance monitoring, creating a full lifecycle relationship rather than a one-time service. Clients benefit from:
- Personalized advisory frameworks tailored to their business model and operational scale.
- Collaborative engagement models featuring joint workshops, stakeholder training, and compliance awareness sessions.
- Board-level guidance and reporting that translates complex technical findings into actionable business intelligence.
- Transparent communication channels with dedicated project managers, secure digital workspaces, and real-time status dashboards.
By combining the objectivity of an auditor with the empathy of an advisor, Codec Networks builds trust, accountability, and measurable security growth. Our commitment is simple — to deliver cybersecurity as a continuous partnership, not a periodic project.
Codec Networks – Where Advisory Meets Assurance.
Empowering Clients Through Partnership, Transparency, and Trust.
At Codec Networks, integrity, professionalism, and ethical responsibility form the cornerstone of every engagement. As a trusted strategic partner in cybersecurity, we operate within the highest standards of ethical conduct, legal compliance, and regulatory governance, ensuring our services strengthen both our clients’ defenses and their reputations.
We adhere to a strict ethical code of conduct, driven by transparency, independence, and accountability. Every consultant, auditor, and engineer within Codec Networks upholds the core security triad of Confidentiality, Integrity, and Availability (CIA) — ensuring data protection, operational reliability, and business continuity at all times.
Our professional ethos blends technical excellence with moral responsibility, following structured processes, defined service standards, and adherence to international and national regulatory frameworks.
Our Ethical & Professional Commitments
- Zero-Compromise Consulting: We maintain independence, neutrality, and confidentiality across all audits and advisory engagements.
- Legal & Regulatory Conformance: We assist clients to conform strictly within the boundaries of applicable cyber laws, privacy regulations, and data protection statutes.
- Client-First Philosophy: Every recommendation is designed to safeguard stakeholder interests, minimize legal exposure, and build sustainable resilience.
- Outcome-Driven Security Maturity: Our modular yet integrated delivery approach supports organizations of all sizes in achieving measurable improvements in security posture.
- Global Delivery, Local Integrity: Our Global Network Delivery Model integrates international best practices with local regulatory expertise — ensuring value-driven, compliant outcomes.
Industry-Specific Security Advisory
Recognizing that every sector faces distinct threats and compliance challenges, Codec Networks provides customized, industry-aligned security advisory across BFSI, Fintech, Telecom, Healthcare, Energy, Aviation, E-commerce, Government, and Critical Infrastructure domains.
Our sector-specific consulting translates regulatory complexity into practical, business-aware strategies, ensuring risk mitigation plans are compliant, auditable, and operationally feasible.
Our Commitment
With a zero-tolerance approach to ethical compromise, Codec Networks stands for trust, transparency, and truth in cybersecurity. We are more than consultants — we are custodians of digital integrity, committed to helping organizations navigate risk, maintain compliance, and enable secure business growth.
Codec Networks – Where Integrity Meets Innovation. Trusted. Ethical. Future-Ready.
At Codec Networks, we combine the strength of a global delivery ecosystem with the precision of local regulatory insight to deliver cybersecurity solutions that are both internationally benchmarked and regionally compliant.
Our Global Delivery Capability enables clients across continents to access specialized cybersecurity expertise, advanced technologies, and globally aligned methodologies. Through a distributed network of certified professionals, partner alliances, and intelligence centers, Codec Networks ensures consistent service quality and rapid response across time zones and geographies.
What truly differentiates us is our Local Expertise—a deep understanding of national regulations, industry frameworks, and operational nuances that shape cybersecurity implementation in each region.
Our hybrid delivery model blends remote and on-site collaboration, combining the agility of digital operations with the contextual understanding of local consultants. This ensures culturally aligned communication, faster problem resolution, and seamless coordination with client teams.
With a presence across India, Codec Networks empowers global enterprises to manage cybersecurity uniformly while adapting to local risks, regulations, and realities.
Codec Networks – Global Vision. Local Precision. Consistent Cyber Resilience.
“With Codec Networks, you’re not just buying a service — you’re investing in a cybersecurity ally who understands your business, defends your reputation, and strengthens your future.”
At Codec Networks, we believe cybersecurity is not a project — it’s a partnership.
Our approach is built on trust, transparency, and transformation, helping clients evolve from compliance readiness to cyber resilience.
Your Strategic Security Partner
Codec Networks acts as a strategic security partner, providing continuous roadmap development, architecture reviews, and improvement programs that evolve with your business and the threat landscape.
“We don’t just secure businesses — we empower them to lead with confidence in a digital-first world.”
Our strength lies in the fusion of technical depth, regulatory insight, industry specialization, and future readiness — providing unmatched cybersecurity value to enterprises across India and beyond.
Codec Networks – Certified Competence. Proven Expertise. Real-World Cyber Resilience.
Empowering enterprises through advanced security engineering, continuous monitoring, and forensic intelligence.
Every engagement reflects our belief that advisory must meet assurance — a promise we deliver through partnership, integrity, and measurable impact.
Codec Networks – Where Advisory Meets Assurance.
Empowering Clients Through Partnership, Transparency, and Trust.
And above all —
“Decoding Threats. Coding Solutions.”
That’s the Codec Networks Advantage.
Codec Networks deliver specialized cyber security services focused on identifying and mitigating database security weaknesses arising from misconfigurations, insecure default settings, weak access controls, and excessive user privileges. Through a combination of technical expertise, industry best practices, automated security validation, and risk-driven remediation strategies, the company helps organizations strengthen database security posture, improve regulatory compliance, and reduce the risk of unauthorized access and data breaches.
Key Industry Value Propositions
Proactive Identification of Database Security Weaknesses
- Comprehensive reviews of database environments help identify:
- Default usernames and passwords
- Excessive user privileges
- Weak authentication controls
- Misconfigured access permissions
- Insecure database parameters and settings
- Early detection minimizes the risk of:
- Unauthorized data access
- Insider threats
- Privilege escalation attacks
- Data leakage and ransomware exploitation
Delivery Approach of Codec Networks
Structured & Risk-Based Security Assessment Methodology
Codec Networks follows a systematic and industry-aligned delivery approach that includes:
Assessment Planning & Scoping
- Identification of critical databases, assets, and business applications
- Classification of sensitive and regulated data repositories
- Definition of security review objectives and compliance requirements
Configuration & Access Control Review
- Validation of database configurations against:
- CIS Benchmarks
- OWASP Guidelines
- Vendor security best practices
- Review of:
- Role-based access controls (RBAC)
- Administrative privileges
- Service accounts
- Shared credentials
- Dormant or orphan accounts
Vulnerability & Exposure Analysis
- Detection of:
- Default credentials
- Weak password policies
- Open database ports
- Insecure communication protocols
- Misconfigured audit logging
Remediation Guidance
- Prioritized remediation recommendations based on:
- Risk severity
- Business impact
- Exploitability
- Compliance implications
- Practical hardening guidance to reduce operational disruption
Validation & Reporting
- Detailed technical and executive-level reports
- Risk dashboards and remediation tracking
- Validation testing after remediation implementation
Technical Competency of Codec Networks
Expertise Across Multiple Database Technologies
Cyber security professionals at Codec Networks possess technical expertise in securing:
- Relational Databases:
- Oracle
- Microsoft SQL Server
- MySQL
- PostgreSQL
- IBM DB2
- NoSQL & Big Data Platforms:
- MongoDB
- Cassandra
- Elasticsearch
- Hadoop
- Redis
- Cloud Database Platforms:
- AWS RDS
- Azure SQL
- Google Cloud SQL
- Snowflake
Cyber Security Skills of Professionals
Highly Skilled Cyber Security Professionals
Codec Networks’ security experts demonstrate strong competencies in:
Database Security Hardening
- Secure configuration management
- Access control optimization
- Encryption implementation
- Database activity monitoring
Identity & Privilege Management
- Least privilege enforcement
- Privileged access reviews
- Segregation of duties validation
- Role-based access control implementation
Vulnerability Assessment & Penetration Testing
- Database vulnerability scanning
- Exploitation testing for privilege escalation
- Credential attack simulations
- Configuration weakness analysis
Compliance & Governance
Knowledge of industry regulations and standards including:
- ISO 27001
- PCI-DSS
- GDPR
- HIPAA
- NIST Cybersecurity Framework
- SOC 2
Business Benefits to Organizations
Enhanced Cyber Resilience
- Reduces attack surface created by insecure database configurations
- Prevents unauthorized access to critical business data
- Minimizes risks associated with insider threats and privilege misuse
Improved Regulatory Compliance
- Supports compliance audits through secure configuration validation
- Demonstrates implementation of strong access governance controls
- Reduces non-compliance penalties and audit findings
Reduced Risk of Data Breaches
- Eliminates exploitable default credentials
- Restricts unnecessary privileged access
- Strengthens protection against ransomware and credential-based attacks
Better Visibility & Governance
- Improves visibility into database security posture
- Enables continuous monitoring and governance of privileged accounts
- Facilitates security policy standardization across environments
Cost-Effective Risk Mitigation
- Identifies security gaps before exploitation occurs
- Reduces incident response and recovery costs
- Minimizes operational downtime caused by cyber incidents
Strategic Advantage of Codec Networks
Trusted Security Partner for Enterprise Database Protection
Codec Networks combines:
- Deep technical expertise
- Proven cyber security methodologies
- Skilled security professionals
- Industry best practices
- Risk-focused remediation strategies
to deliver comprehensive database misconfiguration review services that help organizations secure critical data assets, maintain compliance, and strengthen enterprise-wide cyber resilience.
Founded in 2008 with 17+ Years of Industry Experience in Information and Cyber Security domain
Codec Networks Full-Spectrum Cybersecurity Expertise across all Industry Domains:
- Security Vulnerability Assessment & Penetration Testing (VAPT): Covering Web, Mobile, API, IoT, Blockchain, Cloud-Native, and smart infrastructure environments, with a focus on OWASP, MITRE ATT&CK, and real-world exploit simulation.
- Offensive Security & Deep Level Security Assessments: Advanced Red Team, Blue Team and Purple Team Exercises, Threat Simulations, Social Engineering Campaigns, and Secure Code Review.
- IT Security Audit & Compliance Services: Implementation and audit support for ISO/IEC 27001, ISO 27701, NIST CSF, RBI-CSF, SEBI, IRDAI, PCI DSS, HIPAA, SOC 2, GDPR, and India’s DPDPA 2023.
- Data Privacy & Strategic Risk Advisory: ISO 27701, GDPR, DPDPA, Cross-border compliance, DPIA, DPO-as-a-service, supply chain risk management, and digital transformation risk consulting.
- Emerging Technology Security (Web3.0 | AI | Blockchain): Specialized testing for smart contracts, DeFi platforms, Metaverse applications, AI/ML models, quantum readiness, and blockchain nodes.
- Managed SOC & Threat Monitoring Services: End-to-end SOC operations, SIEM/EDR/XDR/SOAR integration, threat intelligence, cloud security monitoring, and 24/7 incident response.
- Cyber Forensics & Threat Analysis: Investigation services including Device forensics, Malware Analysis, Cloud and Mobile forensics, insider threat detection, and Forensic support.
- Board-Level Cybersecurity Advisory Services to build governance, quantify risks, and align with enterprise-wide digital priorities : Codec Networks enables this transformation by offering Integrated Cyber Risk Management, GRC Program Advisory, Reputation Management, Crisis Communication Readiness, and CISO Support, tailored for CXOs and board members seeking to integrate cybersecurity into strategic decision-making.
- Cyber Security Education & Global Certifications - Through the Codec Centre for Professional Excellence, we deliver Post Graduate Certification in Advanced Cybersecurity (PGCAC), Graduate Certification in Advanced Cybersecurity (GCAC), Accredited Trainings & Certifications from EC Council, PECB, TUV, Quality Austria, ISACA and ISC2 - building the next generation of cybersecurity leaders.
- CERT-IN empaneled Information Security Auditing Organization
- NICSI empaneled for providing Application Audit and Compliance Services under Start-Up Category
- An ISO/IEC 27001:2022 certified company, has established Information Security Management System (ISMS), demonstrating a structured approach to manage and protect sensitive information from cyber threats.
- An ISO 9001 certified company, has established and maintains a certified Quality Management System (QMS) that meets international standards for quality and consistency
At Codec Networks, our foundation is built on deep technical mastery, certified expertise, and an unrelenting pursuit of cyber excellence. With a team of globally accredited professionals, advanced methodologies, and next-generation tools, we deliver measurable security outcomes across assessment, compliance, monitoring, and forensic domains.
Our competency-driven approach ensures every engagement is governed by precision, accountability, and alignment with international standards — empowering enterprises to stay secure, compliant, and resilient.
Governance, Risk & Compliance (GRC) Competency
Codec Networks’ dedicated Governance, Risk & Compliance (GRC) group specializes in security assessments, risk management, regulatory compliance, and audit readiness. The team partners with organizations to strengthen governance frameworks and ensure end-to-end compliance in a complex regulatory landscape.
Key Attributes:
- Team of certified auditors and consultants with credentials including ISO 27001 LA/LI, ISO 31000 Risk Specialist, ISO 27701 PIMS, GDPR, SOC 2, HIPAA, CCPA, DPO, CISA, CISM, CRISC, CISSP and other advanced industry certifications.
- Expertise in enterprise risk quantification, privacy impact assessment (PIA/DPIA), audit automation, and supply chain risk mapping.
- Proven track record in implementing ISO-based ISMS/PIMS frameworks, RBI/SEBI/IRDAI audits, and cross-border data compliance projects.
Vulnerability Assessment & Penetration Testing (VAPT) Expertise
Our VAPT teams bring extensive technical depth across Web, Mobile, API, Cloud, Network, Database, Infrastructure, IoT, and People & Process domains.
Every engagement is mapped to OWASP, NIST, MITRE ATT&CK, ISO 27001, PCI DSS, HIPAA, RBI, and GDPR frameworks — ensuring real-world relevance and compliance alignment.
Core Strengths:
- Certified professionals with CEH, C-PENT, LPT, OSCP, OSWE, OSEE, and CREST credentials, averaging 7–10 years of offensive security experience.
- Proven expertise in Red/Blue/Purple Teaming, DevSecOps, secure SDLC, and threat emulation.
- Continuous skill enhancement through CTFs, hackathons, and product certifications (on case to case basis) such as CCNA, CCNP etc
Managed SOC & Threat Intelligence Operations
Codec Networks operates a 24/7 Managed Security Operations Center (SOC) delivering continuous visibility, detection, and response across hybrid environments.
Our SOC integrates SIEM, SOAR, EDR/XDR, and Cloud-Native Analytics to ensure rapid threat detection, incident containment, and business continuity.
Key Capabilities:
- Certified SOC analysts with credentials such as CHFI, CEH, CompTIA CySA+, GCIA, GCFA, and Splunk Certified Architect.
- Integration with platforms like Splunk, QRadar, SentinelOne, CrowdStrike, Elastic, Microsoft Sentinel, and Cortex XSOAR.
- Advanced use cases include cloud posture management, insider threat analytics, MITRE ATT&CK–aligned detections, and threat hunting automation.
- Comprehensive SOC Maturity Assessments and Threat Intelligence Fusion through integration with global feeds and dark web monitoring.
Cyber Forensics & Threat Analysis Expertise
Our Cyber Forensic Division delivers end-to-end investigation, evidence preservation, and digital analysis services — designed to support law enforcement, corporate forensics, and internal response teams.
We combine forensic science with cyber intelligence to identify root causes, trace adversaries, and restore operational integrity.
Core Expertise Areas:
- Device, Network, Cloud, and Mobile Forensics – leveraging latest forensic tools (wherever applicable) such as Autopsy, Cyber Triage, Kape, EnCase, FTK, Magnet AXIOM, and Cellebrite.
- Malware Reverse Engineering and Memory Forensics for incident containment and threat attribution.
- Blockchain & Crypto Forensics – tracing DeFi fraud, NFT manipulation, and crypto laundering activities using Chainalysis, TRM Labs, and Elliptic (wherever applicable).
- Incident Response Support – forensic readiness, eDiscovery, evidence preservation, aligned with ISO/IEC 27037 & 27043.
- Certified experts including CHFI, eCIR, eCDFP, GCFE, GCFA, EnCE, CFCE and ECIH, ensuring investigations meet both technical and legal standards.
Advanced Tools, Frameworks & Continuous Innovation
Codec Networks leverages industry-leading tools and platforms such as Burp Suite Pro, Nessus, Prisma Cloud, Splunk, QRadar, CrowdStrike, SentinelOne, Autopsy, Chainalysis, MythX, and Prowler, (wherever applicable) ensuring accuracy, scalability, and efficiency.
Our methodologies align with globally recognized frameworks including:
- MITRE ATT&CK & D3FEND
- OWASP Top 10 / MASVS / ASVS
- NIST Cybersecurity Framework & SP 800-115
- ISO/IEC 27001, 27701, 31000, 22301
Through ongoing research, Codec Networks continually evolves to address modern threats — from Generative AI prompt attacks and smart contract exploits to IoT zero-days, metaverse impersonation, and quantum-era vulnerabilities.
Compliance-Driven Deliverables
All technical engagements and reports are mapped to major global and Indian compliance frameworks — including ISO 27001, PCI DSS, HIPAA, GDPR, RBI-CSF, SEBI, IRDAI, and DPDPA 2023.
Our structured technical and executive reports support board-level visibility, audit evidence, and certification readiness, ensuring that every engagement drives both technical assurance and regulatory confidence.
Codec Networks – Certified Competence. Proven Expertise. Real-World Cyber Resilience.
Empowering enterprises through advanced security engineering, continuous monitoring, and forensic intelligence.
Agile & Modular Methodology
Our delivery framework integrates global best practices with localized regulatory insight, ensuring each engagement is executed with clarity, accountability, and precision. Clients benefit from seamless onboarding, milestone-driven execution, and transparent reporting throughout the lifecycle.
- Discovery & Scoping: Collaborative workshops to understand business context, IT landscape, compliance obligations, and risk appetite, forming the foundation of a well-defined project scope.
- Risk Profiling & Gap Assessment: Comprehensive evaluation of people, process, and technology controls aligned with ISO 27001, NIST CSF, GDPR, HIPAA, DPDPA 2023, RBI, and PCI DSS.
- Regulatory Mapping & Framework Alignment: Mapping organizational obligations against applicable standards and laws — from ISO & NIST to RBI, SEBI, IRDAI, UIDAI, and DPDPA — including new-age frameworks like ISO 42001 (AI) and FATF for emerging technologies.
- Security Architecture & Control Design: Designing or refining network, cloud, and data security architectures with controls tailored for cloud, AI, OT/ICS, and Web3.0 environments.
- Documentation & Policy Development: Creation and refinement of Policies, SOPs, Risk Registers, DPIAs, Incident Response Plans, and Governance Documents, ensuring audit readiness and legal compliance.
- Implementation & Risk Treatment: Execution of remediation roadmaps, vendor risk management, privacy engineering, and workforce training to mitigate gaps and operationalize security controls.
- Validation, Testing & Audit Readiness: Conducting mock audits, VAPT, forensic readiness, and compliance testing to validate effectiveness and prepare for certifications.
- Governance Reporting & Continual Improvement: Delivering executive dashboards, compliance scorecards, and board-level insights with ongoing advisory through vCISO and DPO-as-a-Service models.
Risk-Based & Business-Oriented Audit Approach
Our methodology goes beyond testing systems — it focuses on how vulnerabilities translate into business, reputational, and compliance risks.
- Deliver Deep Insight: Actionable intelligence into vulnerabilities, attack paths, business impact, and remediation priorities.
- Extend Beyond Tools: Manual and contextual assessments combining automation with human expertise across government, financial, and commercial sectors.
- Actionable Reporting: Executive-friendly reports that translate complex findings into strategic, risk-aware recommendations.
- Efficient Execution: Critical assets prioritized for testing to deliver maximum value within tight engagement windows.
Outcome-Driven Engagements for Security Maturity
Each stage is modular yet interconnected, adaptable to enterprises of any scale or industry. Whether it’s a cloud-native fintech pursuing SOC 2, a healthcare provider ensuring HIPAA alignment, or a bank meeting RBI-CSF requirements, Codec Networks ensures consistency, compliance, and measurable improvement.
Beyond certification checklists, our Post-Audit Support and Continuous Risk Monitoring provide remediation guidance, breach response playbooks, staff training, and ongoing compliance tracking — building sustainable security posture and resilient business continuity.
Codec Networks – Turning Compliance into a Competitive Advantage.
Structured. Measurable. Secure. Always Aligned with Your Business Goals.
At Codec Networks, our clients are not just audit subjects—they are long-term partners in a shared cybersecurity journey. Every engagement is designed around the client’s business priorities, security maturity, and risk appetite, ensuring solutions that are relevant, practical, and results-driven.
With a legacy of 650+ successful engagements across industries such as Banking, Fintech, Healthcare, Telecom, Energy, Aviation, Manufacturing, E-commerce, and Government, Codec Networks has attempted to become a trusted advisor for organizations seeking to transform compliance into resilience.
Our engagement philosophy extends beyond conventional audits. We integrate strategic advisory, technical assurance, remediation support, and continuous compliance monitoring, creating a full lifecycle relationship rather than a one-time service. Clients benefit from:
- Personalized advisory frameworks tailored to their business model and operational scale.
- Collaborative engagement models featuring joint workshops, stakeholder training, and compliance awareness sessions.
- Board-level guidance and reporting that translates complex technical findings into actionable business intelligence.
- Transparent communication channels with dedicated project managers, secure digital workspaces, and real-time status dashboards.
By combining the objectivity of an auditor with the empathy of an advisor, Codec Networks builds trust, accountability, and measurable security growth. Our commitment is simple — to deliver cybersecurity as a continuous partnership, not a periodic project.
Codec Networks – Where Advisory Meets Assurance.
Empowering Clients Through Partnership, Transparency, and Trust.
At Codec Networks, integrity, professionalism, and ethical responsibility form the cornerstone of every engagement. As a trusted strategic partner in cybersecurity, we operate within the highest standards of ethical conduct, legal compliance, and regulatory governance, ensuring our services strengthen both our clients’ defenses and their reputations.
We adhere to a strict ethical code of conduct, driven by transparency, independence, and accountability. Every consultant, auditor, and engineer within Codec Networks upholds the core security triad of Confidentiality, Integrity, and Availability (CIA) — ensuring data protection, operational reliability, and business continuity at all times.
Our professional ethos blends technical excellence with moral responsibility, following structured processes, defined service standards, and adherence to international and national regulatory frameworks.
Our Ethical & Professional Commitments
- Zero-Compromise Consulting: We maintain independence, neutrality, and confidentiality across all audits and advisory engagements.
- Legal & Regulatory Conformance: We assist clients to conform strictly within the boundaries of applicable cyber laws, privacy regulations, and data protection statutes.
- Client-First Philosophy: Every recommendation is designed to safeguard stakeholder interests, minimize legal exposure, and build sustainable resilience.
- Outcome-Driven Security Maturity: Our modular yet integrated delivery approach supports organizations of all sizes in achieving measurable improvements in security posture.
- Global Delivery, Local Integrity: Our Global Network Delivery Model integrates international best practices with local regulatory expertise — ensuring value-driven, compliant outcomes.
Industry-Specific Security Advisory
Recognizing that every sector faces distinct threats and compliance challenges, Codec Networks provides customized, industry-aligned security advisory across BFSI, Fintech, Telecom, Healthcare, Energy, Aviation, E-commerce, Government, and Critical Infrastructure domains.
Our sector-specific consulting translates regulatory complexity into practical, business-aware strategies, ensuring risk mitigation plans are compliant, auditable, and operationally feasible.
Our Commitment
With a zero-tolerance approach to ethical compromise, Codec Networks stands for trust, transparency, and truth in cybersecurity. We are more than consultants — we are custodians of digital integrity, committed to helping organizations navigate risk, maintain compliance, and enable secure business growth.
Codec Networks – Where Integrity Meets Innovation. Trusted. Ethical. Future-Ready.
At Codec Networks, we combine the strength of a global delivery ecosystem with the precision of local regulatory insight to deliver cybersecurity solutions that are both internationally benchmarked and regionally compliant.
Our Global Delivery Capability enables clients across continents to access specialized cybersecurity expertise, advanced technologies, and globally aligned methodologies. Through a distributed network of certified professionals, partner alliances, and intelligence centers, Codec Networks ensures consistent service quality and rapid response across time zones and geographies.
What truly differentiates us is our Local Expertise—a deep understanding of national regulations, industry frameworks, and operational nuances that shape cybersecurity implementation in each region.
Our hybrid delivery model blends remote and on-site collaboration, combining the agility of digital operations with the contextual understanding of local consultants. This ensures culturally aligned communication, faster problem resolution, and seamless coordination with client teams.
With a presence across India, Codec Networks empowers global enterprises to manage cybersecurity uniformly while adapting to local risks, regulations, and realities.
Codec Networks – Global Vision. Local Precision. Consistent Cyber Resilience.
“With Codec Networks, you’re not just buying a service — you’re investing in a cybersecurity ally who understands your business, defends your reputation, and strengthens your future.”
At Codec Networks, we believe cybersecurity is not a project — it’s a partnership.
Our approach is built on trust, transparency, and transformation, helping clients evolve from compliance readiness to cyber resilience.
Your Strategic Security Partner
Codec Networks acts as a strategic security partner, providing continuous roadmap development, architecture reviews, and improvement programs that evolve with your business and the threat landscape.
“We don’t just secure businesses — we empower them to lead with confidence in a digital-first world.”
Our strength lies in the fusion of technical depth, regulatory insight, industry specialization, and future readiness — providing unmatched cybersecurity value to enterprises across India and beyond.
Codec Networks – Certified Competence. Proven Expertise. Real-World Cyber Resilience.
Empowering enterprises through advanced security engineering, continuous monitoring, and forensic intelligence.
Every engagement reflects our belief that advisory must meet assurance — a promise we deliver through partnership, integrity, and measurable impact.
Codec Networks – Where Advisory Meets Assurance.
Empowering Clients Through Partnership, Transparency, and Trust.
And above all —
“Decoding Threats. Coding Solutions.”
That’s the Codec Networks Advantage.
WHAT OUR CUSTOMERS SAY
Reliable, responsive, and results-driven — Codec Networks' security consultants delivered precise,
high-impact database security assessments that strengthened our data governance program
-
“Vijay Pratap is a passionate Software Developer specializing in building scalable web applications and APIs. He enjoys solving complex problems with clean,”
Vijay Pratap
Software Developer
“Vijay Pratap is a passionate Software Developer specializing in building scalable web applications and APIs. He enjoys solving complex problems with clean,”
Vijay Pratap
Software DeveloperINDUSTRY & SECURITY THREAT LANDSCAPE
Mapping the industry and security threat landscape empowers organizations to anticipate database risks,
strengthen data protection, and ensure sustainable business continuity.
Business & Cyber Challenges
- Core banking systems, payment databases, and customer account repositories operate with accumulated configuration debt and over-permissioned service accounts.
- Regulatory mandates from in-country regulatory bodies require demonstrable database security controls and audit trails.
- Threats include credential stuffing against database authentication, insider data theft, and ransomware targeting financial databases.
- Legacy database systems integrated with modern applications introduce privilege mismatches and credential synchronization gaps.
- Unauthorized access to financial databases can expose millions of customer records and trigger severe regulatory consequences.
How Database Misconfiguration Reviews Help
- Identifies unchanged default credentials and over-privileged service accounts before attackers exploit them.
- Demonstrates compliance with in-country regulatory and GDPR requirements for financial data protection and access governance.
- Protects customer financial records by ensuring database access is restricted to authorized users and applications only.
- Detects misconfigurations in core banking database integrations that create unauthorized access pathways.
- Provides remediation guidance to continuously strengthen financial database environments and access control frameworks.
INDUSTRY & SECURITY THREAT LANDSCAPE
Mapping the industry and security threat landscape empowers organizations to anticipate database risks,
strengthen data protection, and ensure sustainable business continuity.
Industry Landscape
Business & Cyber Challenges
- Core banking systems, payment databases, and customer account repositories operate with accumulated configuration debt and over-permissioned service accounts.
- Regulatory mandates from in-country regulatory bodies require demonstrable database security controls and audit trails.
- Threats include credential stuffing against database authentication, insider data theft, and ransomware targeting financial databases.
- Legacy database systems integrated with modern applications introduce privilege mismatches and credential synchronization gaps.
- Unauthorized access to financial databases can expose millions of customer records and trigger severe regulatory consequences.
How Database Misconfiguration Reviews Help
- Identifies unchanged default credentials and over-privileged service accounts before attackers exploit them.
- Demonstrates compliance with in-country regulatory and GDPR requirements for financial data protection and access governance.
- Protects customer financial records by ensuring database access is restricted to authorized users and applications only.
- Detects misconfigurations in core banking database integrations that create unauthorized access pathways.
- Provides remediation guidance to continuously strengthen financial database environments and access control frameworks.
Business & Cyber Challenges
- Rapid development cycles in FinTech frequently result in database deployments that inherit default settings without proper hardening.
- Transaction databases and KYC repositories store high-value data attractive to sophisticated attackers.
- Excessive application service account permissions create lateral movement pathways in microservices architectures.
- Third-party integrations and partner access introduce external privilege risks into database environments.
How Database Misconfiguration Reviews Help
- Identifies default credentials and excessive permissions within transaction and KYC database environments.
- Validates that service account permissions align with the principle of least privilege across microservice deployments.
- Reviews partner and third-party database access controls for boundary enforcement effectiveness.
- Protects sensitive payment and identity data through comprehensive configuration hardening guidance.
- Builds trust with regulators and partners by demonstrating proactive database security governance.
Business & Cyber Challenges
- Patient health record databases (EHR systems) contain highly sensitive PHI sought by ransomware operators and data brokers.
- Compliance requirements including HIPAA, GDPR, and DPDPA 2023 demand strict database access controls and audit trails.
- Healthcare database environments frequently contain stale accounts from past employees and contractors retaining active permissions.
- Cloud-hosted health databases introduce configuration complexity that often results in misconfigured access controls.
- Insider threats represent a significant risk in healthcare environments with broad clinical access to database systems.
How Database Misconfiguration Reviews Help
- Identifies and eliminates stale accounts, default credentials, and over-permissioned clinical users in health databases.
- Validates database access controls meet HIPAA, GDPR, and DPDPA requirements for PHI protection.
- Reviews cloud-hosted health database configurations for access control and encryption compliance.
- Reduces the risk of ransomware success by hardening database authentication and limiting privilege escalation paths.
- Supports audit readiness through structured configuration evidence and compliance-aligned reporting.
Business & Cyber Challenges
- Product catalog, customer, and payment databases represent high-value targets for credential exploitation and data theft.
- Rapid platform growth often results in accumulated service accounts and permissions that exceed operational requirements.
- PCI DSS compliance requires demonstrable database access controls and audit logging for cardholder data environments.
- Bot-driven attacks targeting database-backed inventory and pricing systems can result in significant financial losses.
- Customer trust is directly tied to data security; database breaches result in immediate reputational and commercial damage.
How Database Misconfiguration Reviews Help
- Identifies excessive permissions and default credentials across customer, payment, and inventory database systems.
- Validates PCI DSS compliance for cardholder data environment database configurations.
- Reviews audit logging coverage to support forensic capability in the event of a security incident.
- Provides clear remediation roadmaps to continuously maintain database security through platform growth.
- Protects brand reputation by ensuring customer data remains inaccessible to unauthorized parties.
Business & Cyber Challenges
- Subscriber databases, billing systems, and network management databases hold sensitive personal and operational data.
- 5G infrastructure deployments introduce cloud-native database configurations that require specialized security review.
- Telecom providers represent critical national infrastructure, making their databases attractive to nation-state actors.
- Regulatory obligations from in-country authorities require demonstrable data protection and access governance controls.
- Legacy database systems integrated with modern 5G platforms create credential and permission management challenges.
How Database Misconfiguration Reviews Help
- Identifies default credentials and privilege vulnerabilities in subscriber and network management database systems.
- Validates cloud-native database security configurations in 5G and virtualized telecom environments.
- Reviews segregation of duty controls and access boundaries for sensitive network operations databases.
- Supports compliance with in-country regulatory data protection requirements for telecom operators.
- Strengthens database resilience against nation-state targeting and advanced persistent threat activity.
Business & Cyber Challenges
- Multi-tenant SaaS databases require strict permission boundaries to prevent cross-customer data exposure.
- Development and staging databases frequently retain production-equivalent configurations with weaker access controls.
- Compliance demands across ISO 27001, SOC 2, and GDPR require structured evidence of database access governance.
- DevOps-driven rapid deployment cycles accumulate database configuration debt without corresponding security review.
- Insider threats and insecure CI/CD pipeline access to production databases represent persistent risks.
How Database Misconfiguration Reviews Help
- Validates multi-tenant database isolation controls and permission boundary enforcement.
- Reviews development and staging database security alignment with production-equivalent hardening standards.
- Confirms that CI/CD pipeline service account privileges follow least-privilege principles.
- Supports SOC 2 and ISO 27001 compliance through structured database security evidence and reporting.
- Builds customer confidence by demonstrating secure, well-governed SaaS database delivery.
Business & Cyber Challenges
- Government databases storing citizen identity, tax records, and benefit data require strict access control and configuration governance.
- Nation-state attackers target government databases for intelligence value and disruption potential.
- Data sovereignty and privacy regulations require demonstrable database security controls for public sector data assets.
- Inter-agency database access arrangements frequently result in excessive cross-department permission grants.
- Legacy government database systems accumulate configuration debt and stale accounts over multi-year operational periods.
How Database Misconfiguration Reviews Help
- Identifies stale accounts, default credentials, and excessive permissions across citizen and operational databases.
- Validates database configurations against national cybersecurity standards and audit requirements.
- Reviews inter-agency access arrangements for least-privilege compliance and boundary enforcement.
- Supports compliance with DPDPA, in-country regulatory requirements, and data sovereignty obligations.
- Enhances database resilience against nation-state exploitation through systematic configuration hardening.
8. Energy, Utilities & Critical Infrastructure
Business & Cyber Challenges
- Operational technology databases and SCADA historian systems contain critical control and measurement data.
- Nation-state and hacktivist groups specifically target energy and utility databases for sabotage and intelligence.
- Legacy OT database systems frequently operate with default vendor credentials and unpatched configurations.
- Regulatory frameworks including NERC CIP and ISO 27019 mandate database security controls for critical infrastructure.
- Operational disruption from database compromise can affect millions of consumers and national infrastructure.
How Database Misconfiguration Reviews Help
- Identifies default credentials in OT and SCADA historian databases that represent immediate exploitation risk.
- Reviews access controls and network exposure for critical infrastructure database environments.
- Supports compliance with NERC CIP and ISO 27019 database security requirements.
- Prevents unauthorized database access that could enable manipulation of utility operations or data.
- Strengthens database resilience against ransomware and nation-state-level attacks on critical infrastructure.
9. Transportation & Aviation (Airlines, Railways, Logistics)
Business & Cyber Challenges
- Passenger data, biometric records, and reservation databases represent high-value targets for theft and fraud.
- APIs and applications connecting transportation platforms to backend databases expand credential and access risks.
- Regulatory oversight from in-country authorities and international aviation bodies mandates data protection controls.
- Business logic database access patterns in booking and loyalty systems frequently result in excessive application permissions.
- Integration between airline, rail, and logistics database systems creates cross-organizational privilege management complexity.
How Database Misconfiguration Reviews Help
- Identifies excessive permissions and default credentials in passenger and operational database systems.
- Reviews application service account database permissions for compliance with least-privilege principles.
- Validates encryption and access control configurations protecting biometric and passenger identity data.
- Supports compliance with in-country regulatory privacy requirements and international transport security standards.
- Enhances passenger trust through demonstrable commitment to secure data infrastructure governance.
Business & Cyber Challenges
- Operational technology databases and SCADA historian systems contain critical control and measurement data.
- Nation-state and hacktivist groups specifically target energy and utility databases for sabotage and intelligence.
- Legacy OT database systems frequently operate with default vendor credentials and unpatched configurations.
- Regulatory frameworks including NERC CIP and ISO 27019 mandate database security controls for critical infrastructure.
- Operational disruption from database compromise can affect millions of consumers and national infrastructure.
How Database Misconfiguration Reviews Help
- Identifies default credentials in OT and SCADA historian databases that represent immediate exploitation risk.
- Reviews access controls and network exposure for critical infrastructure database environments.
- Supports compliance with NERC CIP and ISO 27019 database security requirements.
- Prevents unauthorized database access that could enable manipulation of utility operations or data.
- Strengthens database resilience against ransomware and nation-state-level attacks on critical infrastructure.
Business & Cyber Challenges
- Passenger data, biometric records, and reservation databases represent high-value targets for theft and fraud.
- APIs and applications connecting transportation platforms to backend databases expand credential and access risks.
- Regulatory oversight from in-country authorities and international aviation bodies mandates data protection controls.
- Business logic database access patterns in booking and loyalty systems frequently result in excessive application permissions.
- Integration between airline, rail, and logistics database systems creates cross-organizational privilege management complexity.
How Database Misconfiguration Reviews Help
- Identifies excessive permissions and default credentials in passenger and operational database systems.
- Reviews application service account database permissions for compliance with least-privilege principles.
- Validates encryption and access control configurations protecting biometric and passenger identity data.
- Supports compliance with in-country regulatory privacy requirements and international transport security standards.
- Enhances passenger trust through demonstrable commitment to secure data infrastructure governance.
Business & Cyber Challenges
- Student records, assessment databases, and payment systems contain sensitive personal data warranting strong access controls.
- EdTech platforms prioritizing speed-to-market frequently deploy databases without completing hardening processes.
- Compliance obligations including GDPR, DPDPA, and FERPA require demonstrable database security controls.
- Credential stuffing and unauthorized access attempts against educational databases are increasing in frequency.
- Multi-institution database sharing arrangements create permission boundary and data isolation challenges.
How Database Misconfiguration Reviews Help
- Identifies default credentials and excessive permissions across student record and operational databases.
- Reviews configuration hardening across LMS, assessment, and payment database environments.
- Supports GDPR, DPDPA, and FERPA compliance through structured database security evidence.
- Validates access isolation between institutional database environments in shared platform scenarios.
- Builds trust among students, parents, and institutions by demonstrating secure data infrastructure practices.
Threat Landscape
Threat/Challenge:
Database management systems ship with vendor-defined default usernames and passwords that are intended for initial setup purposes. In a significant proportion of production environments, these credentials remain unchanged long after deployment. Attackers maintain curated lists of default credentials for every major database platform and systematically scan for exposed database ports to attempt login.
Once authenticated using default credentials, attackers gain unrestricted administrative access to the database engine, all hosted schemas, and potentially the underlying operating system through stored procedures. Even a single database instance with unchanged default credentials can serve as the pivot point for a full enterprise data breach. The consequences range from complete data exfiltration to ransomware deployment across connected systems.
How Database Misconfiguration Reviews Help
- Systematically identifies all default and vendor-supplied credentials remaining active across database instances.
- Tests authentication endpoints using known default credential pairs for each assessed database platform.
- Validates that post-installation credential change procedures have been completed across all environments.
- Provides specific guidance for implementing strong credential policies and secure authentication configurations.
Threat/Challenge:
Database environments accumulate excessive permissions over time through operational shortcuts, legacy access grants, and service account over-provisioning. Developers, application accounts, and operational users frequently retain broader database access than their current roles require. Excessive privilege creates both insider threat and external attacker risk — anyone compromising an over-privileged account gains far greater access than intended.
Privilege abuse enables attackers to read sensitive data outside their authorization scope, modify or delete records, and potentially execute operating system commands through database-linked functions. Over time, accumulated privilege debt creates an expanding blast radius that transforms any credential compromise into a catastrophic data breach. Without regular privilege reviews and least-privilege enforcement, organizations operate with a persistently elevated risk exposure.
How Database Misconfiguration Reviews Help
- Maps all database user accounts, roles, and permissions against documented operational requirements.
- Identifies accounts possessing administrative rights, schema-level access, or execute permissions beyond functional need.
- Simulates privilege escalation scenarios to confirm the real-world impact of over-permissioned configurations.
- Provides structured remediation guidance for revoking excessive permissions and implementing least-privilege enforcement.
Threat/Challenge:
Database engines deploy with default configurations that prioritize functionality and compatibility over security. Unused features, remote access capabilities, debugging interfaces, and legacy protocol support remain enabled across many production environments. These settings expand the attack surface unnecessarily and provide attackers with additional exploitation pathways beyond direct credential attacks.
Insecure configurations enable attackers to leverage stored procedures for command execution, exploit remote access interfaces exposed on network segments, and abuse enabled features to pivot from database access to broader infrastructure compromise. Configuration weaknesses compound the impact of credential and privilege vulnerabilities by providing additional tools for exploitation and persistence.
How Database Misconfiguration Reviews Help
- Evaluates database configurations against CIS Benchmark controls and hardening standards for each platform.
- Identifies enabled features, remote access settings, and legacy protocols that create unnecessary attack surface.
- Reviews network exposure configurations to confirm databases are accessible only from authorized systems and segments.
- Provides platform-specific hardening guidance to eliminate unnecessary functionality and reduce configuration risk.
Threat/Challenge:
Database management systems are complex software products that regularly receive security patches addressing discovered vulnerabilities. Organizations frequently delay database patching due to concerns about operational disruption, application compatibility, or maintenance window constraints. Running unpatched database engines exposes organizations to exploitation of publicly known vulnerabilities with available proof-of-concept exploit code.
Automated attack tools specifically target known CVEs in common database engines, making unpatched systems low-effort targets for opportunistic attackers. Critical vulnerabilities in database platforms can enable remote code execution, authentication bypass, and privilege escalation without requiring valid credentials. The longer a known vulnerability remains unpatched, the higher the probability of successful exploitation.
How Database Misconfiguration Reviews Help
- Enumerates database engine versions and correlates against current CVE databases for each platform.
- Identifies critical unpatched vulnerabilities with documented exploitation potential.
- Evaluates third-party plugins, extensions, and drivers for patch status alongside core engine versions.
- Provides risk-prioritized patching recommendations ordered by exploitability and business impact.
Threat/Challenge:
Databases frequently store sensitive data without adequate encryption controls at the column, tablespace, or storage layer. Connection encryption between applications and databases is often disabled or configured with weak parameters. When encryption is absent or improperly implemented, attackers who gain network access or storage-level access can directly read sensitive data without requiring database authentication.
Missing encryption amplifies the impact of every other database vulnerability. An attacker who intercepts unencrypted database traffic or accesses unencrypted backup files can exfiltrate complete datasets without triggering authentication controls. Regulatory frameworks universally require encryption of sensitive data at rest and in transit, making encryption gaps both a security and compliance risk simultaneously.
How Database Misconfiguration Reviews Help
- Validates that TLS/SSL is enforced for all database connections and rejects unencrypted communication attempts.
- Reviews encryption at rest configurations for sensitive schemas, columns, and tablespaces.
- Confirms that database backup files are encrypted and protected with appropriate access controls.
- Provides specific encryption implementation guidance aligned with regulatory and compliance requirements.
Threat/Challenge:
Database audit logging is frequently disabled, incompletely configured, or limited to recording only failed login attempts rather than comprehensive activity. Without adequate logging, organizations cannot detect unauthorized access attempts, privilege abuse, or data exfiltration in progress. The absence of audit trails also prevents forensic investigation following security incidents, complicating breach response and regulatory reporting.
Attackers operating within database environments rely on the absence of monitoring to maintain persistence, exfiltrate data slowly, and avoid detection. Regulatory frameworks including PCI DSS, HIPAA, and ISO 27001 mandate specific database audit logging requirements, making logging gaps both a security weakness and a compliance deficiency. Organizations cannot protect what they cannot observe.
How Database Misconfiguration Reviews Help
- Reviews database audit logging configurations for coverage of authentication, privilege use, and data access events.
- Evaluates integration of database logs with centralized SIEM platforms and alerting infrastructure.
- Confirms that audit log retention meets regulatory requirements and logs are protected against tampering.
- Provides recommendations for implementing comprehensive database activity monitoring across all environments.
Threat/Challenge:
Database management systems exposed on broad network segments or accessible directly from untrusted networks represent a significant attack surface. Default database ports for MySQL, MSSQL, Oracle, and PostgreSQL are well-known and actively scanned by automated reconnaissance tools globally. Databases accessible from the internet or unrestricted internal segments without compensating controls are routinely targeted by opportunistic attackers.
Exposed database network interfaces allow attackers to directly attempt authentication attacks, exploit unpatched vulnerabilities, and enumerate instance configurations without first needing application-layer access. Network-accessible databases also increase the scope of impact from other security incidents, enabling lateral movement from compromised hosts to database systems across insufficiently segmented environments.
How Database Misconfiguration Reviews Help
- Identifies database instances accessible on untrusted network segments or exposed on default ports.
- Reviews firewall rules and network access controls governing database connectivity from application and user tiers.
- Evaluates remote administration interface configurations and access restrictions.
- Provides network segmentation and access control recommendations to reduce database exposure.
Threat/Challenge:
Database backups and replication configurations frequently inherit inadequate security controls from primary database environments. Backup files stored without encryption or with overly permissive access controls represent a complete copy of database contents accessible without database authentication. Replication configurations with weak authentication or excessive replication user permissions create additional exploitation pathways.
Attackers who identify accessible backup storage can exfiltrate complete database contents without interacting with the live database system, bypassing authentication controls entirely. Insecure replication configurations enable unauthorized subscription to database change streams, providing persistent access to data modifications. Backup and replication security is frequently overlooked in standard database reviews despite its critical impact.
How Database Misconfiguration Reviews Help
- Reviews backup storage configurations for encryption and access control appropriateness.
- Evaluates replication user accounts for least-privilege compliance and authentication strength.
- Identifies backup retention configurations that create unnecessary long-term data exposure risk.
- Provides backup and replication security hardening guidance aligned with platform best practices.
Threat/Challenge:
Organizations handling sensitive data face increasing regulatory obligations requiring demonstrable database security controls. Frameworks including PCI DSS, HIPAA, ISO 27001, DPDPA, and in-country norms mandate specific configuration, access control, encryption, and logging requirements for databases handling regulated data. Lack of structured database security reviews frequently results in compliance gaps identified only during external audits.
Non-compliance with database security requirements results in significant financial penalties, operational restrictions, and reputational damage. Regulatory bodies are increasing their scrutiny of database security practices following high-profile breach incidents where basic configuration controls were absent. Organizations demonstrating proactive database security governance receive more favorable regulatory treatment than those responding reactively.
How Database Misconfiguration Reviews Help
- Demonstrates proactive compliance with CIS Benchmarks, PCI DSS, HIPAA, ISO 27001, DPDPA, and in-country norms.
- Generates audit-ready configuration evidence and compliance mapping documentation for regulatory submissions.
- Identifies specific control gaps against each applicable regulatory requirement before external audit exposure.
- Builds regulator and stakeholder confidence through structured, evidence-based database security governance.
Threat/Challenge:
Database environments with excessive permissions create conditions where authorized users can access, copy, or modify data far beyond their operational need. Malicious insiders, compromised internal accounts, and negligent users with over-privileged database access represent a persistent and high-impact threat to data integrity and confidentiality. Unlike external attackers, insiders operate within existing authentication controls and may evade detection for extended periods.
Insider database misuse is particularly damaging because it exploits legitimate access granted through operational trust. Without least-privilege enforcement, segregation of duty controls, and comprehensive audit logging, organizations cannot prevent or detect insider data exfiltration, unauthorized modification, or deliberate data destruction. The impact extends to regulatory liability, litigation exposure, and permanent loss of customer trust.
How Database Misconfiguration Reviews Help
- Identifies over-permissioned accounts and segregation of duty violations enabling insider exploitation.
- Validates audit logging coverage to support detection and investigation of insider misuse.
- Tests privilege escalation pathways that could allow insiders to expand unauthorized access.
- Provides access governance recommendations to enforce accountability and limit insider threat exposure.
BLOGS & ARTICLES
Our blogs and industry articles provide actionable insights, helping enterprises navigate
cybersecurity challenges, regulatory shifts, and emerging technology trends
IT / ITES / SaaS / Telecom
Multi-Tenant Database Isolation Failures: How SaaS Privilege Misconfigurations Expose Every Customer
Read FurtherBanking & Financial Services / FinTech / Insurance
FinTech's Hidden Risk: How Over-Permissioned Service Accounts Expose Transaction Databases
Read FurtherE-Commerce & Retail
E-Commerce Database Exposure: How Excessive Permissions Enable Customer Data Theft at Scale
Read FurtherHealthcare & HealthTech
Patient Data at Risk: Why Default Credentials in EHR Databases Are Healthcare's Most Dangerous Secret
Read FurtherFREQUENTLY ASKED QUESTION
Asking the right questions is the first step toward security; our FAQs deliver clear,
concise, and practical guidance for clients
CODEC NETWORKS OTHER RELATED SERVICES
Codec Networks doesn’t just test your databases — we uncover how data can be exposed, misused, or exfiltrated
across traditional, cloud, big data, and decentralized environments before attackers ever reach it
-
Data Exfiltration Simulation mimics unauthorized data extraction techniques to assess an organization’s ability to detect, prevent, and respond to data
-
Data Encryption Testing evaluates encryption methods used for data at rest and in transit to ensure confidentiality, integrity, and compliance with security
-
Big Data Security Testing examines large-scale data systems for vulnerabilities in storage, processing, access controls, and data leakage risks across distributed
-
Database Audit Logging & Monitoring Tests verify the effectiveness of logging mechanisms to track access, detect anomalies, and ensure compliance with
-
Web Application Penetration Testing is the process of identifying, exploiting, and reporting security vulnerabilities in web apps to prevent real-world attacks.
Data Exfiltration Simulation mimics unauthorized data extraction techniques to assess an organization’s ability to detect, prevent, and respond to data
Data Encryption Testing evaluates encryption methods used for data at rest and in transit to ensure confidentiality, integrity, and compliance with security
Big Data Security Testing examines large-scale data systems for vulnerabilities in storage, processing, access controls, and data leakage risks across distributed
Database Audit Logging & Monitoring Tests verify the effectiveness of logging mechanisms to track access, detect anomalies, and ensure compliance with
Web Application Penetration Testing is the process of identifying, exploiting, and reporting security vulnerabilities in web apps to prevent real-world attacks.