

On this page
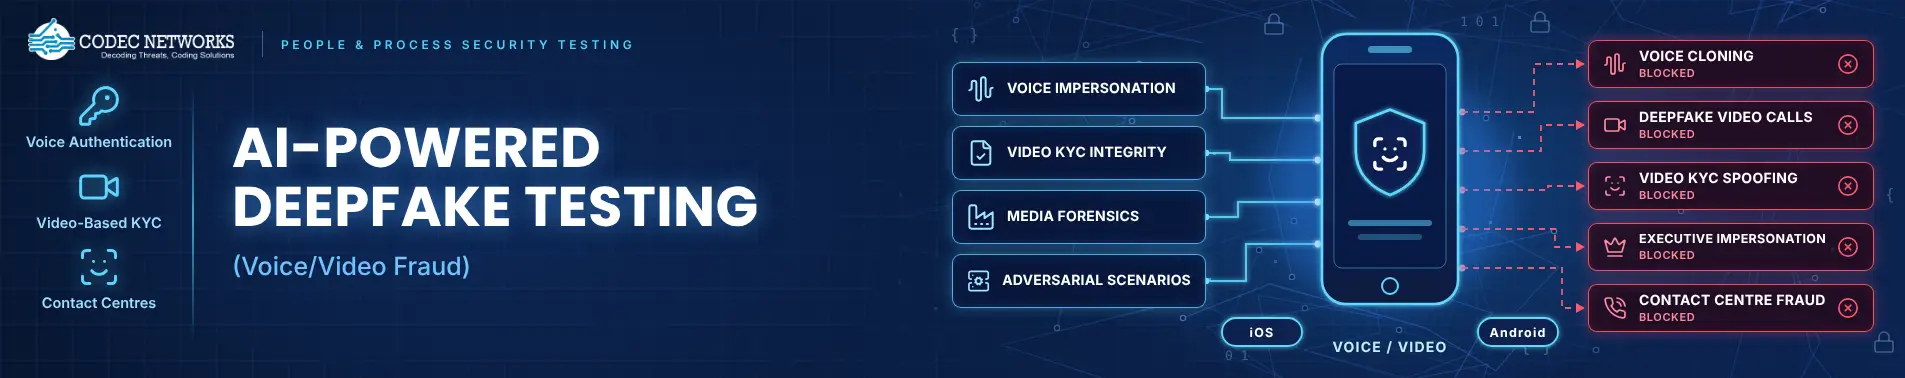
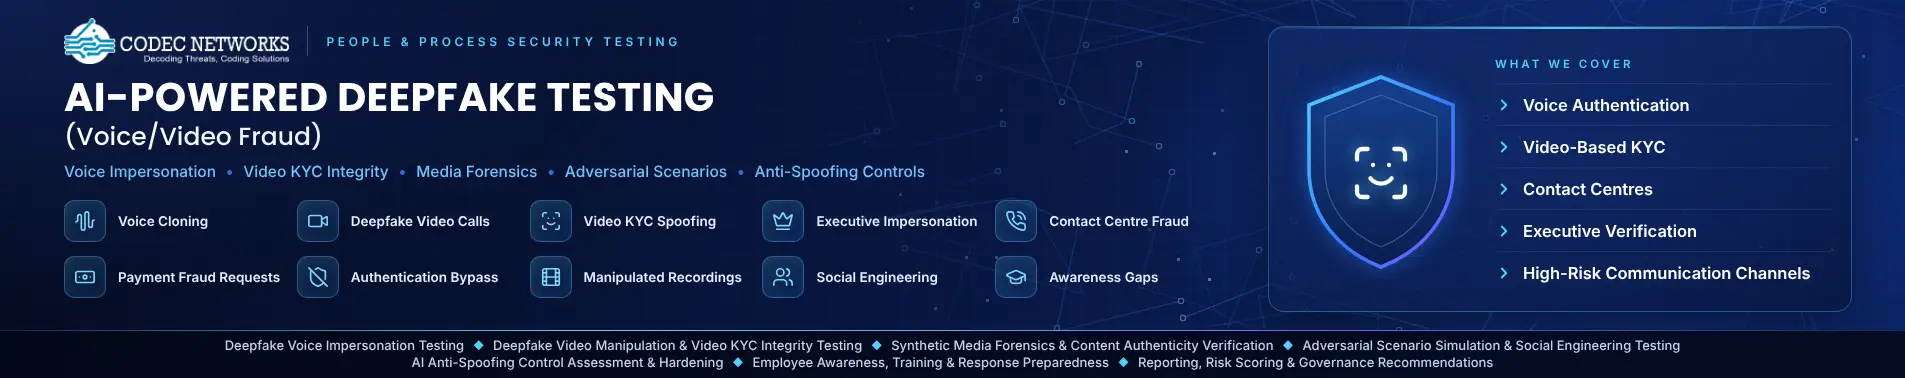

AI-Powered Deepfake Testing (Voice/Video Fraud)
Codec Networks’ AI-Powered Deepfake Testing service helps organizations identify, assess, and mitigate the growing risks of synthetic media manipulation across voice and video channels. Using advanced machine-learning analyzers, forensic signal comparison, and behavioural anomaly detection, our experts simulate real-world deepfake attack scenarios to evaluate how susceptible your systems, workflows, and users are to impersonation-based fraud.
The service conducts controlled deepfake generation and adversarial testing to uncover gaps in authentication processes, contact-center validation, executive verification procedures, and high-risk communication channels. Our assessment identifies whether attackers can spoof leadership voices, tamper with video-based KYC processes, or manipulate recorded media to trigger unauthorized actions.
Post-assessment, Codec Networks delivers a detailed risk report, along with practical mitigation guidance such as multi-factor validation enhancements, anti-spoofing integration recommendations, employee awareness modules, and governance controls for synthetic media threats. This ensures your organization is resilient against voice/video fraud attempts and aligned with emerging global security best practices.
Industry Significance
AI-Powered Deepfake Testing helps organizations detect and assess synthetic voice and video manipulation risks across critical communication channels. The service strengthens fraud prevention, validates identity-verification controls, and protects businesses from rapidly evolving impersonation attacks in today’s AI-driven threat landscape.
Read More
Service Relevance
AI-Powered Deepfake Testing evaluates an organization’s exposure to synthetic voice and video manipulation, identifying weaknesses in identity verification and communication workflows. The service enhances technical resilience, strengthens fraud defenses, and ensures business operations remain secure against rapidly evolving AI-driven impersonation threats.
Read More
Benefits to Customers
AI-Powered Deepfake Testing enables customers to strengthen security, enhance identity verification efficiency, and maintain trust across digital interactions. The service helps organizations meet compliance expectations, prevent impersonation fraud, and confidently innovate in an environment increasingly challenged by AI-generated voice and video threats.
Read More
AI-Powered Deepfake Testing (Voice/Video Fraud)
SERVICE FEATURES AND DELIVERY FRAMEWORK
Codec Networks’ delivery methodology integrates controlled adversarial testing, forensic evaluation, and actionable reporting
to uncover vulnerabilities in real-world communication scenarios.
Service Feature
AI-Powered Deepfake Testing evaluates an organization’s exposure to synthetic voice and video manipulation, identifying weaknesses in identity verification and communication workflows. The service enhances technical resilience, strengthens fraud defenses, and ensures business operations remain secure against rapidly evolving AI-driven impersonation threats.
Codec Networks offers these services across following segments:
1. Deepfake Voice Impersonation Testing
This sub-service evaluates an organization’s vulnerability to AI-generated voice spoofing used in fraud, social engineering, or unauthorized approvals.
Key Features
- Synthetic Voice Generation Simulation: Creates controlled, realistic voice deepfakes mimicking executives, customers, or employees to assess fraud exposure.
- Voice Authentication Bypass Testing: Examines how easily automated IVR, call-center systems, or voice biometrics can be fooled.
- Signal & Acoustic Forensics: Uses spectral analysis to detect compression artifacts, pitch anomalies, and synthesis markers in manipulated audio.
- Vishing Attack Simulation: Tests employee response to cloned-voice scam calls, focusing on procedural adherence and escalation behaviors.
- Executive Impersonation Threat Mapping: Identifies high-risk roles and communication channels susceptible to synthetic voice exploitation.
2. Deepfake Video Manipulation & Video KYC Integrity Testing
This sub-service assesses whether AI-generated or altered video can bypass verification processes or compromise trust in digital interactions.
Key Features
- Video KYC Spoofing Simulation: Tests if manipulated faces, lip-sync deepfakes, or replay attacks can pass automated or manual video verification.
- Facial Consistency & Temporal Analysis: Detects frame-level distortions, unnatural blinking patterns, facial warping, and lighting inconsistencies.
- Liveness Validation Stress Tests: Challenges the robustness of facial recognition and liveness checks against synthetic media.
- Tampered Media Detection: Identifies edits, overlays, and AI regeneration in submitted video evidence or identity documents.
- Remote Onboarding Threat Evaluation: Analyzes vulnerabilities in HR onboarding, customer onboarding, or video interviews.
3. Synthetic Media Forensics & Content Authenticity Verification
This sub-service provides detailed media forensic analysis to differentiate real audio/video content from AI-generated or manipulated versions.
Key Features
- Advanced ML-Based Detection Models: Uses neural classifiers to distinguish deepfakes from legitimate recordings based on latent media patterns.
- Metadata & Hash Integrity Validation: Verifies timestamps, encoding signatures, camera source data, and digital fingerprints.
- Cross-Channel Correlation Checks: Compares voice, video, transcripts, and contextual metadata to detect inconsistencies.
- Chain-of-Custody Assessment: Ensures recorded media used for investigations or compliance retains evidentiary value.
- Authenticity Scoring & Risk Indexing: Assigns risk ratings based on manipulation likelihood and operational impact.
4. Adversarial Scenario Simulation & Social Engineering Testing
This sub-service replicates real-world deepfake-enabled attacks to evaluate human, procedural, and technical response mechanisms.
Key Features
- Executive Fraud Simulation (CEO Fraud): Emulates high-pressure scenarios where attackers use synthetic voices/videos to authorize fund transfers.
- Multi-Vector Social Engineering: Combines emails, phone calls, and video messages to test layered deception techniques.
- Operational Workflow Stress Testing: Assesses resilience of approval chains, escalation policies, and transaction validation steps.
- Behavioral Response Analysis: Measures employee decision-making, verification habits, and compliance with internal protocols.
- Incident Response Validation: Tests how quickly teams identify manipulation and initiate containment procedures.
5. AI Anti-Spoofing Control Assessment & Hardening
This sub-service evaluates existing security systems and provides recommendations to strengthen defenses against AI-generated spoofing.
Key Features
- Voice & Video Verification Control Review: Analyzes biometric systems, KYC workflows, authentication tools, and communication protocols.
- Technical Gap Identification: Highlights weaknesses in liveness checks, anti-spoof algorithms, multi-factor processes, and user training.
- Integration Readiness Assessment: Evaluates compatibility with advanced anti-deepfake solutions, risk scoring engines, and trust frameworks.
- Hardening Recommendations: Provides technology, policy, and process enhancements for fraud-proof communication channels.
- Compliance Alignment: Ensures controls align with global digital identity and media integrity expectations.
6. Employee Awareness, Training & Response Preparedness
This sub-service equips staff to recognize and respond effectively to deepfake-based deception attempts.
Key Features
- Role-Based Training Modules: Executive, finance, operations, support, and customer-facing teams receive customized training content.
- Recognition Skills Development: Practical examples and real deepfake samples improve employees' ability to detect subtle cues.
- Simulated Learning Exercises: Hands-on tests measure alertness to voice/video manipulation.
- Response Playbooks: Provides actionable steps for verification, escalation, and containment when deepfakes are suspected.
- Awareness Campaign Kits: Posters, digital guides, and communication templates reinforce ongoing vigilance.
7. Reporting, Risk Scoring & Governance Recommendations
This sub-service provides structured insights, measurable outputs, and strategic mitigation guidance.
Key Features
- Detailed Risk Reports: Includes findings, attack paths, control weaknesses, and forensic observations.
- Exposure Scoring Framework: Quantifies susceptibility across people, processes, and technology.
- Maturity Benchmarking: Compares organizational resilience against industry standards and threat trends.
- Remediation Roadmap: Provides prioritized recommendations with timelines, ownership, and required controls.
- Governance & Policy Guidance: Supports creation or enhancement of media integrity, identity-verification, and fraud-prevention policies.
Codec Networks follows a structured, phased, and intelligence-driven methodology to deliver AI-Powered Deepfake Testing services. The methodology ensures thorough assessment, realistic adversarial simulation, accurate detection insights, and actionable remediation tailored to organizational risk profiles. Each phase integrates technical analysis, forensic validation, and stakeholder engagement to deliver high-quality, measurable outcomes.
1. Requirement Understanding & Engagement Initiation
Activities
- Conduct stakeholder discussions to define objectives, communication channels in scope, and high-risk roles or processes (e.g., financial approvals, video KYC, executive interactions).
- Identify existing controls—voice biometrics, video liveness checks, call-center procedures, onboarding workflows, and identity verification systems.
- Finalize technical environment access, data handling requirements, compliance constraints, and confidentiality considerations.
Outcome
A customized engagement plan aligned with organizational goals, threat landscape, and operational maturity.
2. Architecture Review & Control Mapping
Activities
- Map communication systems, authentication tools, video verification processes, and platform dependencies.
- Review anti-spoofing mechanisms, identity validation frameworks, escalation policies, and human verification steps.
- Identify potential attack surfaces exposed to deepfake voice or video exploitation.
Outcome
A complete control blueprint highlighting areas that require in-depth testing and adversarial simulation.
3. Synthetic Media Threat Modeling
Activities
- Conduct threat modeling to identify plausible exploitation scenarios—CEO fraud, vishing, manipulated video KYC, tampered onboarding, remote interviews, etc.
- Classify threat actors, techniques, and deepfake generation capabilities relevant to the organization.
- Define adversarial use cases tailored to business operations.
Outcome
A structured threat model defining risks, probable attack paths, and test scenarios.
4. Deepfake Attack Simulation & Test Case Design
Activities
- Develop test cases for voice spoofing, video manipulation, KYC bypass, approval-chain exploitation, and communication interference.
- Prepare synthetic voice samples, video alterations, lip-sync deepfakes, or model-generated impersonations based on defined use cases.
- Ensure all simulations meet ethical, legal, and confidentiality guidelines.
Outcome
A comprehensive set of controlled adversarial scenarios.
5. Execution of Deepfake Testing (Voice & Video)
Activities
- Perform voice spoofing attempts against IVR systems, contact centers, voice authentication tools, and operational workflows.
- Conduct video deepfake submission tests, including liveness bypass attempts, manipulated KYC submissions, and tampered recordings.
- Execute multi-vector social engineering simulations combining voice/video deception, emails, and contextual manipulation.
- Capture system responses, human reactions, detection failures, and workflow deviations.
Outcome
Real-world assessment data on vulnerabilities, process weaknesses, and control gaps.
6. Forensic Analysis & Detection Evaluation
Activities
- Apply machine-learning detection engines, acoustic forensics, temporal video analysis, metadata validation, and anomaly scoring.
- Compare real vs. synthetic samples to assess system capability to detect manipulation.
- Evaluate the accuracy and robustness of identity verification systems and human operators.
Outcome
Objective detection metrics, false-positive/false-negative observations, and forensic insights on media authenticity.
7. Control Effectiveness Assessment & Gap Identification
Activities
- Assess the performance of voice biometrics, liveness checks, and manual verification practices.
- Validate escalation procedures against simulated deepfake attacks.
- Identify deficiencies across people, processes, and technology.
Outcome
A clear picture of organizational readiness and control effectiveness.
8. Risk Scoring, Impact Analysis & Benchmarking
Activities
- Assign quantitative risk scores using maturity models and exposure frameworks.
- Evaluate potential financial, operational, reputational, and compliance impacts.
- Benchmark results against industry trends, best practices, and global digital trust standards.
Outcome
A measurable risk posture that highlights priority improvement areas.
9. Remediation Guidance & Hardening Recommendations
Activities
- Provide detailed recommendations for enhancing voice/video authentication, workflow security, anti-spoofing controls, and governance.
- Suggest technology integrations, multi-factor enhancements, and policy updates for communication integrity.
- Deliver tactical and strategic roadmaps with timelines and ownership.
Outcome
A concrete, actionable plan to strengthen enterprise resilience against deepfake threats.
10. Reporting, Presentation & Advisory Consultation
Activities
- Deliver comprehensive reports containing findings, evidence, exploit paths, control gaps, and risk scores.
- Conduct executive presentations to explain vulnerabilities, business impacts, and remediation priorities.
- Provide advisory support for tool selection, process redesign, and long-term governance.
Outcome
Stakeholder clarity and alignment on next steps to improve synthetic media defenses.
11. Post-Engagement Support & Continuous Improvement
Activities
- Offer periodic review sessions, follow-up assessments, and capability enhancement workshops.
- Monitor emerging deepfake techniques and update clients on evolving threats and preventive strategies.
- Support re-validation exercises to confirm remediation effectiveness.
Outcome
Sustained security maturity and adaptability to evolving AI-driven attack methods.
|
International Standard |
Focus Area |
Relevance to Service Delivery |
|
ISO/IEC 27001 |
Information Security Management |
Ensures secure handling of audio/video data, assessment artifacts, and forensic evidence throughout the engagement. |
|
ISO/IEC 27701 |
Privacy Information Management |
Supports responsible collection, processing, and protection of identity-related media used during testing activities. |
|
ISO/IEC 30107 (Biometric Presentation Attack Detection) |
Anti-Spoofing & Liveness Detection |
Guides evaluation of voice/video authentication systems against deepfake spoofing and presentation attacks. |
|
ISO/IEC 38500 |
IT Governance |
Ensures structured governance, accountability, and oversight for synthetic media risk assessments. |
|
ISO/IEC 27037 |
Digital Evidence Handling |
Provides methods for collecting, analyzing, and preserving media samples used for forensic validation. |
|
ISO/IEC 27041 |
Incident Investigation & Readiness |
Supports methodology for testing organizational readiness to detect and respond to deepfake-based incidents. |
|
NIST AI Risk Management Framework (AI RMF) |
AI Risk, Integrity & Trustworthiness |
Guides evaluation of AI-generated manipulation risks and promotes trustworthy assessment practices. |
|
NIST SP 800-63 (Digital Identity Guidelines) |
Identity Assurance & Authentication |
Helps assess resilience of remote identity verification, video KYC, and biometric authentication systems. |
Please Note –
- Service delivery aligns with recognized international standards but does not guarantee full compliance of client systems or processes.
- Assessments focus on evaluating controls against referenced standards and exclude certification, accreditation, or regulatory approvals.
- Recommendations are advisory and do not imply liability for audit outcomes, regulatory interpretations, or compliance failures.
- Client remains responsible for adopting controls, maintaining compliance, and validating implementation against relevant standards.
- Codec Networks is not liable for security incidents, fraud, or breaches occurring before, during, or after the assessment.
- Engagement scope covers assessment-only activities and excludes operational execution, system configuration, or ongoing compliance management.
- Total liability for all services is strictly limited to the international standards as far as possible as agreed in contracted engagement value. Codec Networks expressly excludes any indirect, financial, operational, incidental, punitive, or consequential damages, which may arise due to any coincidental events, or changes in international standards guidelines time to time.
Service Feature
AI-Powered Deepfake Testing evaluates an organization’s exposure to synthetic voice and video manipulation, identifying weaknesses in identity verification and communication workflows. The service enhances technical resilience, strengthens fraud defenses, and ensures business operations remain secure against rapidly evolving AI-driven impersonation threats.
Codec Networks offers these services across following segments:
1. Deepfake Voice Impersonation Testing
This sub-service evaluates an organization’s vulnerability to AI-generated voice spoofing used in fraud, social engineering, or unauthorized approvals.
Key Features
- Synthetic Voice Generation Simulation: Creates controlled, realistic voice deepfakes mimicking executives, customers, or employees to assess fraud exposure.
- Voice Authentication Bypass Testing: Examines how easily automated IVR, call-center systems, or voice biometrics can be fooled.
- Signal & Acoustic Forensics: Uses spectral analysis to detect compression artifacts, pitch anomalies, and synthesis markers in manipulated audio.
- Vishing Attack Simulation: Tests employee response to cloned-voice scam calls, focusing on procedural adherence and escalation behaviors.
- Executive Impersonation Threat Mapping: Identifies high-risk roles and communication channels susceptible to synthetic voice exploitation.
2. Deepfake Video Manipulation & Video KYC Integrity Testing
This sub-service assesses whether AI-generated or altered video can bypass verification processes or compromise trust in digital interactions.
Key Features
- Video KYC Spoofing Simulation: Tests if manipulated faces, lip-sync deepfakes, or replay attacks can pass automated or manual video verification.
- Facial Consistency & Temporal Analysis: Detects frame-level distortions, unnatural blinking patterns, facial warping, and lighting inconsistencies.
- Liveness Validation Stress Tests: Challenges the robustness of facial recognition and liveness checks against synthetic media.
- Tampered Media Detection: Identifies edits, overlays, and AI regeneration in submitted video evidence or identity documents.
- Remote Onboarding Threat Evaluation: Analyzes vulnerabilities in HR onboarding, customer onboarding, or video interviews.
3. Synthetic Media Forensics & Content Authenticity Verification
This sub-service provides detailed media forensic analysis to differentiate real audio/video content from AI-generated or manipulated versions.
Key Features
- Advanced ML-Based Detection Models: Uses neural classifiers to distinguish deepfakes from legitimate recordings based on latent media patterns.
- Metadata & Hash Integrity Validation: Verifies timestamps, encoding signatures, camera source data, and digital fingerprints.
- Cross-Channel Correlation Checks: Compares voice, video, transcripts, and contextual metadata to detect inconsistencies.
- Chain-of-Custody Assessment: Ensures recorded media used for investigations or compliance retains evidentiary value.
- Authenticity Scoring & Risk Indexing: Assigns risk ratings based on manipulation likelihood and operational impact.
4. Adversarial Scenario Simulation & Social Engineering Testing
This sub-service replicates real-world deepfake-enabled attacks to evaluate human, procedural, and technical response mechanisms.
Key Features
- Executive Fraud Simulation (CEO Fraud): Emulates high-pressure scenarios where attackers use synthetic voices/videos to authorize fund transfers.
- Multi-Vector Social Engineering: Combines emails, phone calls, and video messages to test layered deception techniques.
- Operational Workflow Stress Testing: Assesses resilience of approval chains, escalation policies, and transaction validation steps.
- Behavioral Response Analysis: Measures employee decision-making, verification habits, and compliance with internal protocols.
- Incident Response Validation: Tests how quickly teams identify manipulation and initiate containment procedures.
5. AI Anti-Spoofing Control Assessment & Hardening
This sub-service evaluates existing security systems and provides recommendations to strengthen defenses against AI-generated spoofing.
Key Features
- Voice & Video Verification Control Review: Analyzes biometric systems, KYC workflows, authentication tools, and communication protocols.
- Technical Gap Identification: Highlights weaknesses in liveness checks, anti-spoof algorithms, multi-factor processes, and user training.
- Integration Readiness Assessment: Evaluates compatibility with advanced anti-deepfake solutions, risk scoring engines, and trust frameworks.
- Hardening Recommendations: Provides technology, policy, and process enhancements for fraud-proof communication channels.
- Compliance Alignment: Ensures controls align with global digital identity and media integrity expectations.
6. Employee Awareness, Training & Response Preparedness
This sub-service equips staff to recognize and respond effectively to deepfake-based deception attempts.
Key Features
- Role-Based Training Modules: Executive, finance, operations, support, and customer-facing teams receive customized training content.
- Recognition Skills Development: Practical examples and real deepfake samples improve employees' ability to detect subtle cues.
- Simulated Learning Exercises: Hands-on tests measure alertness to voice/video manipulation.
- Response Playbooks: Provides actionable steps for verification, escalation, and containment when deepfakes are suspected.
- Awareness Campaign Kits: Posters, digital guides, and communication templates reinforce ongoing vigilance.
7. Reporting, Risk Scoring & Governance Recommendations
This sub-service provides structured insights, measurable outputs, and strategic mitigation guidance.
Key Features
- Detailed Risk Reports: Includes findings, attack paths, control weaknesses, and forensic observations.
- Exposure Scoring Framework: Quantifies susceptibility across people, processes, and technology.
- Maturity Benchmarking: Compares organizational resilience against industry standards and threat trends.
- Remediation Roadmap: Provides prioritized recommendations with timelines, ownership, and required controls.
- Governance & Policy Guidance: Supports creation or enhancement of media integrity, identity-verification, and fraud-prevention policies.
AI-POWERED DEEPFAKE TESTING (VOICE/VIDEO FRAUD) - CODEC NETWORK’S INDUSTRY OFFERINGS
Unified service bundles delivering advanced AI threat simulations, authentication resilience checks, and communication
integrity assessments across enterprise environments.
Foundation Deepfake Risk Screening
Target Clients:
Small and growing businesses seeking affordable, entry-level protection against emerging deepfake threats without extensive security infrastructure investment.
Sub-Services in Scope:
- Voice Deepfake Exposure Scan
- Video KYC Integrity Check
- Awareness & Alertness Training
Objective:
To provide foundational visibility into deepfake-related risks, enabling early detection and strengthening basic communication and identity verification security.
Value Delivered:
Delivers quick insights, improves employee vigilance, and strengthens baseline protection against impersonation attempts across commonly exploited communication channels.
Enhanced Deepfake Resilience Suite
Target Clients:
Mid-sized enterprises managing moderate digital operations and requiring robust fraud-prevention capabilities across customer-facing and internal communication channels.
Sub-Services in Scope:
- Advanced Voice Spoof Simulation
- Video Manipulation & Workflow Testing
- Synthetic Media Forensic Screening
- Process & Control Gap Analysis
Objective:
To strengthen operational resilience by evaluating technical, procedural, and human vulnerabilities through realistic adversarial testing and forensic assessments.
Value Delivered:
Enhances fraud resistance, improves workflow credibility, and supports risk-based decision-making for enterprises scaling their digital verification ecosystems.
Comprehensive Deepfake Defense & Trust Assurance Program
Target Clients:
Large enterprises and global organizations requiring advanced, holistic deepfake defense integrated across governance, operations, identity systems, and communication channels.
Sub-Services in Scope:
- Full-Spectrum Deepfake Attack Simulation
- AI Anti-Spoofing Control Audit
- Digital Identity Trust Framework Assessment
- Governance, Policy & Hardening Roadmap
- Executive & High-Risk Role Protection Module
Objective:
To deliver enterprise-wide assurance against sophisticated AI-driven fraud by reinforcing governance, workflows, and digital trust ecosystems.
Value Delivered:
Provides comprehensive protection, measurable risk reduction, and long-term resilience against evolving deepfake threats affecting critical enterprise communication and decision pathways.
Foundation Deepfake Risk Screening
Target Clients:
Small and growing businesses seeking affordable, entry-level protection against emerging deepfake threats without extensive security infrastructure investment.
Sub-Services in Scope:
- Voice Deepfake Exposure Scan
- Video KYC Integrity Check
- Awareness & Alertness Training
Objective:
To provide foundational visibility into deepfake-related risks, enabling early detection and strengthening basic communication and identity verification security.
Value Delivered:
Delivers quick insights, improves employee vigilance, and strengthens baseline protection against impersonation attempts across commonly exploited communication channels.
Enhanced Deepfake Resilience Suite
Target Clients:
Mid-sized enterprises managing moderate digital operations and requiring robust fraud-prevention capabilities across customer-facing and internal communication channels.
Sub-Services in Scope:
- Advanced Voice Spoof Simulation
- Video Manipulation & Workflow Testing
- Synthetic Media Forensic Screening
- Process & Control Gap Analysis
Objective:
To strengthen operational resilience by evaluating technical, procedural, and human vulnerabilities through realistic adversarial testing and forensic assessments.
Value Delivered:
Enhances fraud resistance, improves workflow credibility, and supports risk-based decision-making for enterprises scaling their digital verification ecosystems.
Comprehensive Deepfake Defense & Trust Assurance Program
Target Clients:
Large enterprises and global organizations requiring advanced, holistic deepfake defense integrated across governance, operations, identity systems, and communication channels.
Sub-Services in Scope:
- Full-Spectrum Deepfake Attack Simulation
- AI Anti-Spoofing Control Audit
- Digital Identity Trust Framework Assessment
- Governance, Policy & Hardening Roadmap
- Executive & High-Risk Role Protection Module
Objective:
To deliver enterprise-wide assurance against sophisticated AI-driven fraud by reinforcing governance, workflows, and digital trust ecosystems.
Value Delivered:
Provides comprehensive protection, measurable risk reduction, and long-term resilience against evolving deepfake threats affecting critical enterprise communication and decision pathways.
CODEC NETWORKS VALUE PROPOSITION
Enhancing digital trust by identifying deepfake vulnerabilities and enabling robust protection for
high-risk roles, workflows, and authentication systems.
Codec Networks brings deep technical expertise, specialized cyber defense capabilities, and a structured delivery methodology to help organizations mitigate the fast-growing risks of AI-generated voice and video manipulation. The company’s experience in cybersecurity, digital identity assurance, and adversarial simulations positions it as a trusted partner for enterprises seeking to strengthen fraud prevention, communication integrity, and operational resilience. At Codec Networks’ we ensure that:
1. Strong Delivery Approach Anchored in Methodology and Precision
- Robust assessment frameworks combining threat modeling, adversarial simulations, and forensic validation to deliver comprehensive deepfake risk insights.
- Phased delivery methodology ensuring structured execution—from scoping and testing to reporting and strategic remediation planning.
- Data-driven decisioning using quantifiable metrics, risk scoring models, and maturity benchmarks to inform executive-level strategies.
- Client-aligned customization adapting test scenarios, workflows, and verification processes to match industry, operational, and regulatory contexts.
2. High Technical Competency in Deepfake Analysis and AI-driven Threat Detection
- Expertise in AI, machine learning, and audio-video manipulation detection, enabling precise identification of synthetic media threats.
- Advanced forensic capabilities to analyze metadata, acoustic fingerprints, facial anomalies, temporal distortions, and manipulation artifacts.
- Experience with biometric systems including voice authentication, facial recognition, liveness detection, and KYC integrity architectures.
- Ability to simulate real-world deepfake attacks involving executive impersonation, workflow manipulation, or cross-channel deception.
3. Skilled Cybersecurity Professionals with Specialized Capabilities
- Certified cybersecurity experts trained in adversarial testing, digital forensics, incident response, and identity security.
- Hands-on exposure to evolving AI-enabled threats, ensuring testing aligns with global attack trends and adversarial tactics.
- Cross-functional teams combining penetration testers, threat analysts, biometric specialists, and governance consultants for end-to-end coverage.
- Operational understanding of high-risk business processes, enabling realistic evaluation of approval chains, onboarding flows, and customer interactions.
4. End-to-End Value Across People, Process, Technology & Governance
- Strategic insights helping organizations enhance governance frameworks, identity assurance models, and communication integrity controls.
- Process resilience improvements that reinforce verification steps, escalation paths, and policy adherence during high-risk interactions.
- Workforce readiness uplift through awareness training, simulation-based learning, and response playbook development.
- Technology optimization support helping clients strengthen anti-spoofing systems, biometric controls, and AI detection mechanisms.
5. Industry-Relevant Expertise for India and Global Markets
- Understanding of sector-specific needs across BFSI, telecom, healthcare, government, critical infrastructure, and digital-first enterprises.
- Alignment with international standards ensuring assessments follow recognized security, privacy, and digital identity frameworks.
- Scalable service models offering Basic, Medium, and Advanced packages tailored to small, medium, and global enterprises.
- Experience in multicultural communication ecosystems enabling region-specific deepfake testing and fraud-prevention strategies.
6. Business Value Delivered to Clients
- Improved fraud prevention capability through identification of system and process gaps vulnerable to synthetic media exploitation.
- Enhanced trust and credibility across digital channels, customer interactions, and executive communications.
- Reduced operational and financial risks stemming from impersonation attacks, tampered KYC, and manipulated workflows.
- Long-term resilience as organizations adopt proactive defense strategies aligned with evolving AI-driven threat landscapes.
Founded in 2008 with 17+ Years of Industry Experience in Information and Cyber Security domain
Codec Networks Full-Spectrum Cybersecurity Expertise across all Industry Domains:
- Security Vulnerability Assessment & Penetration Testing (VAPT): Covering Web, Mobile, API, IoT, Blockchain, Cloud-Native, and smart infrastructure environments, with a focus on OWASP, MITRE ATT&CK, and real-world exploit simulation.
- Offensive Security & Deep Level Security Assessments: Advanced Red Team, Blue Team and Purple Team Exercises, Threat Simulations, Social Engineering Campaigns, and Secure Code Review.
- IT Security Audit & Compliance Services: Implementation and audit support for ISO/IEC 27001, ISO 27701, NIST CSF, RBI-CSF, SEBI, IRDAI, PCI DSS, HIPAA, SOC 2, GDPR, and India’s DPDPA 2023.
- Data Privacy & Strategic Risk Advisory: ISO 27701, GDPR, DPDPA, Cross-border compliance, DPIA, DPO-as-a-service, supply chain risk management, and digital transformation risk consulting.
- Emerging Technology Security (Web3.0 | AI | Blockchain): Specialized testing for smart contracts, DeFi platforms, Metaverse applications, AI/ML models, quantum readiness, and blockchain nodes.
- Managed SOC & Threat Monitoring Services: End-to-end SOC operations, SIEM/EDR/XDR/SOAR integration, threat intelligence, cloud security monitoring, and 24/7 incident response.
- Cyber Forensics & Threat Analysis: Investigation services including Device forensics, Malware Analysis, Cloud and Mobile forensics, insider threat detection, and Forensic support.
- Board-Level Cybersecurity Advisory Services to build governance, quantify risks, and align with enterprise-wide digital priorities : Codec Networks enables this transformation by offering Integrated Cyber Risk Management, GRC Program Advisory, Reputation Management, Crisis Communication Readiness, and CISO Support, tailored for CXOs and board members seeking to integrate cybersecurity into strategic decision-making.
- Cyber Security Education & Global Certifications - Through the Codec Centre for Professional Excellence, we deliver Post Graduate Certification in Advanced Cybersecurity (PGCAC), Graduate Certification in Advanced Cybersecurity (GCAC), Accredited Trainings & Certifications from EC Council, PECB, TUV, Quality Austria, ISACA and ISC2 - building the next generation of cybersecurity leaders.
- CERT-IN empaneled Information Security Auditing Organization
- NICSI empaneled for providing Application Audit and Compliance Services under Start-Up Category


- An ISO/IEC 27001:2022 certified company, has established Information Security Management System (ISMS), demonstrating a structured approach to manage and protect sensitive information from cyber threats.
- An ISO 9001 certified company, has established and maintains a certified Quality Management System (QMS) that meets international standards for quality and consistency
At Codec Networks, our foundation is built on deep technical mastery, certified expertise, and an unrelenting pursuit of cyber excellence. With a team of globally accredited professionals, advanced methodologies, and next-generation tools, we deliver measurable security outcomes across assessment, compliance, monitoring, and forensic domains.
Our competency-driven approach ensures every engagement is governed by precision, accountability, and alignment with international standards — empowering enterprises to stay secure, compliant, and resilient.
Governance, Risk & Compliance (GRC) Competency
Codec Networks’ dedicated Governance, Risk & Compliance (GRC) group specializes in security assessments, risk management, regulatory compliance, and audit readiness. The team partners with organizations to strengthen governance frameworks and ensure end-to-end compliance in a complex regulatory landscape.
Key Attributes:
- Team of certified auditors and consultants with credentials including ISO 27001 LA/LI, ISO 31000 Risk Specialist, ISO 27701 PIMS, GDPR, SOC 2, HIPAA, CCPA, DPO, CISA, CISM, CRISC, CISSP and other advanced industry certifications.
- Expertise in enterprise risk quantification, privacy impact assessment (PIA/DPIA), audit automation, and supply chain risk mapping.
- Proven track record in implementing ISO-based ISMS/PIMS frameworks, RBI/SEBI/IRDAI audits, and cross-border data compliance projects.
Vulnerability Assessment & Penetration Testing (VAPT) Expertise
Our VAPT teams bring extensive technical depth across Web, Mobile, API, Cloud, Network, Database, Infrastructure, IoT, and People & Process domains.
Every engagement is mapped to OWASP, NIST, MITRE ATT&CK, ISO 27001, PCI DSS, HIPAA, RBI, and GDPR frameworks — ensuring real-world relevance and compliance alignment.
Core Strengths:
- Certified professionals with CEH, C-PENT, LPT, OSCP, OSWE, OSEE, and CREST credentials, averaging 7–10 years of offensive security experience.
- Proven expertise in Red/Blue/Purple Teaming, DevSecOps, secure SDLC, and threat emulation.
- Continuous skill enhancement through CTFs, hackathons, and product certifications (on case to case basis) such as CCNA, CCNP, Juniper, Fortinet, McAfee, RSA etc
Managed SOC & Threat Intelligence Operations
Codec Networks operates a 24/7 Managed Security Operations Center (SOC) delivering continuous visibility, detection, and response across hybrid environments.
Our SOC integrates SIEM, SOAR, EDR/XDR, and Cloud-Native Analytics to ensure rapid threat detection, incident containment, and business continuity.
Key Capabilities:
- Certified SOC analysts with credentials such as CHFI, CEH, CompTIA CySA+, GCIA, GCFA, and Splunk Certified Architect.
- Integration with platforms like Splunk, QRadar, SentinelOne, CrowdStrike, Elastic, Microsoft Sentinel, and Cortex XSOAR.
- Advanced use cases include cloud posture management, insider threat analytics, MITRE ATT&CK–aligned detections, and threat hunting automation.
- Comprehensive SOC Maturity Assessments and Threat Intelligence Fusion through integration with global feeds and dark web monitoring.
Cyber Forensics & Threat Analysis Expertise
Our Cyber Forensic Division delivers end-to-end investigation, evidence preservation, and digital analysis services — designed to support law enforcement, corporate forensics, and internal response teams.
We combine forensic science with cyber intelligence to identify root causes, trace adversaries, and restore operational integrity.
Core Expertise Areas:
- Device, Network, Cloud, and Mobile Forensics – leveraging latest forensic tools (wherever applicable) such as Autopsy, Cyber Triage, Kape, EnCase, FTK, Magnet AXIOM, and Cellebrite.
- Malware Reverse Engineering and Memory Forensics for incident containment and threat attribution.
- Blockchain & Crypto Forensics – tracing DeFi fraud, NFT manipulation, and crypto laundering activities using Chainalysis, TRM Labs, and Elliptic (wherever applicable).
- Incident Response Support – forensic readiness, eDiscovery, evidence preservation, aligned with ISO/IEC 27037 & 27043.
- Certified experts including CHFI, eCIR, eCDFP, GCFE, GCFA, EnCE, CFCE and ECIH, ensuring investigations meet both technical and legal standards.
Advanced Tools, Frameworks & Continuous Innovation
Codec Networks leverages industry-leading tools and platforms such as Burp Suite Pro, Nessus, Prisma Cloud, Splunk, QRadar, CrowdStrike, SentinelOne, Autopsy, Chainalysis, MythX, and Prowler, (wherever applicable) ensuring accuracy, scalability, and efficiency.
Our methodologies align with globally recognized frameworks including:
- MITRE ATT&CK & D3FEND
- OWASP Top 10 / MASVS / ASVS
- NIST Cybersecurity Framework & SP 800-115
- ISO/IEC 27001, 27701, 31000, 22301
Through ongoing research, Codec Networks continually evolves to address modern threats — from Generative AI prompt attacks and smart contract exploits to IoT zero-days, metaverse impersonation, and quantum-era vulnerabilities.
Compliance-Driven Deliverables
All technical engagements and reports are mapped to major global and Indian compliance frameworks — including ISO 27001, PCI DSS, HIPAA, GDPR, RBI-CSF, SEBI, IRDAI, and DPDPA 2023.
Our structured technical and executive reports support board-level visibility, audit evidence, and certification readiness, ensuring that every engagement drives both technical assurance and regulatory confidence.
Codec Networks – Certified Competence. Proven Expertise. Real-World Cyber Resilience.
Empowering enterprises through advanced security engineering, continuous monitoring, and forensic intelligence.
At Codec Networks, we believe that cybersecurity excellence is not achieved through tools alone — it is built through methodical delivery, risk-based insight, and measurable outcomes.
Our Agile and Modular 8-Stage Delivery Methodology ensures that every engagement — from rapid risk assessments to full-scale ISMS implementations - is structured, standards-aligned, and business-focused.
Agile & Modular Methodology
Our delivery framework integrates global best practices with localized regulatory insight, ensuring each engagement is executed with clarity, accountability, and precision. Clients benefit from seamless onboarding, milestone-driven execution, and transparent reporting throughout the lifecycle.
- Discovery & Scoping: Collaborative workshops to understand business context, IT landscape, compliance obligations, and risk appetite, forming the foundation of a well-defined project scope.
- Risk Profiling & Gap Assessment: Comprehensive evaluation of people, process, and technology controls aligned with ISO 27001, NIST CSF, GDPR, HIPAA, DPDPA 2023, RBI, and PCI DSS.
- Regulatory Mapping & Framework Alignment: Mapping organizational obligations against applicable standards and laws — from ISO & NIST to RBI, SEBI, IRDAI, UIDAI, and DPDPA — including new-age frameworks like ISO 42001 (AI) and FATF for emerging technologies.
- Security Architecture & Control Design: Designing or refining network, cloud, and data security architectures with controls tailored for cloud, AI, OT/ICS, and Web3.0 environments.
- Documentation & Policy Development: Creation and refinement of Policies, SOPs, Risk Registers, DPIAs, Incident Response Plans, and Governance Documents, ensuring audit readiness and legal compliance.
- Implementation & Risk Treatment: Execution of remediation roadmaps, vendor risk management, privacy engineering, and workforce training to mitigate gaps and operationalize security controls.
- Validation, Testing & Audit Readiness: Conducting mock audits, VAPT, forensic readiness, and compliance testing to validate effectiveness and prepare for certifications.
- Governance Reporting & Continual Improvement: Delivering executive dashboards, compliance scorecards, and board-level insights with ongoing advisory through vCISO and DPO-as-a-Service models.
Risk-Based & Business-Oriented Audit Approach
Our methodology goes beyond testing systems — it focuses on how vulnerabilities translate into business, reputational, and compliance risks.
- Deliver Deep Insight: Actionable intelligence into vulnerabilities, attack paths, business impact, and remediation priorities.
- Extend Beyond Tools: Manual and contextual assessments combining automation with human expertise across government, financial, and commercial sectors.
- Actionable Reporting: Executive-friendly reports that translate complex findings into strategic, risk-aware recommendations.
- Efficient Execution: Critical assets prioritized for testing to deliver maximum value within tight engagement windows.
Outcome-Driven Engagements for Security Maturity
Each stage is modular yet interconnected, adaptable to enterprises of any scale or industry. Whether it’s a cloud-native fintech pursuing SOC 2, a healthcare provider ensuring HIPAA alignment, or a bank meeting RBI-CSF requirements, Codec Networks ensures consistency, compliance, and measurable improvement.
Beyond certification checklists, our Post-Audit Support and Continuous Risk Monitoring provide remediation guidance, breach response playbooks, staff training, and ongoing compliance tracking — building sustainable security posture and resilient business continuity.
Codec Networks – Turning Compliance into a Competitive Advantage.
Structured. Measurable. Secure. Always Aligned with Your Business Goals.
At Codec Networks, our clients are not just audit subjects—they are long-term partners in a shared cybersecurity journey. Every engagement is designed around the client’s business priorities, security maturity, and risk appetite, ensuring solutions that are relevant, practical, and results-driven.
With a legacy of 650+ successful engagements across industries such as Banking, Fintech, Healthcare, Telecom, Energy, Aviation, Manufacturing, E-commerce, and Government, Codec Networks has attempted to become a trusted advisor for organizations seeking to transform compliance into resilience.
Our engagement philosophy extends beyond conventional audits. We integrate strategic advisory, technical assurance, remediation support, and continuous compliance monitoring, creating a full lifecycle relationship rather than a one-time service. Clients benefit from:
- Personalized advisory frameworks tailored to their business model and operational scale.
- Collaborative engagement models featuring joint workshops, stakeholder training, and compliance awareness sessions.
- Board-level guidance and reporting that translates complex technical findings into actionable business intelligence.
- Transparent communication channels with dedicated project managers, secure digital workspaces, and real-time status dashboards.
By combining the objectivity of an auditor with the empathy of an advisor, Codec Networks builds trust, accountability, and measurable security growth. Our commitment is simple — to deliver cybersecurity as a continuous partnership, not a periodic project.
Codec Networks – Where Advisory Meets Assurance.
Empowering Clients Through Partnership, Transparency, and Trust.
At Codec Networks, integrity, professionalism, and ethical responsibility form the cornerstone of every engagement. As a trusted strategic partner in cybersecurity, we operate within the highest standards of ethical conduct, legal compliance, and regulatory governance, ensuring our services strengthen both our clients’ defenses and their reputations.
We adhere to a strict ethical code of conduct, driven by transparency, independence, and accountability. Every consultant, auditor, and engineer within Codec Networks upholds the core security triad of Confidentiality, Integrity, and Availability (CIA) — ensuring data protection, operational reliability, and business continuity at all times.
Our professional ethos blends technical excellence with moral responsibility, following structured processes, defined service standards, and adherence to international and national regulatory frameworks.
Our Ethical & Professional Commitments
- Zero-Compromise Consulting: We maintain independence, neutrality, and confidentiality across all audits and advisory engagements.
- Legal & Regulatory Conformance: We assist clients to conform strictly within the boundaries of applicable cyber laws, privacy regulations, and data protection statutes.
- Client-First Philosophy: Every recommendation is designed to safeguard stakeholder interests, minimize legal exposure, and build sustainable resilience.
- Outcome-Driven Security Maturity: Our modular yet integrated delivery approach supports organizations of all sizes in achieving measurable improvements in security posture.
- Global Delivery, Local Integrity: Our Global Network Delivery Model integrates international best practices with local regulatory expertise — ensuring value-driven, compliant outcomes.
Industry-Specific Security Advisory
Recognizing that every sector faces distinct threats and compliance challenges, Codec Networks provides customized, industry-aligned security advisory across BFSI, Fintech, Telecom, Healthcare, Energy, Aviation, E-commerce, Government, and Critical Infrastructure domains.
Our sector-specific consulting translates regulatory complexity into practical, business-aware strategies, ensuring risk mitigation plans are compliant, auditable, and operationally feasible.
Our Commitment
With a zero-tolerance approach to ethical compromise, Codec Networks stands for trust, transparency, and truth in cybersecurity. We are more than consultants — we are custodians of digital integrity, committed to helping organizations navigate risk, maintain compliance, and enable secure business growth.
Codec Networks – Where Integrity Meets Innovation. Trusted. Ethical. Future-Ready.
At Codec Networks, we combine the strength of a global delivery ecosystem with the precision of local regulatory insight to deliver cybersecurity solutions that are both internationally benchmarked and regionally compliant.
Our Global Delivery Capability enables clients across continents to access specialized cybersecurity expertise, advanced technologies, and globally aligned methodologies. Through a distributed network of certified professionals, partner alliances, and intelligence centers, Codec Networks ensures consistent service quality and rapid response across time zones and geographies.
What truly differentiates us is our Local Expertise—a deep understanding of national regulations, industry frameworks, and operational nuances that shape cybersecurity implementation in each region.
Our hybrid delivery model blends remote and on-site collaboration, combining the agility of digital operations with the contextual understanding of local consultants. This ensures culturally aligned communication, faster problem resolution, and seamless coordination with client teams.
With a presence across India, Codec Networks empowers global enterprises to manage cybersecurity uniformly while adapting to local risks, regulations, and realities.
Codec Networks – Global Vision. Local Precision. Consistent Cyber Resilience.
“With Codec Networks, you’re not just buying a service — you’re investing in a cybersecurity ally who understands your business, defends your reputation, and strengthens your future.”
At Codec Networks, we believe cybersecurity is not a project — it’s a partnership.
Our approach is built on trust, transparency, and transformation, helping clients evolve from compliance readiness to cyber resilience.
Your Strategic Security Partner
Codec Networks acts as a strategic security partner, providing continuous roadmap development, architecture reviews, and improvement programs that evolve with your business and the threat landscape.
“We don’t just secure businesses — we empower them to lead with confidence in a digital-first world.”
Our strength lies in the fusion of technical depth, regulatory insight, industry specialization, and future readiness — providing unmatched cybersecurity value to enterprises across India and beyond.
Codec Networks – Certified Competence. Proven Expertise. Real-World Cyber Resilience.
Empowering enterprises through advanced security engineering, continuous monitoring, and forensic intelligence.
Every engagement reflects our belief that advisory must meet assurance — a promise we deliver through partnership, integrity, and measurable impact.
Codec Networks – Where Advisory Meets Assurance.
Empowering Clients Through Partnership, Transparency, and Trust.
And above all —
“Decoding Threats. Coding Solutions.”
That’s the Codec Networks Advantage.
Codec Networks brings deep technical expertise, specialized cyber defense capabilities, and a structured delivery methodology to help organizations mitigate the fast-growing risks of AI-generated voice and video manipulation. The company’s experience in cybersecurity, digital identity assurance, and adversarial simulations positions it as a trusted partner for enterprises seeking to strengthen fraud prevention, communication integrity, and operational resilience. At Codec Networks’ we ensure that:
1. Strong Delivery Approach Anchored in Methodology and Precision
- Robust assessment frameworks combining threat modeling, adversarial simulations, and forensic validation to deliver comprehensive deepfake risk insights.
- Phased delivery methodology ensuring structured execution—from scoping and testing to reporting and strategic remediation planning.
- Data-driven decisioning using quantifiable metrics, risk scoring models, and maturity benchmarks to inform executive-level strategies.
- Client-aligned customization adapting test scenarios, workflows, and verification processes to match industry, operational, and regulatory contexts.
2. High Technical Competency in Deepfake Analysis and AI-driven Threat Detection
- Expertise in AI, machine learning, and audio-video manipulation detection, enabling precise identification of synthetic media threats.
- Advanced forensic capabilities to analyze metadata, acoustic fingerprints, facial anomalies, temporal distortions, and manipulation artifacts.
- Experience with biometric systems including voice authentication, facial recognition, liveness detection, and KYC integrity architectures.
- Ability to simulate real-world deepfake attacks involving executive impersonation, workflow manipulation, or cross-channel deception.
3. Skilled Cybersecurity Professionals with Specialized Capabilities
- Certified cybersecurity experts trained in adversarial testing, digital forensics, incident response, and identity security.
- Hands-on exposure to evolving AI-enabled threats, ensuring testing aligns with global attack trends and adversarial tactics.
- Cross-functional teams combining penetration testers, threat analysts, biometric specialists, and governance consultants for end-to-end coverage.
- Operational understanding of high-risk business processes, enabling realistic evaluation of approval chains, onboarding flows, and customer interactions.
4. End-to-End Value Across People, Process, Technology & Governance
- Strategic insights helping organizations enhance governance frameworks, identity assurance models, and communication integrity controls.
- Process resilience improvements that reinforce verification steps, escalation paths, and policy adherence during high-risk interactions.
- Workforce readiness uplift through awareness training, simulation-based learning, and response playbook development.
- Technology optimization support helping clients strengthen anti-spoofing systems, biometric controls, and AI detection mechanisms.
5. Industry-Relevant Expertise for India and Global Markets
- Understanding of sector-specific needs across BFSI, telecom, healthcare, government, critical infrastructure, and digital-first enterprises.
- Alignment with international standards ensuring assessments follow recognized security, privacy, and digital identity frameworks.
- Scalable service models offering Basic, Medium, and Advanced packages tailored to small, medium, and global enterprises.
- Experience in multicultural communication ecosystems enabling region-specific deepfake testing and fraud-prevention strategies.
6. Business Value Delivered to Clients
- Improved fraud prevention capability through identification of system and process gaps vulnerable to synthetic media exploitation.
- Enhanced trust and credibility across digital channels, customer interactions, and executive communications.
- Reduced operational and financial risks stemming from impersonation attacks, tampered KYC, and manipulated workflows.
- Long-term resilience as organizations adopt proactive defense strategies aligned with evolving AI-driven threat landscapes.
Founded in 2008 with 17+ Years of Industry Experience in Information and Cyber Security domain
Codec Networks Full-Spectrum Cybersecurity Expertise across all Industry Domains:
- Security Vulnerability Assessment & Penetration Testing (VAPT): Covering Web, Mobile, API, IoT, Blockchain, Cloud-Native, and smart infrastructure environments, with a focus on OWASP, MITRE ATT&CK, and real-world exploit simulation.
- Offensive Security & Deep Level Security Assessments: Advanced Red Team, Blue Team and Purple Team Exercises, Threat Simulations, Social Engineering Campaigns, and Secure Code Review.
- IT Security Audit & Compliance Services: Implementation and audit support for ISO/IEC 27001, ISO 27701, NIST CSF, RBI-CSF, SEBI, IRDAI, PCI DSS, HIPAA, SOC 2, GDPR, and India’s DPDPA 2023.
- Data Privacy & Strategic Risk Advisory: ISO 27701, GDPR, DPDPA, Cross-border compliance, DPIA, DPO-as-a-service, supply chain risk management, and digital transformation risk consulting.
- Emerging Technology Security (Web3.0 | AI | Blockchain): Specialized testing for smart contracts, DeFi platforms, Metaverse applications, AI/ML models, quantum readiness, and blockchain nodes.
- Managed SOC & Threat Monitoring Services: End-to-end SOC operations, SIEM/EDR/XDR/SOAR integration, threat intelligence, cloud security monitoring, and 24/7 incident response.
- Cyber Forensics & Threat Analysis: Investigation services including Device forensics, Malware Analysis, Cloud and Mobile forensics, insider threat detection, and Forensic support.
- Board-Level Cybersecurity Advisory Services to build governance, quantify risks, and align with enterprise-wide digital priorities : Codec Networks enables this transformation by offering Integrated Cyber Risk Management, GRC Program Advisory, Reputation Management, Crisis Communication Readiness, and CISO Support, tailored for CXOs and board members seeking to integrate cybersecurity into strategic decision-making.
- Cyber Security Education & Global Certifications - Through the Codec Centre for Professional Excellence, we deliver Post Graduate Certification in Advanced Cybersecurity (PGCAC), Graduate Certification in Advanced Cybersecurity (GCAC), Accredited Trainings & Certifications from EC Council, PECB, TUV, Quality Austria, ISACA and ISC2 - building the next generation of cybersecurity leaders.
- CERT-IN empaneled Information Security Auditing Organization
- NICSI empaneled for providing Application Audit and Compliance Services under Start-Up Category
- An ISO/IEC 27001:2022 certified company, has established Information Security Management System (ISMS), demonstrating a structured approach to manage and protect sensitive information from cyber threats.
- An ISO 9001 certified company, has established and maintains a certified Quality Management System (QMS) that meets international standards for quality and consistency
At Codec Networks, our foundation is built on deep technical mastery, certified expertise, and an unrelenting pursuit of cyber excellence. With a team of globally accredited professionals, advanced methodologies, and next-generation tools, we deliver measurable security outcomes across assessment, compliance, monitoring, and forensic domains.
Our competency-driven approach ensures every engagement is governed by precision, accountability, and alignment with international standards — empowering enterprises to stay secure, compliant, and resilient.
Governance, Risk & Compliance (GRC) Competency
Codec Networks’ dedicated Governance, Risk & Compliance (GRC) group specializes in security assessments, risk management, regulatory compliance, and audit readiness. The team partners with organizations to strengthen governance frameworks and ensure end-to-end compliance in a complex regulatory landscape.
Key Attributes:
- Team of certified auditors and consultants with credentials including ISO 27001 LA/LI, ISO 31000 Risk Specialist, ISO 27701 PIMS, GDPR, SOC 2, HIPAA, CCPA, DPO, CISA, CISM, CRISC, CISSP and other advanced industry certifications.
- Expertise in enterprise risk quantification, privacy impact assessment (PIA/DPIA), audit automation, and supply chain risk mapping.
- Proven track record in implementing ISO-based ISMS/PIMS frameworks, RBI/SEBI/IRDAI audits, and cross-border data compliance projects.
Vulnerability Assessment & Penetration Testing (VAPT) Expertise
Our VAPT teams bring extensive technical depth across Web, Mobile, API, Cloud, Network, Database, Infrastructure, IoT, and People & Process domains.
Every engagement is mapped to OWASP, NIST, MITRE ATT&CK, ISO 27001, PCI DSS, HIPAA, RBI, and GDPR frameworks — ensuring real-world relevance and compliance alignment.
Core Strengths:
- Certified professionals with CEH, C-PENT, LPT, OSCP, OSWE, OSEE, and CREST credentials, averaging 7–10 years of offensive security experience.
- Proven expertise in Red/Blue/Purple Teaming, DevSecOps, secure SDLC, and threat emulation.
- Continuous skill enhancement through CTFs, hackathons, and product certifications (on case to case basis) such as CCNA, CCNP, Juniper, Fortinet, McAfee, RSA etc
Managed SOC & Threat Intelligence Operations
Codec Networks operates a 24/7 Managed Security Operations Center (SOC) delivering continuous visibility, detection, and response across hybrid environments.
Our SOC integrates SIEM, SOAR, EDR/XDR, and Cloud-Native Analytics to ensure rapid threat detection, incident containment, and business continuity.
Key Capabilities:
- Certified SOC analysts with credentials such as CHFI, CEH, CompTIA CySA+, GCIA, GCFA, and Splunk Certified Architect.
- Integration with platforms like Splunk, QRadar, SentinelOne, CrowdStrike, Elastic, Microsoft Sentinel, and Cortex XSOAR.
- Advanced use cases include cloud posture management, insider threat analytics, MITRE ATT&CK–aligned detections, and threat hunting automation.
- Comprehensive SOC Maturity Assessments and Threat Intelligence Fusion through integration with global feeds and dark web monitoring.
Cyber Forensics & Threat Analysis Expertise
Our Cyber Forensic Division delivers end-to-end investigation, evidence preservation, and digital analysis services — designed to support law enforcement, corporate forensics, and internal response teams.
We combine forensic science with cyber intelligence to identify root causes, trace adversaries, and restore operational integrity.
Core Expertise Areas:
- Device, Network, Cloud, and Mobile Forensics – leveraging latest forensic tools (wherever applicable) such as Autopsy, Cyber Triage, Kape, EnCase, FTK, Magnet AXIOM, and Cellebrite.
- Malware Reverse Engineering and Memory Forensics for incident containment and threat attribution.
- Blockchain & Crypto Forensics – tracing DeFi fraud, NFT manipulation, and crypto laundering activities using Chainalysis, TRM Labs, and Elliptic (wherever applicable).
- Incident Response Support – forensic readiness, eDiscovery, evidence preservation, aligned with ISO/IEC 27037 & 27043.
- Certified experts including CHFI, eCIR, eCDFP, GCFE, GCFA, EnCE, CFCE and ECIH, ensuring investigations meet both technical and legal standards.
Advanced Tools, Frameworks & Continuous Innovation
Codec Networks leverages industry-leading tools and platforms such as Burp Suite Pro, Nessus, Prisma Cloud, Splunk, QRadar, CrowdStrike, SentinelOne, Autopsy, Chainalysis, MythX, and Prowler, (wherever applicable) ensuring accuracy, scalability, and efficiency.
Our methodologies align with globally recognized frameworks including:
- MITRE ATT&CK & D3FEND
- OWASP Top 10 / MASVS / ASVS
- NIST Cybersecurity Framework & SP 800-115
- ISO/IEC 27001, 27701, 31000, 22301
Through ongoing research, Codec Networks continually evolves to address modern threats — from Generative AI prompt attacks and smart contract exploits to IoT zero-days, metaverse impersonation, and quantum-era vulnerabilities.
Compliance-Driven Deliverables
All technical engagements and reports are mapped to major global and Indian compliance frameworks — including ISO 27001, PCI DSS, HIPAA, GDPR, RBI-CSF, SEBI, IRDAI, and DPDPA 2023.
Our structured technical and executive reports support board-level visibility, audit evidence, and certification readiness, ensuring that every engagement drives both technical assurance and regulatory confidence.
Codec Networks – Certified Competence. Proven Expertise. Real-World Cyber Resilience.
Empowering enterprises through advanced security engineering, continuous monitoring, and forensic intelligence.
At Codec Networks, we believe that cybersecurity excellence is not achieved through tools alone — it is built through methodical delivery, risk-based insight, and measurable outcomes.
Our Agile and Modular 8-Stage Delivery Methodology ensures that every engagement — from rapid risk assessments to full-scale ISMS implementations - is structured, standards-aligned, and business-focused.
Agile & Modular Methodology
Our delivery framework integrates global best practices with localized regulatory insight, ensuring each engagement is executed with clarity, accountability, and precision. Clients benefit from seamless onboarding, milestone-driven execution, and transparent reporting throughout the lifecycle.
- Discovery & Scoping: Collaborative workshops to understand business context, IT landscape, compliance obligations, and risk appetite, forming the foundation of a well-defined project scope.
- Risk Profiling & Gap Assessment: Comprehensive evaluation of people, process, and technology controls aligned with ISO 27001, NIST CSF, GDPR, HIPAA, DPDPA 2023, RBI, and PCI DSS.
- Regulatory Mapping & Framework Alignment: Mapping organizational obligations against applicable standards and laws — from ISO & NIST to RBI, SEBI, IRDAI, UIDAI, and DPDPA — including new-age frameworks like ISO 42001 (AI) and FATF for emerging technologies.
- Security Architecture & Control Design: Designing or refining network, cloud, and data security architectures with controls tailored for cloud, AI, OT/ICS, and Web3.0 environments.
- Documentation & Policy Development: Creation and refinement of Policies, SOPs, Risk Registers, DPIAs, Incident Response Plans, and Governance Documents, ensuring audit readiness and legal compliance.
- Implementation & Risk Treatment: Execution of remediation roadmaps, vendor risk management, privacy engineering, and workforce training to mitigate gaps and operationalize security controls.
- Validation, Testing & Audit Readiness: Conducting mock audits, VAPT, forensic readiness, and compliance testing to validate effectiveness and prepare for certifications.
- Governance Reporting & Continual Improvement: Delivering executive dashboards, compliance scorecards, and board-level insights with ongoing advisory through vCISO and DPO-as-a-Service models.
Risk-Based & Business-Oriented Audit Approach
Our methodology goes beyond testing systems — it focuses on how vulnerabilities translate into business, reputational, and compliance risks.
- Deliver Deep Insight: Actionable intelligence into vulnerabilities, attack paths, business impact, and remediation priorities.
- Extend Beyond Tools: Manual and contextual assessments combining automation with human expertise across government, financial, and commercial sectors.
- Actionable Reporting: Executive-friendly reports that translate complex findings into strategic, risk-aware recommendations.
- Efficient Execution: Critical assets prioritized for testing to deliver maximum value within tight engagement windows.
Outcome-Driven Engagements for Security Maturity
Each stage is modular yet interconnected, adaptable to enterprises of any scale or industry. Whether it’s a cloud-native fintech pursuing SOC 2, a healthcare provider ensuring HIPAA alignment, or a bank meeting RBI-CSF requirements, Codec Networks ensures consistency, compliance, and measurable improvement.
Beyond certification checklists, our Post-Audit Support and Continuous Risk Monitoring provide remediation guidance, breach response playbooks, staff training, and ongoing compliance tracking — building sustainable security posture and resilient business continuity.
Codec Networks – Turning Compliance into a Competitive Advantage.
Structured. Measurable. Secure. Always Aligned with Your Business Goals.
At Codec Networks, our clients are not just audit subjects—they are long-term partners in a shared cybersecurity journey. Every engagement is designed around the client’s business priorities, security maturity, and risk appetite, ensuring solutions that are relevant, practical, and results-driven.
With a legacy of 650+ successful engagements across industries such as Banking, Fintech, Healthcare, Telecom, Energy, Aviation, Manufacturing, E-commerce, and Government, Codec Networks has attempted to become a trusted advisor for organizations seeking to transform compliance into resilience.
Our engagement philosophy extends beyond conventional audits. We integrate strategic advisory, technical assurance, remediation support, and continuous compliance monitoring, creating a full lifecycle relationship rather than a one-time service. Clients benefit from:
- Personalized advisory frameworks tailored to their business model and operational scale.
- Collaborative engagement models featuring joint workshops, stakeholder training, and compliance awareness sessions.
- Board-level guidance and reporting that translates complex technical findings into actionable business intelligence.
- Transparent communication channels with dedicated project managers, secure digital workspaces, and real-time status dashboards.
By combining the objectivity of an auditor with the empathy of an advisor, Codec Networks builds trust, accountability, and measurable security growth. Our commitment is simple — to deliver cybersecurity as a continuous partnership, not a periodic project.
Codec Networks – Where Advisory Meets Assurance.
Empowering Clients Through Partnership, Transparency, and Trust.
At Codec Networks, integrity, professionalism, and ethical responsibility form the cornerstone of every engagement. As a trusted strategic partner in cybersecurity, we operate within the highest standards of ethical conduct, legal compliance, and regulatory governance, ensuring our services strengthen both our clients’ defenses and their reputations.
We adhere to a strict ethical code of conduct, driven by transparency, independence, and accountability. Every consultant, auditor, and engineer within Codec Networks upholds the core security triad of Confidentiality, Integrity, and Availability (CIA) — ensuring data protection, operational reliability, and business continuity at all times.
Our professional ethos blends technical excellence with moral responsibility, following structured processes, defined service standards, and adherence to international and national regulatory frameworks.
Our Ethical & Professional Commitments
- Zero-Compromise Consulting: We maintain independence, neutrality, and confidentiality across all audits and advisory engagements.
- Legal & Regulatory Conformance: We assist clients to conform strictly within the boundaries of applicable cyber laws, privacy regulations, and data protection statutes.
- Client-First Philosophy: Every recommendation is designed to safeguard stakeholder interests, minimize legal exposure, and build sustainable resilience.
- Outcome-Driven Security Maturity: Our modular yet integrated delivery approach supports organizations of all sizes in achieving measurable improvements in security posture.
- Global Delivery, Local Integrity: Our Global Network Delivery Model integrates international best practices with local regulatory expertise — ensuring value-driven, compliant outcomes.
Industry-Specific Security Advisory
Recognizing that every sector faces distinct threats and compliance challenges, Codec Networks provides customized, industry-aligned security advisory across BFSI, Fintech, Telecom, Healthcare, Energy, Aviation, E-commerce, Government, and Critical Infrastructure domains.
Our sector-specific consulting translates regulatory complexity into practical, business-aware strategies, ensuring risk mitigation plans are compliant, auditable, and operationally feasible.
Our Commitment
With a zero-tolerance approach to ethical compromise, Codec Networks stands for trust, transparency, and truth in cybersecurity. We are more than consultants — we are custodians of digital integrity, committed to helping organizations navigate risk, maintain compliance, and enable secure business growth.
Codec Networks – Where Integrity Meets Innovation. Trusted. Ethical. Future-Ready.
At Codec Networks, we combine the strength of a global delivery ecosystem with the precision of local regulatory insight to deliver cybersecurity solutions that are both internationally benchmarked and regionally compliant.
Our Global Delivery Capability enables clients across continents to access specialized cybersecurity expertise, advanced technologies, and globally aligned methodologies. Through a distributed network of certified professionals, partner alliances, and intelligence centers, Codec Networks ensures consistent service quality and rapid response across time zones and geographies.
What truly differentiates us is our Local Expertise—a deep understanding of national regulations, industry frameworks, and operational nuances that shape cybersecurity implementation in each region.
Our hybrid delivery model blends remote and on-site collaboration, combining the agility of digital operations with the contextual understanding of local consultants. This ensures culturally aligned communication, faster problem resolution, and seamless coordination with client teams.
With a presence across India, Codec Networks empowers global enterprises to manage cybersecurity uniformly while adapting to local risks, regulations, and realities.
Codec Networks – Global Vision. Local Precision. Consistent Cyber Resilience.
“With Codec Networks, you’re not just buying a service — you’re investing in a cybersecurity ally who understands your business, defends your reputation, and strengthens your future.”
At Codec Networks, we believe cybersecurity is not a project — it’s a partnership.
Our approach is built on trust, transparency, and transformation, helping clients evolve from compliance readiness to cyber resilience.
Your Strategic Security Partner
Codec Networks acts as a strategic security partner, providing continuous roadmap development, architecture reviews, and improvement programs that evolve with your business and the threat landscape.
“We don’t just secure businesses — we empower them to lead with confidence in a digital-first world.”
Our strength lies in the fusion of technical depth, regulatory insight, industry specialization, and future readiness — providing unmatched cybersecurity value to enterprises across India and beyond.
Codec Networks – Certified Competence. Proven Expertise. Real-World Cyber Resilience.
Empowering enterprises through advanced security engineering, continuous monitoring, and forensic intelligence.
Every engagement reflects our belief that advisory must meet assurance — a promise we deliver through partnership, integrity, and measurable impact.
Codec Networks – Where Advisory Meets Assurance.
Empowering Clients Through Partnership, Transparency, and Trust.
And above all —
“Decoding Threats. Coding Solutions.”
That’s the Codec Networks Advantage.
WHAT OUR CUSTOMERS SAY
Their deepfake simulation services reveals critical vulnerabilities and enabled us to
reinforce identity verification across high-risk workflows.
-
“Vijay is a passionate Software Developer specializing in building scalable web applications and APIs. He enjoys solving complex problems with clean”
Vijay
Software Developer -
“Deepak is a passionate Software Developer specializing in building scalable web applications and APIs. He enjoys solving complex problems with clean”
Deepak
Software Developer -
“Dhruv is a passionate Software Developer specializing in building scalable web applications and APIs. He enjoys solving complex problems with clean”
Dhruv
Software Developer
“Vijay is a passionate Software Developer specializing in building scalable web applications and APIs. He enjoys solving complex problems with clean”
Vijay
Software Developer
“Deepak is a passionate Software Developer specializing in building scalable web applications and APIs. He enjoys solving complex problems with clean”
Deepak
Software Developer
“Dhruv is a passionate Software Developer specializing in building scalable web applications and APIs. He enjoys solving complex problems with clean”
Dhruv
Software DeveloperINDUSTRY & SECURITY THREAT LANDSCAPE
Deepfake sophistication is accelerating, enabling attackers to exploit weak verification
controls and bypass traditional fraud-prevention mechanisms.
Industry Dynamics:
- High-volume remote transactions & voice approvals: Banks increasingly accept remote authorizations and IVR approvals; attackers abuse voice cloning to authorize fraudulent transfers, causing immediate financial loss and complex forensic trails. Detection gaps in legacy voice systems increase risk exposure.
- Digital onboarding / video KYC reliance: Rapid digital onboarding raises dependence on automated video KYC and liveness checks that can be bypassed by deepfakes or replay attacks, enabling synthetic-identity fraud.
- Regulatory & compliance pressure: Regulators expect strong identity-assurance controls and audit trails; failures can trigger fines, reputational harm, and stricter oversight.
- Social-engineering augmented by deepfakes: Multi-channel fraud (email + vishing + deepfake voice) increases success rates of account takeover and CEO/funds-transfer scams.
- High financial impact & speed of loss: Once fraud executes, reversal is hard—rapid detection and validated evidence are vital to contain losses and support remediation.
How AI-Powered Deepfake Testing helps:
- Validate voice-biometric resilience: Simulated voice-clone attacks test IVR and biometric thresholds, revealing bypass methods and required tuning to reduce spoof acceptance. This provides evidence-based tuning and vendor-hardening recommendations.
- Harden video KYC & liveness checks: Controlled deepfake KYC attempts show where automated checks fail and how manual/ML hybrid controls should be applied. Results enable improved onboarding gating and fraud rules.
- Refine escalation & transaction controls: Tests expose weak approval chains; remediation designs multi-step verifications and anomaly triggers for high-risk transactions, reducing single-point failures.
- Provide forensic evidence & audit trails: Forensic scoring of attempted spoofs creates admissible artifacts and timelines useful for investigations and regulator reporting.
- Train frontline staff with realistic simulations: Phishing + vishing + deepfake drills increase employee detection capability and correct procedural behaviours under pressure.
- Quantify residual risk for boards/regulators: Risk scoring and post-remediation re-tests produce measurable KPIs for governance and compliance evidence.
INDUSTRY & SECURITY THREAT LANDSCAPE
Deepfake sophistication is accelerating, enabling attackers to exploit weak verification
controls and bypass traditional fraud-prevention mechanisms.
Industry Landscape
Industry Dynamics:
- High-volume remote transactions & voice approvals: Banks increasingly accept remote authorizations and IVR approvals; attackers abuse voice cloning to authorize fraudulent transfers, causing immediate financial loss and complex forensic trails. Detection gaps in legacy voice systems increase risk exposure.
- Digital onboarding / video KYC reliance: Rapid digital onboarding raises dependence on automated video KYC and liveness checks that can be bypassed by deepfakes or replay attacks, enabling synthetic-identity fraud.
- Regulatory & compliance pressure: Regulators expect strong identity-assurance controls and audit trails; failures can trigger fines, reputational harm, and stricter oversight.
- Social-engineering augmented by deepfakes: Multi-channel fraud (email + vishing + deepfake voice) increases success rates of account takeover and CEO/funds-transfer scams.
- High financial impact & speed of loss: Once fraud executes, reversal is hard—rapid detection and validated evidence are vital to contain losses and support remediation.
How AI-Powered Deepfake Testing helps:
- Validate voice-biometric resilience: Simulated voice-clone attacks test IVR and biometric thresholds, revealing bypass methods and required tuning to reduce spoof acceptance. This provides evidence-based tuning and vendor-hardening recommendations.
- Harden video KYC & liveness checks: Controlled deepfake KYC attempts show where automated checks fail and how manual/ML hybrid controls should be applied. Results enable improved onboarding gating and fraud rules.
- Refine escalation & transaction controls: Tests expose weak approval chains; remediation designs multi-step verifications and anomaly triggers for high-risk transactions, reducing single-point failures.
- Provide forensic evidence & audit trails: Forensic scoring of attempted spoofs creates admissible artifacts and timelines useful for investigations and regulator reporting.
- Train frontline staff with realistic simulations: Phishing + vishing + deepfake drills increase employee detection capability and correct procedural behaviours under pressure.
- Quantify residual risk for boards/regulators: Risk scoring and post-remediation re-tests produce measurable KPIs for governance and compliance evidence.
Industry Dynamics:
- Highly digital-native, irreversible transactions: Crypto and fintech transactions are often instantaneous and irreversible; deepfake-enabled KYC bypass or voice scams enable large, final losses.
- Mass onboarding at scale: Automated onboarding and lightweight KYC create an attractive surface for synthetic identities and deepfake KYC fraud.
- Innovation speed vs. security trade-offs: Fast product cycles sometimes outpace robust anti-spoofing controls, increasing exploitable gaps.
- Targeting high-value accounts and transfers: Attackers prioritize high-net-worth users and exchange withdrawals—deepfake voice/email combos increase success likelihood.
- Regulatory scrutiny & AML expectations: Regulators demand stronger identity proofing and transaction monitoring as fraud trends escalate.
How AI-Powered Deepfake Testing helps:
- Stress-test KYC pipelines at scale: Large-batch deepfake submissions reveal systemic acceptance gaps, informing thresholds and human-review triggers.
- Protect high-value transactions with multi-vector checks: Design of multi-modal verification (behavioral, device, voice/video) reduces single-factor exploitation.
- Reduce false positives while catching deepfakes: Forensic scoring balances UX and security by tuning detection models to minimize customer friction.
- Provide evidence to exchanges/regulators: Detailed incident artifacts assist in compliance reporting and law-enforcement engagement.
- Help build fraud playbooks for rapid containment: Scenario-based response plans reduce time-to-containment for live incidents.
Industry Dynamics:
- Heavy dependence on voice channels: Telcos and contact centers use voice for authentication, support, and service changes—making them prime targets for voice cloning and vishing.
- Large distributed agent workforces: Agents often follow scripts and may be tricked by convincing cloned voices, increasing successful social-engineering incidents.
- Omnichannel integration risk: Voice attacks paired with compromised digital channels accelerate fraud and data exfiltration.
- Regulatory obligations for customer data protection: Telecom regulators require robust authentication and incident management; breaches invite penalties and customer churn.
- Operational strain from fraud volume spikes: Large-scale vishing campaigns can overwhelm verification processes and erode trust.
How AI-Powered Deepfake Testing helps:
- Simulated vishing campaigns against live processes: Reveal agent behaviours and procedural gaps to refine scripting and verification checklists.
- Test and harden voice-biometric vendor setups: Determine spoof thresholds and integration points that reduce false acceptance without harming throughput.
- Design agent escalation workflows: Strengthen multi-factor confirmation and supervisory checks for high-risk requests, reducing unilateral action.
- Provide training modules with real deepfake samples: Builds agent intuition and improves compliance to verification scripts.
- Supply monitoring rules and detection signatures: Forensic artifacts support deployment of real-time anomaly detection and call-scoring systems.
Industry Dynamics:
- Growing telehealth adoption: Remote consultations and recorded telemedicine sessions can be spoofed, risking misdiagnoses, false prescriptions, and misinformation. Recent cases show fake-doctor videos spreading harmful health claims.
- Sensitive personal data exposure: Health records and identifying data are valuable for identity fraud and insurance scams; deepfakes enable social-engineering to access records.
- Regulatory privacy obligations (HIPAA, local health laws): Providers must demonstrate controls for patient identity validation and secure telehealth interactions.
- Reputation risk from misattributed medical statements: Fake videos of clinicians endorsing products or making statements can damage trust and invite legal action.
- Supply chain & appointment fraud: Deepfakes may be used to alter consent or authorize procedures illicitly.
How AI-Powered Deepfake Testing helps:
- Validate telehealth identity-verification: Test liveness and identity checks for teleconsultations to prevent fake-patient or fake-clinician scenarios.
- Detect manipulated clinical recordings: Forensic analysis differentiates authentic clinical media from synthesized or tampered content.
- Reduce insurance and prescription fraud: Simulated attacks uncover avenues fraudsters use to claim benefits or falsify authorizations.
- Support regulatory evidence and incident response: Forensic artifacts and chain-of-custody help comply with audits and investigations.
- Train clinical and administrative staff: Awareness modules help frontline staff spot suspicious interactions and follow escalation protocols.
Industry dynamics:
- Content authenticity & brand protection: Media firms risk reputational damage when deepfakes misattribute statements to public figures or manipulate news content.
- Rapid viral spread on social platforms: Fake celebrity or journalist videos amplify misinformation, legal disputes, and advertiser fallout.
- Copyright & consent issues: Unauthorized synthetic reuse of actors’ likenesses creates IP, personality-rights, and contractual liabilities.
- Monetization & trust challenges for streaming platforms: Platforms need robust detection to prevent reputational harm and regulatory scrutiny.
- Demand for authenticity verification tools: Publishers require fast verification for UGC, wire content, and breaking-news sources.
How AI-Powered Deepfake Testing helps:
- Provide rapid forensic verification for editorial workflows: Fast authenticity scoring helps editors decide whether to publish or flag content.
- Protect talent and IP through detection & monitoring: Continuous monitoring and forensics identify misuse of artist likeness and enable takedowns.
- Support legal claims with forensic evidence: Chain-of-custody and manipulation reports strengthen legal action and takedown requests.
- Reduce misinformation impact via early detection: Early identification allows platforms to label, remove, or contextualize manipulated media quickly.
- Advise content-provenance controls: Recommend provenance standards (hashing, watermarks, metadata practices) to reduce falsification risks.
Industry Dynamics:
- Threats to public trust & democratic processes: Deepfakes of officials or political ads can influence public opinion, spread disinformation, and destabilize civic processes.
- Critical communication integrity needs: Emergency alerts, public health announcements, and official briefings must be reliably authenticated.
- Regulatory and legal complexity: Governments must balance free speech, platform liability, and anti-misinformation laws; prosecutions and policy actions are evolving.
- National security & foreign influence risks: State and non-state actors may use synthetic media for strategic deception or influence operations.
- Operational exposure across agencies: Identity spoofing can target procurement, finance, and citizen services with direct operational impact.
How AI-Powered Deepfake Testing helps:
- Test public-facing authentication channels: Simulated manipulations of official media help agencies harden verification and provenance controls.
- Support election and campaign monitoring: Forensic tools detect synthetic campaign content and provide evidence for platform takedowns and legal action.
- Strengthen crisis communication authenticity: Verification frameworks ensure citizens can trust emergency communications and official statements.
- Inform policy and governance frameworks: Assessment outcomes inform technical standards and guidance for labeling and transparency.
- Train officials on response & rapid verification: Equip spokespeople and media teams to validate and respond to manipulated content quickly.
Industry dynamics:
- Large online customer base and remote verification: E-commerce platforms rely on remote identity checks for high-value orders and seller onboarding; deepfakes enable fraud and account takeover.
- Merchant onboarding & KYC vulnerabilities: Fraudsters use synthetic IDs and deepfake KYC to onboard as sellers or access payouts.
- Chargebacks and seller fraud complexity: Manipulated evidence complicates dispute resolution and increases operational costs.
- Brand trust & customer experience trade-offs: Stronger checks may hurt conversion rates; false rejections damage UX and sales.
- Cross-border regulatory and payment compliance: Payment processors need verified identities to meet AML/CFT and PSP requirements.
How AI-Powered Deepfake Testing helps:
- Tune KYC/liveness thresholds to reduce fraud without harming conversions: Forensic testing helps set optimal tradeoffs between UX and security.
- Detect synthetic merchant or buyer profiles: Deepfake tests reveal how fraudsters bypass seller verification and enable tighter controls.
- Support dispute resolution with credible forensic reports: Forensic artifacts assist in adjudicating chargebacks and liability claims.
- Design layered verification journeys: Recommend risk-based flows where high-risk transactions trigger additional checks or human review.
- Enable continuous monitoring of onboarding pipelines: Periodic re-testing ensures evolving attack techniques remain covered.
Industry Dynamics:
- Claims fraud and false documentation: Attackers use manipulated audio/video to support false claims, authorize payouts, or impersonate policyholders.
- Remote assessment & tele-insurance processes: Virtual inspections and recorded statements are vulnerable to tampering and synthetic replacement.
- Regulatory scrutiny on claims validation & anti-fraud measures: Insurers must show robust processes to avoid sanction and financial loss.
- High-cost payouts & adversarial incentives: Large payouts incentivize sophisticated fraud like deepfake-supported liability claims.
- Complex multi-party verification challenges: Claim verification often needs cross-validation across providers, making synthesized evidence disruptive.
How AI-Powered Deepfake Testing helps:
- Authenticate claimant media using forensic scoring: Distinguish genuine claimant statements from manipulated submissions and preserve chain-of-custody.
- Simulate fraud scenarios to strengthen controls: Tests reveal weak steps in claims acceptance and suggest tightened verification or additional evidence requirements.
- Reduce false claims payout through improved detection: Early detection of synthetic media prevents erroneous disbursal and protects reserves.
- Support regulatory compliance and audit readiness: Forensic artifacts and process improvements demonstrate robust anti-fraud postures.
- Train claims adjusters and fraud teams: Scenario-based exercises improve adjudicators’ ability to spot manipulation and follow escalation.
Industry Dynamics
- Increasing Remote Collaboration and Digital Communication Platforms
IT and ITES companies rely extensively on video conferencing, voice communication, and collaboration tools for client interactions and project management. - Outsourced Service Delivery and Global Client Interactions
Technology service providers frequently manage remote operations and cross-border communication with global clients. - Growing Use of AI-Based Authentication and Voice Interfaces
Many technology companies deploy voice assistants, voice authentication systems, and AI-enabled customer service platforms - Regulatory and Data Protection Compliance Requirements
Deepfake impersonation attacks could lead to data breaches, reputational damage, and regulatory non-compliance.
How AI-Powered Deepfake Testing Helps
- Identification of Vulnerabilities in Digital Communication Platforms
Deepfake testing simulates voice and video impersonation scenarios during remote meetings and client interactions, helping organizations detect weaknesses in communication verification processes. - Strengthening Identity Verification and Authentication Mechanisms
Testing helps validate the resilience of voice-based authentication systems and AI-driven communication tools against synthetic voice manipulation. - Enhancing Employee Awareness and Fraud Detection
Simulated deepfake scenarios train employees to identify suspicious voice or video communications, reducing the risk of social engineering attacks. - Protecting Client Data and Business Operations
By identifying potential impersonation attack vectors, organizations can strengthen internal controls and ensure secure handling of client communications and sensitive data.
Industry Dynamics
- High-Value Target for Nation-State Cyber Attacks
Defense and aerospace organizations are frequent targets of sophisticated cyber adversaries seeking access to classified information and strategic communication systems. - Secure Communication Requirements for Strategic Operations
Deepfake manipulation of such communications could disrupt operations or create misinformation during critical missions. - Protection of Classified Information and Sensitive Infrastructure
Deepfake impersonation could be used to trick personnel into sharing classified information or granting unauthorized access. - Compliance with National Cybersecurity and Defense Regulations
Defense and aerospace sectors operate under strict regulatory frameworks and national security guidelines..
How AI-Powered Deepfake Testing Helps
- Validation of Secure Communication Channels
Deepfake testing evaluates whether voice and video communication systems used in defense environments can detect or resist synthetic impersonation attacks. - Prevention of High-Level Impersonation Attacks
Simulated attacks help identify vulnerabilities where adversaries could impersonate senior officials or commanders to manipulate operational decisions. - Strengthening Security Awareness Among Personnel
Deepfake simulations help defense personnel recognize manipulated voice or video communications and follow strict verification protocols. - Protecting National Security and Strategic Information
By identifying weaknesses in authentication and communication systems, deepfake testing strengthens defenses against advanced AI-enabled espionage and information manipulation threats
Threat Landscape
Threat / Challenge:
Deepfake voice impersonation is one of the fastest-growing threats, where attackers clone the voice of executives, customers, or approval authorities with astonishing realism. These synthetic voices are used to trick employees into authorizing payments, sharing confidential information, or overriding controls in high-pressure situations. Because voice carries authority and familiarity, staff often comply without questioning the authenticity of the caller. Traditional verification methods—such as callback checks or simple questioning—are ineffective when attackers can convincingly mimic vocal tone, cadence, and emotional cues. This enables fraudsters to bypass internal controls and exploit trust-based communication processes. Organizations face severe financial damage, internal confusion, and breakdown of accountability when fraudulent instructions appear to come from leadership. The psychological impact on teams—realizing they acted on a fake voice—can further erode long-term trust in communication channels.
How AI-Powered Deepfake Testing Mitigates This Threat
- Simulated voice-clone attacks replicate real impersonation scenarios to expose procedural weaknesses and reinforce multi-factor verification steps for high-risk actions.
- Acoustic forensic analysis identifies spectral and synthesis anomalies, enabling detection of subtle artifacts invisible to human hearing and exposing disguised callers.
- Voice-biometric bypass testing highlights systemic weaknesses, enabling organizations to recalibrate thresholds and introduce layered authentication mechanisms.
- Risk scoring reveals vulnerable roles and workflows, helping teams redesign approval hierarchies and reduce overreliance on single-person authorization.
- Employee training using real deepfake samples sharpens detection skills, improving their ability to challenge suspicious instructions instead of acting impulsively.
Threat /Challenge:
Video deepfakes are increasingly being used to pass KYC checks, onboarding processes, remote hiring interviews, and vendor verification steps. Attackers manipulate facial features, lip movements, lighting, and expressions to mimic real individuals or create entirely new identities. Automated liveness checks often fail to detect these synthetic models, especially when attackers use well-trained generative systems tailored to specific platform weaknesses. The growing dependence on digital onboarding means organizations may unknowingly approve fraudulent accounts, merchants, or job applicants who later conduct large-scale financial or operational fraud. This creates regulatory exposure, as auditors expect verifiable identity assurance, especially in risk-sensitive sectors. The damage is not only operational—deepfake-enabled onboarding fraud erodes trust in digital-first processes and forces companies to re-invest heavily in remediation.
How AI-Powered Deepfake Testing Mitigates This Threat
- Controlled deepfake KYC submissions identify failure points in liveness detection, document verification, and facial recognition pipelines across all onboarding journeys.
- Video forensic analysis detects inconsistencies in frames, lighting, artifacts, and movement, enabling rapid identification of manipulated media.
- Process evaluations highlight procedural loopholes, such as weak secondary checks, insufficient manual review, or overdependence on automation.
- Remediation recommendations strengthen digital identity proofing, improving the reliability and defensibility of onboarding and verification workflows.
- Post-fix validation ensures enhanced controls actually detect synthetic videos, delivering long-term resilience against evolving attack methods.
Threat / Challenge:
Attackers now combine phishing emails, cloned voice calls, and manipulated video messages to execute highly coordinated social-engineering operations. These multi-vector attacks create a convincing narrative that appears consistent across communication channels, making them extremely difficult for employees to challenge. When an email is reinforced by a follow-up deepfake voice call—or a fake video of a senior leader—the urgency and authenticity feel overwhelmingly real. This manipulative layering bypasses human intuition, incident escalation protocols, and standard verification steps. Organizations struggle because most training and policies are designed for traditional social engineering, not AI-augmented deception. The real danger lies in how these attacks exploit trust, context, and pressure to trick employees into harmful decisions. This results in compromised accounts, unauthorized transfers, confidential data exposure, and long-lasting operational disruption.
How AI-Powered Deepfake Testing Mitigates This Threat
- End-to-end deepfake attack simulations reveal weaknesses in human judgment, process adherence, and cross-functional escalation mechanisms.
- Targeted testing uncovers vulnerable departments, allowing for role-specific improvements to procedures and staffing readiness.
- Awareness modules incorporating real deepfake samples recalibrate employee intuition, teaching them to challenge even convincing communication.
- Structured verification playbooks strengthen staff decision-making, reducing reliance on trust and contextual cues that attackers exploit.
- Layered authentication designs reduce single-channel reliance, ensuring multi-vector attacks cannot bypass controls easily.
Threat / Challenge:
Synthetic identities—created using a mix of real data and AI-generated voice/video—pose one of the most difficult challenges to modern enterprises. These identities can pass automated onboarding, apply for credit, obtain benefits, gain platform access, or integrate into supply chains. Deepfakes make these identities appear extremely authentic during KYC, HR interviews, vendor validations, or customer support interactions. Once established, synthetic personas can remain undetected for months, causing operational disruption, revenue leakage, and compliance failures. Regulators expect enterprises to demonstrate robust identity assurance, and synthetic identity fraud raises the likelihood of penalties and legal consequences. The long life cycle of synthetic identities means that detection delays translate directly to larger damage footprints. Without proactive testing, organizations inadvertently build systems that deepfakes can exploit with ease.
How AI-Powered Deepfake Testing Mitigates This Threat
- Synthetic-media forensic testing uncovers manipulated onboarding artifacts, helping organizations spot synthetic or hybrid identities early.
- Pipeline assessments identify weaknesses in document validation and identity verification logic, informing stronger review protocols.
- Threat modeling reveals how synthetic identities bypass checks, guiding design of enhanced authentication requirements.
- Video/voice spoof testing shows where additional verification methods are needed, reducing acceptance of fabricated personas.
- Governance recommendations align identity workflows to global digital-trust frameworks, reducing regulatory and compliance risks.
Threat / Challenge:
Deepfakes enable attackers to authorize financial transfers, modify payment instructions, or demand emergency procurement approvals by impersonating senior decision-makers. These attacks exploit urgency, hierarchy, and trust—especially in organizations where leadership communicates remotely. Employees often fear questioning high-level requests, making impersonation-based fraud extremely effective. When deepfake voices or videos issue “urgent” instructions, teams may bypass controls or skip validation steps altogether. Once executed, fraudulent transactions are difficult to reverse, especially in cross-border or crypto-enabled environments. The reputational fallout can be immense, as stakeholders perceive internal control failures and weak governance. Attackers also use these frauds to pivot deeper into financial systems and conduct follow-up exploits.
How AI-Powered Deepfake Testing Mitigates This Threat
- Simulated impersonation attempts identify weak authorization processes, enabling redesign of multi-step controls for sensitive financial actions.
- Workflow mapping highlights overreliance on trust-based approvals, prompting stronger segregation of duties and supervisory checks.
- Escalation enhancements ensure staff cannot act on high-risk requests without verification, reducing pressure-based errors.
- Forensic outputs support early detection of real attacks, allowing security teams to intervene before losses escalate.
- Training programs reduce susceptibility to authority-based deception, empowering employees to verify first, act later.
Threat / Challenge:
Organizations increasingly face AI-manipulated videos or audio recordings inaccurately portraying senior leaders, employees, or corporate actions. These files spread rapidly across social media and internal networks, creating confusion, misinformation, and reputational damage. Attackers use falsified media to influence markets, harm partnerships, or spark internal disruption. Legal teams struggle to prove authenticity without sophisticated forensic capabilities, delaying crisis response. Stakeholders—customers, investors, regulators—often react before the organization can issue a corrective statement. The speed and believability of deepfake-driven misinformation campaigns make them uniquely dangerous. The impact can extend for months, influencing customer trust, employee morale, and legal exposure.
How AI-Powered Deepfake Testing Mitigates This Threat
- Deep forensic analysis differentiates authentic media from manipulated content, providing fast, defensible evidence for PR, legal, and crisis teams.
- Provenance and media-handling recommendations reduce manipulation opportunities, helping organizations adopt secure content pipelines.
- Simulated misinformation drills train teams for rapid response, minimizing confusion and containing narrative spread.
- Governance frameworks strengthen communication validation, ensuring official statements are verifiable and tamper-resistant.
- Monitoring guidance enhances early detection, allowing misinformation to be addressed before it gains traction externally.
Threat / Challenge:
Biometric systems—voice recognition, facial recognition, and liveness detection—are becoming essential to remote identity verification. However, attackers now create highly accurate voice clones and video deepfakes capable of bypassing these controls with minimal effort. When biometric systems are compromised, attackers can gain unauthorized access, approve high-value activities, or reset accounts. Organizations often assume biometric systems are inherently secure, making them slow to identify bypass attempts. The combination of AI-generated media and system blind spots creates a false sense of trust in automation. Compliance frameworks increasingly demand proof that biometric tools withstand spoofing attempts. Without rigorous testing, enterprises risk silent compromise of critical identity systems.
How AI-Powered Deepfake Testing Mitigates This Threat
- Anti-spoofing testing reveals real bypass scenarios, enabling recalibration of biometric thresholds and vendor engagement for enhanced controls.
- ML-based anomaly detection identifies subtle spoof markers, improving system accuracy against synthetic media.
- Comparative benchmarking helps select stronger biometric solutions, closing systemic weaknesses in voice or face authentication.
- Multi-modal verification recommendations strengthen identity proofing, reducing reliance on any single biometric factor.
- Re-testing confirms long-term improvement, ensuring systems continue resisting new and evolving attack patterns.
Threat / Challenge:
Deepfakes are increasingly used to manipulate public opinion, influence markets, or disrupt internal organizational stability. Attackers craft highly realistic media portraying leaders making damaging statements or acting contrary to policy. Once released, this content circulates quickly, triggering panic, confusion, or reputational crises. Organizations struggle because misinformation spreads faster than official corrections can be issued. Disinformation attacks can also be timed to coincide with critical periods—product launches, investor meetings, regulatory filings—maximizing damage. Employees may also unknowingly amplify synthetic content internally, worsening internal communication breakdowns. The erosion of trust—internally and externally—has financial, operational, and governance consequences that extend far beyond the initial incident.
How AI-Powered Deepfake Testing Mitigates This Threat
- Threat simulations expose weak points in public-facing communications, enabling organizations to design more resilient messaging workflows.
- Forensic validation provides rapid confirmation of authenticity, supporting takedown requests and crisis communications.
- Governance guidance strengthens media integrity controls, preventing uncontrolled release or misuse of official content.
- Awareness training teaches employees to recognize suspicious content, reducing internal spread and confusion.
- Monitoring recommendations enhance early detection, allowing organizations to counter misinformation before it escalates.
Threat / Challenge:
Attackers use voice deepfakes to impersonate customers, request account resets, or manipulate support staff into disclosing sensitive information. Contact centers, especially outsourced ones, remain vulnerable due to script-based responses and high call volumes. Fraudsters exploit empathy, urgency, or pressure to trick agents. Successful attacks lead to account takeover, data leakage, and regulatory noncompliance.
How the Service Mitigates This Threat
- Simulated vishing and voice-clone attacks test agent adherence to verification protocols, identifying training or process gaps.
- Workflow redesign improves escalation procedures, reducing unauthorized account actions.
- Awareness programs increase agent detection skills, helping them recognize unnatural vocal patterns or manipulated context.
- Rules-based guidance adds secondary-verification steps, reducing reliance on caller identity.
- Metrics-driven maturity mapping helps improve verification consistency, ensuring uniform security across distributed centers.
Threat / Challenge:
Attackers now use automated AI pipelines to generate thousands of voice and video spoofs quickly. This leads to scaled fraud operations targeting onboarding pipelines, financial workflows, support centers, and communication channels. Organizations struggle because detection mechanisms often cannot keep pace with attacker automation. Compliance and audit teams face mounting pressure to defend identity-proofing reliability.
How the Service Mitigates This Threat
- High-volume spoof testing exposes system scaling weaknesses, helping organizations prepare for automated attack patterns.
- Model benchmarking guides adoption of more robust anti-spoofing vendors, improving detection consistency under load.
- Control optimization reduces acceptance of bulk synthetic submissions, protecting onboarding, KYC, and transaction workflows.
- Strategic governance recommendations add layered authentication, making automated attacks less effective.
- Continuous testing programs sustain long-term resilience, ensuring defenses evolve with attacker capabilities.
BLOGS & ARTICLES
Why modern enterprises must prepare for synthetic media attacks as
deepfakes rapidly outpace traditional security and fraud controls.
Enterprise Cybersecurity & Social Engineering Defense Industry
How Deepfake-Assisted Social Engineering Is Becoming the Biggest Enterprise Weakness
Read FurtherDigital Identity Security & Fraud Prevention Industry
AI-Generated Synthetic Identities: The Silent Threat That Will Redefine Fraud in 2025–2030
Read FurtherCritical Infrastructure & Operational Technology (OT) Security Industry
Understanding Deepfake Risks in Control Rooms and Remote Maintenance Channels
Read FurtherDigital Trust & Communication Security Industry
Zero Trust for Human Communication: Why Organizations Must Treat Voices and Videos as Untrusted Inputs
Read FurtherFREQUENTLY ASKED QUESTION
Helping you quickly find answers to the critical questions that matter
most in evaluating our cybersecurity services.
CODEC NETWORKS OTHER RELATED SERVICES
Codec Networks “Offers end-to-end defensive capabilities that complement deepfake testing and fortify enterprise security
across digital, operational, and communication channels.
-
Simulates crypto-focused social engineering attacks including fake wallet deployments and NFT scams. This testing assesses user awareness and organizational resilience against phishing targeting digital assets. It evaluates incident response capabilities for crypto-related fraud and unauthorized access.
-
Evaluates organizational approval workflows for vulnerabilities enabling unauthorized process circumvention. This testing identifies weaknesses in multi-party authorization, segregation of duties, and critical transaction validation. It ensures process integrity by uncovering exploitable paths leading to unauthorized actions or financial losses.
-
Evaluates identity and access management controls against bypass techniques like SIM swapping and OTP interception. Testing simulates real-world attacks targeting authentication mechanisms including credential stuffing and session hijacking. This ensures multi-factor authentication implementations resist sophisticated evasion methods.
-
Simulates malicious insider scenarios including data theft and privilege abuse to evaluate internal controls. This assessment tests detection capabilities against unauthorized data exfiltration, lateral movement, and privilege escalation. It validates monitoring systems for identifying suspicious employee or compromised account activities.
-
Emulates advanced persistent threat tactics to evaluate organizational detection and response capabilities. This simulation replicates sophisticated adversary behaviors including stealthy persistence, lateral movement, and data exfiltration. It validates security controls against targeted attacks designed to evade traditional defenses.
Simulates crypto-focused social engineering attacks including fake wallet deployments and NFT scams. This testing assesses user awareness and organizational resilience against phishing targeting digital assets. It evaluates incident response capabilities for crypto-related fraud and unauthorized access.
Evaluates organizational approval workflows for vulnerabilities enabling unauthorized process circumvention. This testing identifies weaknesses in multi-party authorization, segregation of duties, and critical transaction validation. It ensures process integrity by uncovering exploitable paths leading to unauthorized actions or financial losses.
Evaluates identity and access management controls against bypass techniques like SIM swapping and OTP interception. Testing simulates real-world attacks targeting authentication mechanisms including credential stuffing and session hijacking. This ensures multi-factor authentication implementations resist sophisticated evasion methods.
Simulates malicious insider scenarios including data theft and privilege abuse to evaluate internal controls. This assessment tests detection capabilities against unauthorized data exfiltration, lateral movement, and privilege escalation. It validates monitoring systems for identifying suspicious employee or compromised account activities.
Emulates advanced persistent threat tactics to evaluate organizational detection and response capabilities. This simulation replicates sophisticated adversary behaviors including stealthy persistence, lateral movement, and data exfiltration. It validates security controls against targeted attacks designed to evade traditional defenses.