A. Service Scope and Client Fit
A1We already have SIEM and EDR tools. Why do we need a SOC?
Tools generate alerts; people and processes turn them into detection and response. Many organisations own good tools that nobody watches at night or that were never tuned. Codec Networks' SOC monitors, triages and responds using your tools or its own.
A2Do you work with our existing tools?
Yes. Codec Networks is tool-neutral and works with the main SIEM, EDR/XDR and SOAR platforms. Where a client has none, Codec Networks can provide them as part of the service.
A3What is the difference between a SOC and threat hunting?
The SOC responds to alerts from detection rules. Threat hunting looks for attackers that rules have missed, using hypotheses drawn from threat intelligence.
A4Why does the Board need SOC reporting?
Because directors must oversee cyber risk, and the SOC is where risk becomes visible. A short quarterly pack with KPIs, incidents and test results lets the Board judge whether security is working.
A5Is a red team exercise safe for our business?
Yes, when planned properly. Codec Networks agrees objectives, scope, rules of engagement and safety controls in writing, and deconflicts with your team so that business operations are protected.
A6Why monitor the dark web?
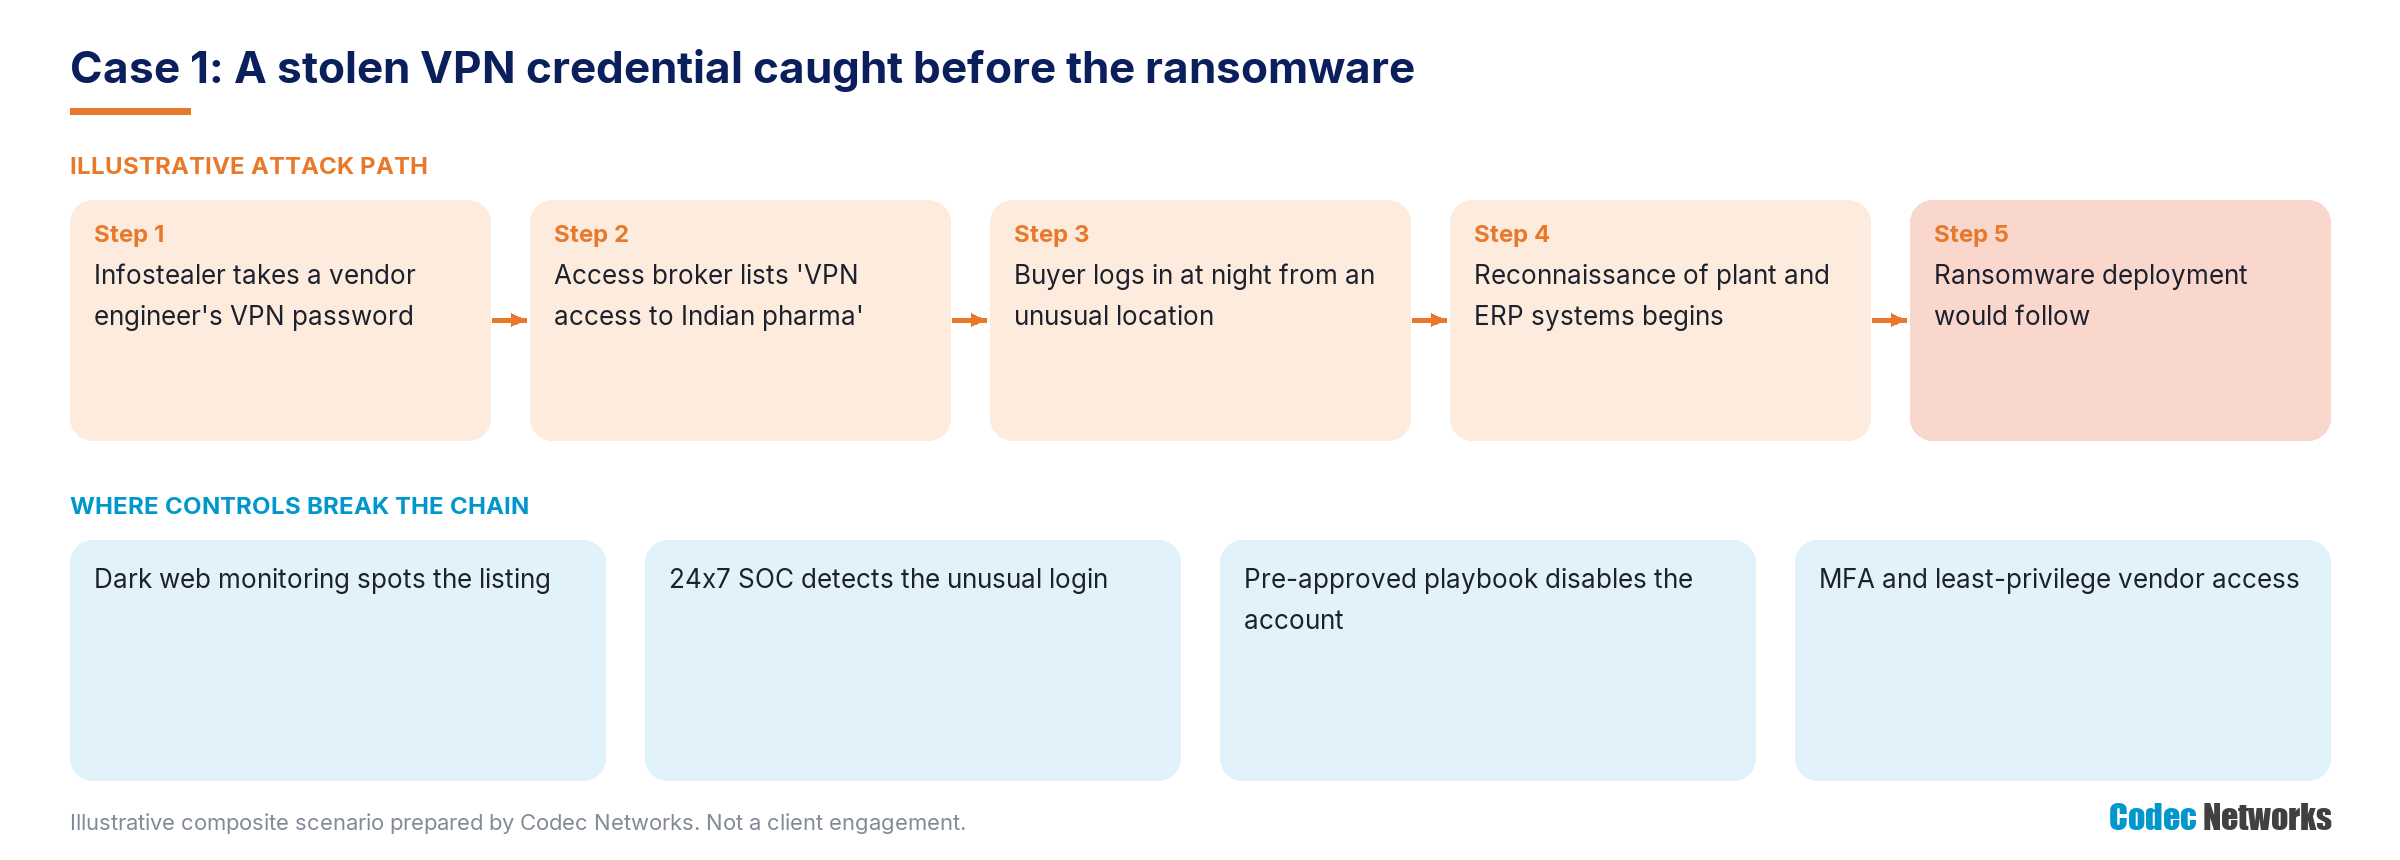
Because stolen credentials and access to company networks are often sold there before an attack. Finding them early lets you reset accounts and close access first.
A7How does cyber fit into ESG reporting?
Investors and regulators treat cyber security and data privacy as governance and social topics. In India, SEBI's BRSR includes cyber security and data privacy indicators, such as data breaches, for the top 1,000 listed companies.
A8Can you cover operational technology as well as IT?
Yes. Codec Networks can monitor OT networks with suitable sensors and use cases, separated from IT, and include OT in hunts and readiness tests with the owner's approval.
B. Standards, Laws and Regulatory Alignment
B1What logs does CERT-In require us to keep?
As general information: CERT-In's Directions of 28 April 2022 require service providers, intermediaries, data centres, body corporates and government organisations to maintain ICT system logs for 180 days within India and to synchronise clocks. Codec Networks designs log retention to meet this.
B2How fast must incidents be reported?
As general information: CERT-In requires specified incidents to be reported within six hours of noticing them; India's Telecom Cyber Security Rules 2024 require telecom entities to report within six hours of becoming aware; and SEC registrants must disclose material incidents within four business days. The SOC provides the facts quickly.
B3Does SEBI expect regulated entities to have a SOC?
As general information: SEBI's CSCRF of 20 August 2024 sets security operations and monitoring expectations by category of regulated entity, with options such as a market SOC for smaller entities. Codec Networks confirms your category and what applies.
B4What did RBI's 2016 framework say about SOCs?
As general information: RBI's Cyber Security Framework in Banks (RBI/2015-16/418, 2 June 2016) set expectations for continuous surveillance through a cyber security operations centre. Codec Networks' SOC can support banks and other entities against these expectations.
B5What cyber data do listed companies disclose in BRSR?
As general information: SEBI's BRSR circular of 10 May 2021 (SEBI/HO/CFD/CMD-2/P/CIR/2021/562) includes, under Principle 9, indicators on cyber security and data privacy, such as the number of data breaches and those involving customers' personal information. Your secretarial team confirms the current format.
B6Which frameworks do you use for KPIs?
NIST CSF 2.0, NIST SP 800-55 and ISO/IEC 27004 for measurement, with MITRE ATT&CK for detection coverage.
B7Which red team frameworks do you follow?
Intelligence-led approaches such as TIBER-EU and CBEST practice, with techniques mapped to MITRE ATT&CK and testing practice from NIST SP 800-115 and PTES.
B8Does the DPDP Act affect SOC operations?
Yes. The SOC handles personal data in logs, so it must be processed lawfully and protected; and breaches the SOC detects may require intimation to the Data Protection Board and affected individuals.
C. Engagement Approach and Delivery
C1How long does onboarding take?
Typically two to six weeks, depending on the number of log sources, tools and approvals. Monitoring starts on priority systems first.
C2Where is our data stored?
Logs are stored in India to meet CERT-In requirements, in Codec Networks' ISO/IEC 27001:2022 certified environment or the client's own platform, as agreed.
C3Who decides on containment actions?
The client. Codec Networks recommends actions and, where the client has pre-approved them, can take agreed steps such as isolating an endpoint or disabling an account.
C4How do you reduce false positives?
By tuning use cases to the client's environment, enriching alerts with context and automating routine checks through SOAR playbooks.
C5How are dark web findings acted on?
Validated findings become SOC tickets: password resets, session revocation, blocking or investigation, with the owner informed.
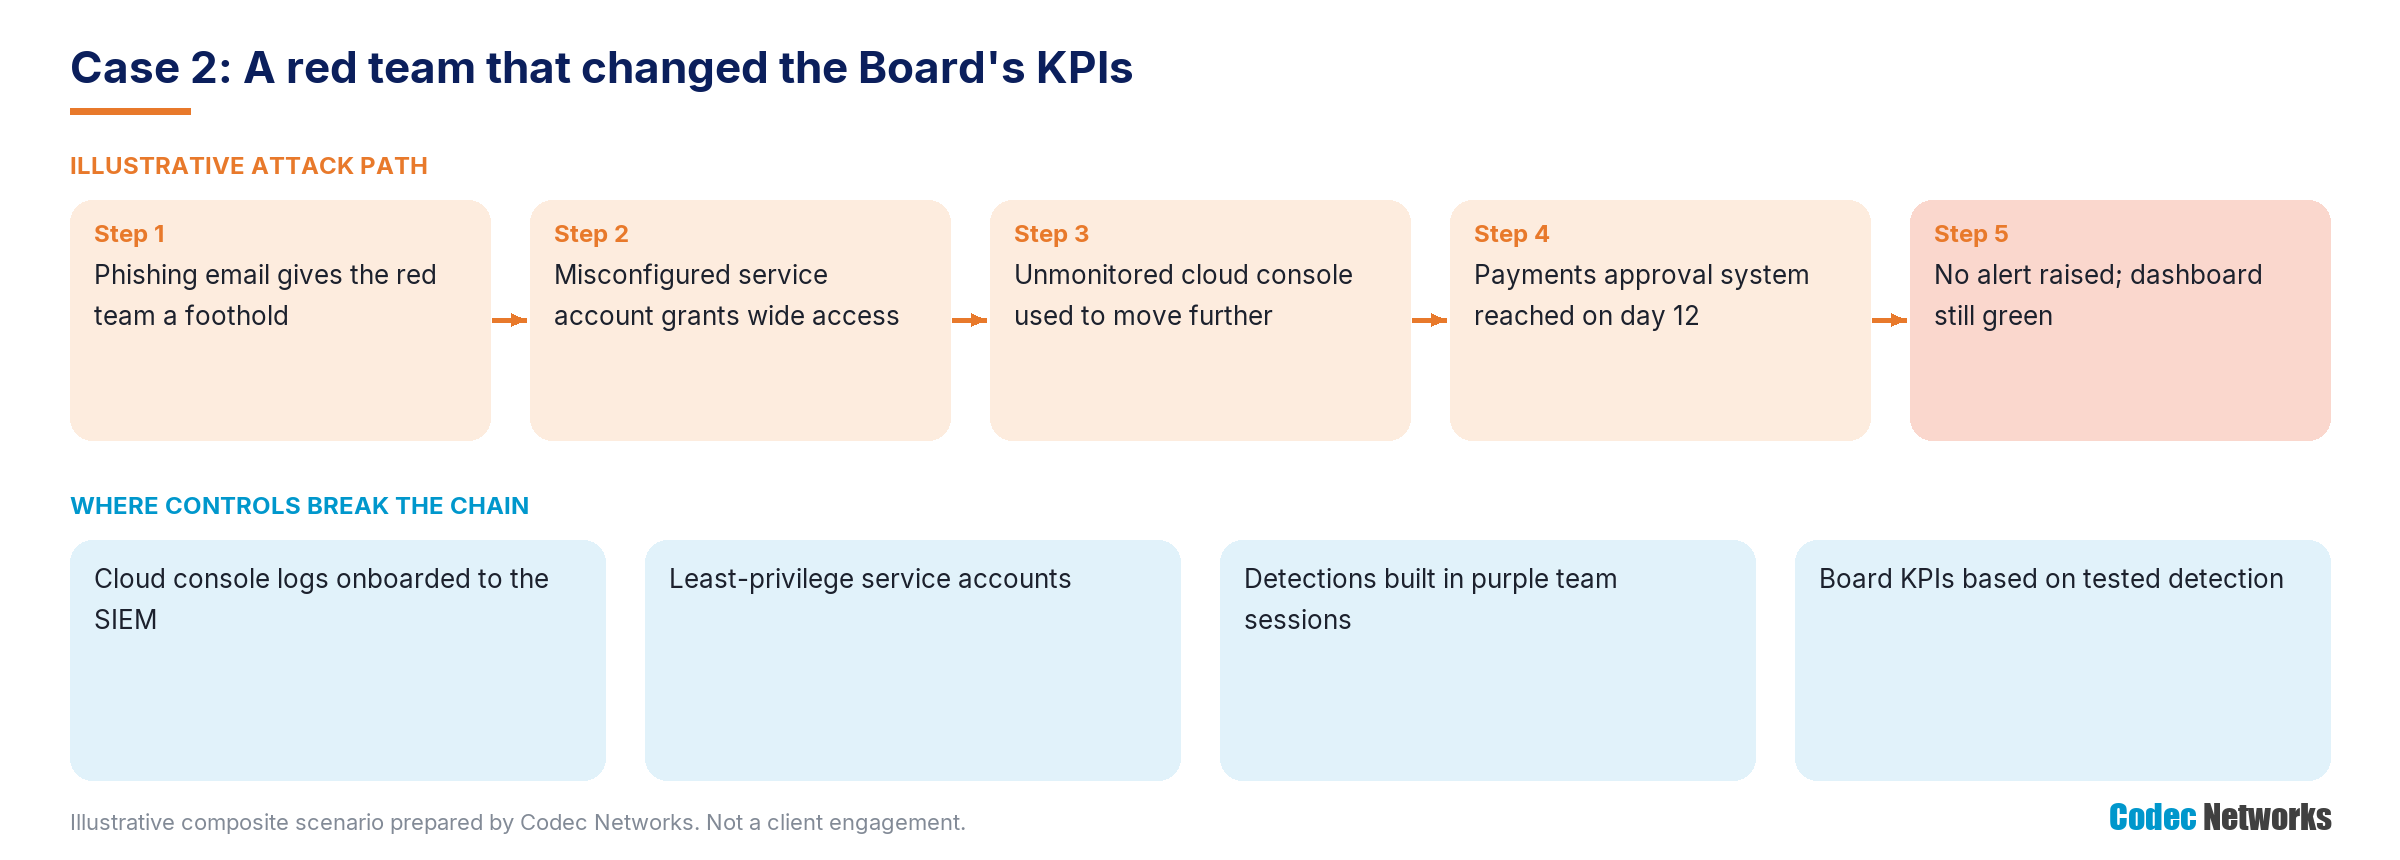
C6How is a red team exercise run?
Objectives and rules of engagement are agreed, intelligence shapes the scenario, the red team emulates the adversary to the objective, and a purple team session improves detections afterwards.
C7What does a Board pack contain?
Top threats, significant incidents, KPIs against targets, hunt and red team results, dark web exposure and decisions required, on a few pages.
C8How do you prepare disclosure metrics?
By defining each metric, reconciling it with SOC and privacy records, keeping evidence and drafting text for your secretarial, legal and sustainability teams to review.
D. Commercials, Timelines and Effort
D1How is the SOC priced?
Monthly, based on log sources, event volume, coverage hours and reporting. Document 7 gives indicative bands from about ₹2 lakh a month for small business-hours coverage to ₹50 lakh a month for large 24x7 estates.
D2Are SIEM and EDR licences included?
Not by default. Third-party licences are listed separately, or Codec Networks can provide platforms within the service where agreed.
D3Can we start with business hours and move to 24x7?
Yes. Many clients start with business-hours or extended coverage and move to 24x7 as their programme matures.
D4How much does a red team exercise cost?
Typically from ₹10 lakh to ₹80 lakh depending on objectives, scope, techniques and duration, with smaller assumed-breach exercises at the lower end.
D5Is dark web monitoring priced separately?
It can be bought alone from about ₹1 lakh a month, or included in SOC bundles.
D6Do bundles cost less?
Yes. SOC Starter, SOC Professional and SOC Enterprise cost less than their parts because the log platform, use cases and reporting are shared.
D7Is there a minimum term?
Managed SOC services usually have an initial term so that onboarding and tuning pay off; terms are set out in the proposal.
D8Can you work alongside our in-house team?
Yes. A co-managed SOC uses your tools and staff with Codec Networks analysts covering shifts, hunting or specialist skills, priced per shift or analyst.
E. Reporting, Evidence and Ongoing Support
E1Which KPIs will the Board see?
Typically mean time to detect and respond, coverage of critical assets and log sources, incidents by severity, dark web exposure, test results and trends against targets.
E2How do you prove the SOC is working?
Through detection tests, hunts and red team exercises that show which techniques are detected, and through KPI trends over time.
E3What evidence do auditors and regulators get?
Log retention records, incident tickets and reports, use-case catalogues, test reports and KPI histories.
E4How often are use cases reviewed?
Continuously as threats change, with a formal coverage review each quarter.
E5What happens in a major incident?
The SOC escalates immediately, guides containment, provides facts for CERT-In and other reports and hands over to Codec Networks' forensic and incident response team where needed.
E6Can the SOC support cyber insurance?
Yes. Monitoring evidence, KPIs and test results help answer underwriting questions and support claims with facts.
E7Will you help us report cyber metrics each year?
Yes. Under a retainer, Codec Networks supports quarterly governance reports and the annual BRSR and sustainability cycle.
E8How do you keep improving?
Through quarterly service reviews, annual test plans, new use cases for emerging threats and updates for new rules.