

Resources Categories
INDUSTRY FACT FILE · AI, ANALYTICS & AUTOMATION
Market Landscape and the Drivers of AI Security and Governance Demand
The business, technology, regulatory, legal and statutory forces that create AI security, governance and assurance work for AI builders and adopters.
|
In this document 1. Market landscape 2. Business drivers 3. Technology drivers 4. Regulatory drivers: India's AI guidelines, IT Rules, DPDP and sector rules 5. Legal and statutory drivers 6. How the drivers differ by player type 7. What this means for buyers and for Codec Networks |
1. Market landscape
India's AI ecosystem combines government-backed initiatives such as the IndiaAI Mission, a fast-growing start-up community and large-scale enterprise adoption in BFSI, healthcare, retail and public services. As AI moves into customer-facing and decision-making roles, buyers, Boards and regulators increasingly expect evidence that AI systems are secure, private and governed.
|
Nov 2025 India AI Governance Guidelines |
20 Feb 2026 Synthetic-content IT Rules in force |
Dec 2023 ISO/IEC 42001 published |
May 2027 Most DPDP obligations take effect |
|
Market segment |
Landscape and buying behaviour |
Cybersecurity opportunity |
|
AI product start-ups |
Fast iteration, enterprise sales ambitions |
AI security testing, governance packs for buyers |
|
Enterprise AI adopters |
Many pilots moving to production |
AI usage policies, red teaming, DLP |
|
BFSI and regulated adopters |
High scrutiny of AI decisions |
Model risk and governance programmes |
|
AI platforms and analytics |
Data-heavy, multi-customer |
Leakage, isolation and supply-chain reviews |
2. Business drivers
|
Business driver |
Buying trigger |
Relevant services |
|
Enterprise sales |
Buyers send AI-specific security questionnaires |
AI test reports, governance evidence |
|
Board scrutiny |
Boards ask about AI risk |
AI risk registers and briefings |
|
Liability and brand |
Wrong or harmful AI answers |
Output safety testing |
|
Fraud prevention |
Deepfake and AI-enabled scams |
Verification controls and simulations |
|
Regulatory expectations |
Sector regulators issue AI guidance |
Governance aligned to frameworks |
3. Technology drivers
|
Technology driver |
Exposure created |
Codec Networks opportunity |
|
LLM applications |
Prompt injection and jailbreaks |
AI/LLM security testing |
|
RAG pipelines |
Data leakage across users |
Retrieval authorisation testing |
|
Agents |
Unsafe autonomous actions |
Agent security reviews |
|
Open models |
Malicious model files |
Model supply-chain review |
|
Synthetic media |
Impersonation fraud |
Deepfake awareness and controls |
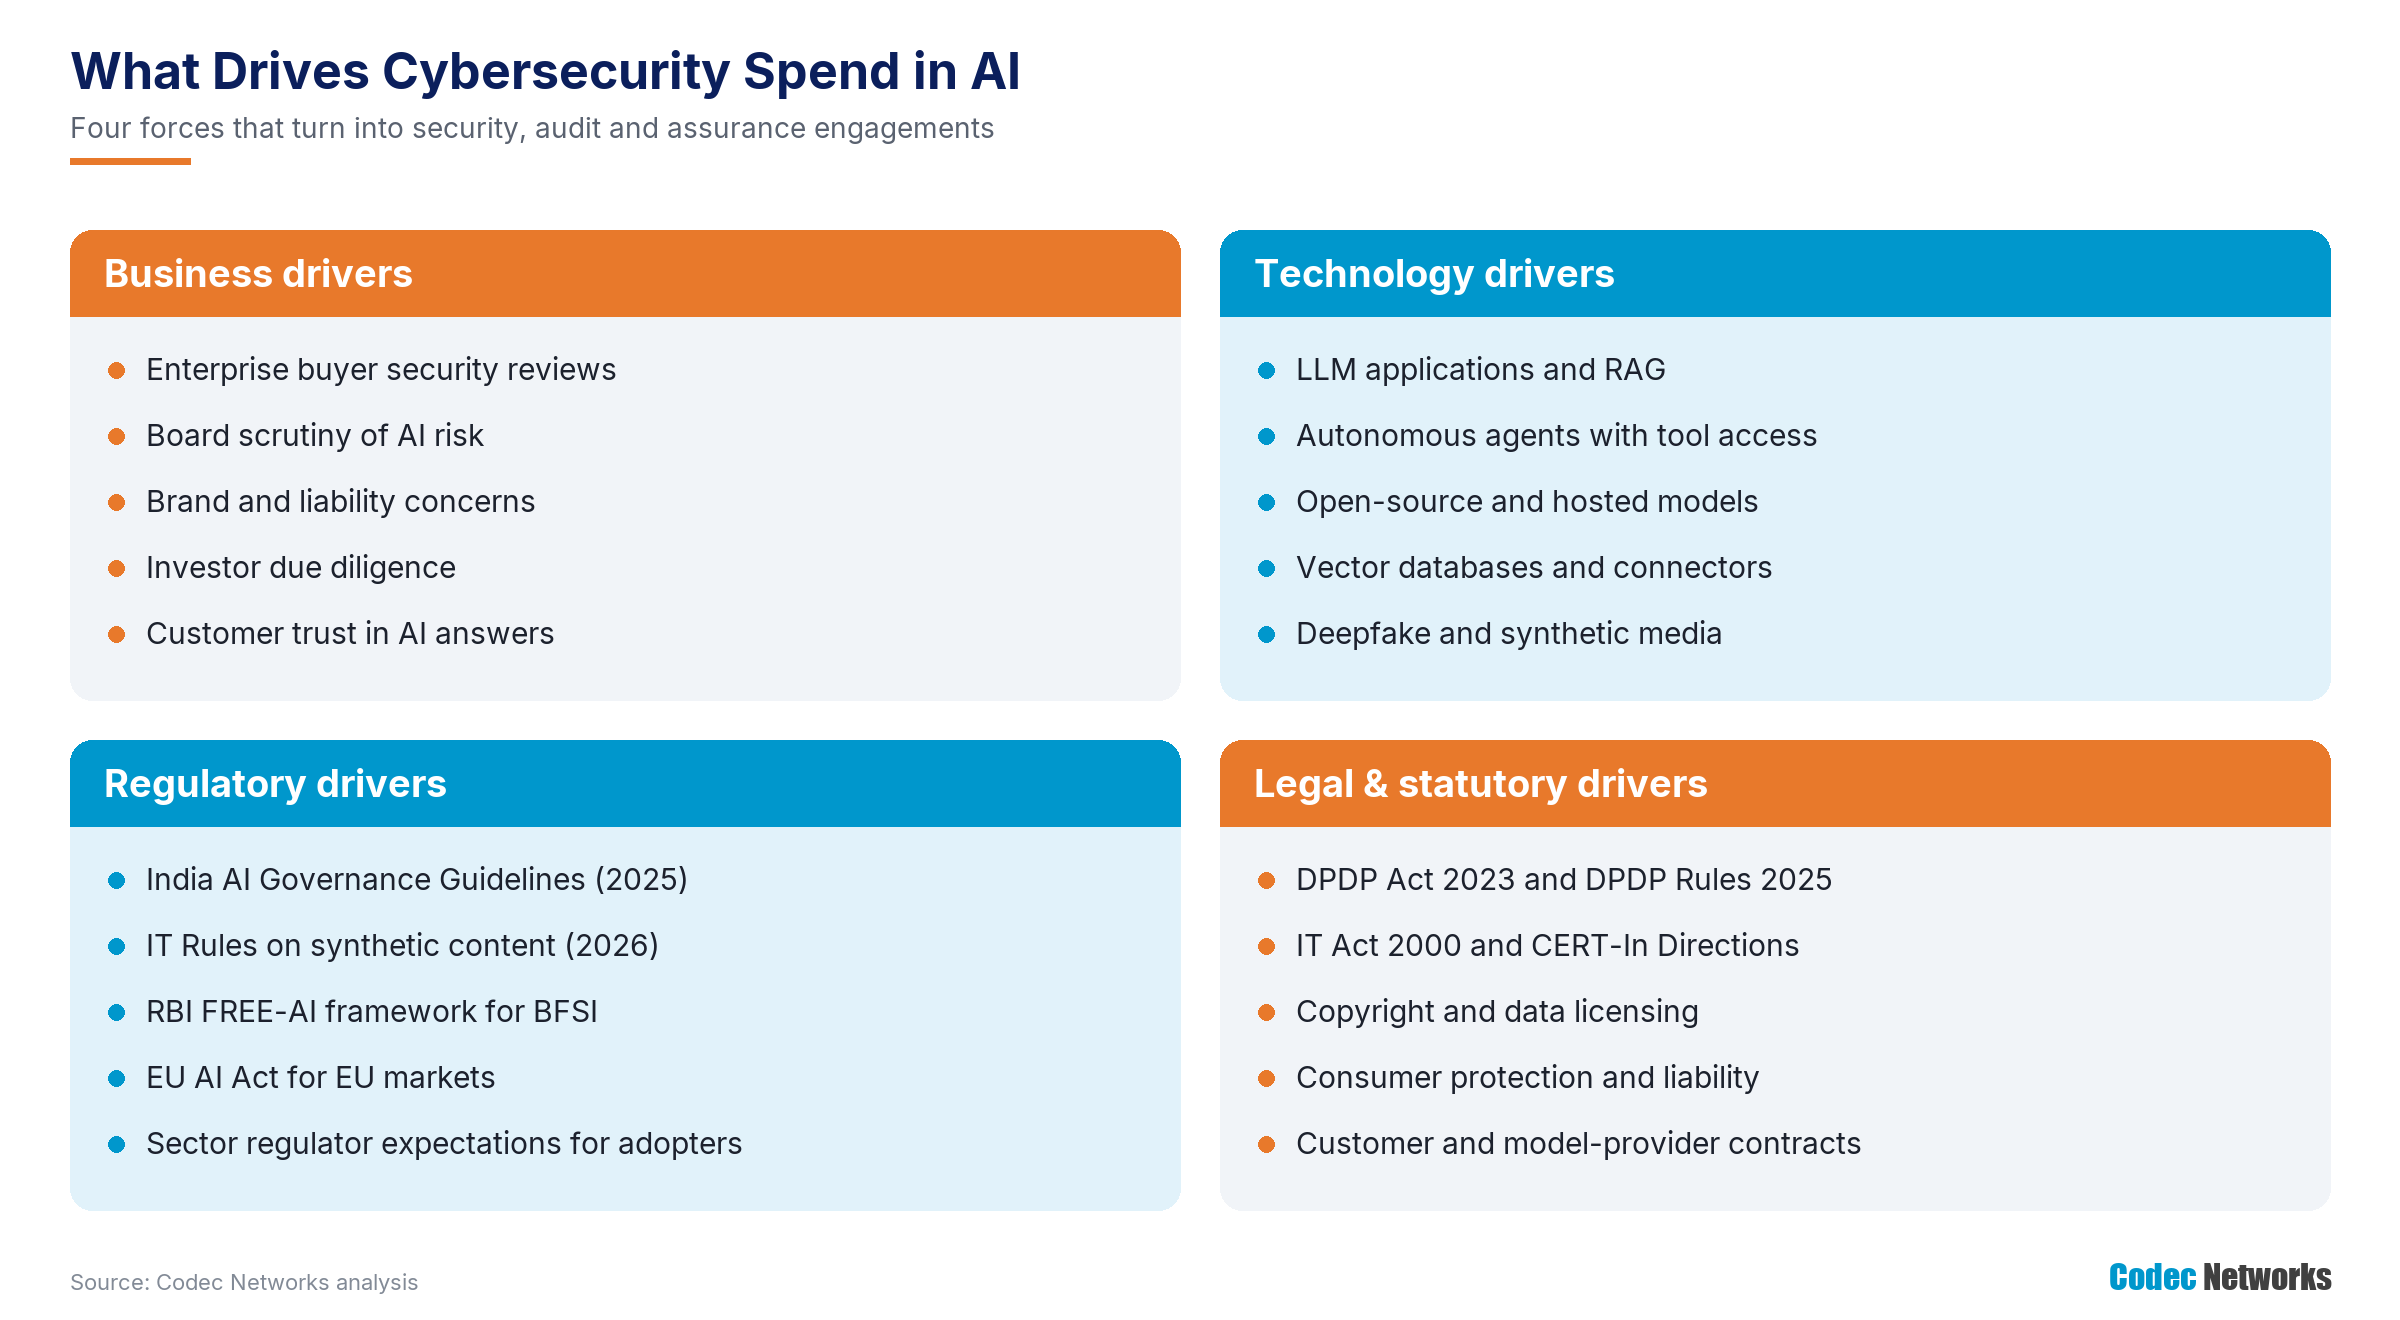
Figure 3: The four groups of drivers behind AI security and governance spending.
4. Regulatory drivers: India's AI guidelines, IT Rules, DPDP and sector rules
|
Instrument |
Key requirements |
|
India AI Governance Guidelines (November 2025) |
Principles-based governance relying on existing laws and sector regulators |
|
IT Rules amendment (in force 20 February 2026) |
Labelling of synthetically generated information and faster takedowns for intermediaries |
|
DPDP Act 2023 and Rules 2025 |
Lawful processing of personal data in training and use; most obligations from May 2027 |
|
RBI FREE-AI framework (2025) |
Responsible and ethical AI enablement in the financial sector |
|
EU AI Act and ISO/IEC 42001 |
Phased risk-based obligations for EU markets; certifiable AI management system standard |
|
Confirm applicability Obligations differ for builders, hosts, intermediaries and adopters. Confirm against the official texts. |
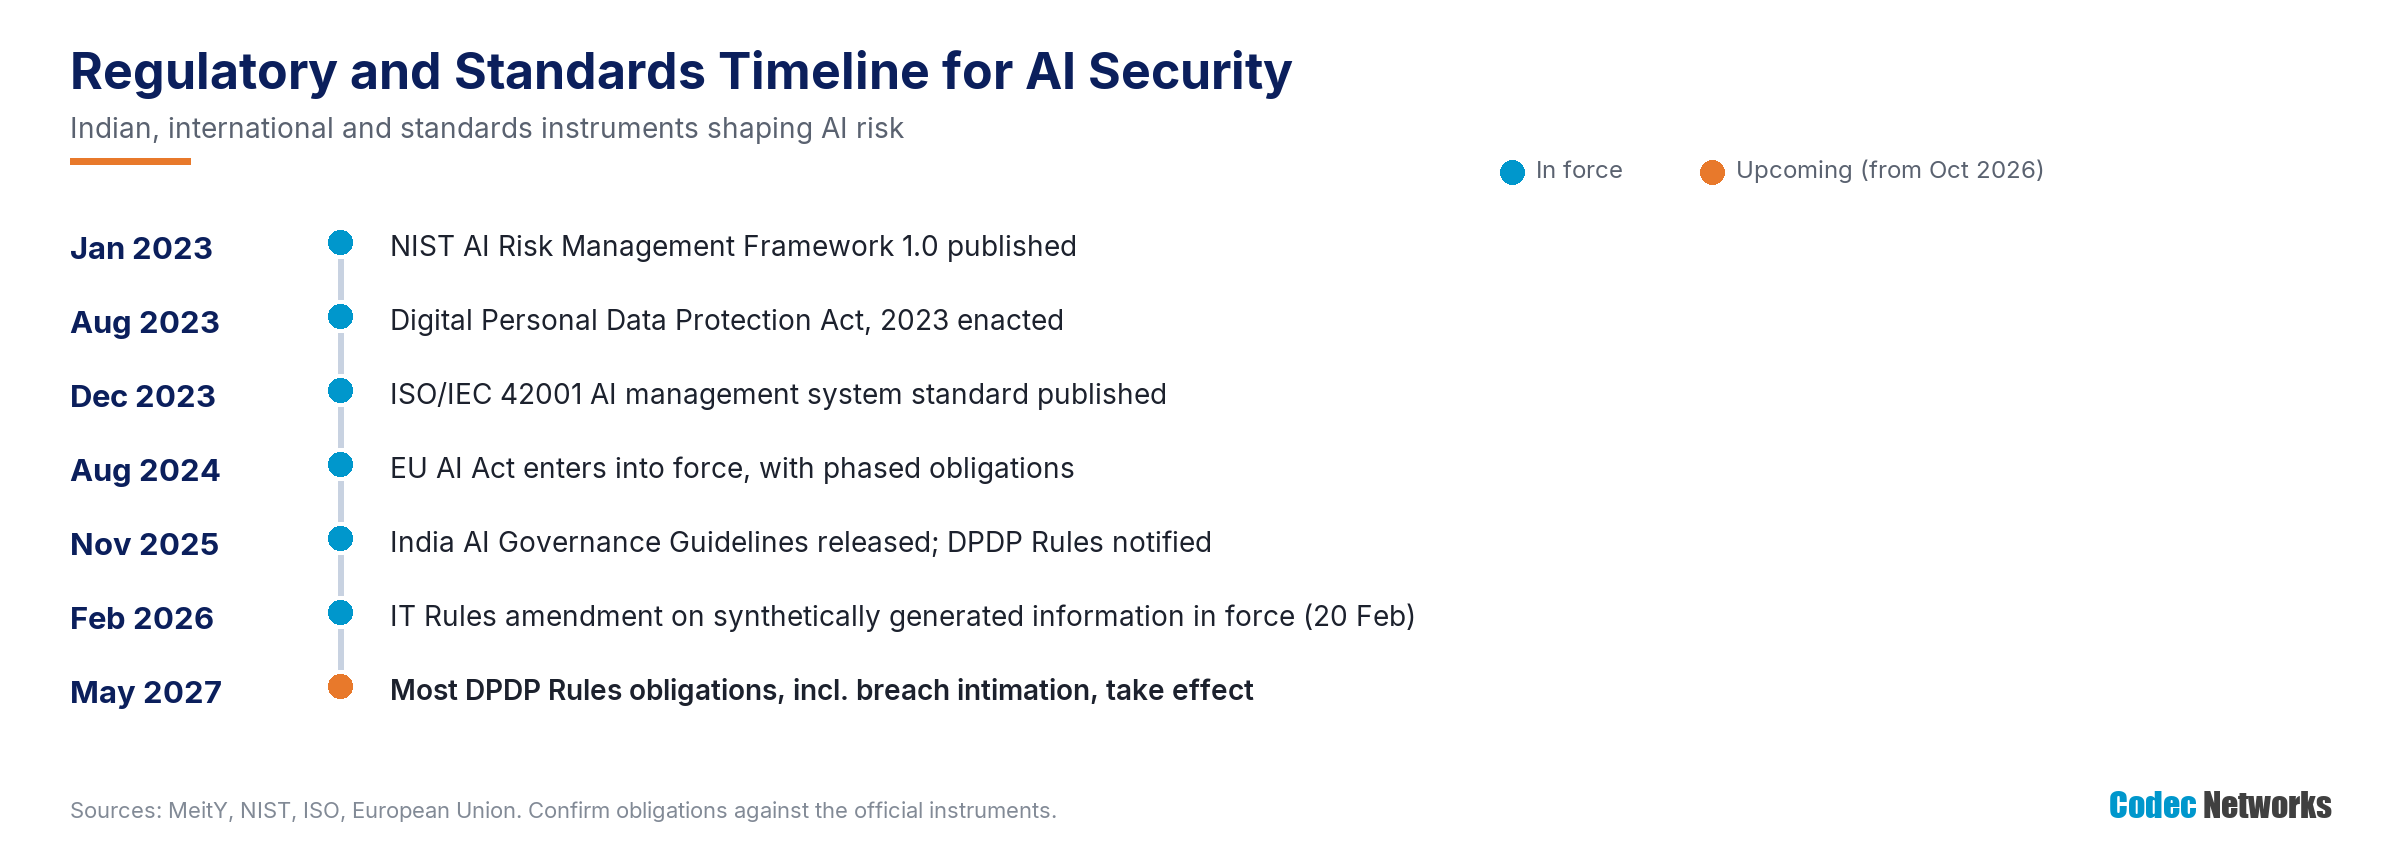
Figure 4: Regulatory and standards timeline for AI security, as of October 2026.
5. Legal and statutory drivers
|
Law or obligation |
Relevance |
Demand created |
|
DPDP Act, 2023 and Rules, 2025 |
Personal data in training, prompts and outputs |
Privacy programmes for AI |
|
IT Act, 2000 and IT Rules |
Intermediary duties, including synthetic content |
Labelling and takedown processes |
|
Consumer protection law |
Misleading or harmful AI outputs |
Output safety testing |
|
Copyright and data licensing |
Rights to training data |
Data provenance reviews |
|
Contracts |
Customer and model-provider terms |
Assurance evidence |
6. How the drivers differ by player type
|
Player type |
Dominant business drivers |
Dominant technology drivers |
Principal regulatory drivers |
|
AI product firms |
Enterprise sales, IP |
Models, training pipelines |
DPDP, IT Rules, EU AI Act |
|
Agent developers |
Customer trust |
Tools and permissions |
DPDP, consumer protection |
|
Enterprise adopters |
Productivity, risk |
Copilots, RAG |
Sector rules, DPDP |
|
BFSI adopters |
Regulatory confidence |
Decision models |
RBI FREE-AI, SEBI, IRDAI, DPDP |
7. What this means for buyers and for Codec Networks
|
Customer buying need |
Recommended offering |
Natural recurring engagement |
|
“Is our chatbot safe to launch?” |
AI/LLM security test |
Release-linked testing |
|
“Could our AI leak data?” |
Data leakage and retrieval testing |
Periodic leakage tests |
|
“What can our agents do?” |
Agent security review |
Continuous agent monitoring |
|
“We need AI governance.” |
ISO/IEC 42001 readiness and AI policy |
Annual governance review |
|
“Is our training data lawful?” |
DPDPA review for AI data |
Data governance programme |
Talk to Codec Networks
|
Contact Codec Networks Pvt. Ltd. New Delhi: 507, 5th Floor, New Delhi House, Barakhamba Road, Connaught Place, New Delhi – 110001 Gurugram: 707, 7th Floor, Silverton Tower, Golf Course Extension Road, Sector 50, Gurugram – 122018, Haryana Landline: 011 430 496 96 | 011 437 522 99 Mobile: +91 99716 76124 | +91 88007 88220 | +91 88003 31124 Email: mktg@codecnetworks.com Web: www.codecnetworks.com |
Note: This document is general industry guidance based on public information available as of October 2026. AI governance instruments are summarised from public sources. Confirm obligations against the official MeitY, CERT-In, sector-regulator and international texts before making compliance decisions.