

Resources Categories
INDUSTRY FACT FILE · DIGITAL IDENTITY, TRUST & ESIGN
Applicable Cybersecurity Services and Codec Networks Bundles for Digital Identity
How Codec Networks services and bundled service models help Aadhaar ecosystem entities, certifying authorities, eSign providers and KYC platforms resolve their threats and meet UIDAI, CCA, RBI KYC and CERT-In expectations.
|
In this document 1. Our approach 2. Mapping threats to services 3. Codec Networks service catalogue for the sector 4. Codec Networks bundles for the sector 5. Sector programmes built from the bundles 6. Packages: Foundation, Assurance and Continuous Resilience 7. Regulatory requirement-to-bundle mapping 8. Threat-to-bundle coverage matrix 9. Delivery methodology and deliverables 10. Why Codec Networks 11. Annex: indicative commercial ranges |
1. Our approach
Identity and trust providers need security that protects people as well as systems and that stands up in audits and disputes. Codec Networks works on four principles:
- Role first: every assessment starts from your role and agreements in the ecosystem, whether AUA, KUA, sub-AUA, ASA, enrolment agency, CA, ESP, ASP or KYC vendor, and the checklist or guideline that applies to it.
- Test the whole flow: devices, apps, APIs, vaults, HSMs, consent screens and logs are tested end to end, because identity fraud exploits the joins between components.
- Minimise and protect: Aadhaar numbers only in the vault, biometrics never stored, tokens elsewhere and identity data kept only as long as it is needed.
- Prove it: findings mapped to the Aadhaar Act and Regulations, UIDAI checklists and Circular 14 of 2025, CCA eSign guidelines, RBI KYC Directions, CERT-In's Directions and the DPDP Act.
2. Mapping threats to services
The table maps the 18 threats identified in Document 4 of this set to the Codec Networks services that help mitigate them.
|
Threat / challenge |
Applicable Codec Networks services |
Intended outcome |
|
Cloned and spoofed biometrics |
Registered device and agent app testing, liveness review, anomaly monitoring |
Spoofs that fail |
|
Replay of stored biometrics or authentication data |
Device integration and AUA server testing, encryption and replay checks |
Captures that cannot be reused |
|
Deepfake and injected video in video-KYC |
Deepfake and injection testing, app attestation review, KYC audit |
Real faces only |
|
Forged documents and synthetic identities |
Document verification testing, fraud rule review, monitoring |
Fewer false identities |
|
Enrolment and update operator misuse |
Operator access review, centre and kit assessment, monitoring |
Accountable operators |
|
Aadhaar numbers stored outside the vault |
Data discovery, vault and tokenisation review, masking |
One protected copy |
|
Authentication and e-KYC API abuse |
API security testing, authorisation and rate-limit review |
APIs that resist abuse |
|
Mobile app and SDK tampering |
Mobile app and SDK testing, root and emulator detection review |
Apps that cannot be bent |
|
Signing without informed consent |
ASP assessment, document-binding and consent tests |
Signatures that hold up |
|
Signing key, HSM and CA compromise |
HSM and key management review, CA infrastructure VAPT |
Keys that stay secret |
|
Registration authority and certificate issuance fraud |
RA control review, PAM, dual control, issuance monitoring |
Certificates only for the right people |
|
OTP and consent social engineering |
Consent flow review, customer awareness, fraud monitoring |
Residents who are hard to trick |
|
Account takeover and SIM-swap linked fraud |
Account recovery testing, risk signals, monitoring |
Fewer hijacked identities |
|
Sub-AUA, vendor and partner compromise |
Sub-AUA and vendor assessments, contract and access reviews |
Partners held to account |
|
Insider misuse of identity data |
Privileged access review, activity monitoring, investigations |
Data used only for its purpose |
|
DigiLocker and document-sharing API misuse |
DigiLocker integration testing, consent and retention review |
Only the documents needed |
|
Ransomware and outages on identity services |
Infrastructure VAPT, backup and failover testing, SOC |
Services that keep running |
|
Weak logs, audit trails and 6-hour reporting |
Log architecture review, managed SOC, IR retainer |
Provable trails, on-time reporting |
3. Codec Networks service catalogue for the sector
|
Service line |
Sector-relevant services |
|
Security Vulnerability Assessment & Penetration Testing |
Authentication stacks, AUA and KUA servers, ASA networks, enrolment kits and centres, CA infrastructure, external attack surface, red teaming of issuance and onboarding |
|
Application, API & mobile security |
Authentication, e-KYC, eSign and DigiLocker API testing; ASP application assessments; mobile apps and SDKs; video-KYC applications |
|
Infrastructure, cloud & zero trust |
Aadhaar Data Vault and HSM architecture, key and token management, cloud hosting reviews, privileged access for vault, RA and CA administrators |
|
Information security audit & compliance |
Role-specific UIDAI IS audits against compliance checklists, CCA audit readiness for CAs and ESPs, CERT-In risk-based audits |
|
Identity fraud & KYC assurance |
Deepfake and injection testing, liveness and face-match reviews, document verification testing, consent and document-binding tests |
|
Supply chain & third-party risk |
Sub-AUA, agent network, ASP and KYC vendor assessments; contract and access reviews |
|
GRC & ISO/IEC 27001 |
ISMS implementation, policies and evidence for UIDAI and CCA audits, SOC 2 readiness for KYC platforms |
|
Data privacy & protection |
Aadhaar consent and purpose reviews, data discovery, DPDP programmes, retention and breach workflows |
|
24/7 Managed SOC & threat monitoring |
Authentication and e-KYC anomaly monitoring, issuance monitoring, vault and HSM access alerts, mule and takeover detection |
|
Cyber forensics & incident response |
Identity fraud investigations, data exposure response, dispute evidence reviews and CERT-In reporting support |
4. Codec Networks bundles for the sector
Eleven of the twelve bundles in the Codec Networks Bundled Service Models apply directly to Aadhaar ecosystem entities, certifying authorities, eSign providers and identity verification platforms; the Global Cyber Back-Office SPV Program (Bundle 12) is offered separately for international clients.
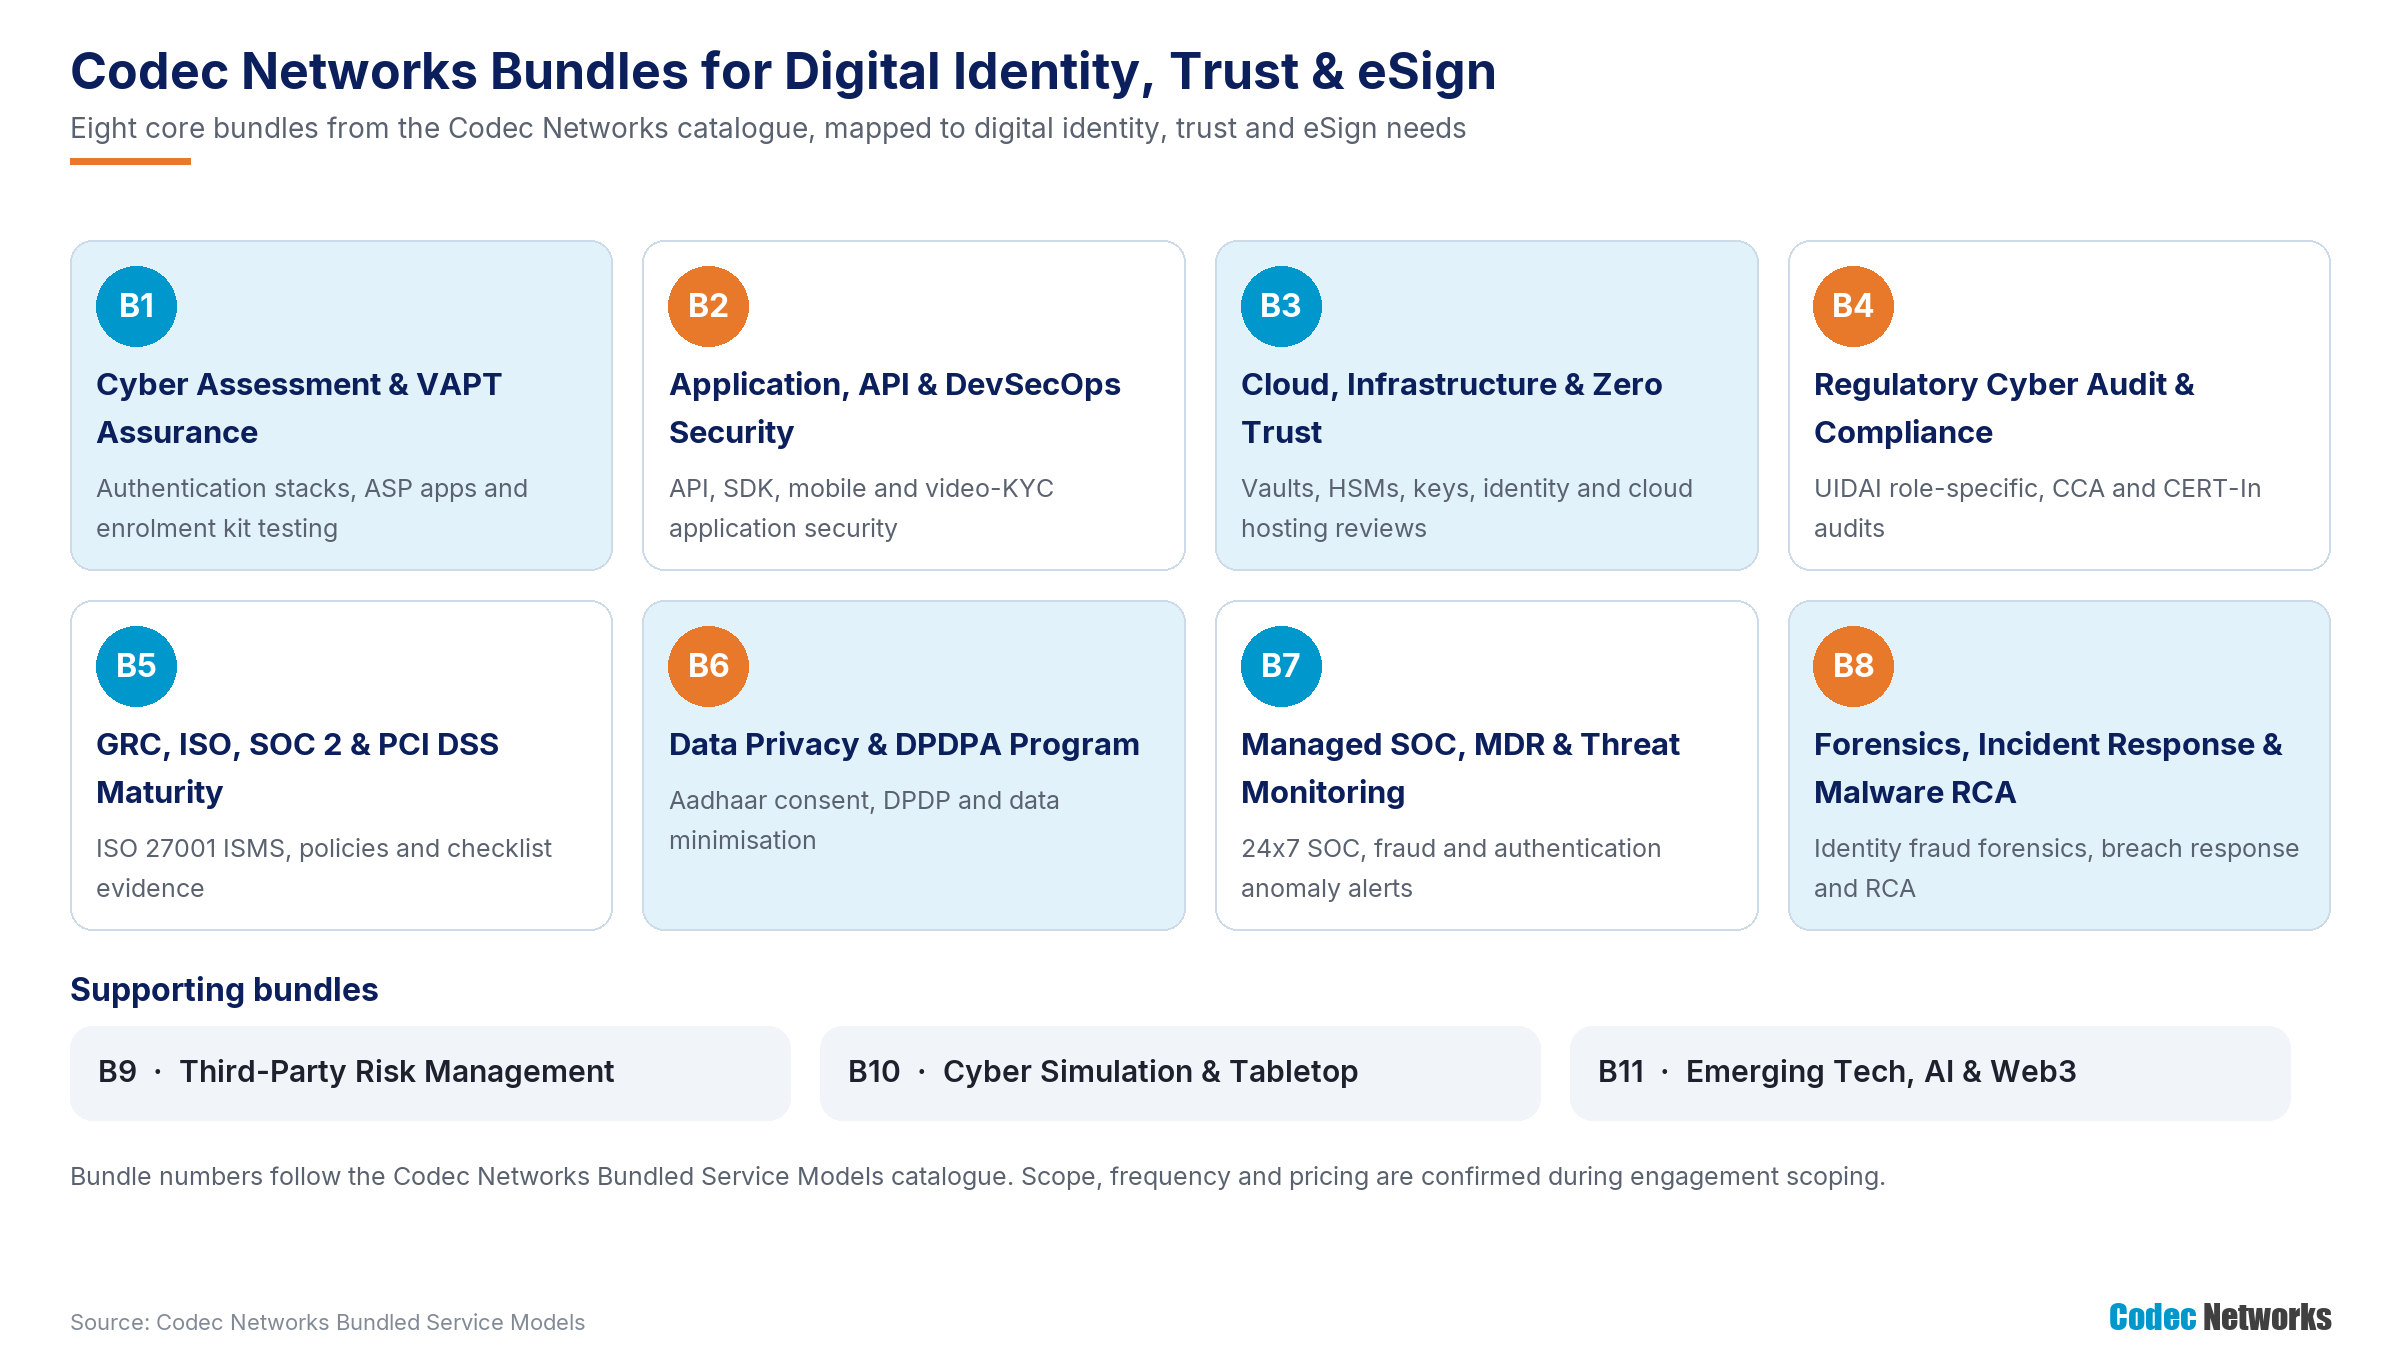
Figure 6: Codec Networks bundles applied to the sector.
|
Bundle |
Name |
Sector-relevant scope |
Best suited for |
Key deliverables |
|
B1 |
Cyber Assessment & VAPT Assurance Program |
Authentication stacks, enrolment kits, ASA networks, CA infrastructure and red teaming |
AUAs, ASAs, enrolment agencies, CAs and ESPs |
Assessment reports, retests and closure tracker |
|
B2 |
Application, API & DevSecOps Security Program |
Authentication, e-KYC, eSign and DigiLocker APIs, ASP apps, mobile apps and SDKs |
ASPs, sub-AUAs, KYC platforms and fintechs |
API and app reports, consent test results |
|
B3 |
Cloud, Infrastructure & Zero Trust Security Program |
Aadhaar Data Vault, HSMs, keys, tokens, cloud hosting and privileged access |
AUAs, KUAs, CAs and ESPs |
Architecture review and remediation roadmap |
|
B4 |
Regulatory Cybersecurity Audit & Compliance Assurance Program |
Role-specific UIDAI IS audits, CCA audit readiness, CERT-In audits |
Every requesting entity, ASA, CA and ESP |
Audit report, gap matrix, evidence tracker |
|
B5 |
GRC, ISO, SOC 2 & Cyber Maturity Program |
ISO/IEC 27001 ISMS, policies, SOC 2 readiness and checklist evidence |
KYC platforms, ASPs and service providers |
Maturity scorecard, policies, ISMS documents |
|
B6 |
Data Privacy, DPDPA & Data Protection Program |
Aadhaar consent, purpose limitation, data discovery and DPDP |
All organisations ahead of May 2027 |
Privacy gap assessment, data map, roadmap |
|
B7 |
Managed SOC, MDR & Continuous Threat Monitoring Program |
24x7 SOC for authentication, issuance, vault and fraud anomalies |
AUAs, KUAs, CAs, ESPs and KYC platforms |
SOC reports, MTTD/MTTR, incident records |
|
B8 |
Digital Forensics, Incident Response & Malware RCA Program |
Identity fraud, data exposure and dispute investigations and RCA |
Any organisation facing an incident or dispute |
Forensic report, RCA, reporting support |
|
B9 |
Third-Party Risk Management & Supply Chain Cyber Risk Program |
Sub-AUA, agent network, ASP and KYC vendor assurance |
AUAs, KUAs, ESPs and regulated entities |
Partner risk register and assessment reports |
|
B10 |
Cyber Simulation, Awareness, Tabletop & Crisis Readiness Program |
Fraud scenario exercises, awareness and crisis tabletops |
Leadership, operations, fraud and security teams |
Exercise reports and playbooks |
|
B11 |
Emerging Technology, AI, Web3 & Future Security Program |
Deepfake, liveness and AI face-match risk reviews |
Video-KYC, IDV platforms and their clients |
AI risk assessment and test evidence |
5. Sector programmes built from the bundles
Codec Networks packages the catalogue bundles into six digital identity, trust and eSign programmes.
|
Programme |
Built from bundles |
Challenges addressed |
|
UIDAI Role Audit Programme |
B4, B5, B1 |
Annual IS audits, checklist evidence, closure |
|
Vault, HSM & Data Minimisation |
B3, B6, B4 |
Vault-only storage, tokens, keys, data discovery |
|
eSign & ASP Onboarding Security |
B2, B1, B9 |
ASP assessments, consent and binding tests, ESP terms |
|
Video-KYC & Deepfake Assurance |
B11, B2, B7 |
Injection and liveness testing, fraud monitoring |
|
Trust Service Provider Assurance |
B3, B1, B4 |
CA, RA, HSM and issuance controls, CCA readiness |
|
Identity SOC & Fraud Response |
B7, B8, B10 |
Anomaly monitoring, investigations, six-hour reporting |
6. Packages: Foundation, Assurance and Continuous Resilience
|
Package element |
Foundation |
Assurance |
Continuous Resilience |
|
Typical organisation |
Sub-AUAs, ASPs and KYC start-ups |
AUAs, KUAs, lenders and IDV platforms |
ASAs, CAs, ESPs and large AUAs |
|
Testing |
B1 + B2: ASP and e-KYC API and app testing |
B1 + B2: authentication stack, app, SDK and video-KYC testing |
B1 + B2 + B10: infrastructure, issuance and red team testing |
|
Audit and GRC |
B4: UIDAI checklist gap review |
B4 + B5: annual UIDAI IS audit, ISO 27001 |
B4 + B5 + B9: UIDAI, CCA readiness and partner audits |
|
Architecture and privacy |
B6: Aadhaar data discovery and consent check |
B3 + B6: vault, HSM and cloud review, DPDP programme |
B3 + B6 + B11: key management, DPDP and AI risk reviews |
|
Monitoring and response |
IR retainer (B8) |
B7: managed SOC + B8 |
B7: SOC with issuance and fraud monitoring + B8 |
|
Reporting |
Partner and ESP evidence pack |
CISO and management reporting |
Board, UIDAI, CCA and client-ready reporting |
7. Regulatory requirement-to-bundle mapping
|
Requirement (source) |
How Codec Networks helps |
Bundle |
|
Annual audit of operations and systems by a certified IS auditor (Aadhaar Authentication Regulations 2021, Regulation 14(1)(h)) |
Role-specific UIDAI IS audit by a CERT-In empanelled team against the current checklist |
B4, B5 |
|
Aadhaar numbers and e-KYC data only in an Aadhaar Data Vault; keys in HSMs (UIDAI Circular 14 of 2025) |
Vault, HSM, tokenisation and cloud hosting review; data discovery |
B3, B6 |
|
No storage of core biometrics; registered devices (Aadhaar Act; UIDAI specifications) |
Device integration and replay testing, data discovery |
B1, B6 |
|
Informed consent and purpose limitation for authentication (Aadhaar Act) |
Consent flow review and privacy programme |
B6 |
|
Licensed CA empanelled as ESP after audit; ASP integration terms (IT Act Second Schedule; CCA) |
CA, RA and signing control reviews; ASP security assessments |
B4, B1, B2 |
|
V-CIP with liveness, spoof detection and face matching (RBI KYC Directions, 2025) |
Deepfake and injection testing, KYC process audit |
B11, B2, B4 |
|
Cyber incidents to CERT-In within six hours; 180-day logs in India (CERT-In Directions, 2022) |
Managed SOC, log architecture, IR retainer and reporting support |
B7, B8 |
|
Reasonable security safeguards and breach intimation (DPDP Act 2023 and Rules 2025) |
DPDP gap assessment, data maps, breach workflow |
B6, B8 |
|
Auditor eligibility and independence UIDAI's compliance checklist calls for the annual information systems audit of requesting entities to be carried out by a CERT-In empanelled auditor, and the CCA empanels its own auditors for CA and ESP audits. Codec Networks is CERT-In empanelled for information security auditing services and empanelled with NICSI for application audit and compliance services (start-up category); it confirms eligibility and independence against UIDAI's, the CCA's and the client's requirements in each proposal, and does not audit systems it has designed or operates. |
8. Threat-to-bundle coverage matrix
|
Threat / challenge |
Primary bundle |
Supporting bundles |
|
Cloned and spoofed biometrics |
B1 |
B7, B8 |
|
Replay of stored biometrics or authentication data |
B1 |
B4, B7 |
|
Deepfake and injected video in video-KYC |
B11 |
B2, B7 |
|
Forged documents and synthetic identities |
B11 |
B7, B8 |
|
Enrolment and update operator misuse |
B4 |
B3, B7 |
|
Aadhaar numbers stored outside the vault |
B6 |
B3, B4 |
|
Authentication and e-KYC API abuse |
B2 |
B1, B7 |
|
Mobile app and SDK tampering |
B2 |
B1 |
|
Signing without informed consent |
B2 |
B4, B6 |
|
Signing key, HSM and CA compromise |
B3 |
B1, B7 |
|
Registration authority and certificate issuance fraud |
B3 |
B7, B10 |
|
OTP and consent social engineering |
B10 |
B6, B7 |
|
Account takeover and SIM-swap linked fraud |
B7 |
B2, B8 |
|
Sub-AUA, vendor and partner compromise |
B9 |
B4, B7 |
|
Insider misuse of identity data |
B7 |
B3, B8 |
|
DigiLocker and document-sharing API misuse |
B2 |
B6 |
|
Ransomware and outages on identity services |
B3 |
B1, B7, B8 |
|
Weak logs, audit trails and 6-hour reporting |
B7 |
B8 |
“Primary” and “supporting” indicate suggested combinations, not guaranteed mitigation or complete coverage.
9. Delivery methodology and deliverables
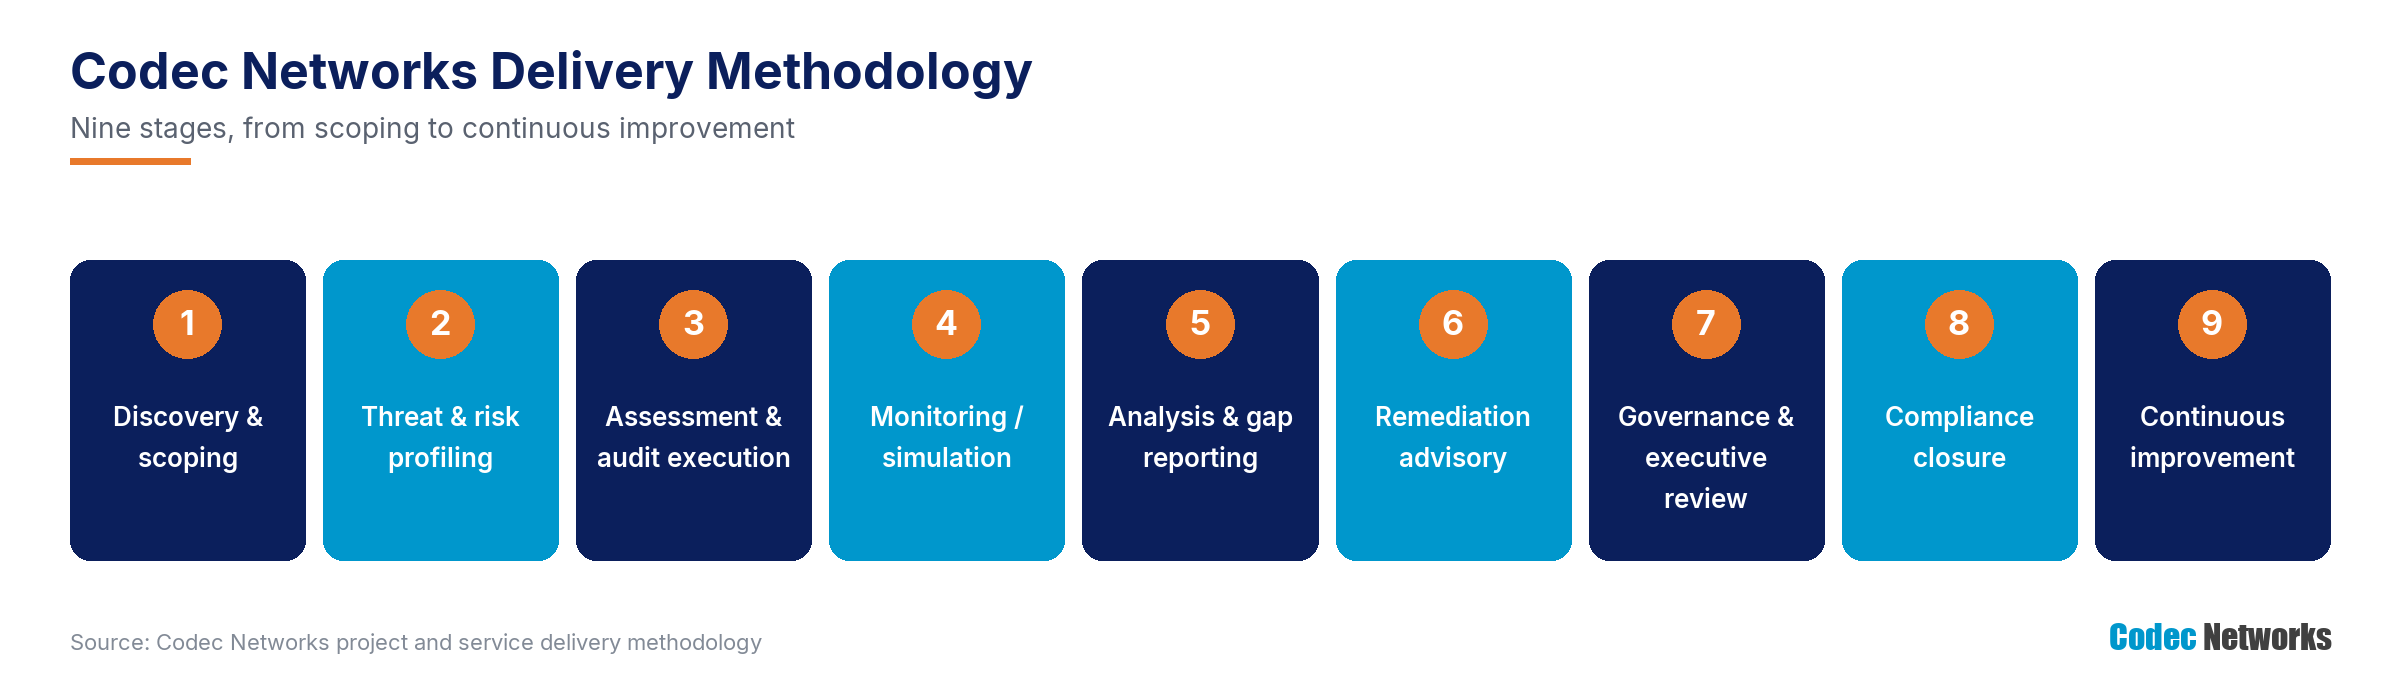
Figure 7: The Codec Networks delivery methodology.
Typical deliverables include role-specific UIDAI IS audit reports with gap matrices and closure trackers, Aadhaar Data Vault, HSM and cloud hosting review reports, data discovery results showing where Aadhaar numbers and e-KYC data sit, authentication stack, registered device and enrolment kit assessment reports with retests, API, mobile app and SDK test reports, ASP security assessment and consent and document-binding test results for ESP onboarding, CA, RA and key management review reports for CCA audit readiness, deepfake and injection test evidence for video-KYC, sub-AUA and vendor assessment reports, ISO 27001 and SOC 2 readiness reports, a DPDP gap assessment, forensic and dispute evidence reports with CERT-In reporting support, exercise reports and managed SOC reporting.
10. Why Codec Networks
- CERT-In empanelled for information security auditing services, and empanelled with NICSI for application audit and compliance services (start-up category).
- Certified to ISO 9001:2015, ISO/IEC 27001:2022 and ISO/IEC 20000-1:2018.
- Full stack: VAPT, regulatory audit, managed SOC, forensics, privacy and Board advisory from one partner, so findings, monitoring and closure stay connected.
- Identity-sector depth: AUA, KUA, sub-AUA, ASA, enrolment, CA, ESP, ASP and KYC platform environments assessed against the Aadhaar Act and Regulations, UIDAI's role-specific checklists and Circular 14 of 2025, CCA eSign guidelines, RBI KYC Directions, CERT-In's Directions and the DPDP Act, with authentication, KYC and signing flows tested end to end.
- Recognised frameworks and tools: OWASP ASVS/MASVS and API Top 10, MITRE ATT&CK, NIST CSF, ISO 27001 and PCI DSS; tools such as Burp Suite, Nessus, Metasploit, Prowler and leading SIEM/EDR platforms.
- Certified people: CEH, OSCP, CPENT, CISA, ISO 27001 LA/LI, CHFI, CTIA and ECIH professionals.
Annex: Indicative commercial ranges
For internal sales reference only—remove this annex before sharing externally. Ranges are taken from the Codec Networks Bundled Service Models and are subject to scoping, asset counts, frequency and service levels.
|
Bundle |
Package examples and indicative ranges |
|
B1 VAPT Assurance |
Essential ₹1.5–5 lakh; Professional ₹5–15 lakh; Enterprise ₹15–40 lakh; Annual retainer ₹25 lakh–₹1.5 crore |
|
B2 AppSec & DevSecOps |
API Quick Check ₹2–6 lakh; AppSec Professional ₹8–20 lakh; DevSecOps Maturity ₹12–35 lakh; Secure SDLC retainer ₹3–15 lakh/month |
|
B3 Cloud & Zero Trust |
Cloud Essential ₹3–8 lakh; Professional ₹8–25 lakh; Enterprise ₹25–75 lakh; Continuous assurance ₹2–10 lakh/month |
|
B4 Regulatory Audit |
Gap review ₹5–15 lakh; Full regulatory audit ₹15–50 lakh; Multi-framework audit ₹30 lakh–₹1.25 crore; Annual retainer ₹3–20 lakh/month |
|
B5 GRC, ISO, SOC 2 |
ISO readiness ₹5–15 lakh; ISO implementation ₹15–45 lakh; SOC 2 readiness ₹15–60 lakh; GRC retainer ₹2–12 lakh/month |
|
B6 Privacy & DPDPA |
Quick assessment ₹3–10 lakh; Implementation ₹10–40 lakh; DPO-as-a-Service ₹2–8 lakh/month; Privacy retainer ₹3–15 lakh/month |
|
B7 Managed SOC |
Starter ₹2–5 lakh/month; Professional ₹5–15 lakh/month; Enterprise ₹15–50 lakh/month; co-managed per FTE/shift |
|
B8 Forensics & IR |
Triage ₹3–15 lakh; Full investigation ₹15–75 lakh; Ransomware response ₹25 lakh–₹1.5 crore; IR retainer ₹5–50 lakh/year |
|
B9 TPRM |
₹25,000–₹2 lakh per vendor; batch pricing for 50–500 vendors; retainer ₹3–25 lakh/month |
|
B10 Simulation & Tabletop |
Awareness ₹1–5 lakh; Phishing simulation ₹2–10 lakh; Tabletop ₹5–20 lakh; Cyber war-game ₹15–75 lakh; Annual retainer ₹10 lakh–₹1 crore/year |
|
B11 Emerging Tech |
AI/LLM risk review ₹5–25 lakh; Smart contract audit ₹5–50 lakh; Emerging tech retainer ₹5–25 lakh/month |
Talk to Codec Networks
|
Contact Codec Networks Pvt. Ltd. New Delhi: 507, 5th Floor, New Delhi House, Barakhamba Road, Connaught Place, New Delhi – 110001 Gurugram: 707, 7th Floor, Silverton Tower, Golf Course Extension Road, Sector 50, Gurugram – 122018, Haryana Landline: 011 430 496 96 | 011 437 522 99 Mobile: +91 99716 76124 | +91 88007 88220 | +91 88003 31124 Email: mktg@codecnetworks.com Web: www.codecnetworks.com |
Note: Service scope, deliverables, monitoring coverage and service levels are confirmed during engagement scoping. Services support risk reduction and assurance but do not guarantee prevention of all cyber incidents or regulatory compliance. Regulatory references are summaries; confirm against the official instruments applicable to each entity.