

Resources Categories
INDUSTRY FACT FILE · INSURANCE
Industry Overview: Insurance and Reinsurance in India
The types of insurers and reinsurers, how they are owned and regulated, who buys cybersecurity inside them, and why each needs a distinct approach.
|
In this document 1. Why insurance cybersecurity matters now 2. The ecosystem at a glance 3. Categories of insurers and industry players 4. IRDAI's 2026 cyber security guidelines in brief 5. Government, public-sector and private participants 6. Who buys cybersecurity inside an insurer 7. Why each insurer type needs a different approach 8. How Codec Networks works with insurers |
|
Sector scope Sector: Insurance and reinsurance — life, general and health insurers, reinsurers and Foreign Reinsurance Branches. Primary service proposition: IRDAI cyber audits, SOC, privacy, cloud security, ransomware resilience and incident exercises. Brokers, corporate agents, web aggregators, TPAs, repositories and insurtech platforms are covered in the separate Insurance Intermediaries & Insurtech fact file. |
1. Why insurance cybersecurity matters now
Insurers hold some of the most sensitive information in the economy: health and medical records, financial and family details, claims histories and payment data. They also run critical services—cashless hospitalisation, claims settlement and policy servicing—that customers depend on at difficult moments. That combination makes insurers prime targets for ransomware, data theft and fraud.
|
6 Apr 2026 IRDAI's revised cyber security guidelines issued |
6 hours To report incidents to CERT-In, with copies to IRDAI |
6-monthly External PT by CERT-In empanelled auditors |
Quarterly ISRMC meetings under the 2026 guidelines |
On 6 April 2026 the Insurance Regulatory and Development Authority of India (IRDAI) issued revised Information and Cyber Security Guidelines, replacing the 2023 guidelines and requiring compliance from the current financial year. They tighten governance, testing, audit, vendor, cloud and data-protection requirements for insurers, Foreign Reinsurance Branches and intermediaries.
|
Key takeaway For insurers, cybersecurity protects both policyholders and the promise to pay claims. IRDAI's 2026 guidelines make it a quarterly governance topic with annual independent assurance. |
2. The ecosystem at a glance
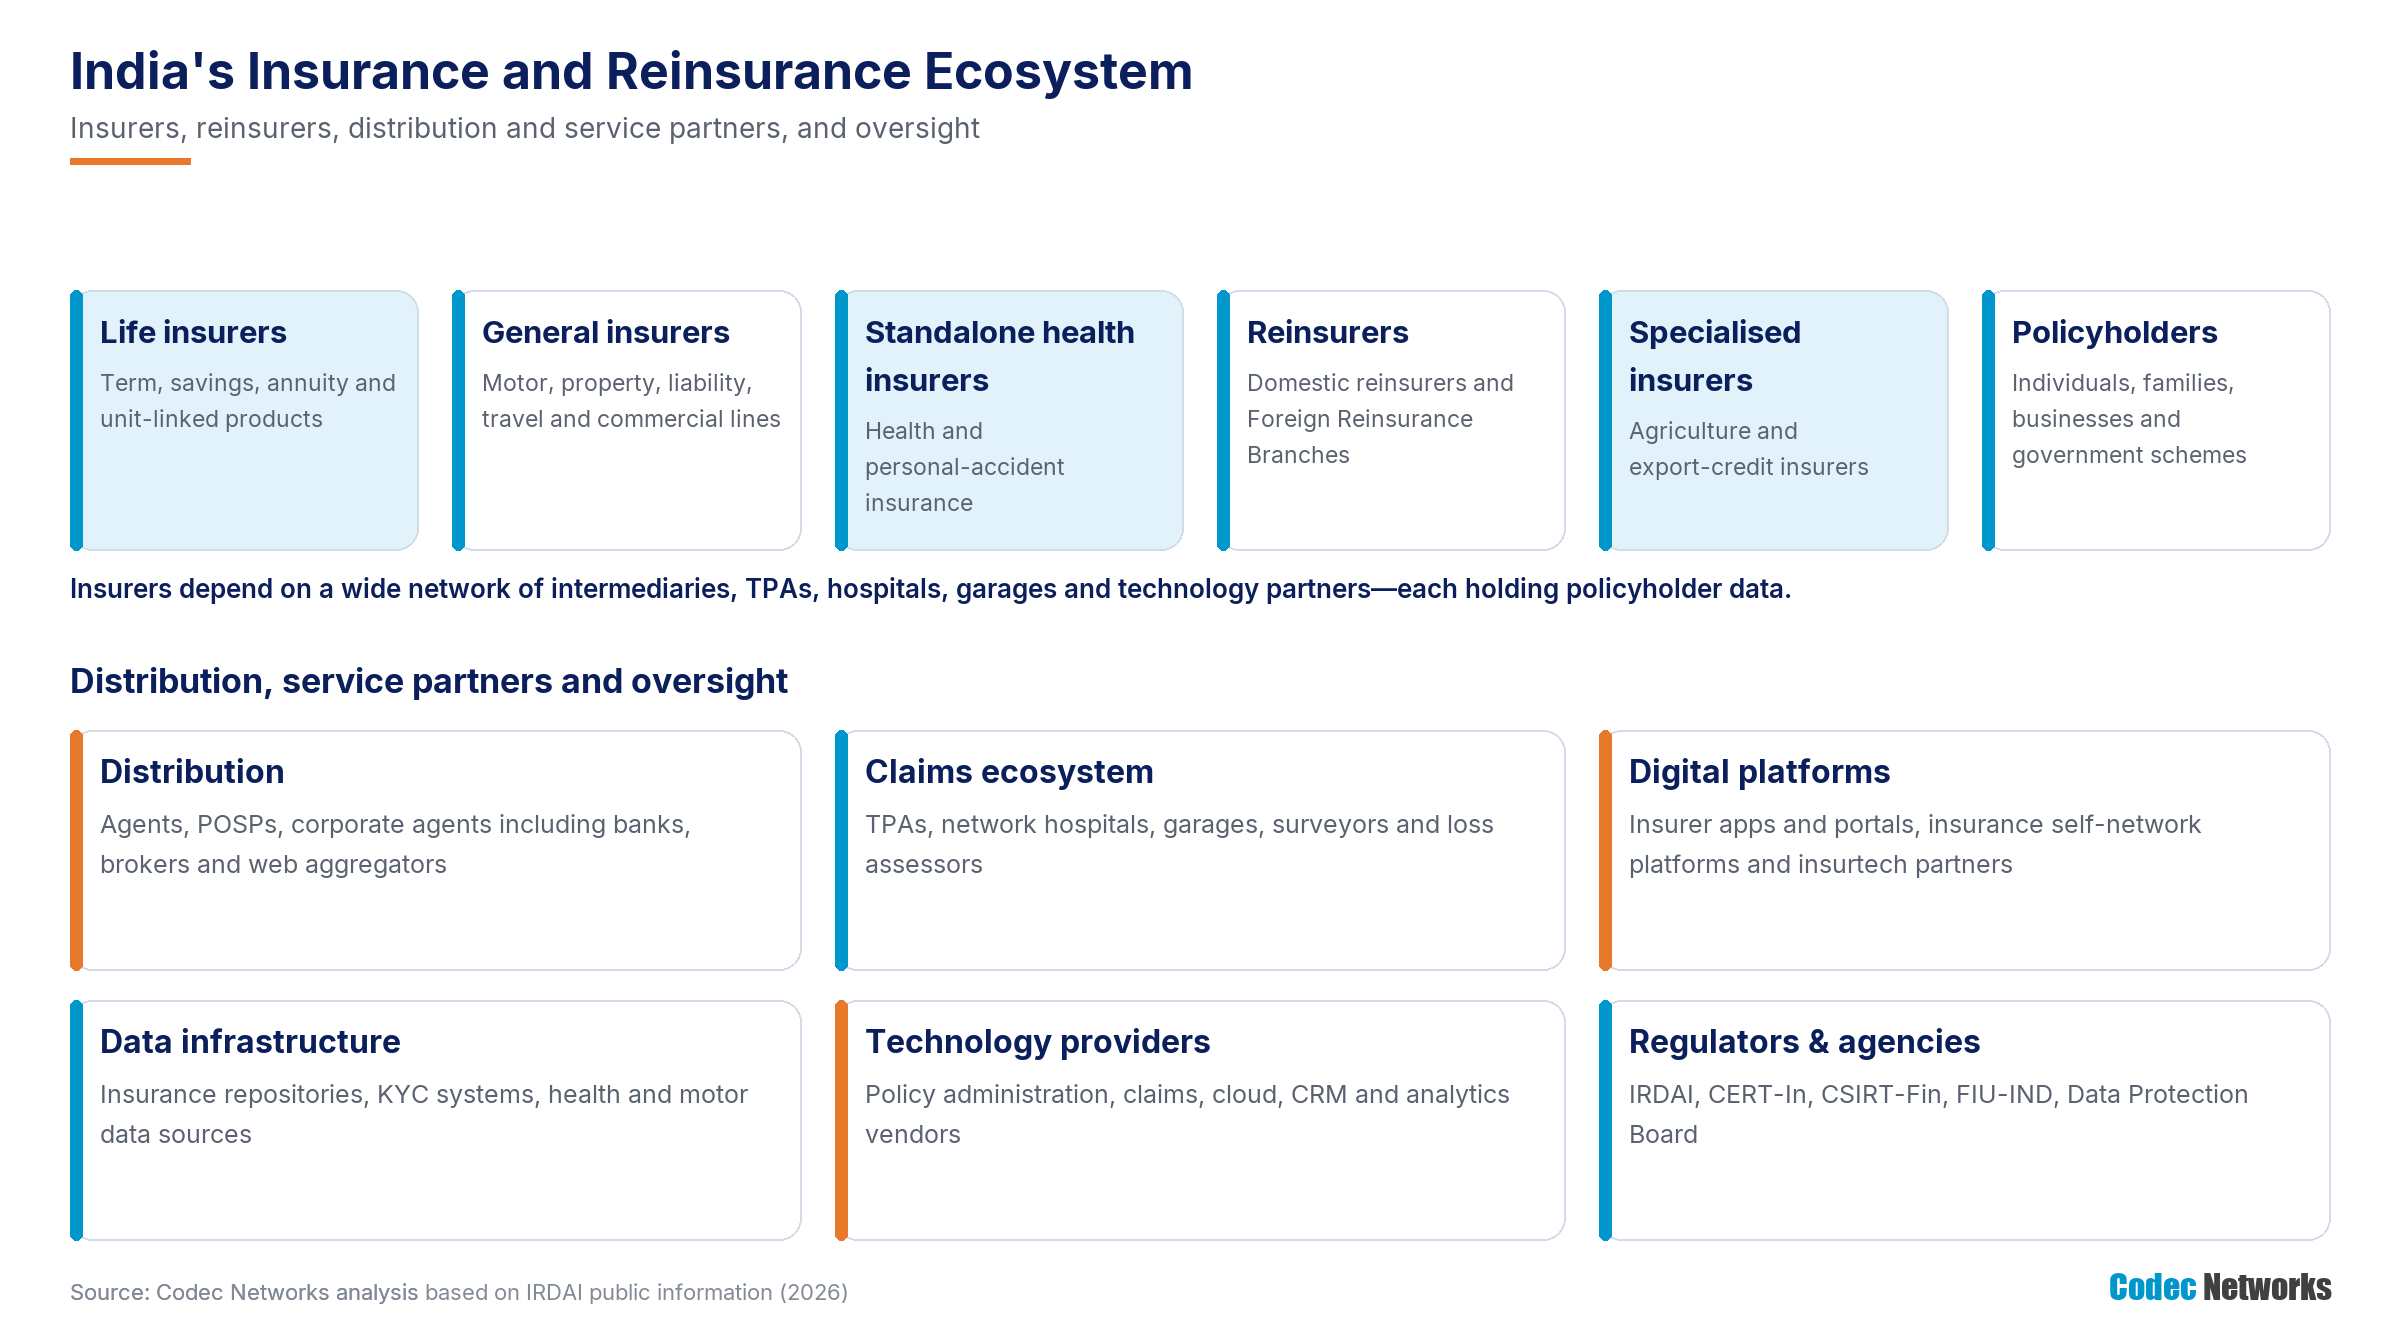
Figure 1: India's insurance and reinsurance ecosystem.
3. Categories of insurers and industry players
|
Category |
Who they are |
Typical ownership |
Key regulatory basis |
|
Life insurers |
Term, endowment, savings, annuity, pension and unit-linked products |
Public-sector (including LIC) and private insurers, many with foreign partners; several listed |
Insurance Act, 1938; IRDAI regulations; IRDAI 2026 cyber guidelines |
|
General insurers |
Motor, health, property, marine, liability, travel and commercial insurance |
Public-sector and private insurers |
Insurance Act; IRDAI regulations; IRDAI 2026 cyber guidelines |
|
Standalone health insurers |
Health, critical illness and personal-accident insurance |
Private insurers |
IRDAI health regulations; IRDAI 2026 cyber guidelines |
|
Reinsurers |
Insurance for insurers, including the national reinsurer |
Public-sector and private reinsurers |
IRDAI reinsurance regulations; IRDAI 2026 cyber guidelines |
|
Foreign Reinsurance Branches (FRBs) |
Branches of global reinsurers operating in India |
Global reinsurance groups |
IRDAI regulations; IRDAI 2026 guidelines on a comply-or-explain basis |
|
Specialised insurers |
Agriculture insurance and export credit insurance |
Government-owned |
Sector-specific mandates; IRDAI regulations |
|
Insurance technology providers |
Policy administration, claims, CRM, cloud and analytics vendors |
Indian and international technology companies |
Insurers' vendor and outsourcing requirements under IRDAI guidelines |
4. IRDAI's 2026 cyber security guidelines in brief
|
Area |
Key requirements (as reported) |
|
Applicability |
Insurers, Foreign Reinsurance Branches (comply or explain) and intermediaries including brokers, corporate agents, web aggregators and TPAs Insurers must ensure agents, POSPs and individual surveyors follow a minimum security framework under the insurer's Board-approved policy |
|
Governance |
Information Security Risk Management Committee (ISRMC) meeting at least quarterly CISO with no direct reporting line to the Head of IT and no business targets; tiered approval of security exceptions |
|
Assurance |
Annual audit by an independent assurance team, with the auditor rotated every three years Insurers submit audit reports to IRDAI within 90 days of financial year-end or 30 days of audit completion, whichever is earlier |
|
Testing |
External penetration testing at least once every six months, using grey-box or white-box methods, by a CERT-In empanelled auditor |
|
Incident reporting and resilience |
Cyber incidents reported to CERT-In within six hours of detection, with copies to IRDAI and other relevant regulators BCP and DR plans tested at least annually against realistic disaster scenarios, with results to the ISRMC |
|
Cloud, vendors and data |
Cloud providers empanelled by MeitY with valid STQC audit status; data erasure on termination Vendor contracts with right-to-audit and prior approval for sub-outsourcing Measures for DPDP Act compliance, classification of personal data and encryption of confidential information |
|
Verify the circular These points summarise the 6 April 2026 guidelines as reported in public sources. Insurers should confirm each requirement and timeline against the official IRDAI text. |
5. Government, public-sector and private participants
- IRDAI regulates insurers, reinsurers and intermediaries under the Insurance Act, 1938 and the IRDA Act, 1999.
- Public-sector insurers—including LIC, public general insurers and the national reinsurer—serve a large share of policyholders and government schemes.
- Government schemes such as health and crop insurance programmes rely on insurers' and TPAs' systems.
- Private insurers, many in joint ventures with global groups, compete strongly on digital distribution and claims experience.
- Hospitals, garages and TPAs form part of the claims ecosystem and hold insurer data.
6. Who buys cybersecurity inside an insurer
|
Stakeholder |
What they care about |
What they buy |
|
Board and ISRMC |
Regulatory standing, policyholder trust, resilience |
Board advisory, ISRMC reporting, crisis exercises |
|
CISO |
Compliance with the 2026 guidelines, control effectiveness, incidents |
Audits, PT, SOC, threat hunting |
|
CIO / CTO and digital |
Platform availability, secure releases, cloud |
Application and API testing, cloud reviews |
|
Claims and fraud control |
Claims fraud and leakage |
Fraud analytics, forensic investigations |
|
Compliance and audit |
IRDAI reporting and audit timelines |
Independent audits, gap assessments, evidence |
|
Data protection lead |
Health and personal data, DPDP readiness |
Privacy programme, classification, DLP |
|
Vendor and partner management |
TPA, hospital, broker and vendor risk |
Third-party assessments, contract reviews |
7. Why each insurer type needs a different approach
|
Insurer type |
Highest-consequence risk |
Starting point for assurance |
|
Life insurer |
Payout and surrender fraud, policyholder scams, legacy systems |
Payout-flow testing, brand monitoring, infrastructure VAPT |
|
General insurer |
Claims fraud, partner and garage ecosystem risk |
Claims platform testing, partner assurance, fraud analytics |
|
Health insurer |
Ransomware and medical data leakage, TPA risk |
SOC, segmentation, TPA assurance, DPDPA programme |
|
Reinsurer / FRB |
Targeted phishing, BEC and confidential data theft |
Email security, executive impersonation testing, data protection |
|
Government-scheme insurer |
Large beneficiary datasets and partner networks |
Data protection, partner assessments, resilience testing |
8. How Codec Networks works with insurers
Codec Networks is a CERT-In empanelled information security auditing organisation certified to ISO 9001:2015, ISO/IEC 27001:2022 and ISO/IEC 20000-1:2018. For insurers we deliver gap assessments and audit support against IRDAI's 2026 guidelines, six-monthly external penetration testing, managed SOC, privacy programmes, cloud security reviews, ransomware resilience testing and incident exercises.
Talk to Codec Networks
|
Contact Codec Networks Pvt. Ltd. New Delhi: 507, 5th Floor, New Delhi House, Barakhamba Road, Connaught Place, New Delhi – 110001 Gurugram: 707, 7th Floor, Silverton Tower, Golf Course Extension Road, Sector 50, Gurugram – 122018, Haryana Landline: 011 430 496 96 | 011 437 522 99 Mobile: +91 99716 76124 | +91 88007 88220 | +91 88003 31124 Email: mktg@codecnetworks.com Web: www.codecnetworks.com |
Note: This document is general industry guidance based on public information available as of October 2026, including reported summaries of IRDAI's 2026 guidelines and CERT-In and MeitY publications. Confirm obligations against the official IRDAI circular before making compliance decisions.